
Managed patching and compliance for an insurer
Held critical-patch SLA to 48 hours across an insurer's estate, evidenced every cycle.
48h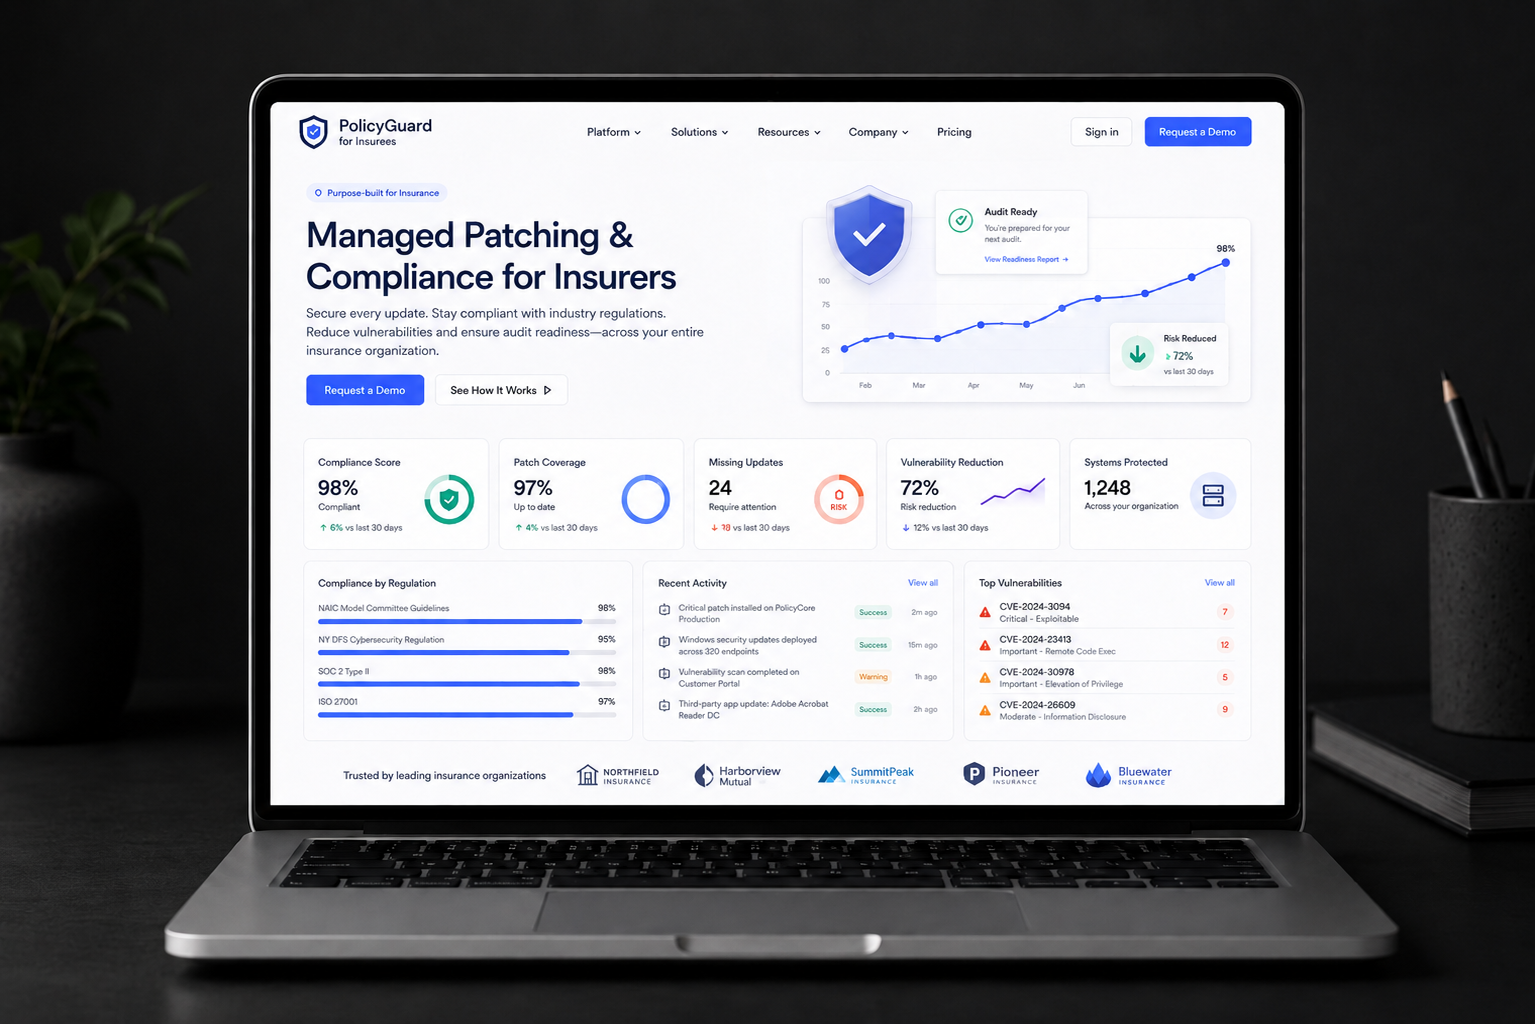
Problem, approach, and the outcome
The client is a UK insurer whose regulated systems had to be kept patched and demonstrably compliant. In insurance, an unpatched vulnerability on a regulated system is both a security and a compliance exposure.
Patching kept slipping whenever delivery pressure rose, which was most of the time, leaving known vulnerabilities open longer than the insurer's own policies allowed.
Patching slipped whenever delivery got busy, which was most of the time, leaving known vulnerabilities open on regulated systems. The most important maintenance kept losing to whatever was more urgent.
Each slip widened the gap between the insurer's stated controls and its actual posture. Policy and reality were drifting apart in a way that would not survive an audit.
It needed patching to happen reliably and to be evidenced, regardless of how busy the delivery teams were. Consistency had to be decoupled from delivery pressure.
We took on managed patching as a standing service, with automated pipelines that apply critical patches within the SLA rather than when someone gets to it. Making patching a dedicated, automated function is what stops it losing to delivery pressure.
A clear exception process handles the cases that genuinely cannot patch on schedule, with sign-off and tracking, so exceptions are managed rather than silent. Nothing falls through the cracks unrecorded.
Every cycle produces evidence aligned to the insurer's control framework, so compliance is provable, not asserted, and coverage was continuous, decoupled from delivery pressure. Posture and policy stayed in step.
- Critical patches applied within 48 hours
- Automated, evidenced patch cycles
- Aligned to the insurer's control framework
- Patching decoupled from delivery pressure
More Cloud & DevOps case studies
24/7 SRE for a telemedicine platform
Ran a telemedicine platform to a 99.98% SLO with a follow-the-sun on-call.
Read the full case study
Managed FinOps for a biotech scale-up
Cut monthly cloud spend 37% for a genomics biotech without slowing a single pipeline.
Read the full case study
Datacenter exit for an NHS hospital group
Migrated 900 clinical workloads off two datacentres to the cloud with zero downtime on patient-facing systems.
Read the full case studyGet a senior architect on the call, first time, every time.
No SDR gauntlet. 30 minutes with an engineer who can scope the problem, name the risks, and give you an honest feasibility call.