Text Classification
Multi-class and multi-label classifiers with calibrated confidences and active-learning loops.
Text extraction, classification, summarisation, and semantic search, domain-tuned, grounded in your data, and shipped with the eval discipline regulated buyers expect.
Pick a single capability or compose them into a full programme. Every engagement is architect-led and runs through the same eval / governance gates.
Multi-class and multi-label classifiers with calibrated confidences and active-learning loops.
Custom NER, relation extraction, and structured-output pipelines, schema-driven and validated by default.
Aspect-level sentiment and intent models tuned to your domain, beyond generic five-star prediction.
Evaluation, observability, policy, and audit across every agent, tool, and workflow.
Faithful, citation-anchored summarisation across long-form documents with controlled style and length.
Hybrid lexical + dense retrieval with reranking, relevance you can defend, not relevance you have to debug.
Task-oriented and open-domain conversation with citation, hand-off, and audit-trail logging from day one.
Modern NLP is more than wrapping a transformer in an API. These are the surrounding capabilities that make an NLP feature production-grade.
Encoder, decoder, and encoder-decoder picks matched to the task, not encoder-only because it was easy.
Custom tokenisers for domain vocabularies, multilingual support, and structured-output schemas.
LoRA, QLoRA, and continued-pretraining on your corpus, measurable uplift on your domain evals.
PII redaction, jailbreak resistance, structured-output validation, and audit-trail logging by default.
Selected programmes from the last 24 months, anonymised where required, specific where it matters.
Topic, severity, and root-cause classification across multi-channel complaints. Cleared SS1/23 evidence first pass.
Structured extraction across 11 carrier templates with confidence-gated human review for low-confidence fields.
Faithful summaries of episode notes with full source-span citations. DSPT-compliant from day one of pilot.
Clause-library-grounded extraction and risk classification across 14 deal teams. First-pass review days → hours.
Generates suitability-aware research summaries with full source lineage. Cleared MiFID II review on first pass.
Aspect-level sentiment across reviews and support tickets, fed into the merchandising and product roadmap.
Every engagement walks the same path, sized to your problem, but with the same verification gates baked in.
Two-week paid sprint. Architect-led. Output: regulator map, costed roadmap, signed scope.
Pod composition, sequenced milestones, change-control governance, and risk register.
Reference architecture, threat model, design system, and acceptance criteria locked.
Weekly demos, trunk-based, CI/CD from day one. Code reviewed against spec at every gate.
Unit, integration, e2e, security, performance, and accessibility, automated and gated.
Blue-green or canary, observability live before launch, rollback rehearsed.
Managed services or hypercare hand-off. Defined SLOs, named on-call, monthly reviews.
Success stories
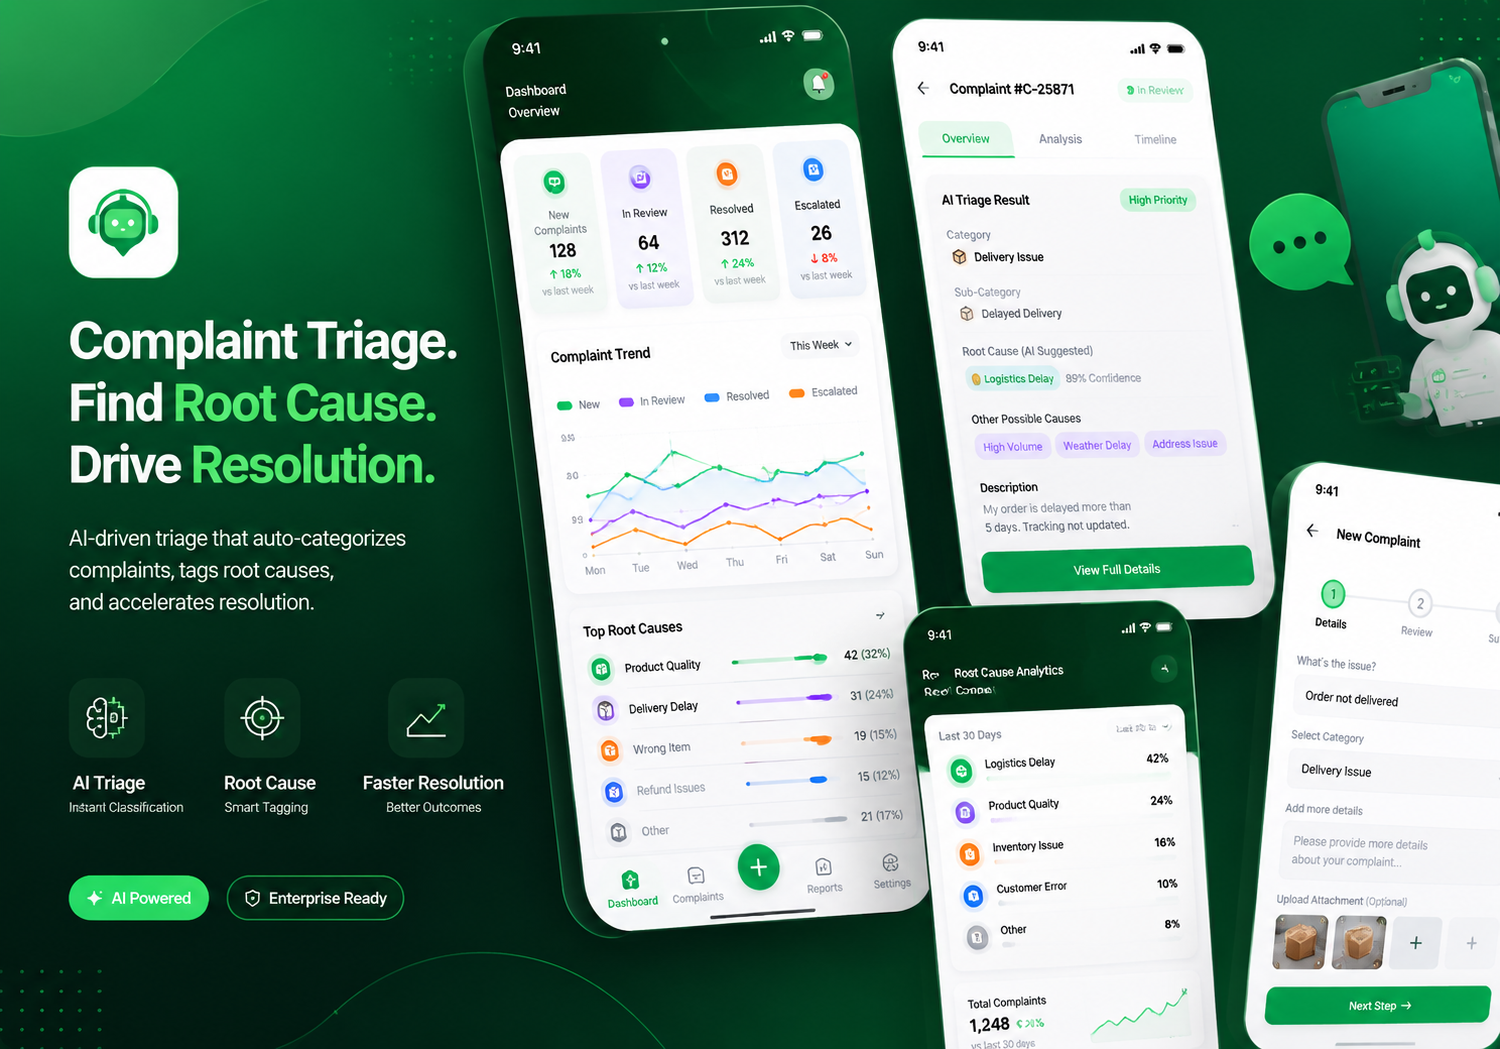
Auto-classified 58% of citizen complaints to root cause, feeding the department's reporting directly.
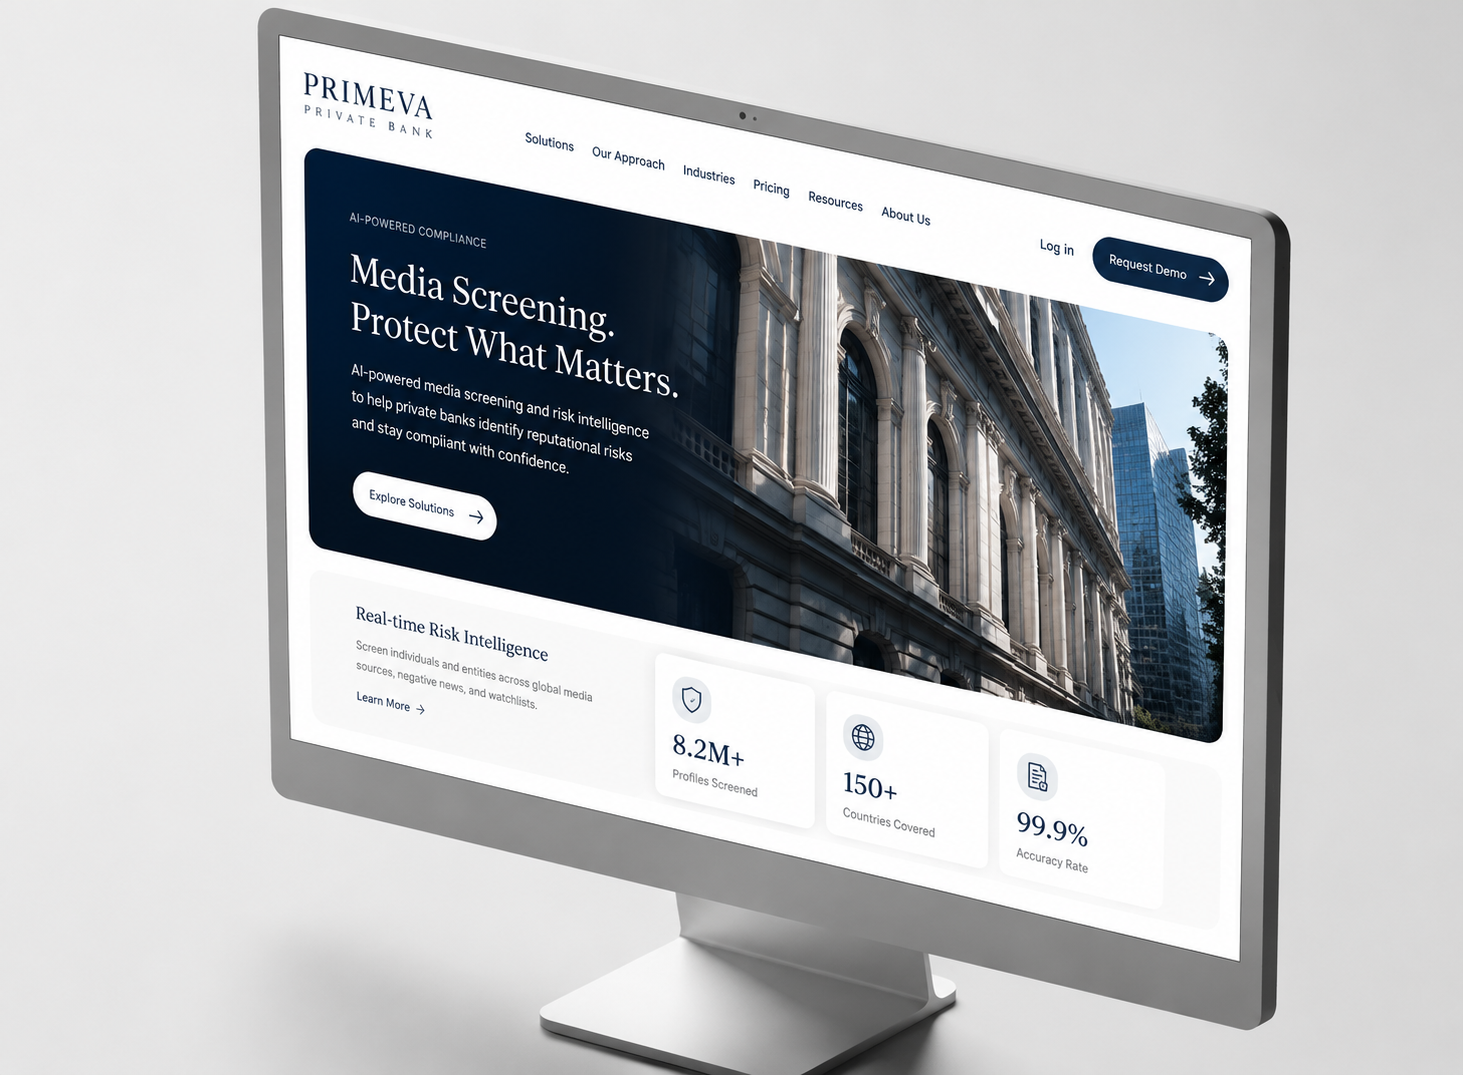
Screened 12x more names at a lower false-positive rate, each hit evidenced.
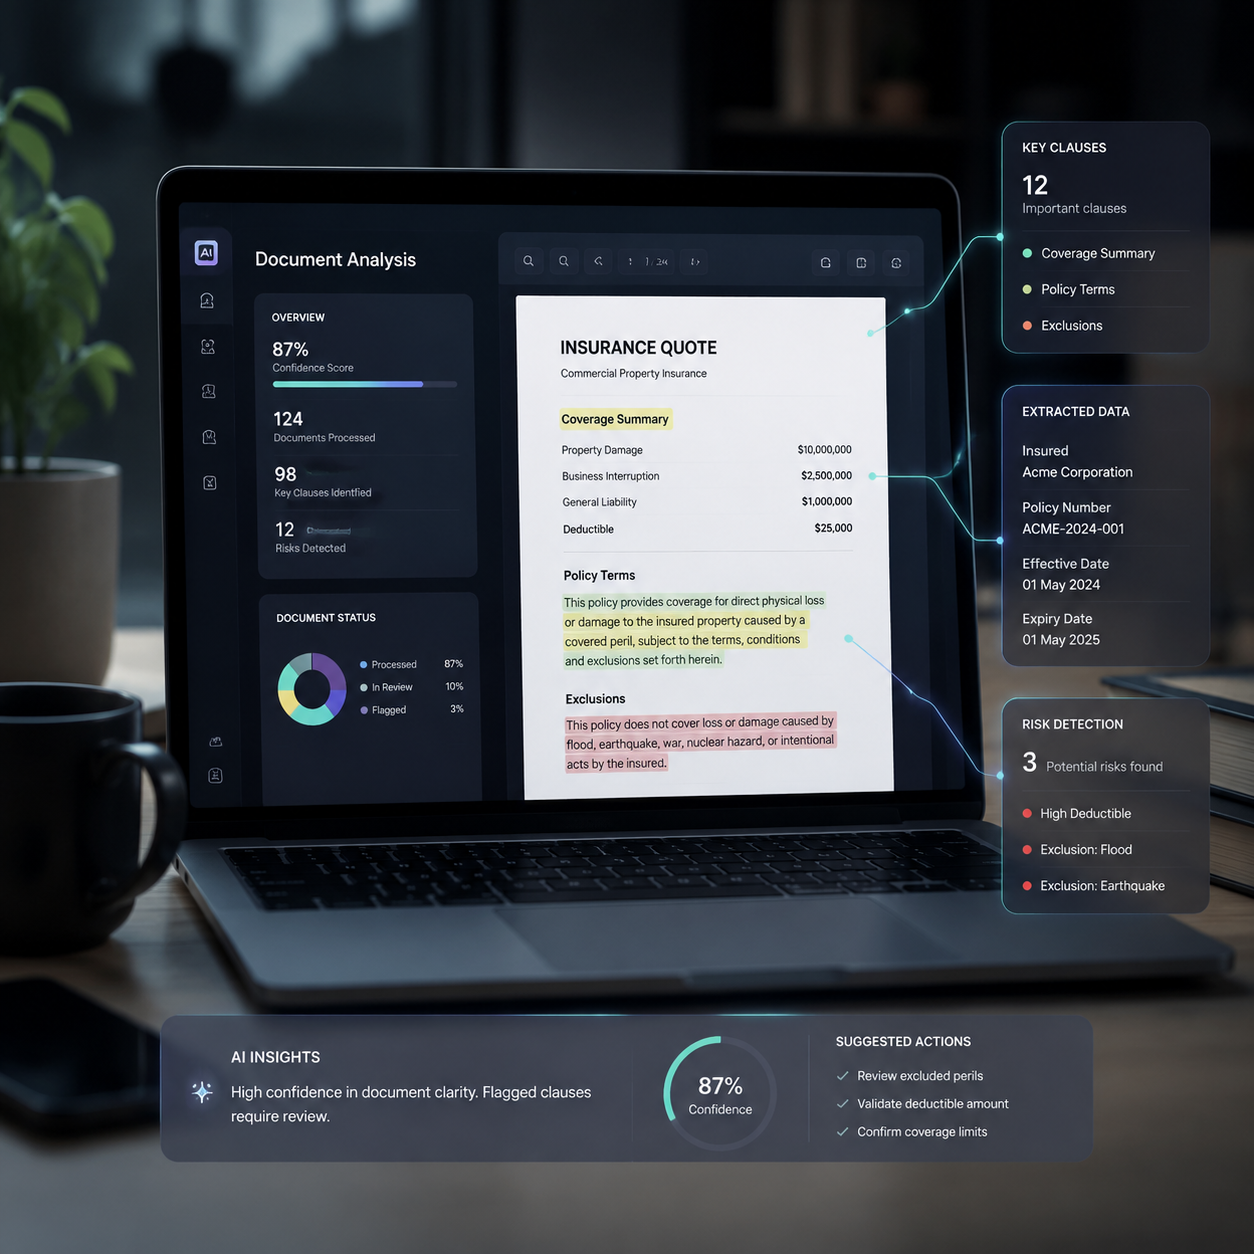
Drafted first-pass quotes from submission packs 3.1x faster, every clause cited back to the wording it came from.
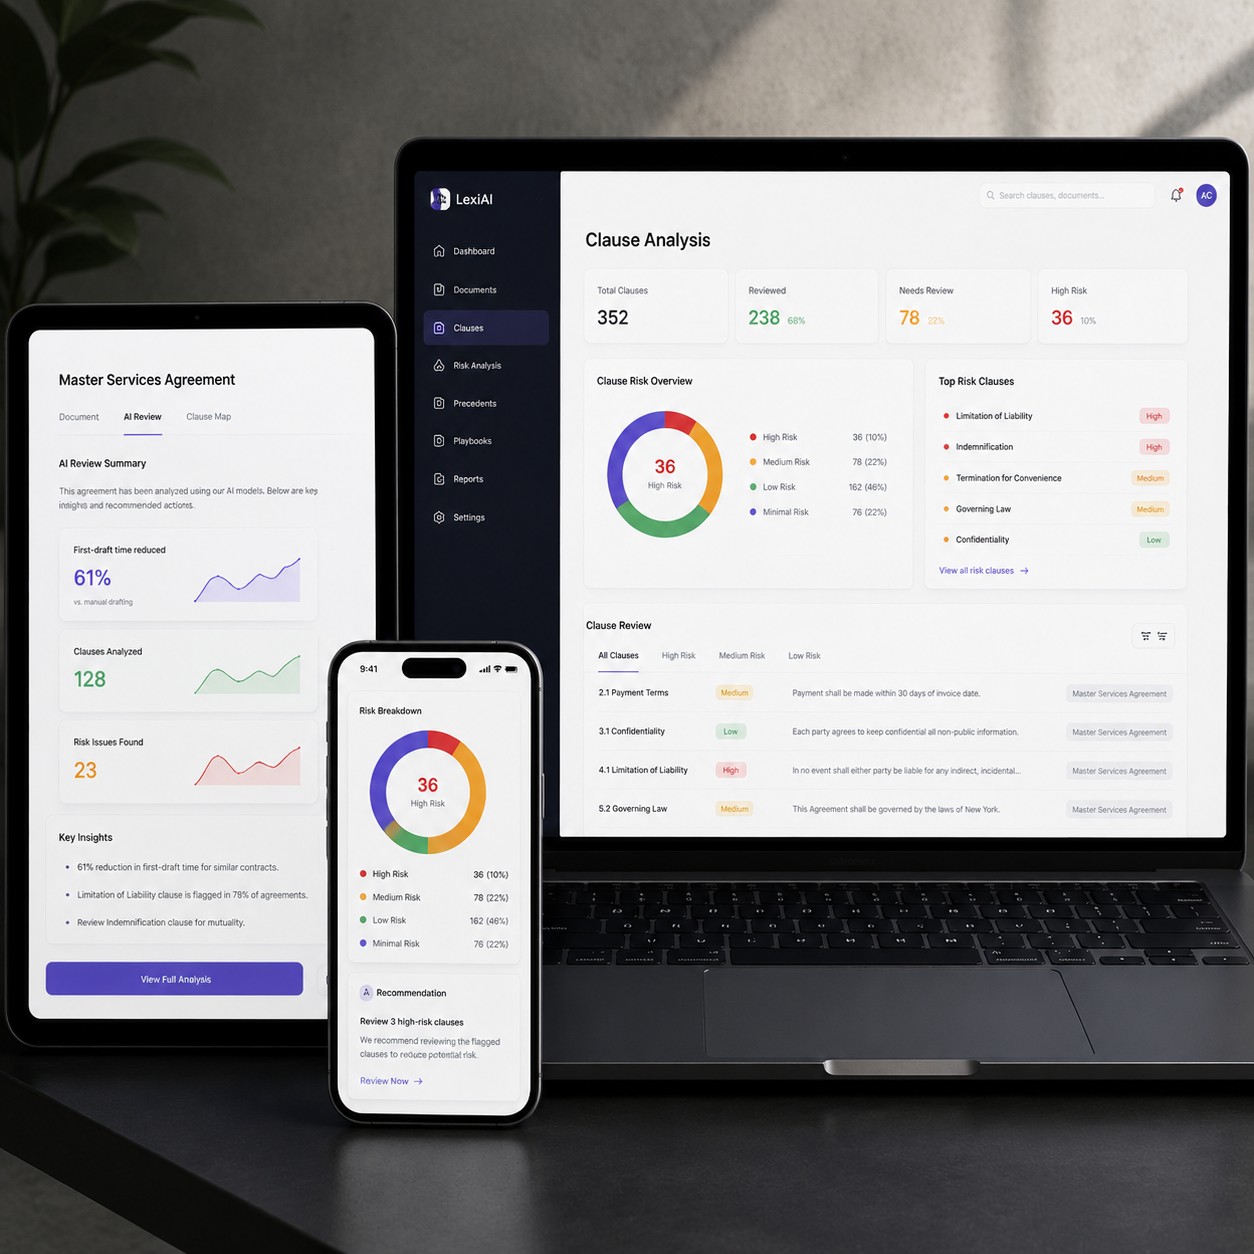
Cut first-draft time on regulated commercial contracts by 61%, each clause traceable to firm precedent.
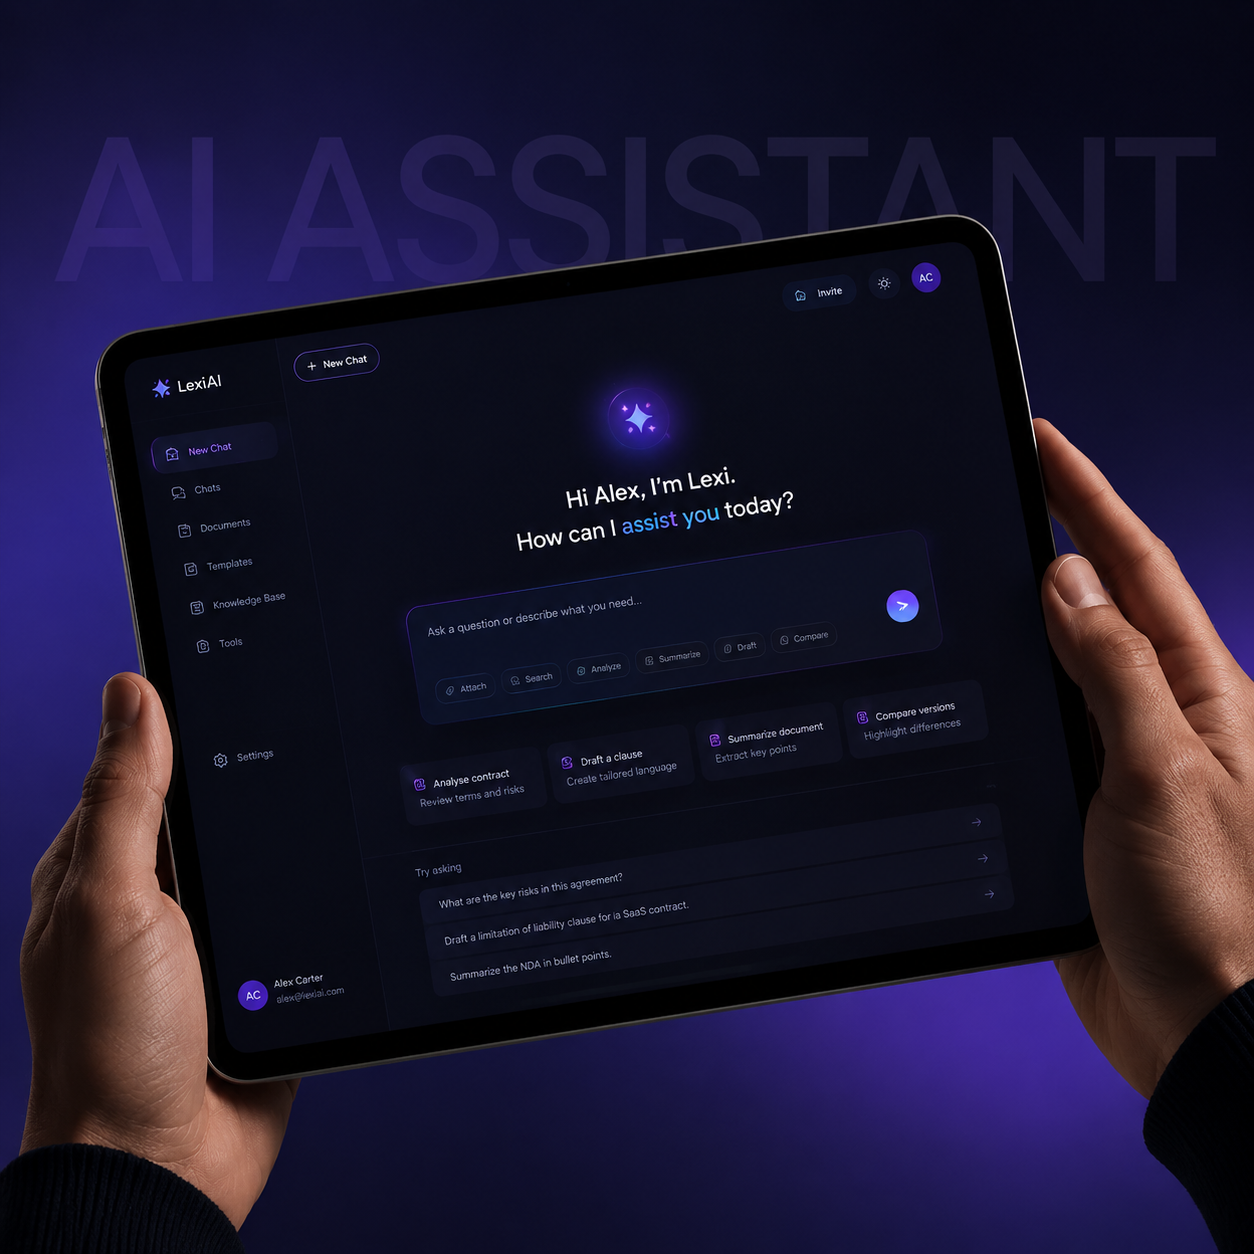
Cut average handle time 44% across 2,600 agents, with answers grounded in approved policy only.
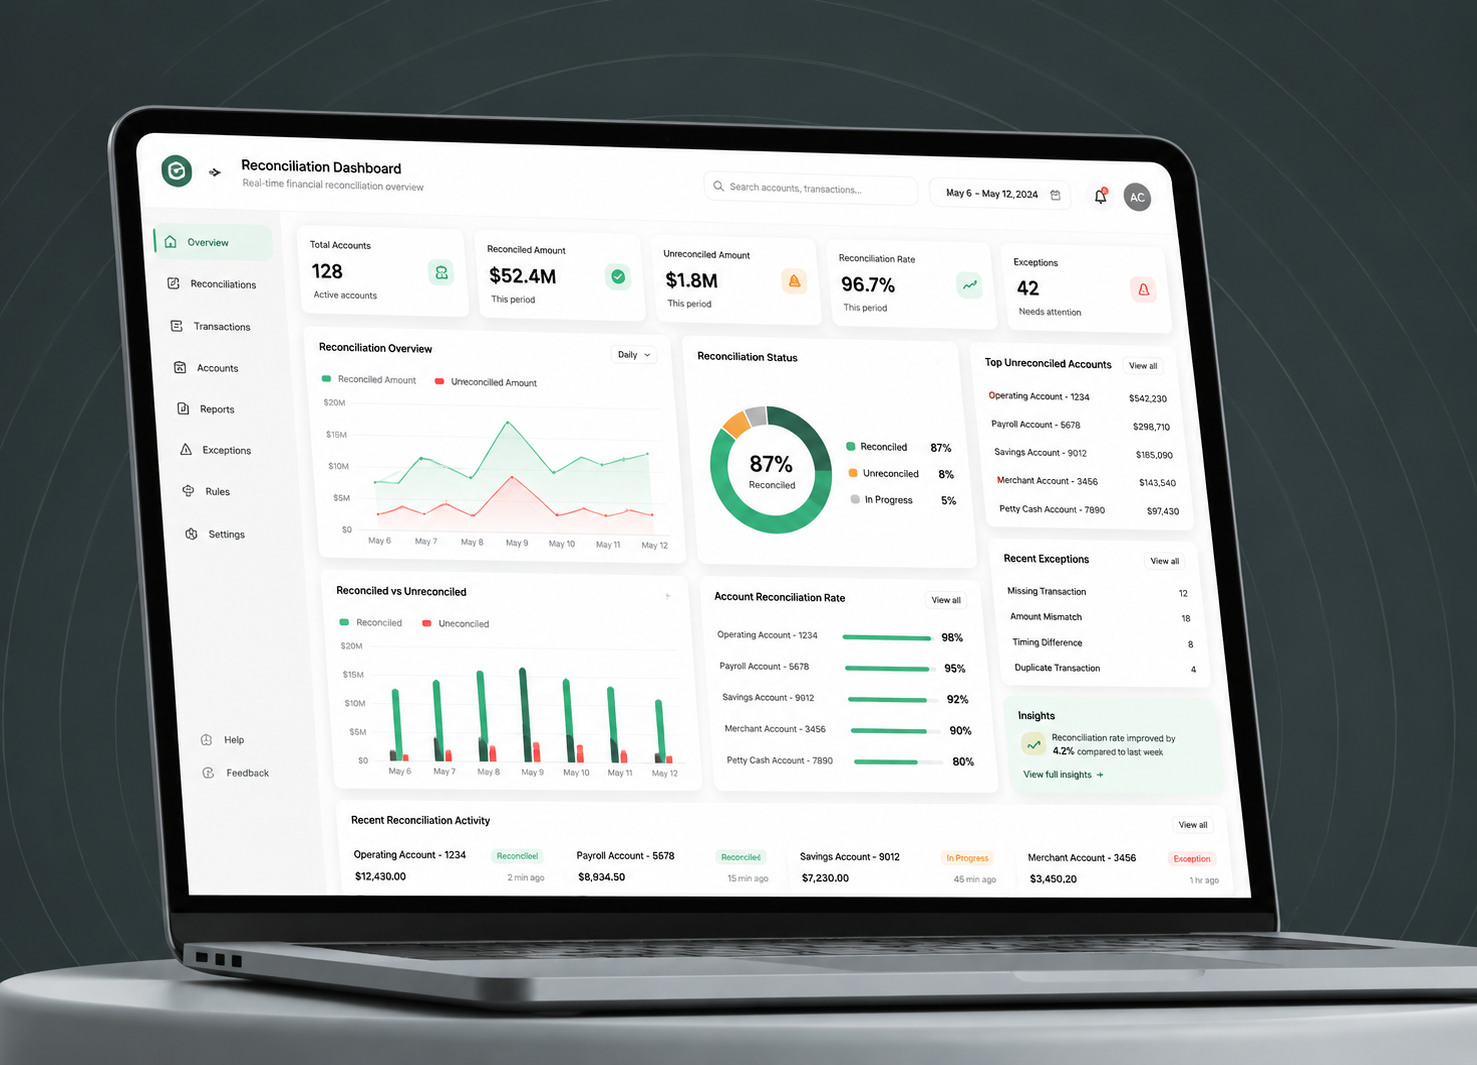
Resolved 89% of reconciliation breaks without a human, every action logged for audit.
Cut median incident remediation from 41 to 7 minutes across a manufacturer's OT platform, with a human approval gate on every action.
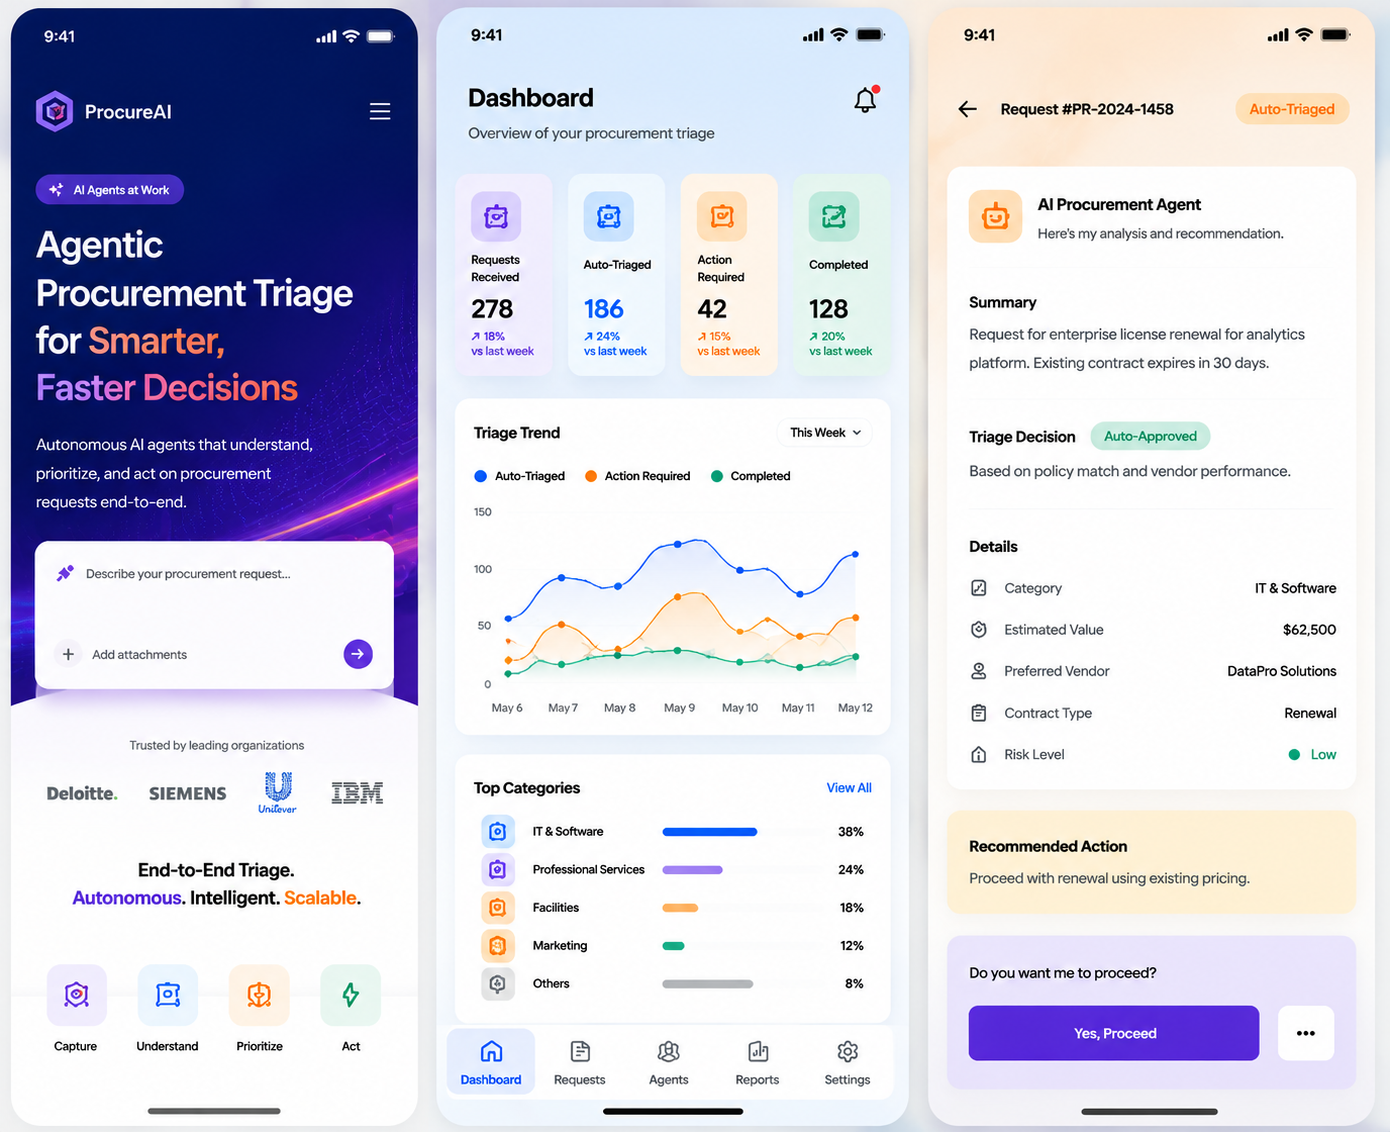
Routed and matched 73% of purchase requests end to end, escalating only genuine exceptions.
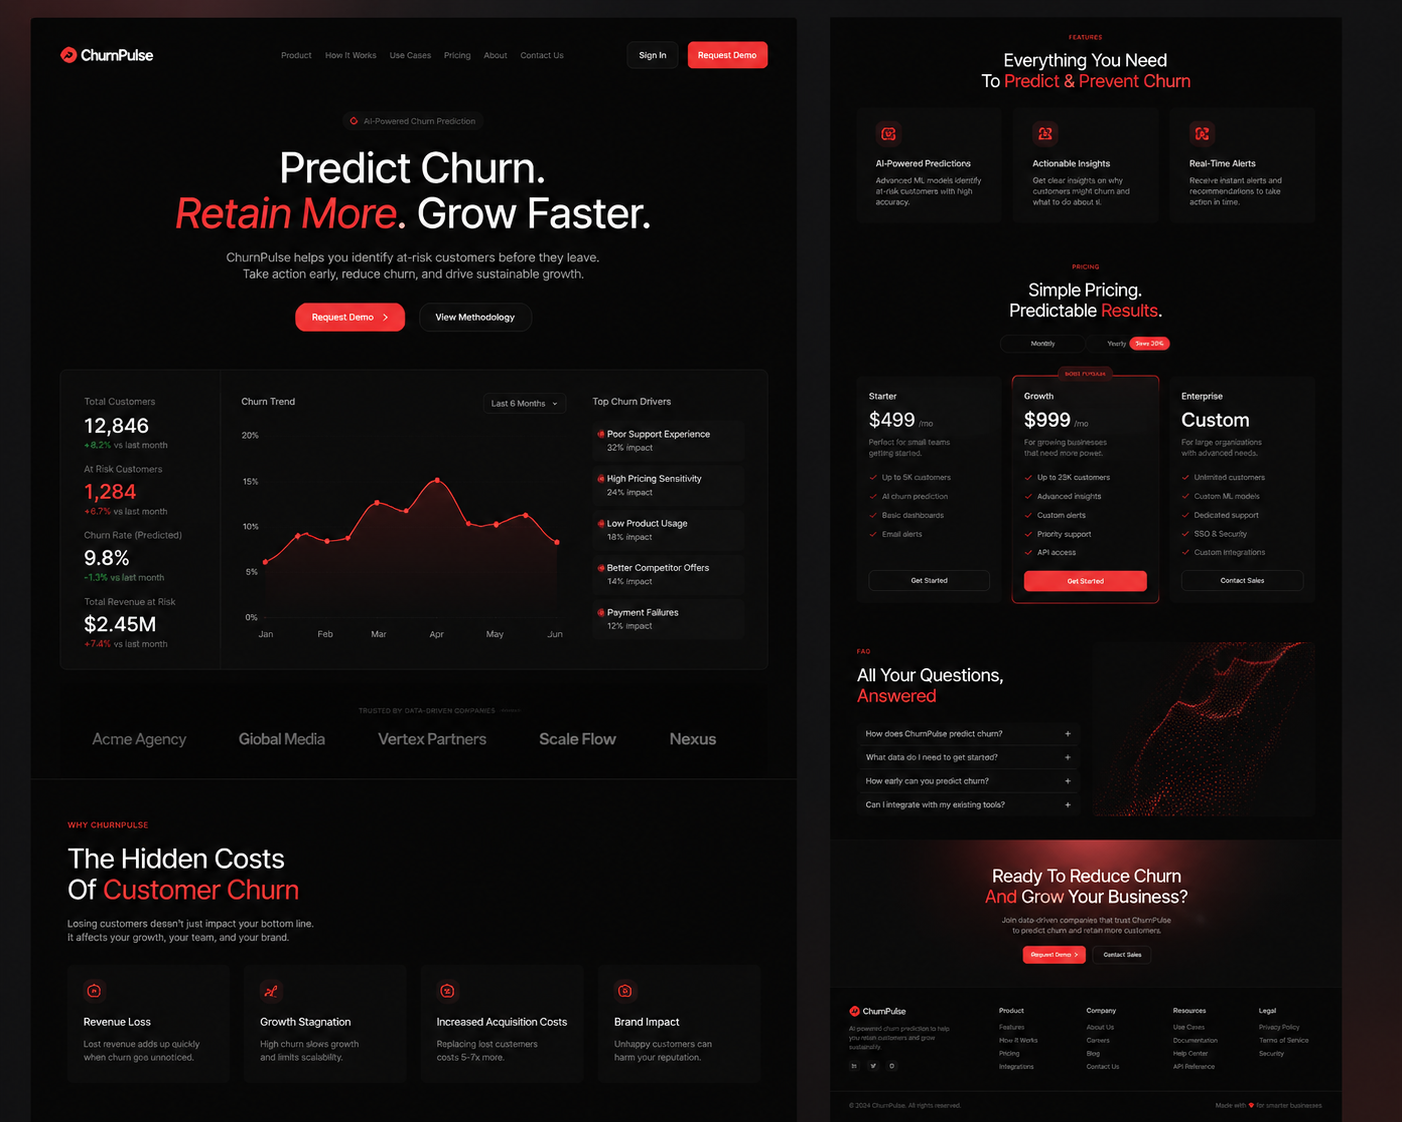
Cut voluntary churn 18% in two quarters with next-best-action scoring for a meal-subscription platform.
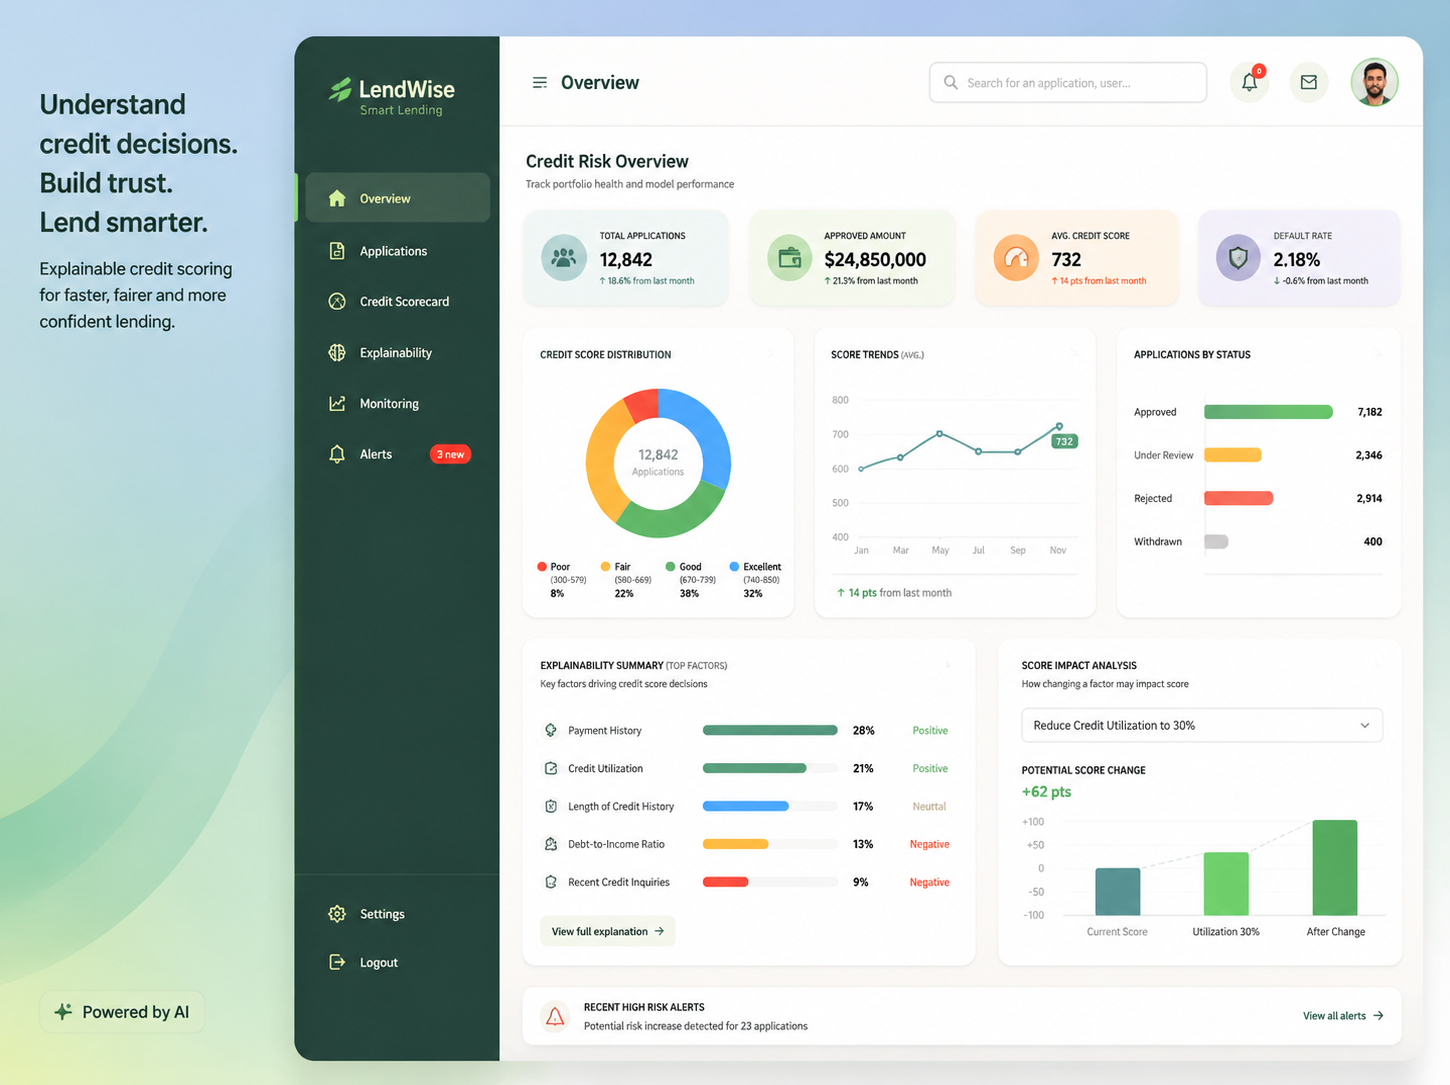
Lifted approval rates 31% at constant loss, every decision reason-coded for the FCA.
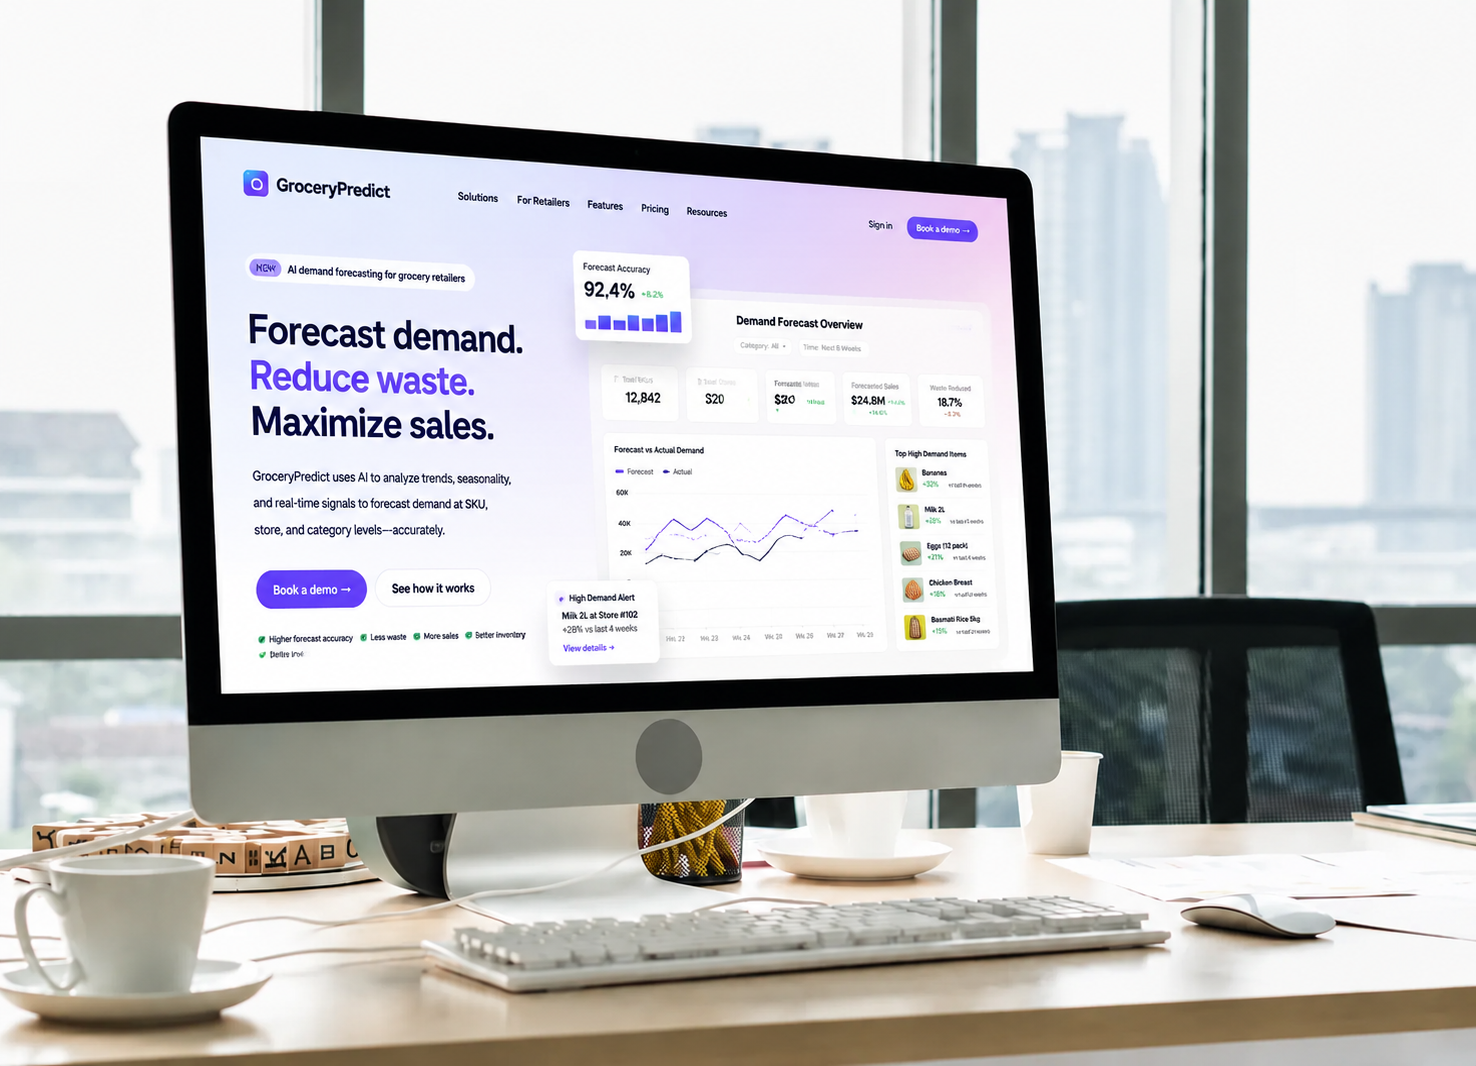
Cut waste 22% across 900 stores with SKU-level probabilistic forecasts.
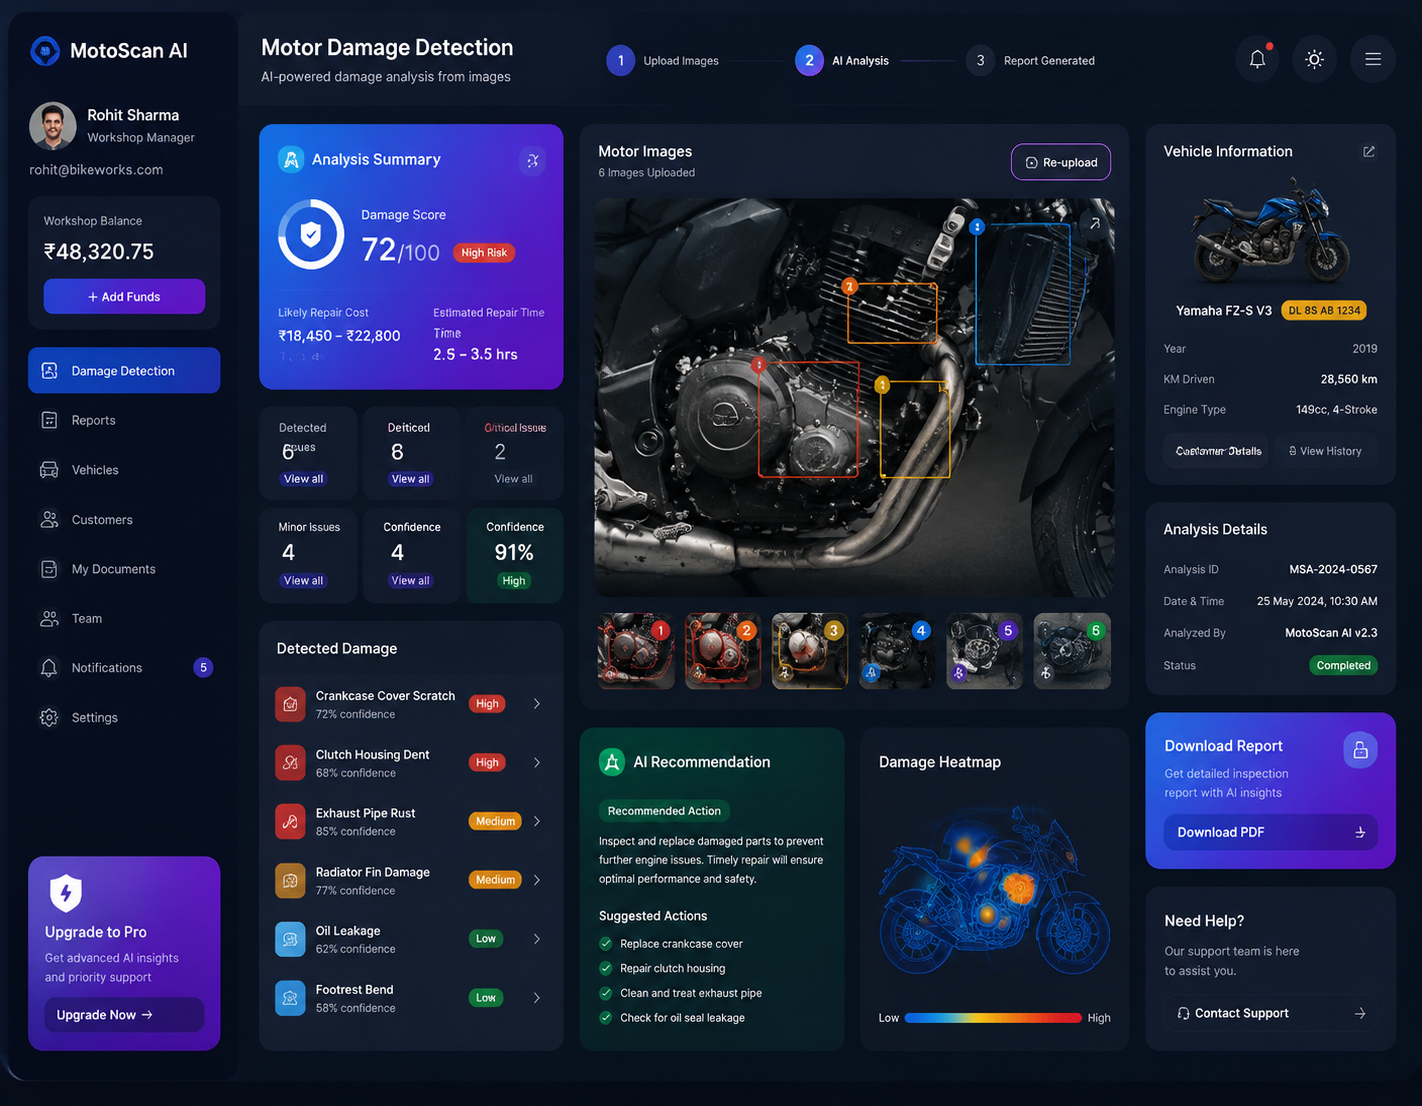
Settled 47% of motor claims from images alone, with fraud flags surfaced inline.
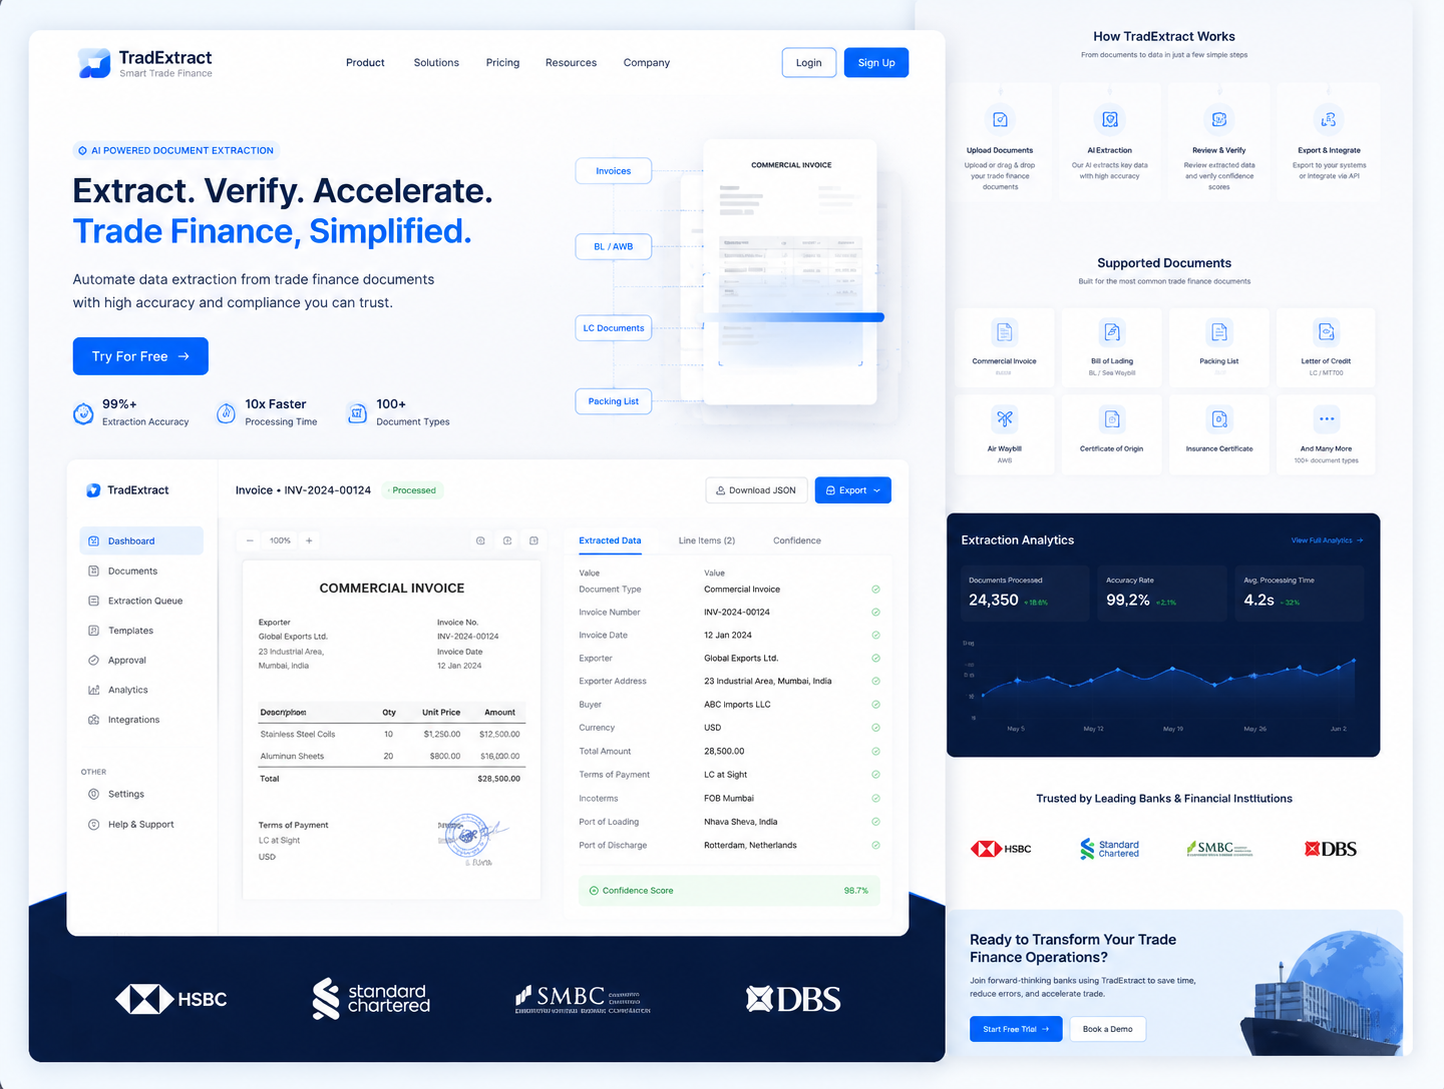
Achieved 94% straight-through extraction on bills of lading and customs paperwork for a logistics operator.
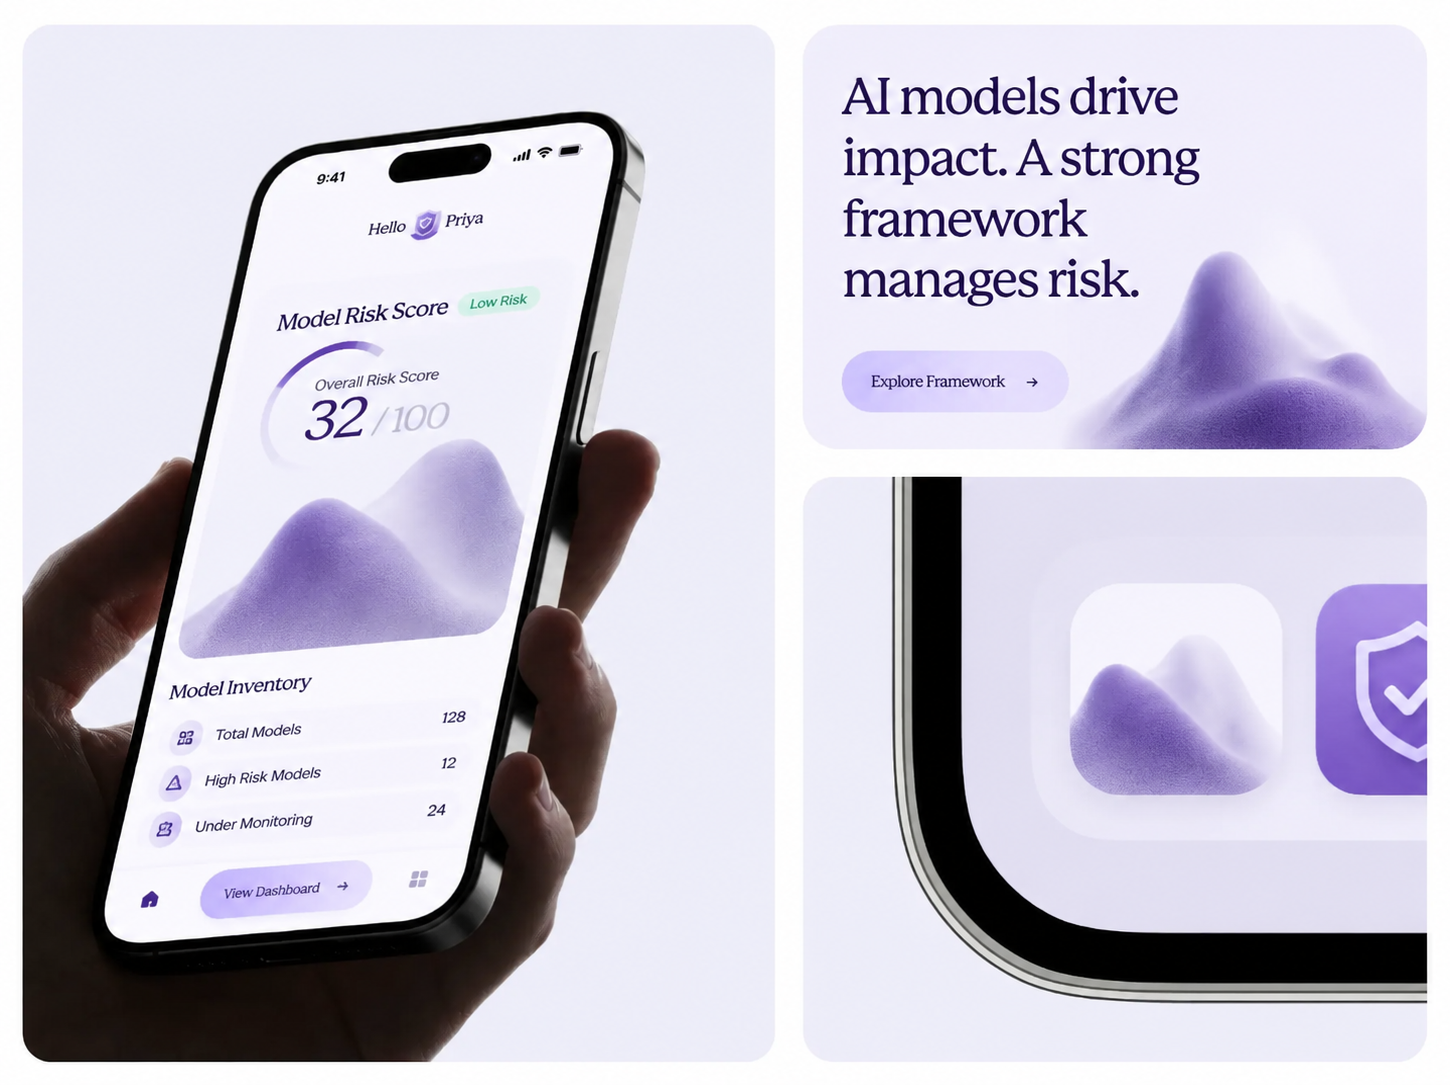
Stood up a board-ready AI governance and model-risk framework for a pharma company in 9 weeks, cleared at first internal audit.
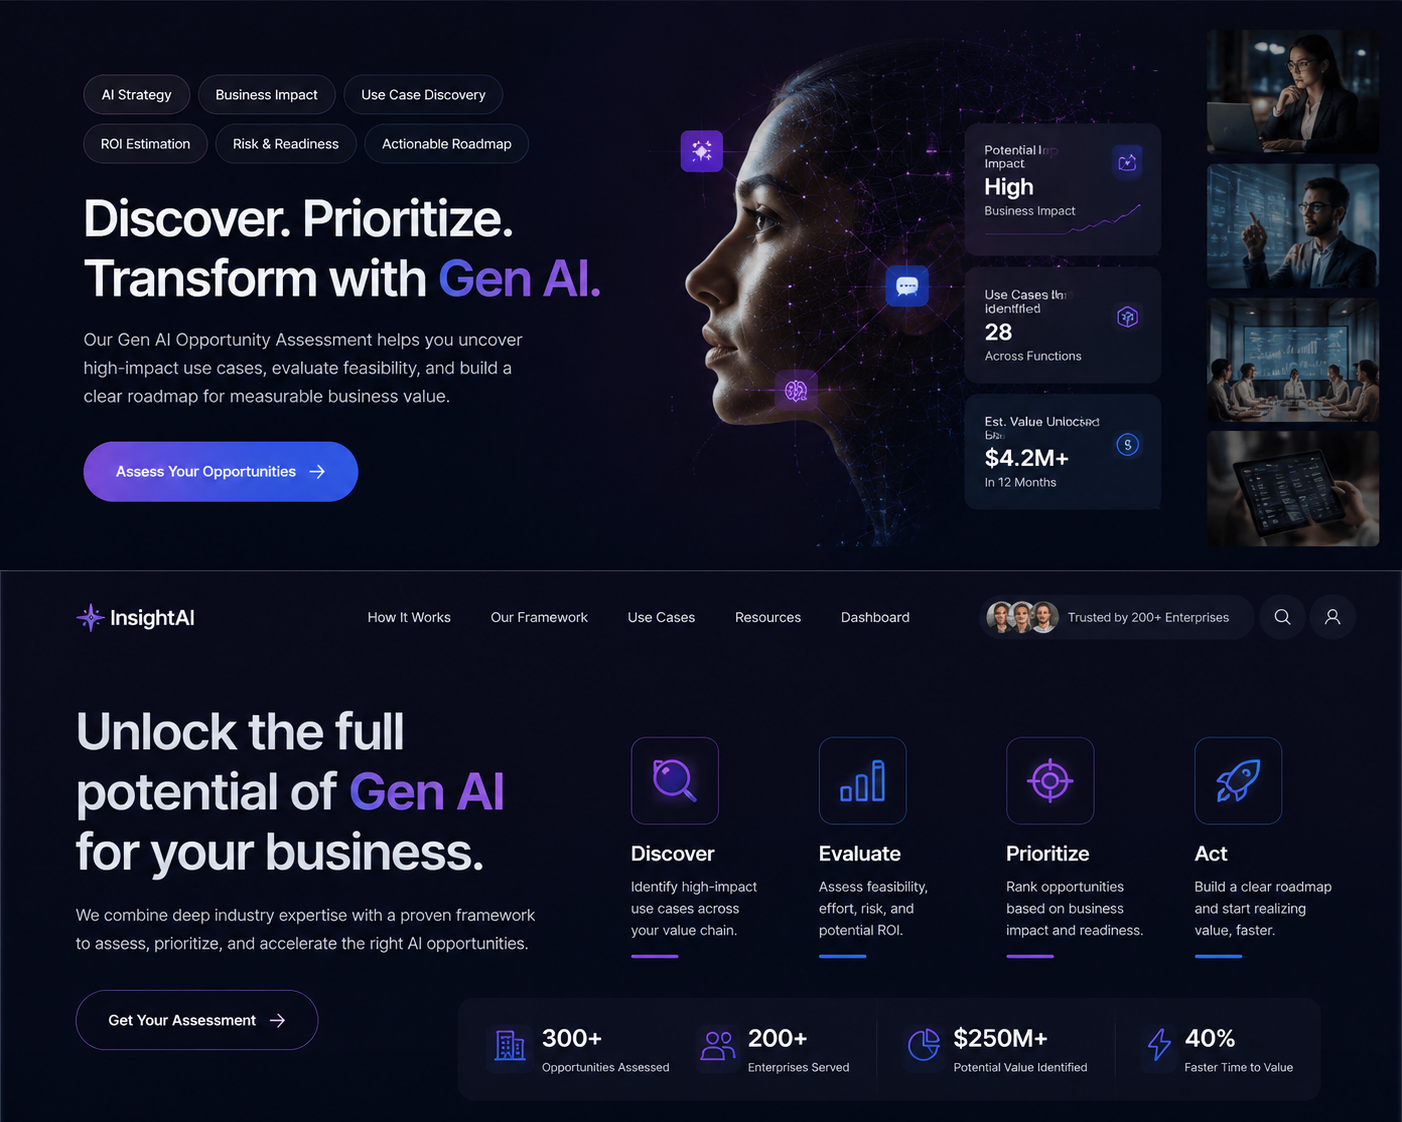
Mapped a £14M annual benefit pipeline across 40 use cases, sequenced by risk.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
We don't compete on lowest day-rate. We compete on shipped outcomes inside environments that have to clear audit.
Every engineer on every engagement is at least senior, typically eight to fifteen years deep in their craft. No bench rotations, no junior pyramid hidden behind a glossy proposal, no bait-and-switch after contract signature. The architect who scoped your engagement is the same person committing code by week three.
FCA, PRA, EBA, BaFin, FINMA, HIPAA, SOC 2 Type II: every framework we work under is treated as a design constraint from day one, not a final-stage gate. Evidence trails, model-risk packs, change-control artefacts, and pen-test reports ship alongside the code, ready for second-line review without a remediation sprint.
Small pods of three to seven engineers, each with a named delivery lead who owns scope, schedule, and outcomes from kickoff to hand-off, never a faceless team you have to chase for an answer. Weekly demos run against the signed scope, frequent verification gates catch regressions early, and quarterly outcome reviews measure real progress against the original business case rather than a moving target. Together those rituals catch scope drift before it has any chance to compound, so programmes that should take six months don't quietly stretch into eighteen, budgets stay anchored to what was agreed, and every milestone ships with a written, testable definition of done that both sides sign off before we move on.
We don't disappear the moment the engagement closes. Managed services, hypercare windows, named on-call rotations, or quarterly health checks: pick the depth that matches your operational risk profile. About seventy percent of clients return for a second programme, usually because the team that shipped the first one is still on the other end of the page.
Anonymous under MNDA. Each quote is from a senior buyer who owned the engagement end to end across the services catalogue.
“BritonOne Technology replaced two of our incumbent vendors with one team. Faster sprints, fewer status meetings, more code shipped per week.”