Problem 01
Hallucination is the wrong risk vocabulary
Regulators don't ask for 'no hallucination'. They ask for every output to be citation-bound and replayable. Most POCs chase benchmark accuracy and never produce the citation trail.
Extract, classify, and route regulated documents, every output citation-bound and replayable, cleared for FCA, PRA, and EU AI Act estates.
From a single policy wording to a forty-year archive, every workload ships with the same citation-bound, replayable evidence trail. Start with the document that's costing you most.
The highest-value GenAI surface in regulated firms, and the one with the most consistent failure rate across banks, insurers, and wealth platforms.
Compliance is not a model feature. It's an end-to-end system.
The technology works. The systems around it don't.
Regulators don't ask for 'no hallucination'. They ask for every output to be citation-bound and replayable. Most POCs chase benchmark accuracy and never produce the citation trail.
Forty years of scanned PDFs, handwritten claims margins, policy wordings in fourteen versions. POCs run on cleaned subsets; production meets the real corpus and stalls.
Underwriters re-read every contract anyway; loss-adjusters re-read every wording. The AI becomes overhead, not leverage, and the business case collapses.
Six months on, the supervisor asks why the model classified a contract that way. The team can't reconstruct the reasoning, the corpus version, or the model card, and confidence collapses.
Not features: outcomes a head of underwriting, claims, or compliance can defend in the room.
Each extracted fact, classification, and routing decision is bound to a source document, page, and chunk, and replayable on demand. “Why did the model decide this?” has a 60-second answer, not a forensic project.
Domain experts stop re-keying and start deciding. 60–70% of extractions auto-route; only medium-risk and exceptions reach a human, and every override sharpens the next quarter's model.
Forty years of scanned PDFs, handwritten claims margins, and policy wordings in fourteen versions, not a cleaned demo subset. 94% top-1 accuracy on the production corpus, against 78% for a tuned-rules baseline.
Regulator evidence is engineering output, not a final-stage scramble. Every build ships the EU AI Act Annex IV pack, 2LoD-approved model cards, and an on-prem sovereign fallback for data that can't leave the estate.
Not features, but four reasons a head of underwriting, claims, or compliance can defend in the room.
FCA, PRA & EU AI Act evidence ships as engineering output, not a final-stage compliance scramble.
Every output is citation-bound to its source and page, and replayable in under 60 seconds.
A phased path from demo to 2LoD-approved production, de-risked at every gate.
60–70% of outputs auto-route; your specialists judge the exceptions, not the data entry.
Five stages, each with a bounded output you can hold us to. No black-box sprints, no big-bang launch: working software and the evidence trail, in step.
We map the problem, the constraints, and the regulatory surface, then commit to a bounded scope and a costed plan, not an open-ended retainer.
Architecture, data flows, and a written threat model, signed off with your security and second-line leads before a line of production code ships.
Working software each sprint, behind feature flags, with tests and CI gates from commit one. You see progress you can run, not a status deck.
Pen-test, audit trails, runbooks, and the documentation pack a regulator asks for, produced as engineering output, not a final-stage scramble.
Run in shadow against live traffic, clear second-line and regulator review, then a documented handover, or a bounded retainer if you'd rather we stay.
Success stories
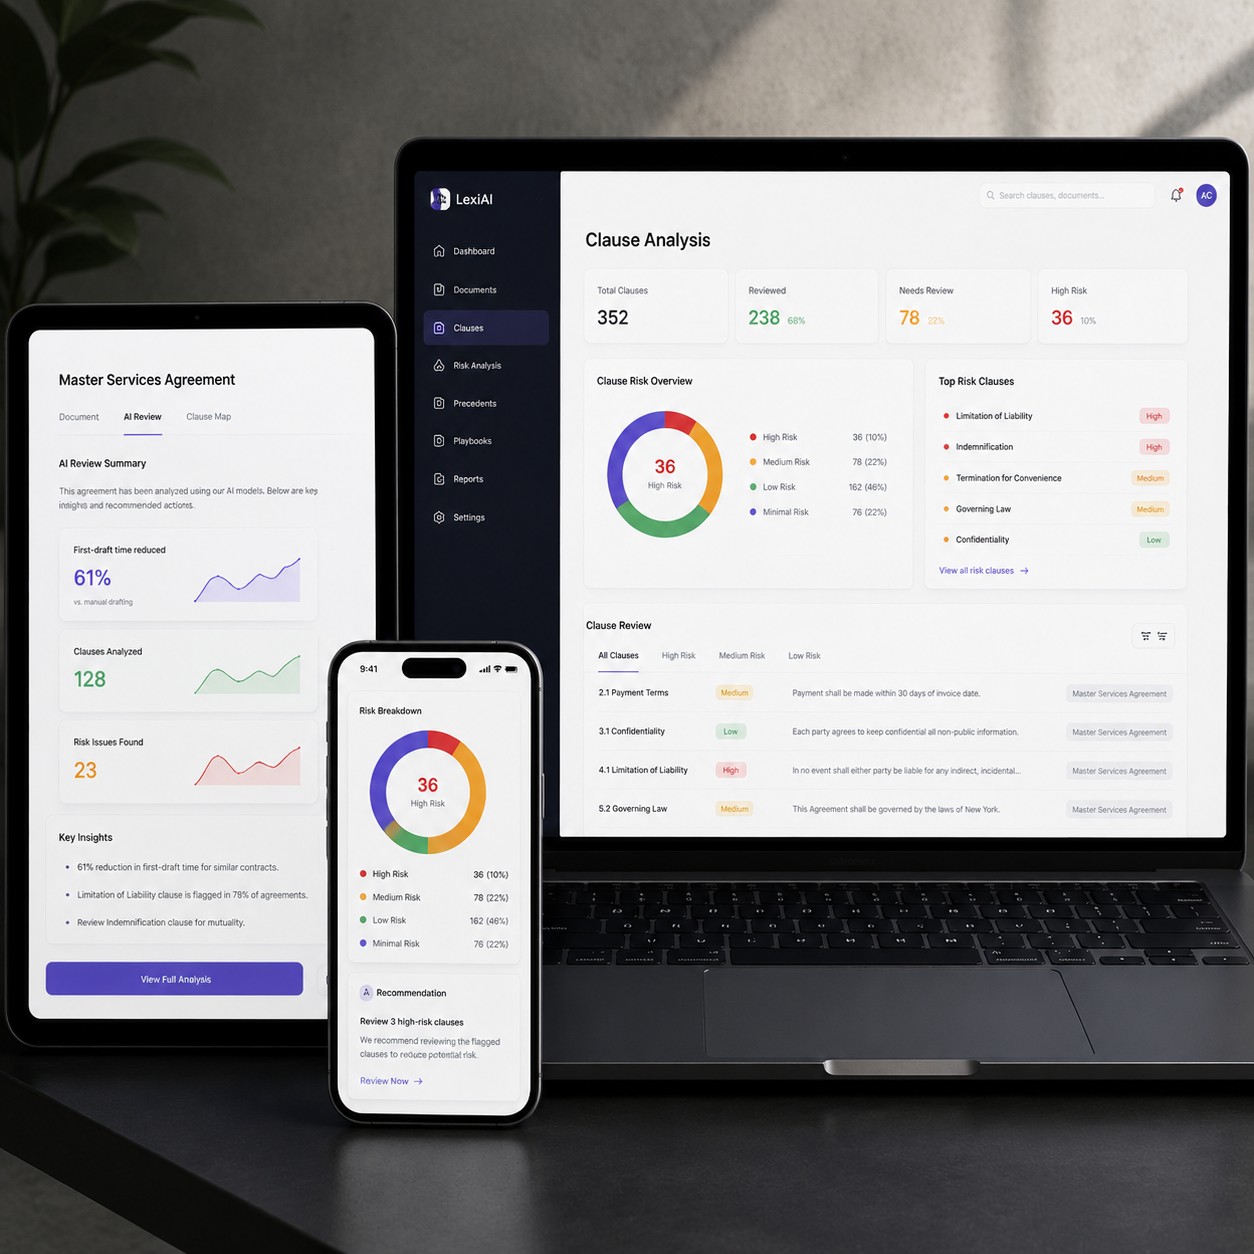
Cut first-draft time on regulated commercial contracts by 61%, each clause traceable to firm precedent.
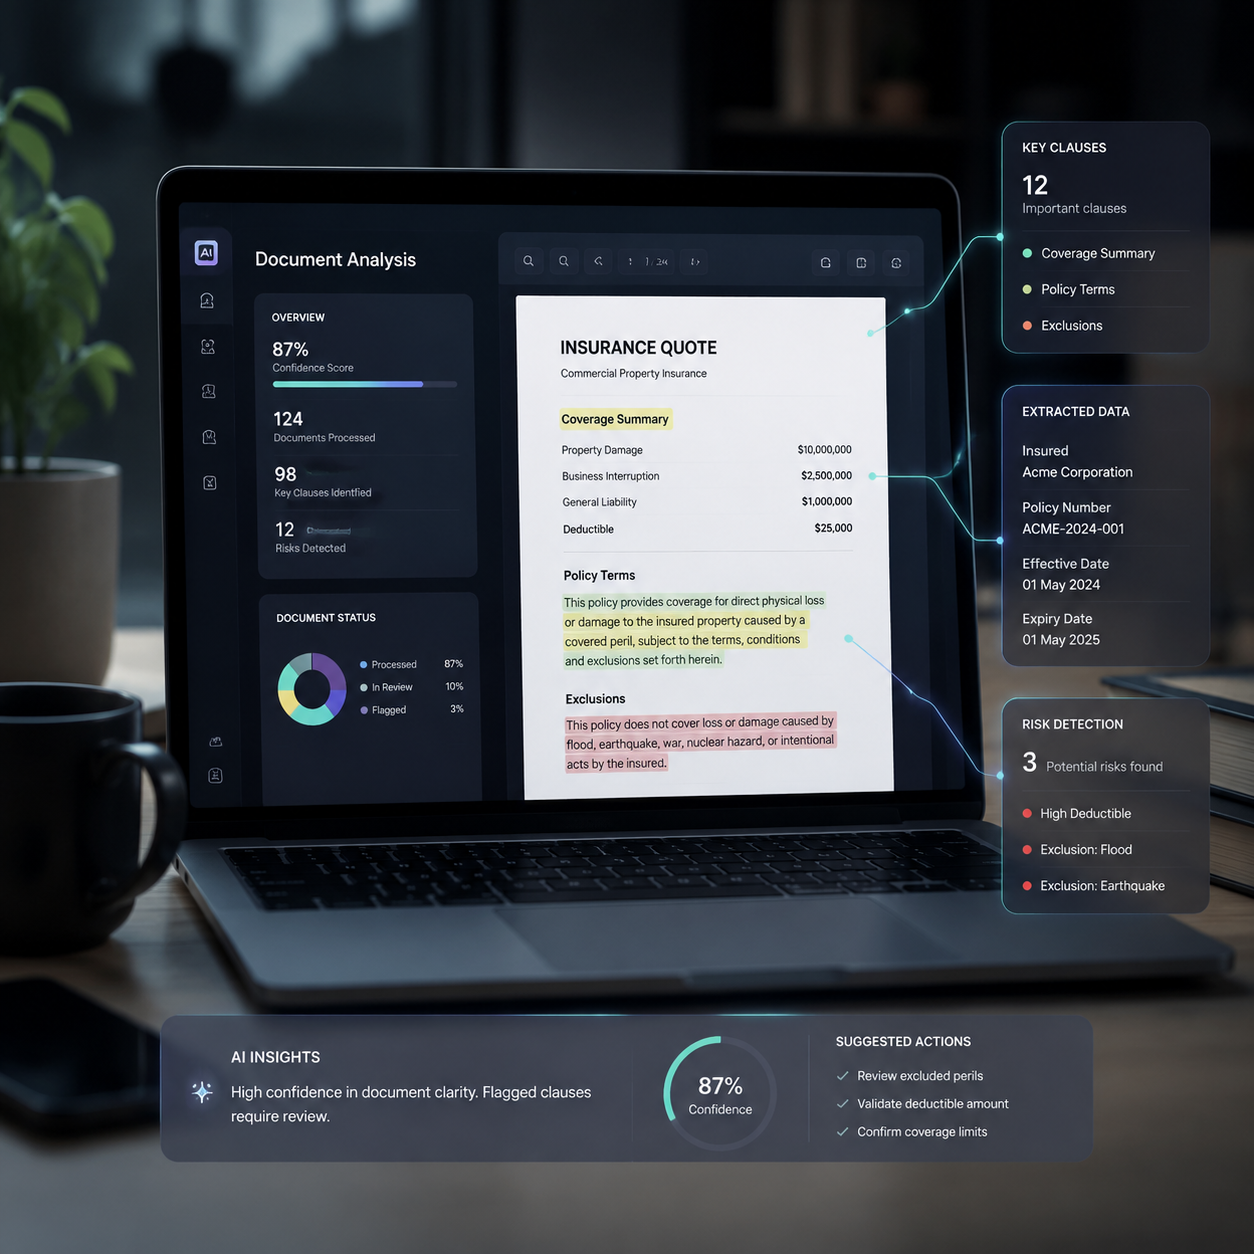
Drafted first-pass quotes from submission packs 3.1x faster, every clause cited back to the wording it came from.
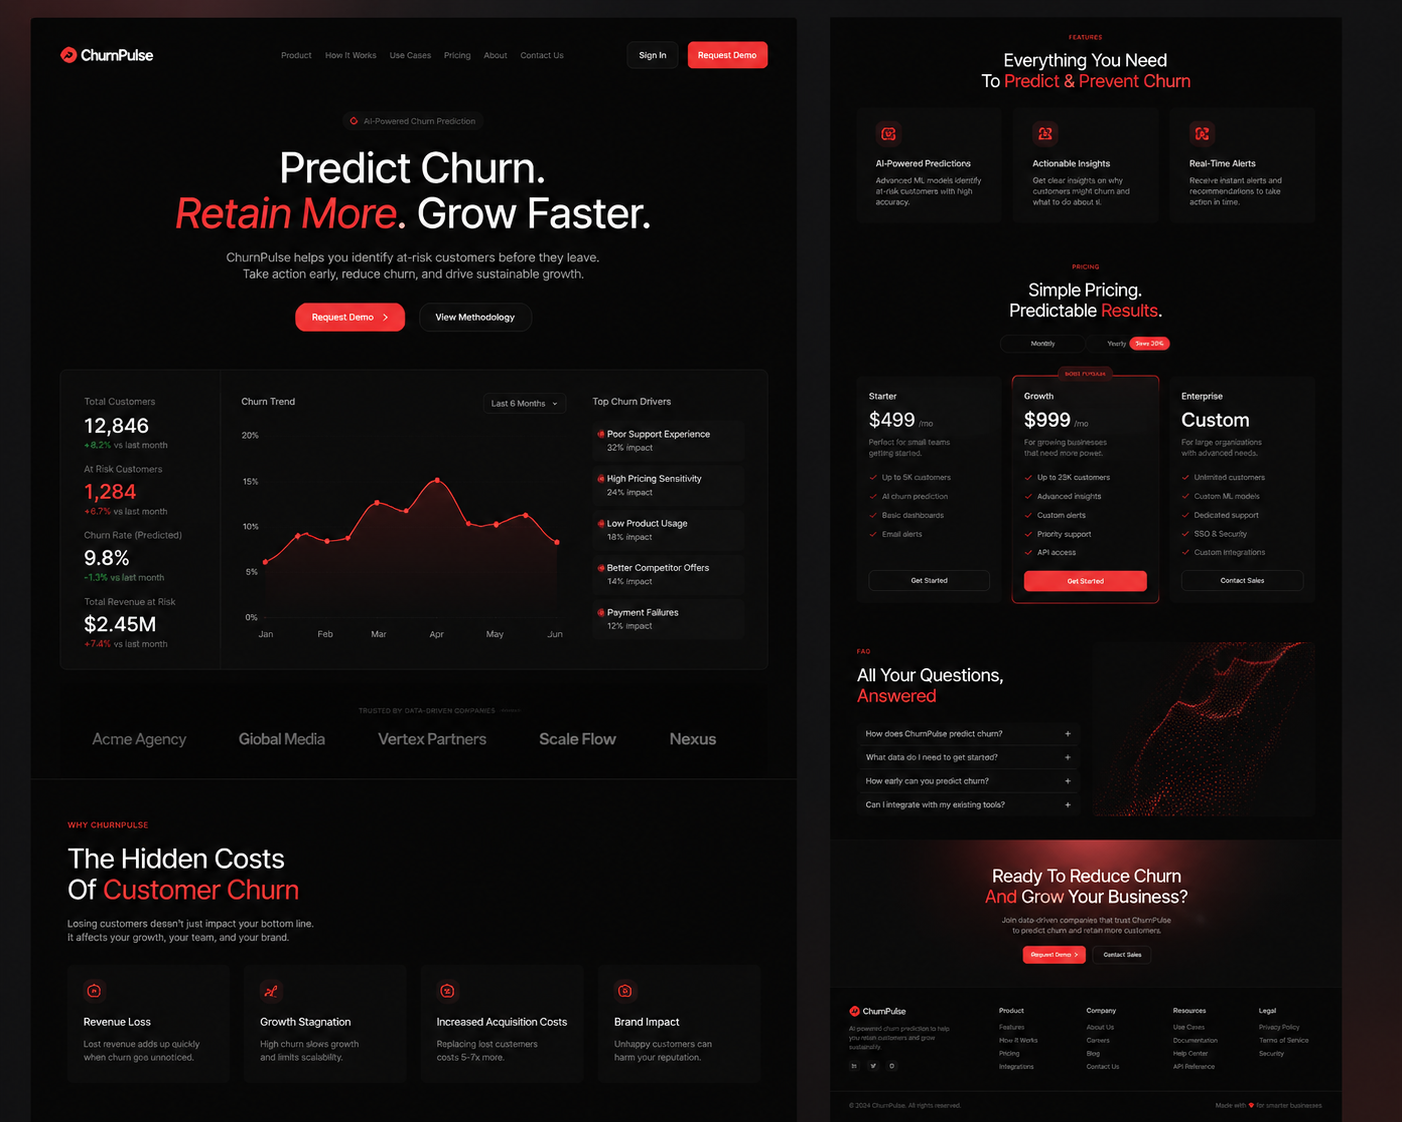
Cut voluntary churn 18% in two quarters with next-best-action scoring for a meal-subscription platform.
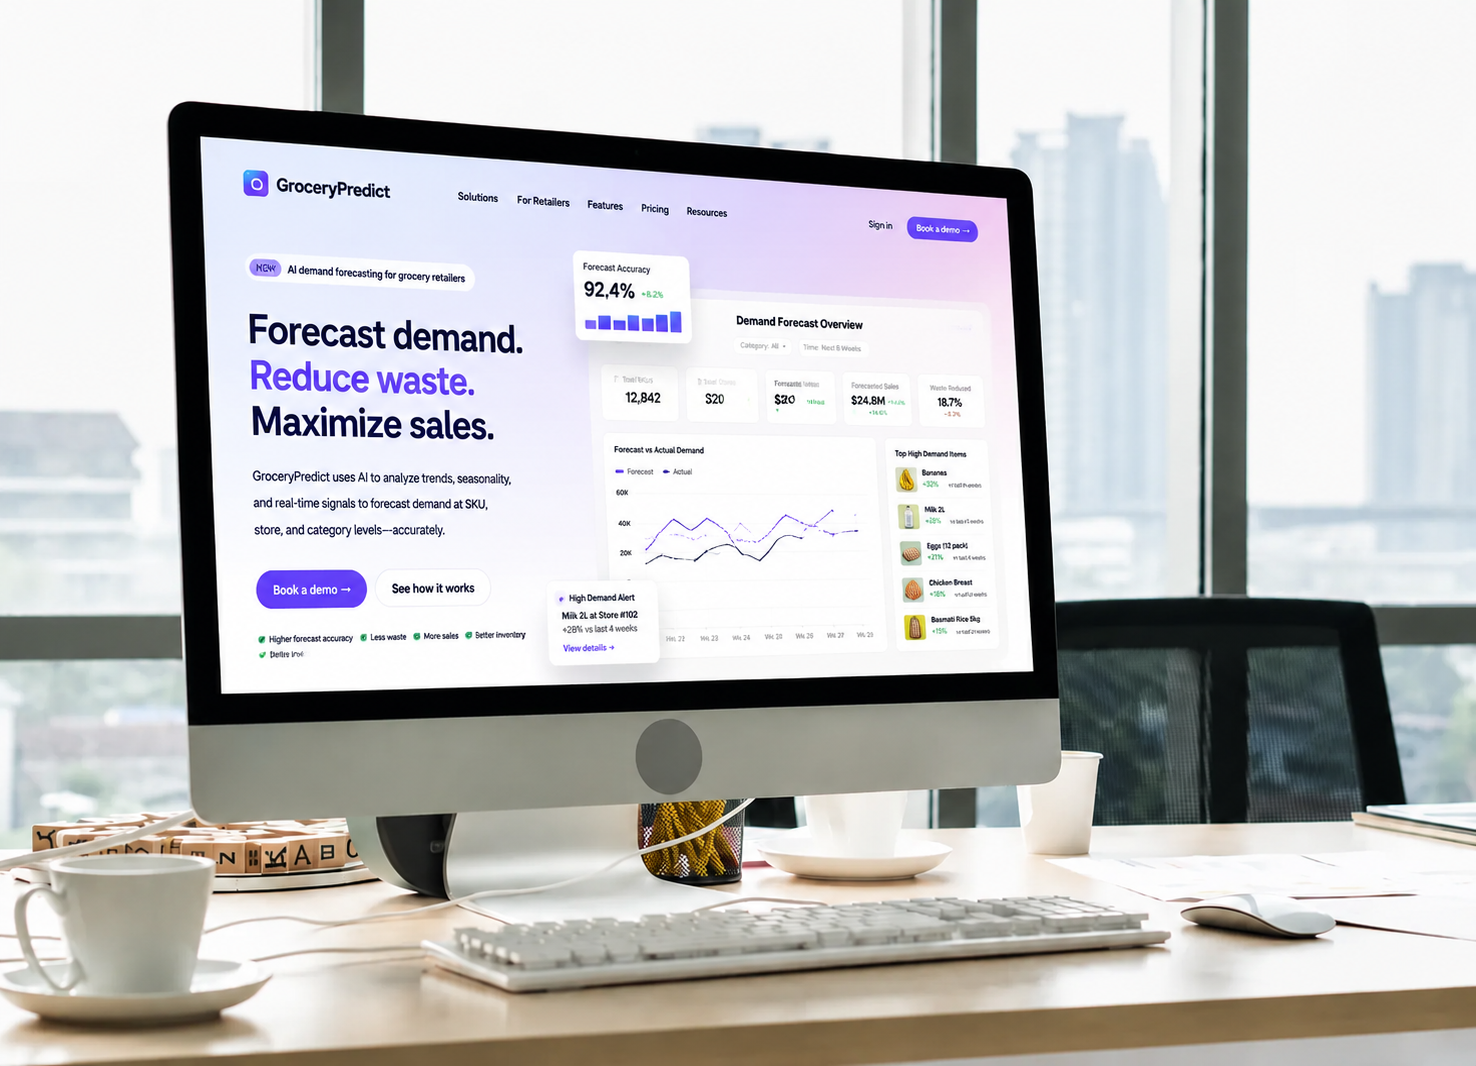
Cut waste 22% across 900 stores with SKU-level probabilistic forecasts.
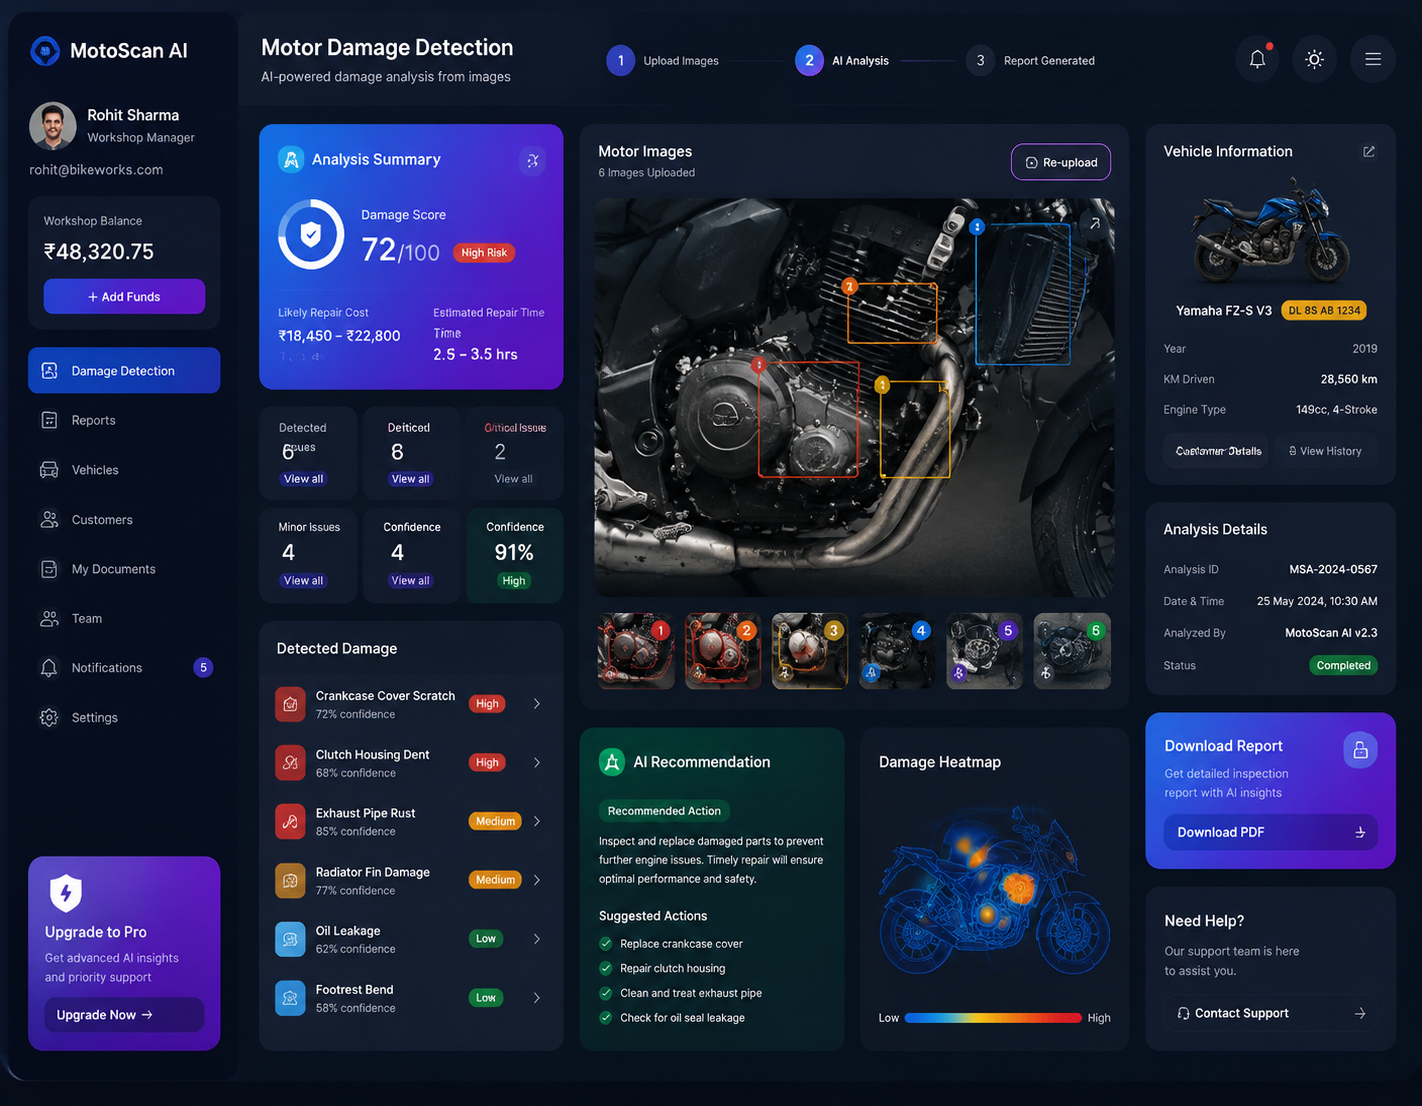
Settled 47% of motor claims from images alone, with fraud flags surfaced inline.
Mapped a £14M annual benefit pipeline across 40 use cases, sequenced by risk.
Replaced a 15-year-old claims system, tripling throughput per handler.
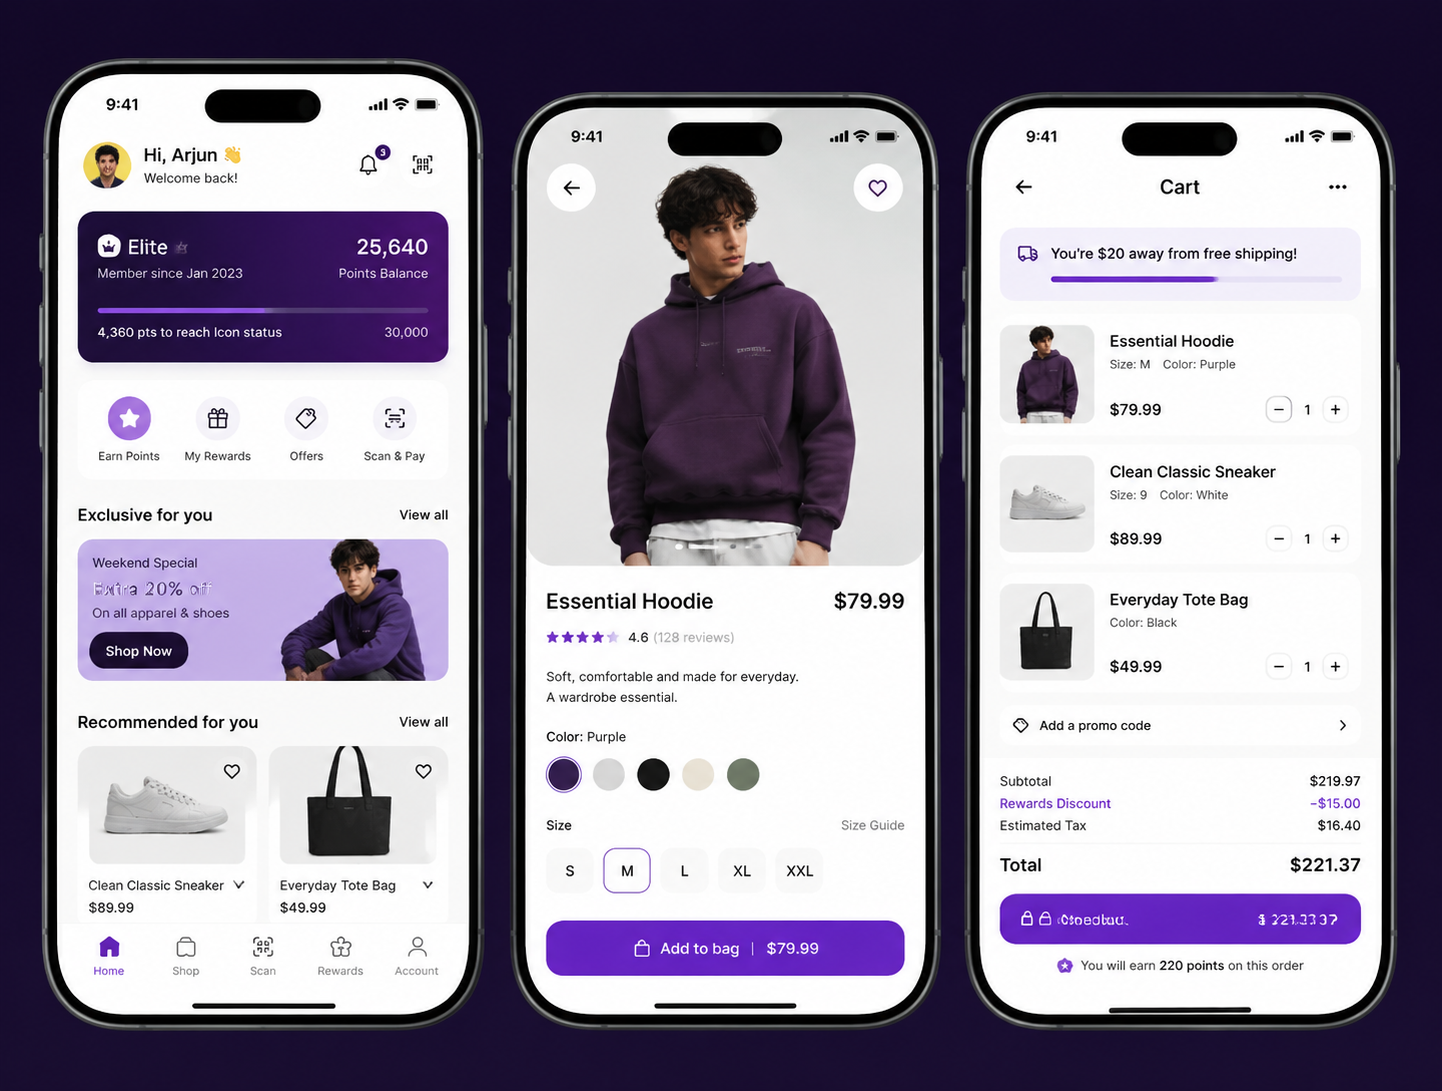
Launched a retail loyalty app to a 4.8-star rating and 200k users in 90 days.
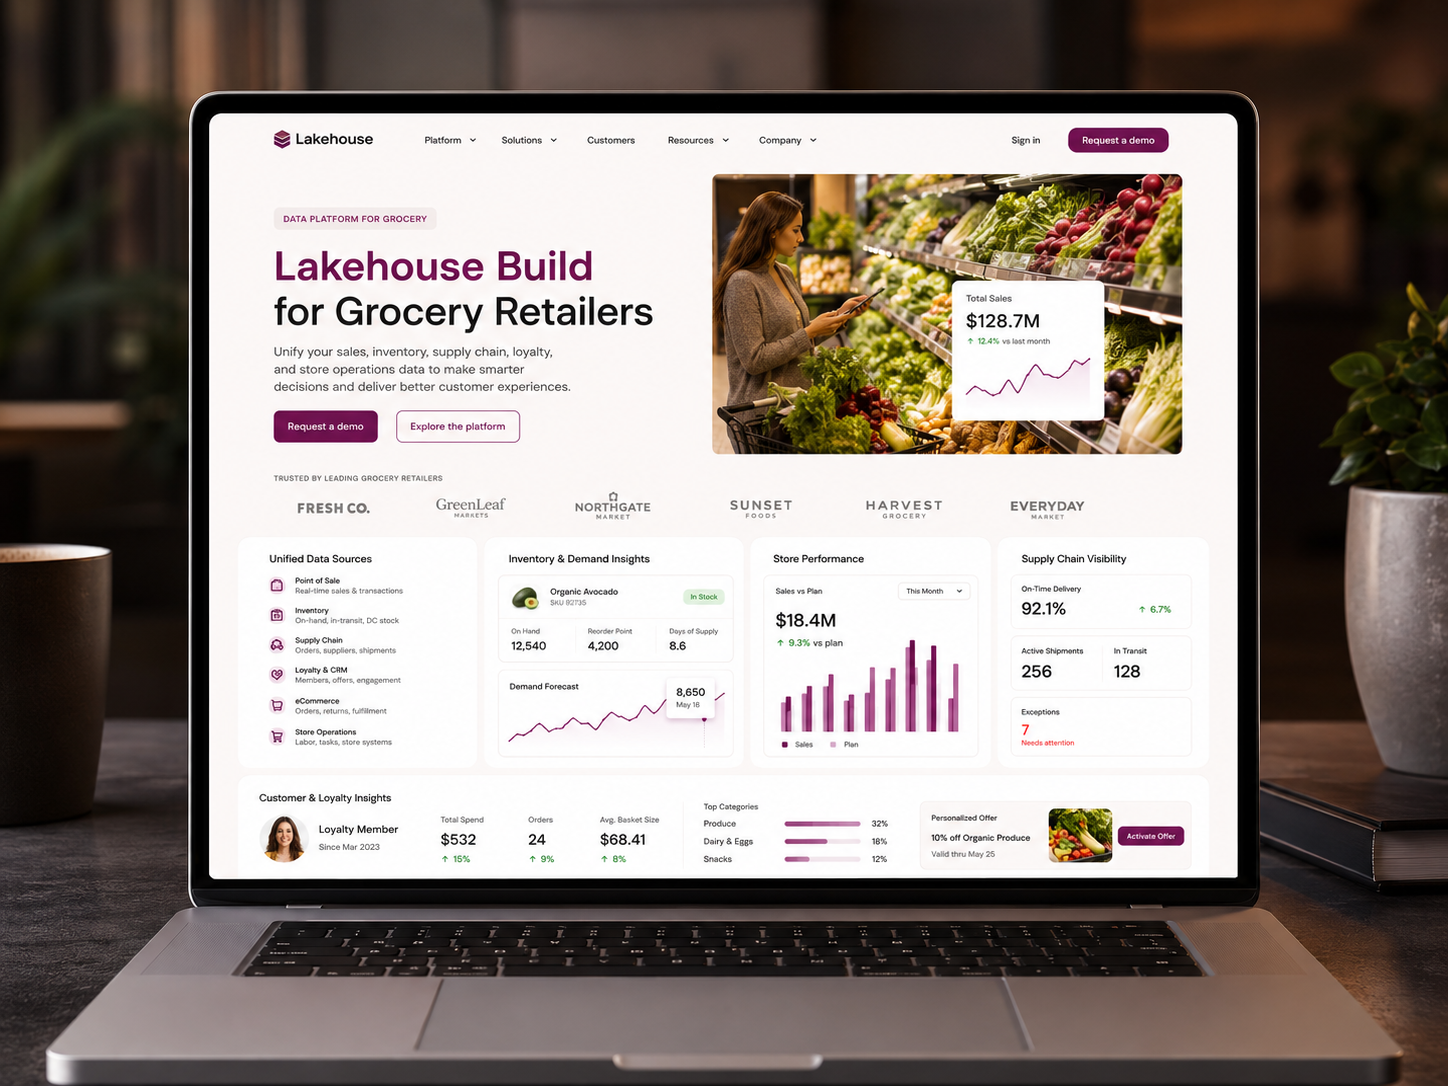
Unified 40 sources into a governed lakehouse, cutting report build time 60% for a grocery retailer.
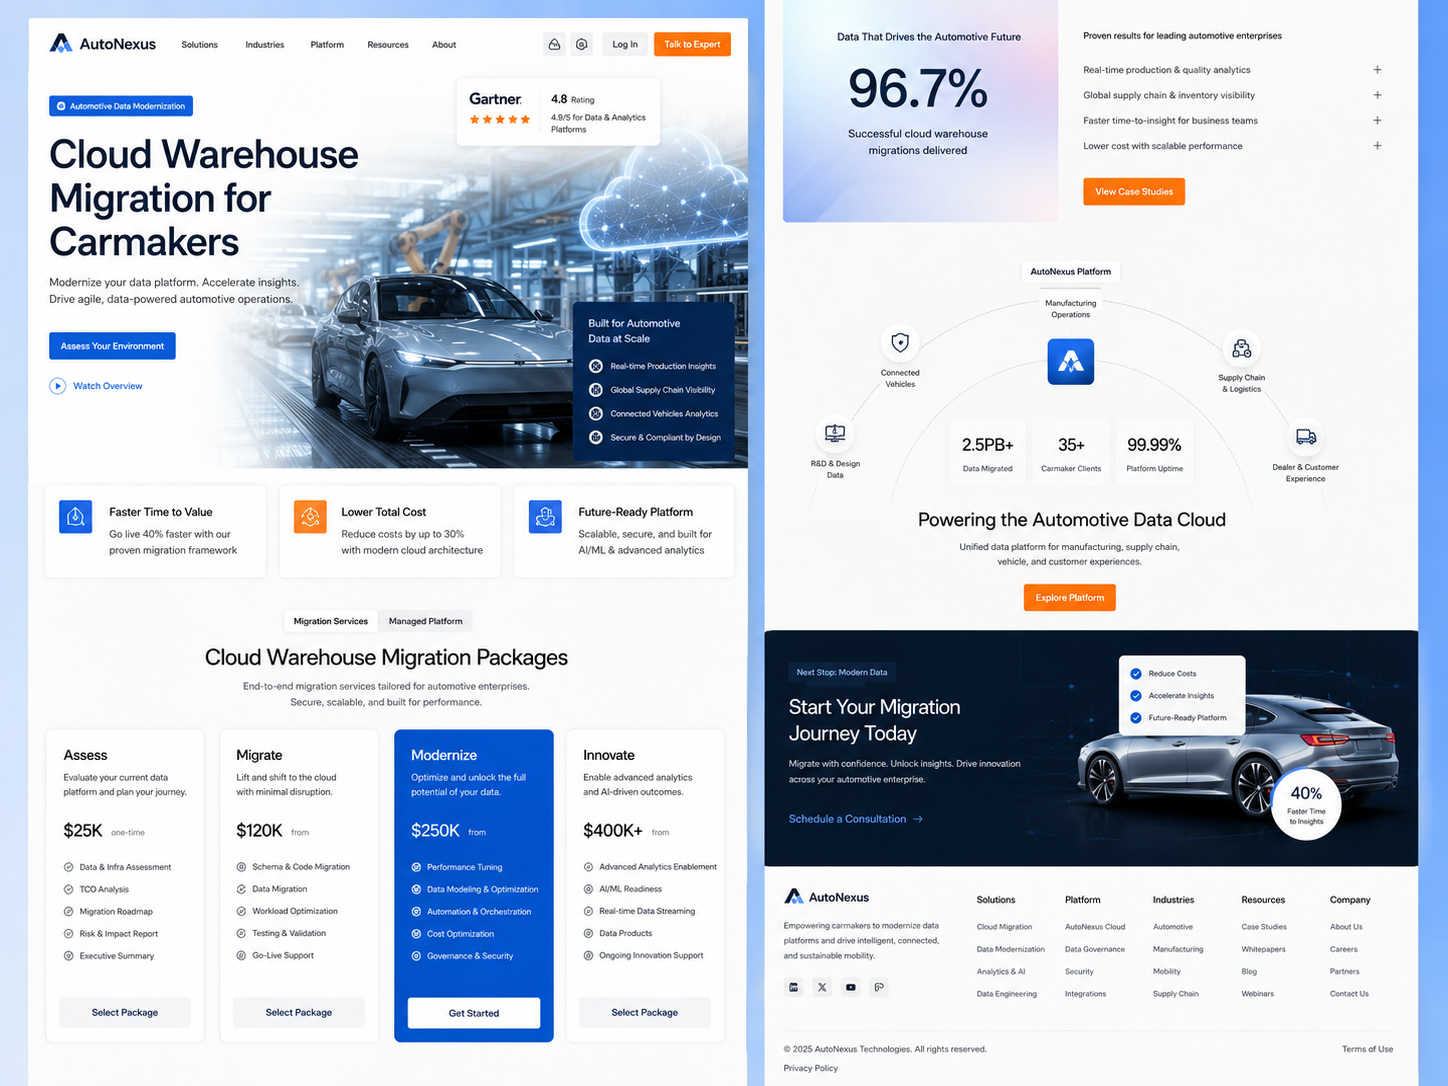
Migrated a legacy warehouse to the cloud, cutting query cost 45% for a carmaker.
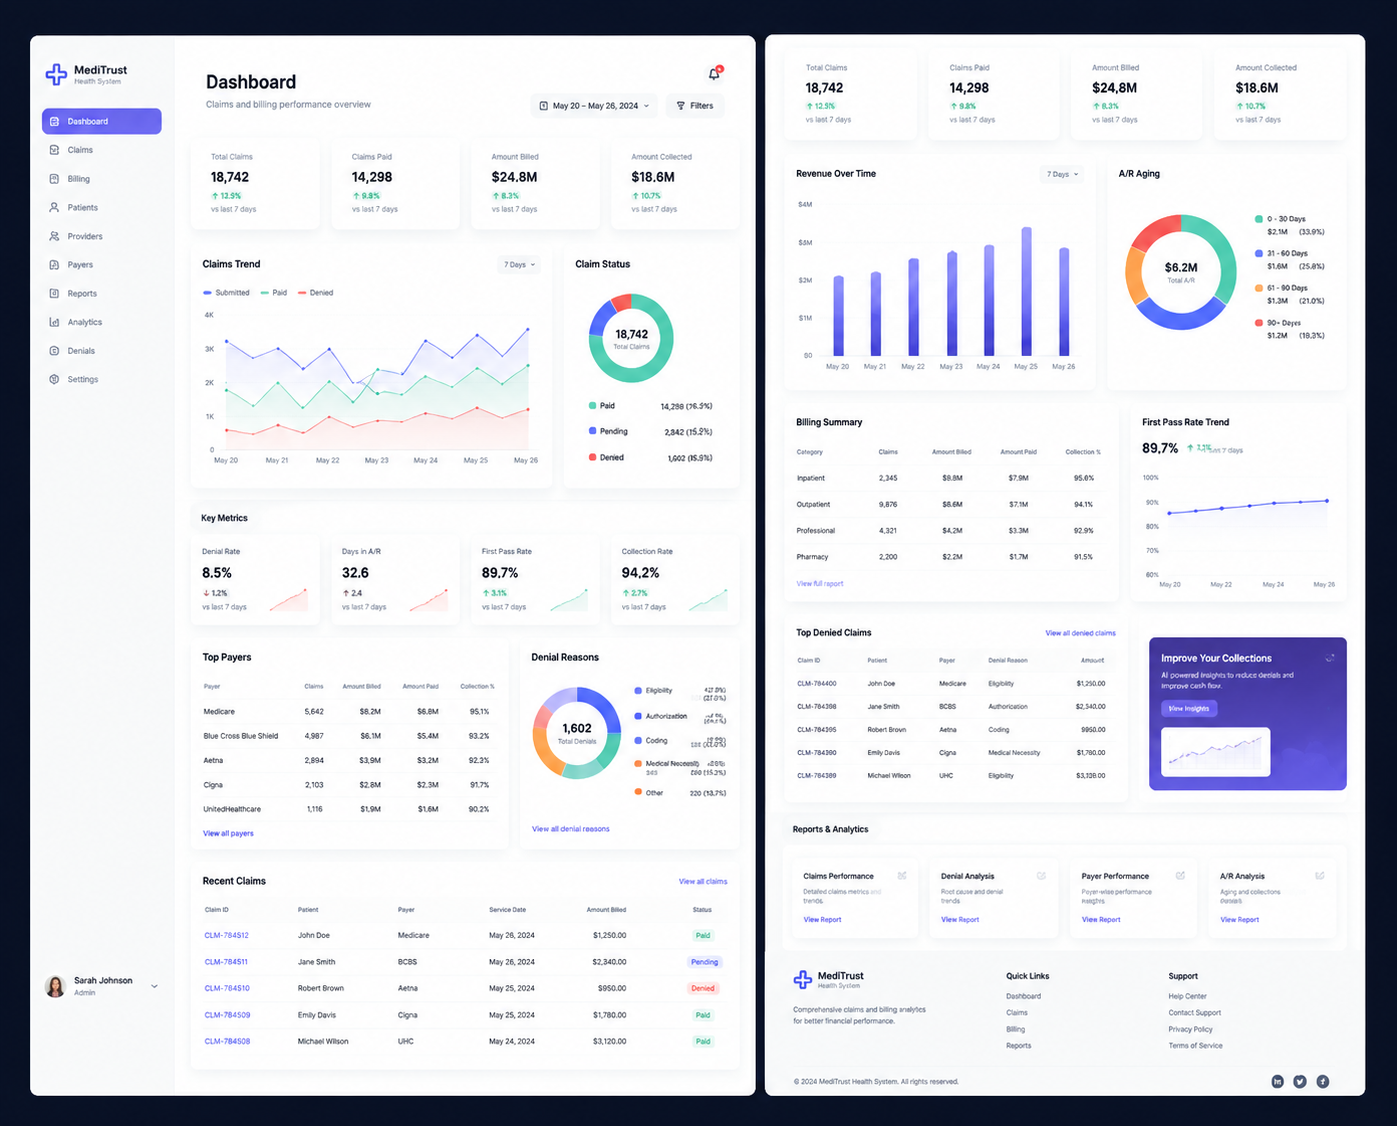
Unified claims and billing data, cutting rejected-claim rework 38% for a hospital group.
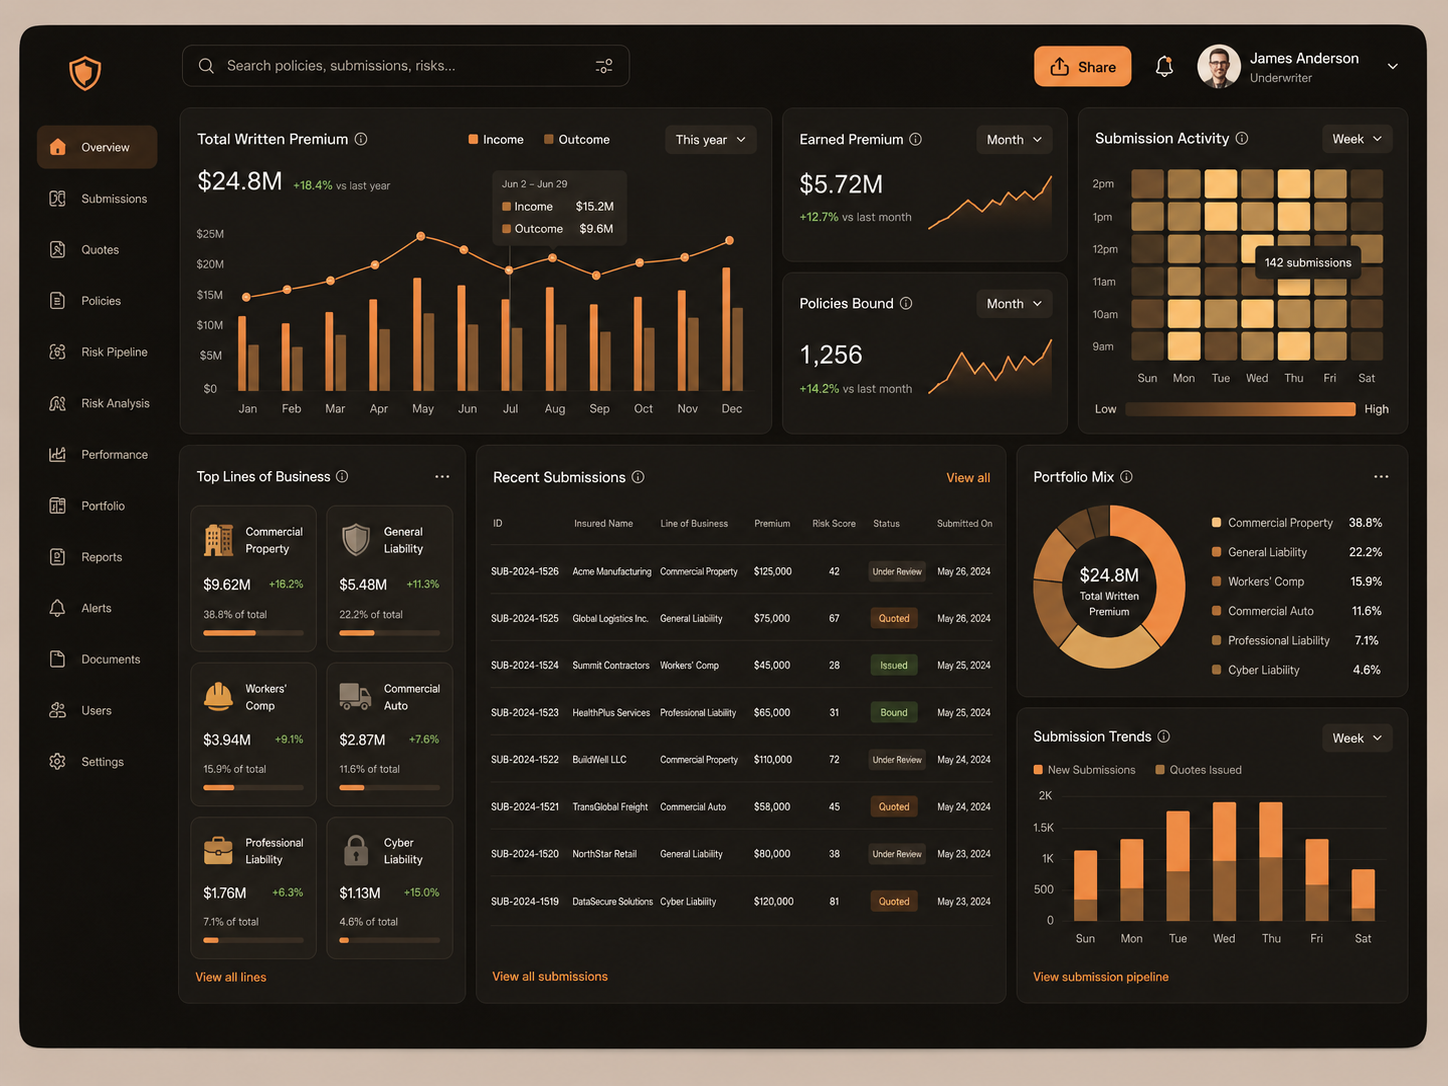
Replaced 60 spreadsheets with one governed underwriting board pack for an insurer.
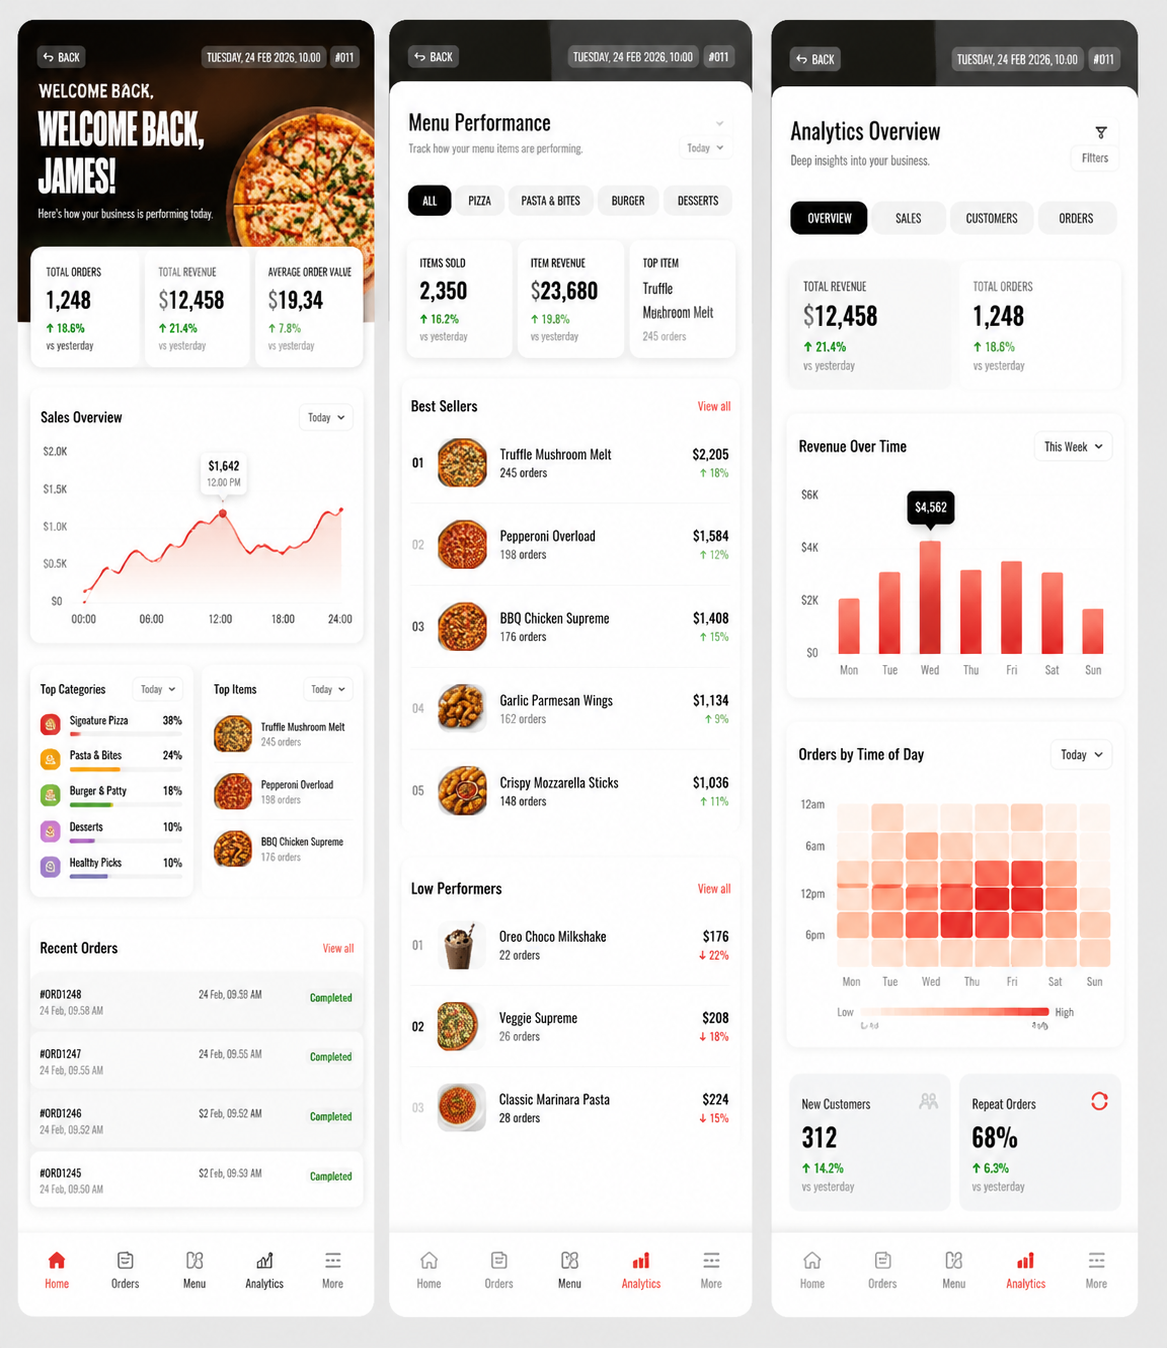
Self-service models tripled analyst throughput at a food-delivery platform.
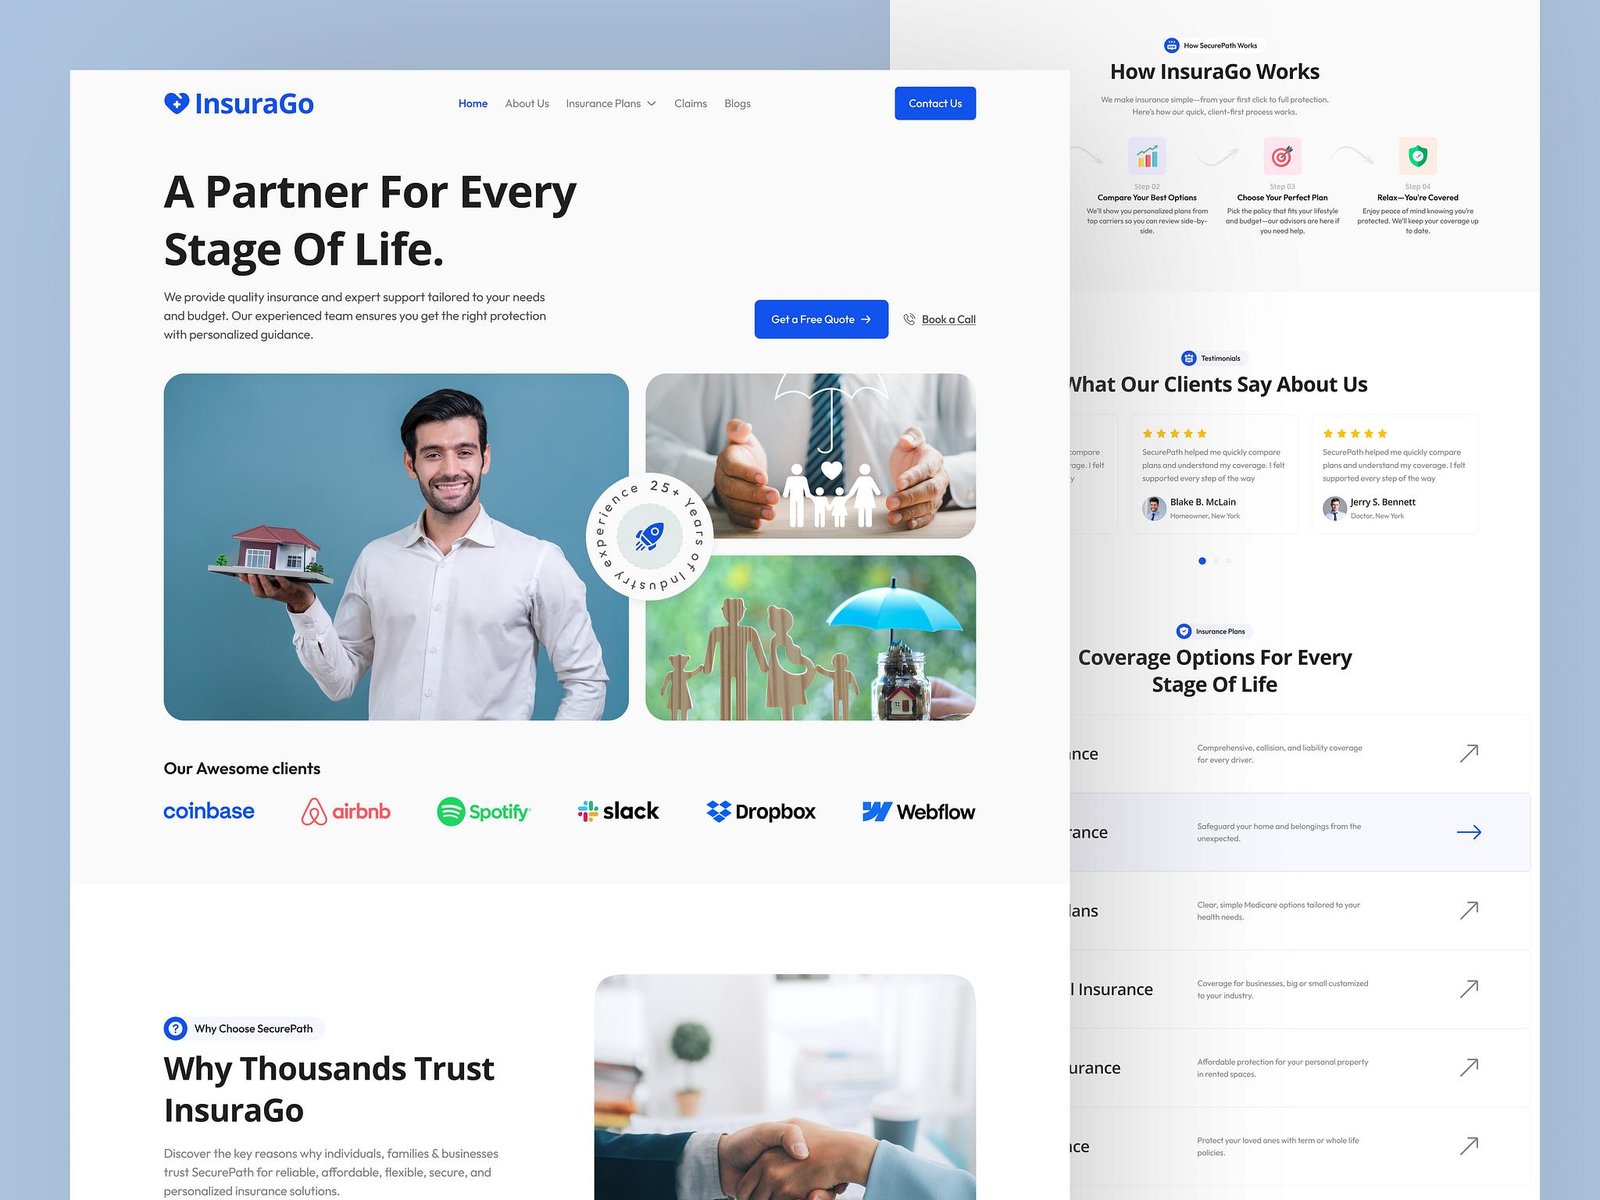
Automated quote, coverage, and claims journeys for a US insurer, holding 100% of critical paths green across a fast release train.
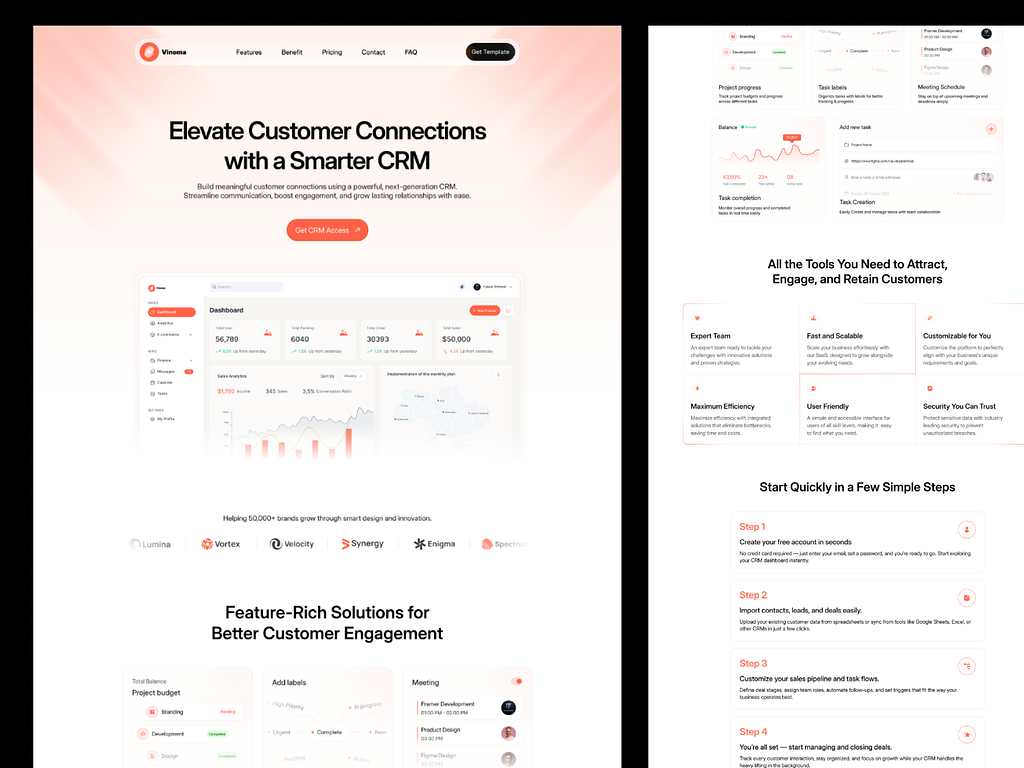
Exploratory and regression testing across pipelines, analytics, and customer records surfaced more than thirty edge-case defects that scripted suites had missed, hardening a German fintech's CRM before a major rollout.
Kept p95 latency flat as audience data and concurrency scaled, proving the analytics dashboards would not slow as customers grew.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
Anonymised under MNDA, verifiable on reference call. Each quote is from a senior owner who carried the engagement through second-line review.
“We had run three internal POCs on policy-extraction over two years. They all stalled at second-line risk review. BritonOne Technology built the citation-bound pipeline in eleven weeks; the FCA review accepted it on first submission. Twelve months later, 64% of policy extractions auto-route; the underwriting team is doing the judgement calls, not the data entry.”