Round-the-clock monitoring
Our analysts watch your systems day and night, catch real threats early, and cut the noise so nothing important slips through.
24×7 monitoring, fast incident response, and audit-ready evidence, built for FCA- and PRA-regulated banks and insurers. We surface real threats sooner, cut the alert noise, and keep the proof your supervisors expect ready before they ask.
Round-the-clock monitoring, a fast response when it matters, and the proof your regulators ask for, joined up into one service.
Our analysts watch your systems day and night, catch real threats early, and cut the noise so nothing important slips through.
When something goes wrong, a clear plan takes over: we contain the threat, keep your key services running, and guide every step.
We build and keep updating the rules that spot attacks on your own systems, so new tricks don't get past unnoticed.
Every alert and action is logged as it happens, so the proof your supervisors want is ready the moment they ask.
It adds up to one thing: threats caught and contained before they reach the services your customers rely on.
Most regulated firms already run a SOC. The trouble is how the older ones were built: reactive, noisy, and slow to prove what actually happened.
Older setups fire thousands of alerts a day. The signals that matter get buried, and a real attack can run for over a week before anyone spots it.
Rules written years ago miss today's attacks. Stolen logins, cloud mistakes, and supply-chain tricks walk straight past them.
When a regulator asks what happened months ago, the old team rebuilds the story from chat logs and memory, and confidence drains away.
What changes for your firm once detection and response run as one service.
 Always-on cover
 Threats caught early
 Faster containment
 Less alert noise
 Audit-ready proof
 Detection tuned to you
Threat detection for supervised banks and insurers is the work we do most. Every reason here is one a reference will back on a call.
The person in your supervisor meeting is the one who designed your detection. PRA SS2/21 and operational resilience are built in from day one, not bolted on before an audit.
We work in your AWS, Azure, or GCP: your keys, your access. No security data is copied out, and there are no shadow systems holding your logs.
Detection coverage, incident records, and the supervisor pack are produced at every step, never scrambled together the week before a review.
Detection, response, and rehearsals come from one experienced team that stays with you: no junior handoffs, no revolving door, cover day and night.
A clear, staged path from first look to round-the-clock cover, and every stage leaves proof behind.
We learn your systems, your critical services, and the impact limits you have to stay inside.
We write detection rules tuned to your own identity, cloud, and endpoints, mapped to MITRE ATT&CK.
Telemetry, SIEM, and response playbooks are joined into one clean detection plane.
We run severe-but-plausible drills (credential theft, ransomware) and tune from what we learn.
Round-the-clock cover begins, with a supervisor-ready evidence pack from day one.
Success stories
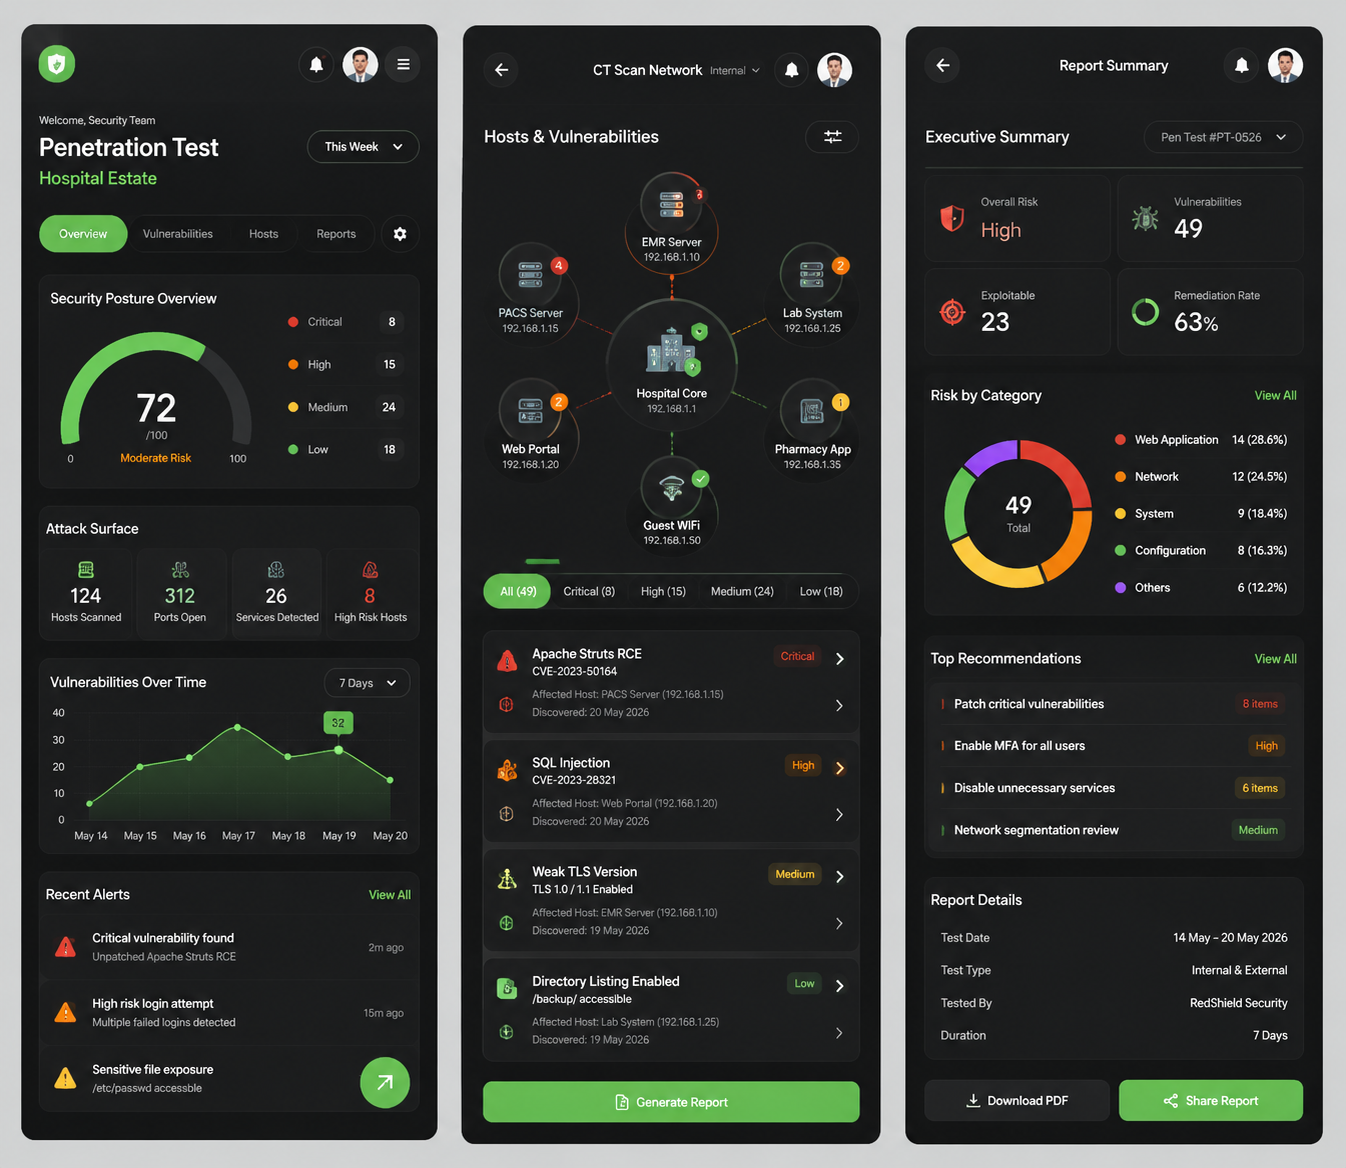
Surfaced 61 exploitable paths across a hospital estate, prioritised by patient-safety impact.
Rolled zero-trust access to 25,000 civil servants without a productivity dip.
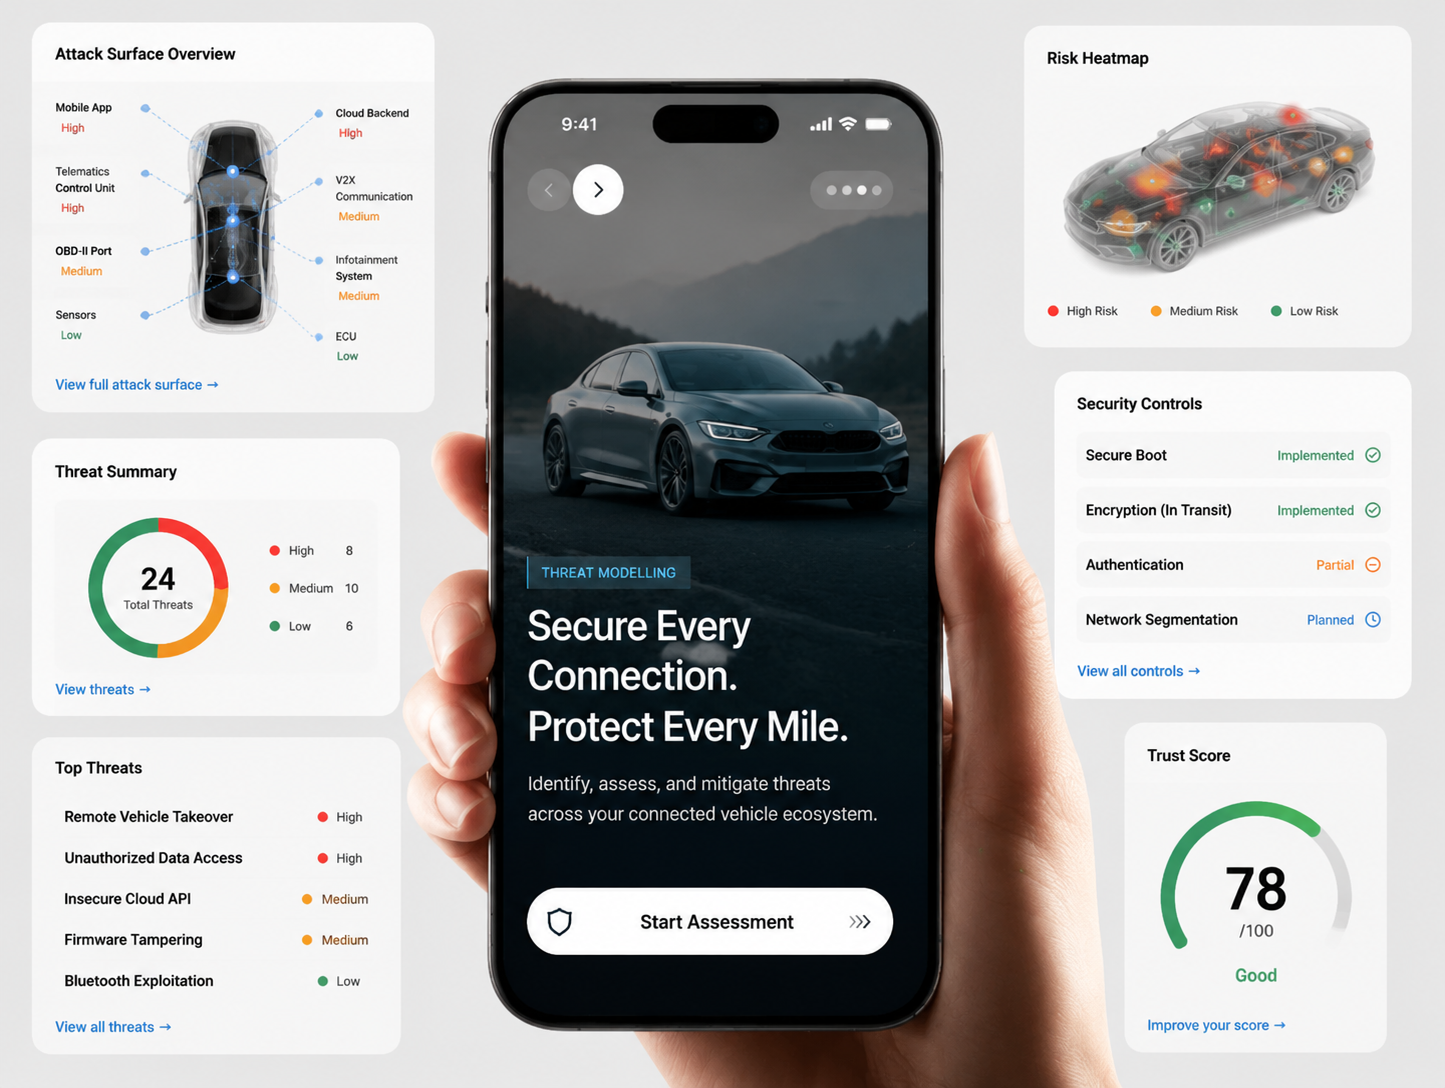
Mapped and mitigated attack paths for a UNECE R155-regulated connected vehicle.
Cut median incident remediation from 41 to 7 minutes across a manufacturer's OT platform, with a human approval gate on every action.
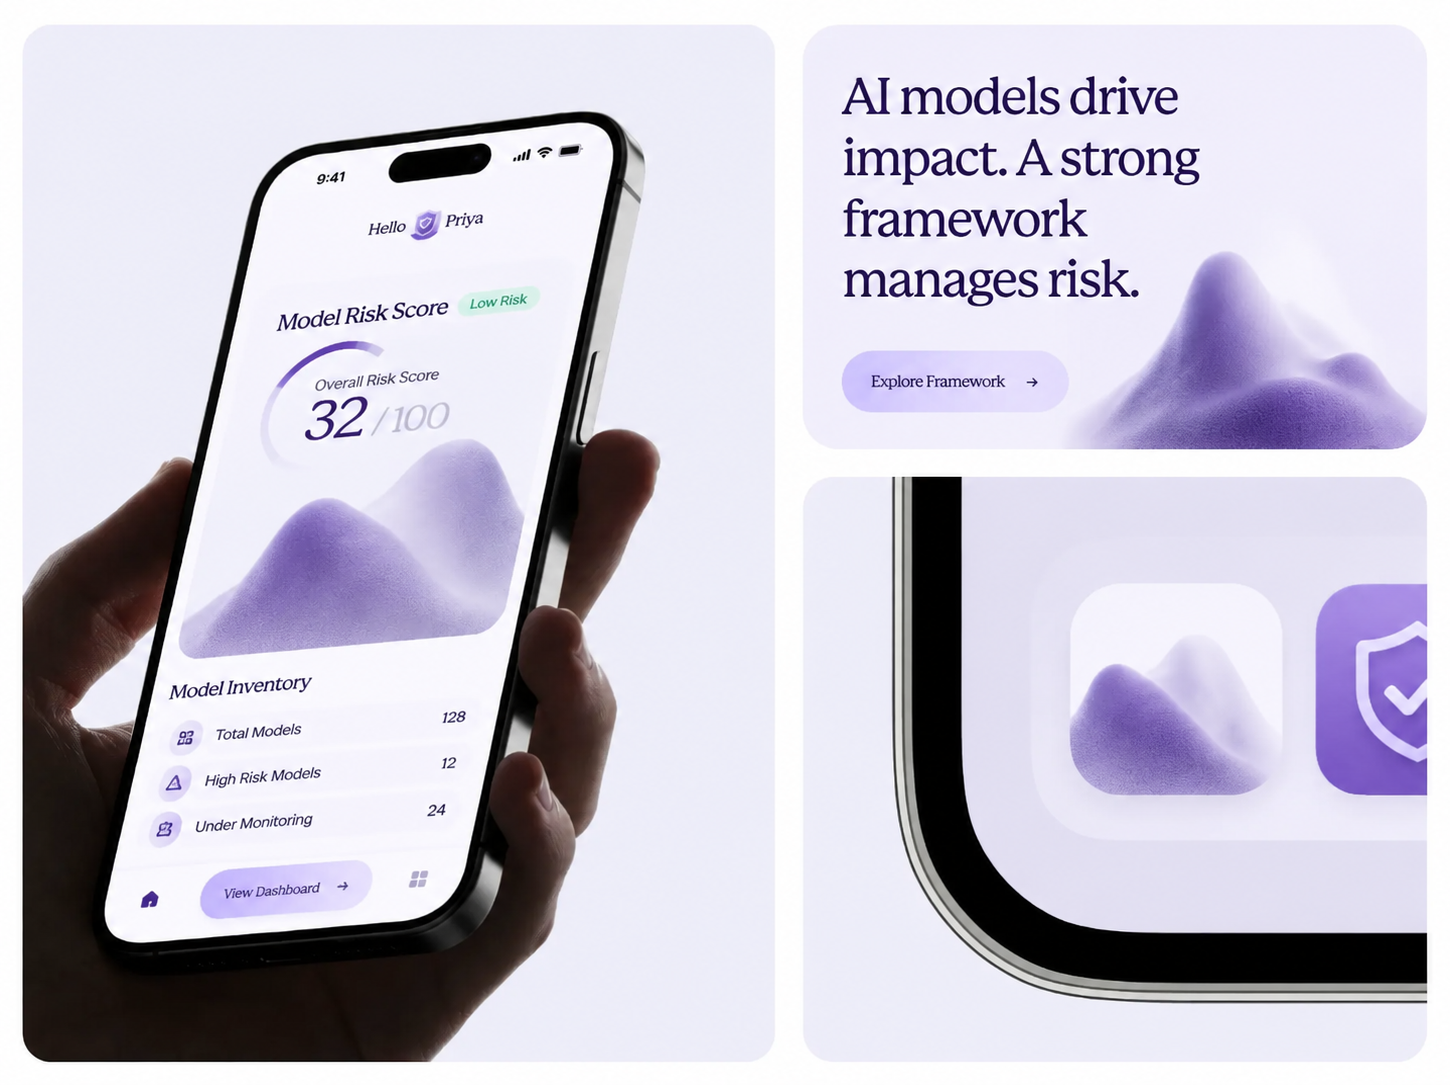
Stood up a board-ready AI governance and model-risk framework for a pharma company in 9 weeks, cleared at first internal audit.
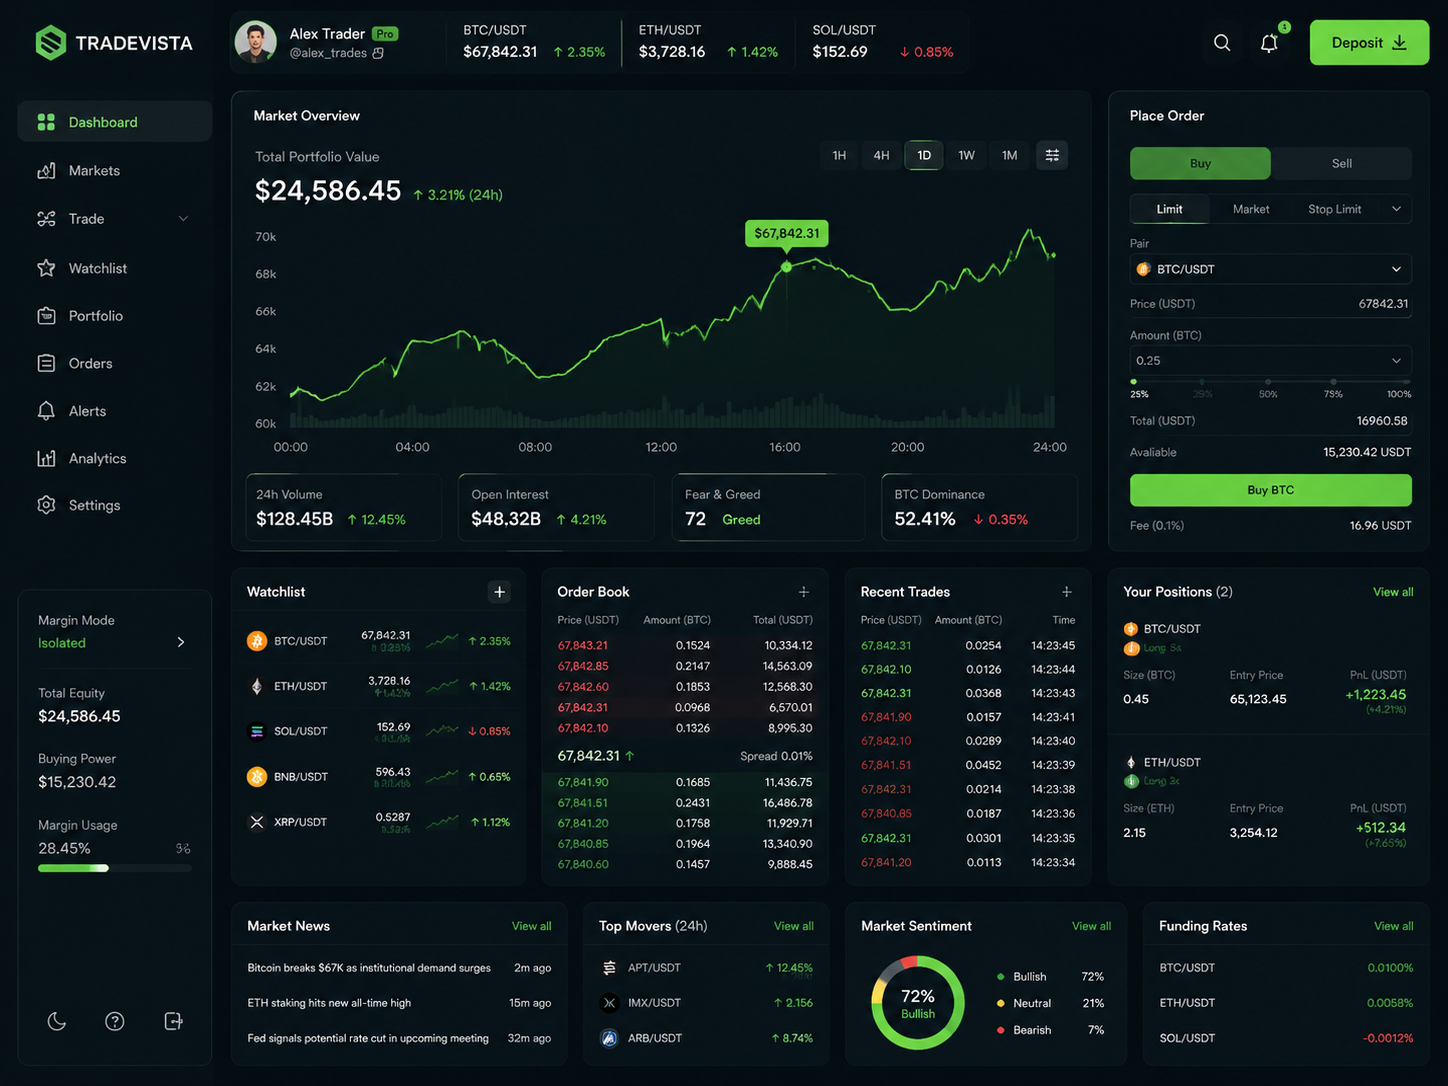
Sub-120ms streaming operations dashboard across 40 control desks for a logistics operator.
Offline-first engineer app cut job-completion admin 31% for a manufacturer's field team.
Migrated 900 clinical workloads off two datacentres to the cloud with zero downtime on patient-facing systems.
Stood up a compliant, multi-account landing zone for a government department in 7 weeks.
Delivered validated, GxP-compliant CI/CD, cutting release lead time 8x with full audit evidence.
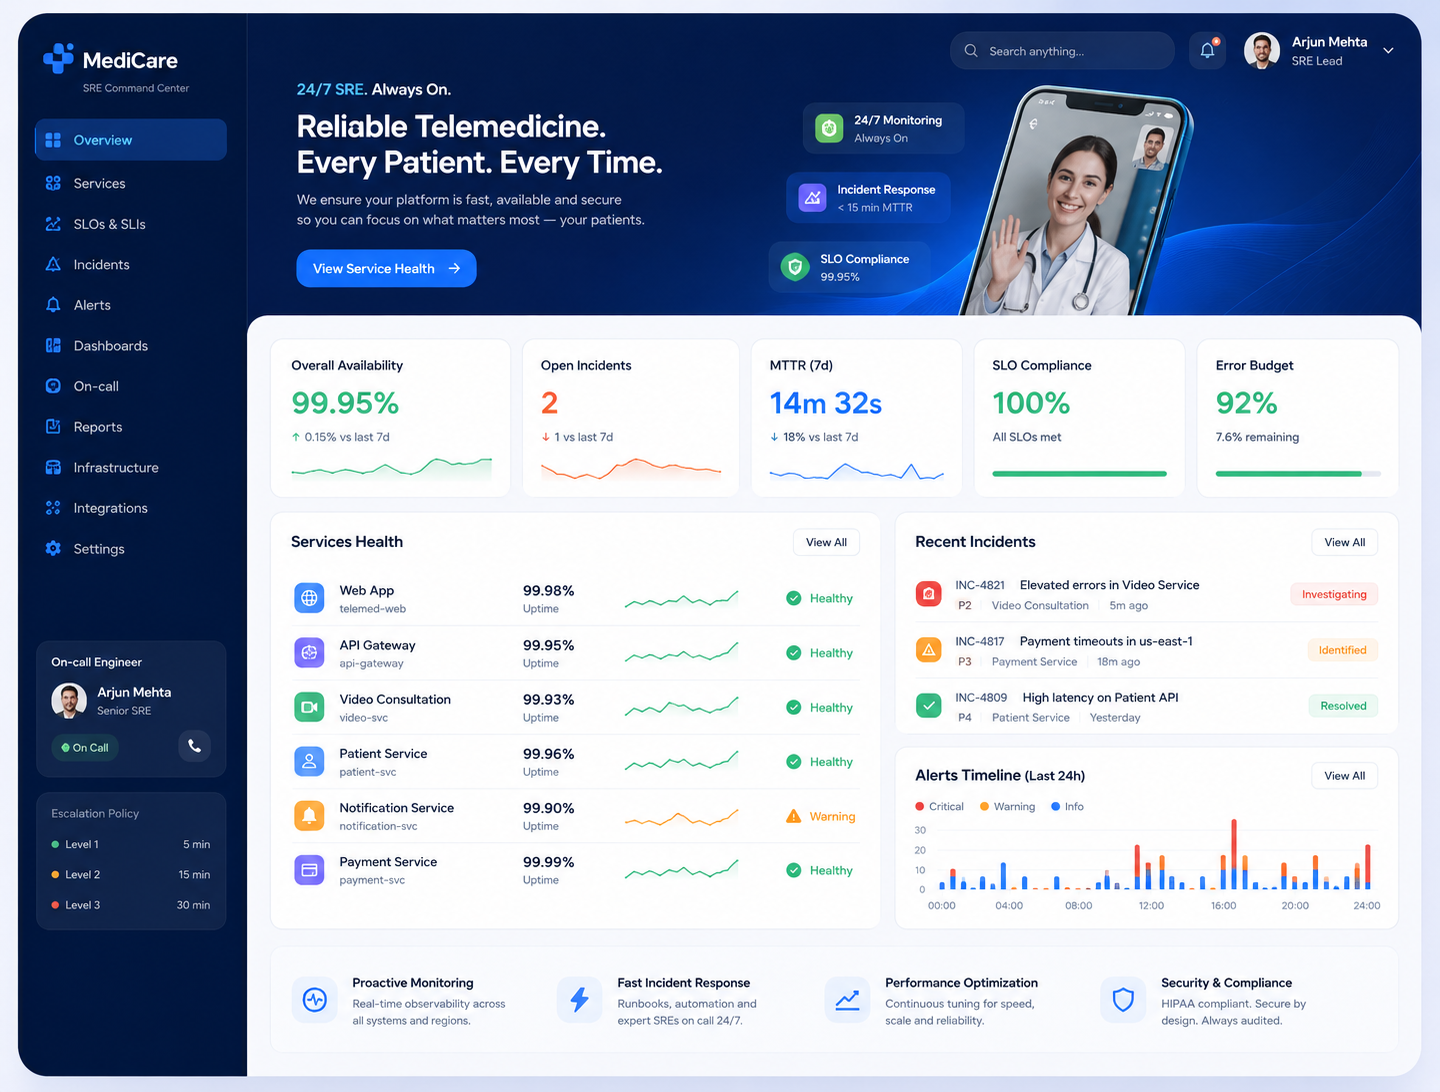
Ran a telemedicine platform to a 99.98% SLO with a follow-the-sun on-call.
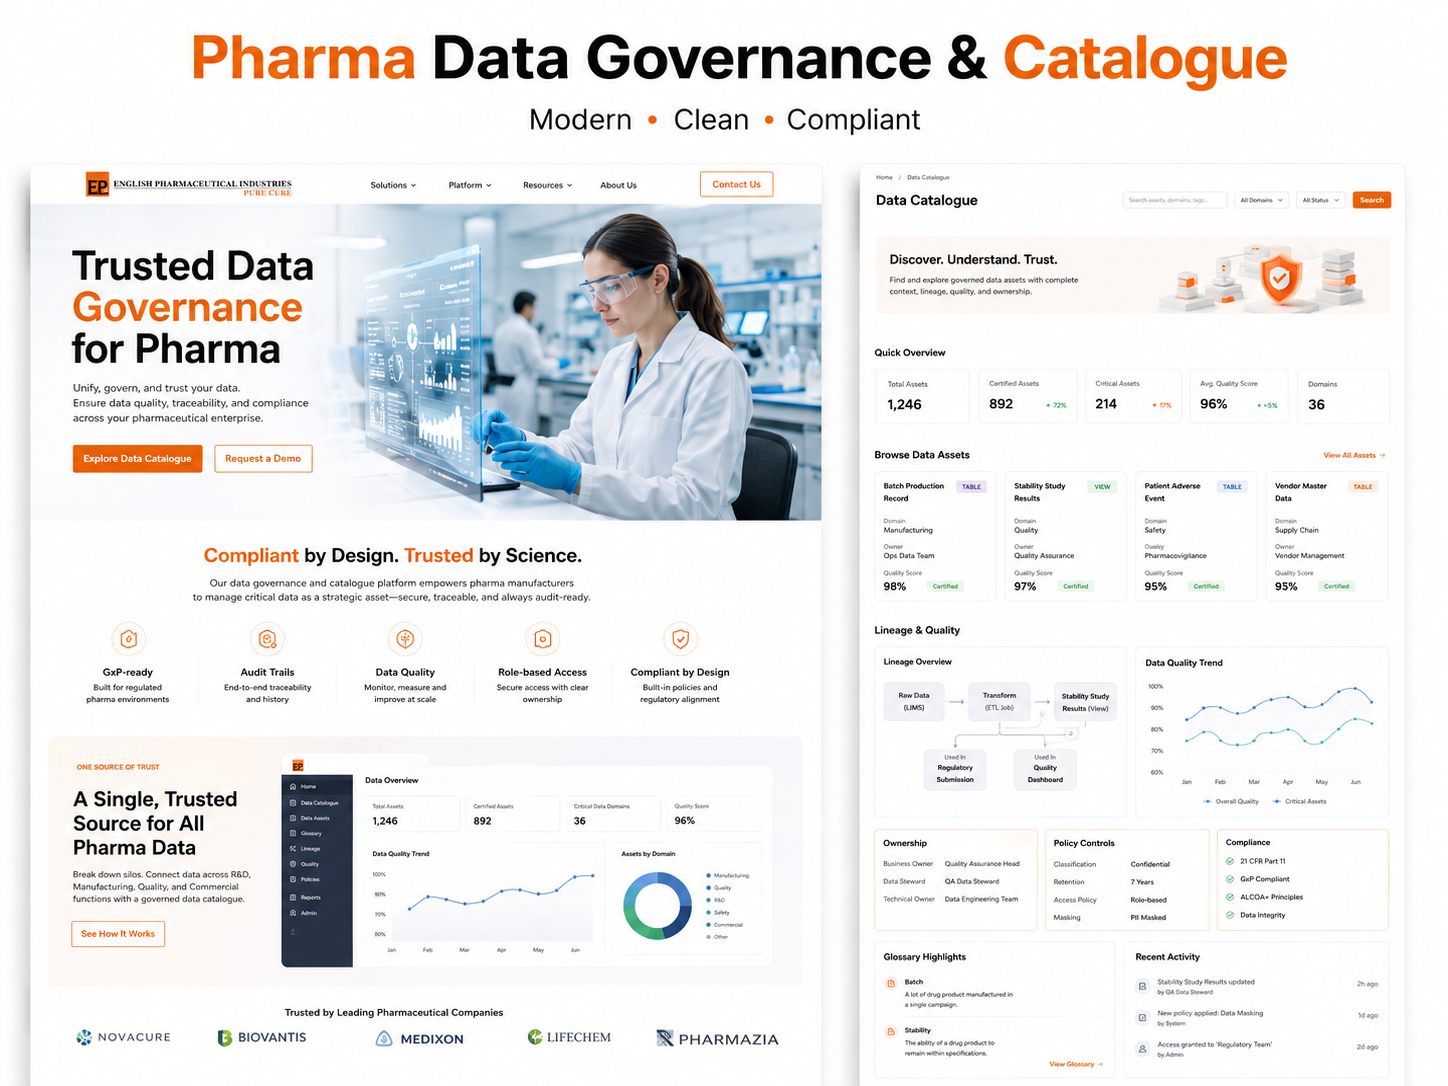
Catalogued and lineage-traced 100% of GxP-regulated data domains for a pharma manufacturer.
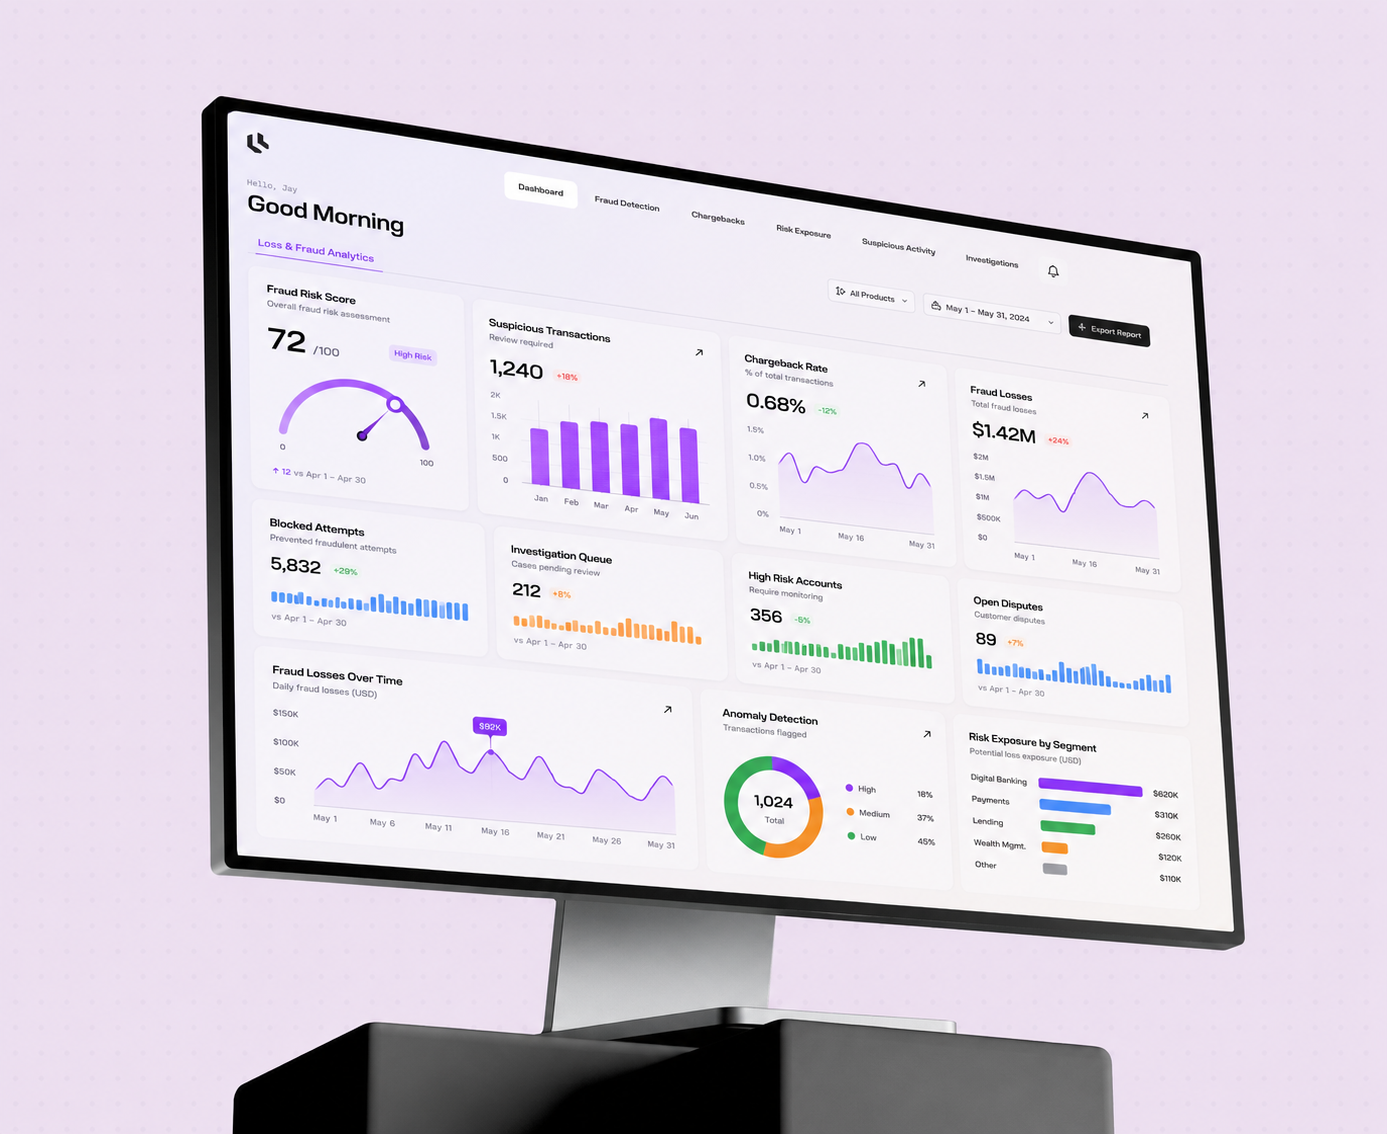
Live loss-and-fraud analytics replaced a two-day report at a fintech, surfacing emerging fraud same-day.
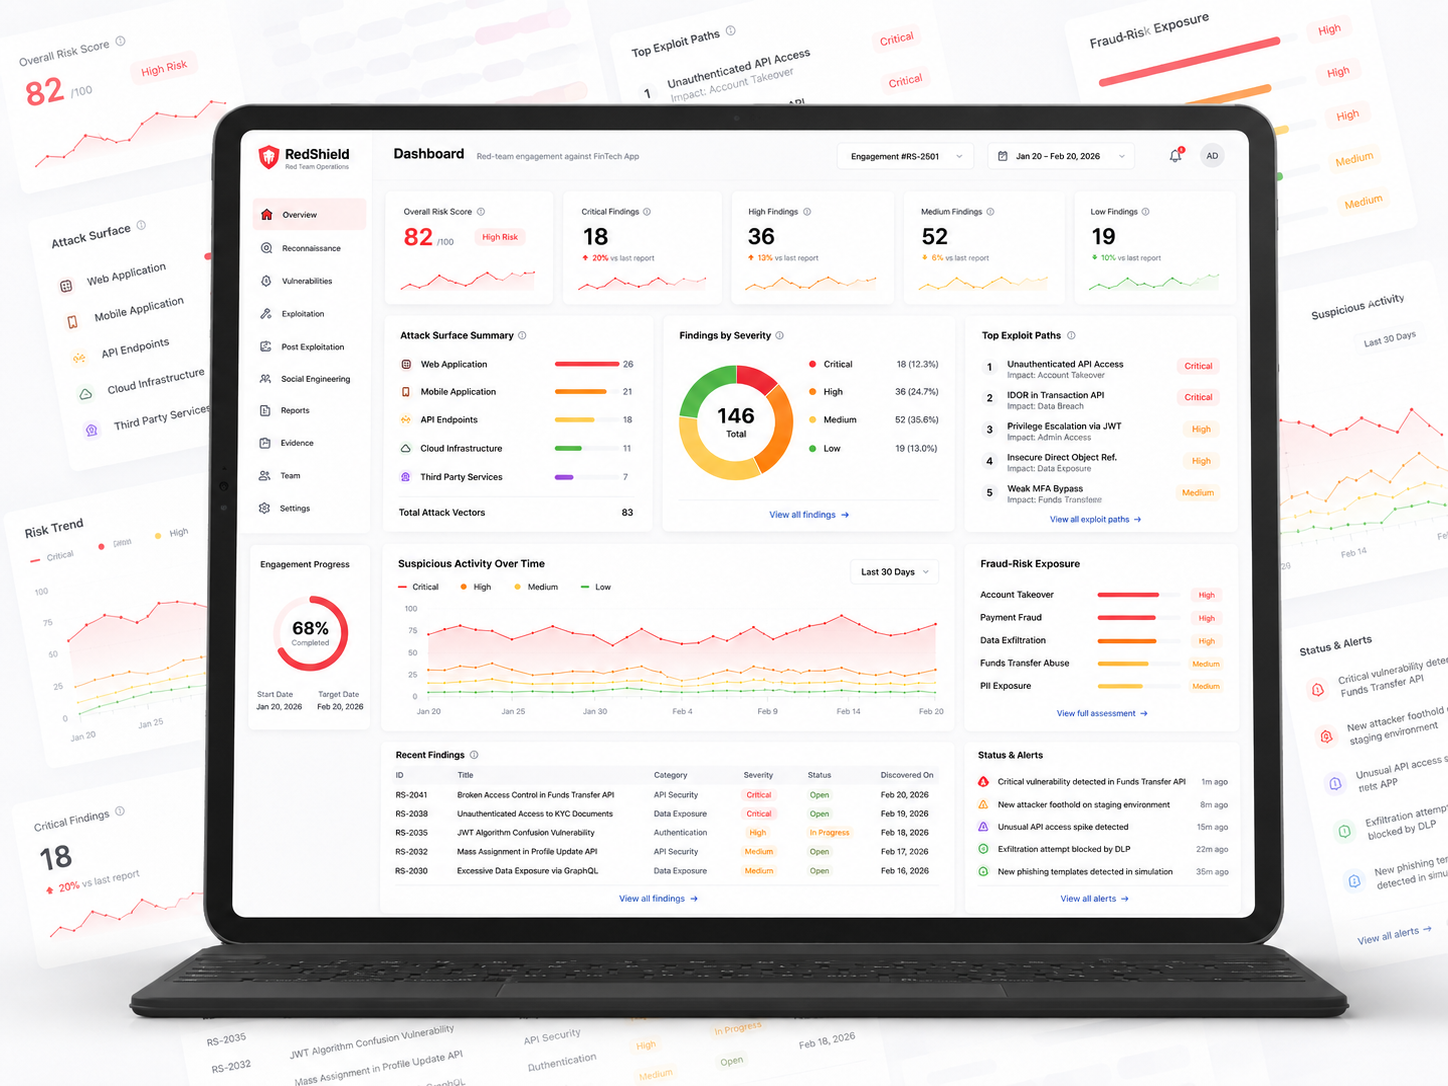
Found and helped close three account-takeover paths before a fintech's launch.
Cut standing privileged access 90% across a manufacturer's IT and OT estate.
Reached validated Annex 11 compliance for a pharma manufacturer in 12 weeks.
Reached DORA operational-resilience readiness in 11 weeks for an insurer.
Validated device, telemetry, and notification APIs under live conditions, shipping a release with zero contract breaks across connected consumers for an IoT platform.
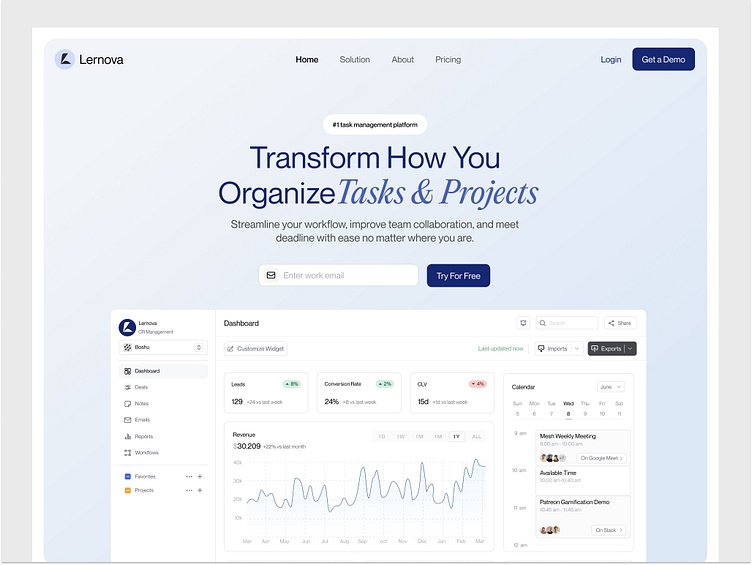
Hands-on regression and exploratory testing of boards, dashboards, and role-based workflows kept every critical path stable through fortnightly releases, holding critical-path coverage at 100% for a UK logistics-operations SaaS.
Validated a 99.9% uptime SLA under peak load, so the cloud portal and provisioning APIs held through demand spikes without incident.
Assessed the attack surface and misconfigurations across AWS, Azure, and GCP and mapped every finding to compliance, leaving the estate audit-ready.
Turned raw on-chain data into a self-service intelligence dashboard that surfaces suspicious wallet activity in seconds for a public financial-intelligence unit.
Automated evidence collection and continuous monitoring got a protocol audit-ready in weeks rather than months, with a complete controls trail behind every review.
On-chain carbon-credit issuance and retirement contracts gave auditors tamper-proof evidence and cut reporting data errors by 94% for an ESG reporting platform.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
Every quote below comes from a programme we shipped, and a reference our prospects are welcome to call.
“Our old SOC produced thousands of alerts a day and still missed an identity-pivot incident that ran for eleven days. BritonOne Technology rebuilt detection around our own identity estate. Median time-to-detect is now under six minutes.”