Product Design & UX
Design systems, prototypes, and accessibility audits, interfaces engineered for the journeys your users actually run.
FigmaStorybookWCAG 2.2
Type-safe React and Next.js apps, headless e-commerce, and marketing platforms, designed around your product workflows and shipped with Core Web Vitals you can prove in CI.
Engage us for a single discipline or compose a full programme. Every engagement is run by a named delivery lead with a senior engineering bench behind them.
Type-safe React and Next.js applications with design-system tokens, motion, and accessibility baked in from the first commit.
Web is rarely one stack. Our delivery squads compose specialists from each discipline so design, code, and platform are owned under one accountable line.
Design systems, prototypes, and accessibility audits, interfaces engineered for the journeys your users actually run.
Type-safe React and Next.js apps with measured Core Web Vitals, components that ship to design tokens, not screenshots.
Typed services, event-driven workflows, and contract-tested APIs: Node, Go, .NET, or Python depending on the operating estate.
Headless storefronts and editor-first content workflows: Shopify, commercetools, Sanity, and Contentful wired to a typed frontend.
Core Web Vitals engineering, structured data, and image budgets, measured improvements baked into CI, not patched after launch.
Infrastructure-as-code, edge runtimes, and observability, production engineering on AWS, Vercel, or Cloudflare from day one.
From the first discovery workshop to long-term evolution. Each phase produces concrete artefacts your stakeholders can review, no opaque hand-offs, no surprise scope.
Architect-led workshops to align scope, success metrics, and operating constraints before a line of code is written.
Reference architecture, API contracts, and design system, the engineering foundations for everything that follows.
Two-week sprints with demo, review, and reprioritisation, working software in your environment from the first release.
Automated regression, performance, and security testing, release evidence captured for your auditors, not invented after the fact.
Zero-downtime release with rollback gates, runbook drills, and an on-call rota the day the product goes live.
Managed support, SLO-backed operations, and a continuous roadmap: the team that built it stays accountable for it.
Every engagement walks the same path, sized to your problem, but with the same verification gates baked in.
Two-week paid sprint. Architect-led. Output: regulator map, costed roadmap, signed scope.
Pod composition, sequenced milestones, change-control governance, and risk register.
Reference architecture, threat model, design system, and acceptance criteria locked.
Weekly demos, trunk-based, CI/CD from day one. Code reviewed against spec at every gate.
Unit, integration, e2e, security, performance, and accessibility, automated and gated.
Blue-green or canary, observability live before launch, rollback rehearsed.
Managed services or hypercare hand-off. Defined SLOs, named on-call, monthly reviews.
Success stories
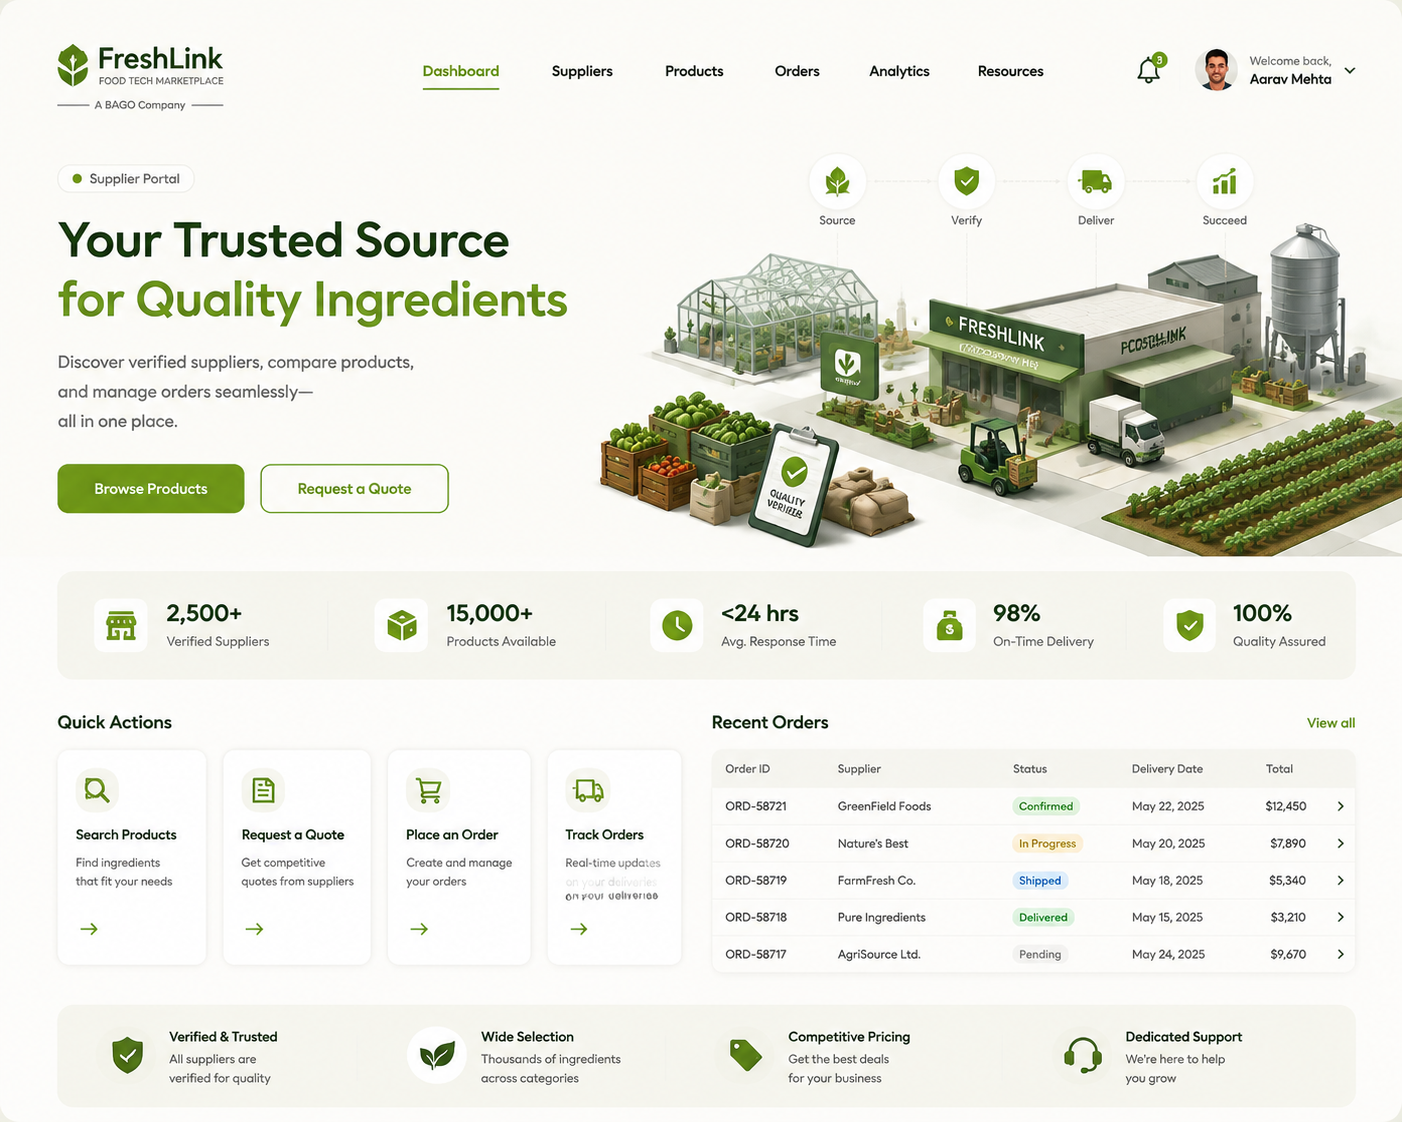
Self-service supplier portal lifted supplier adoption to 62% in one quarter for a foodtech marketplace.
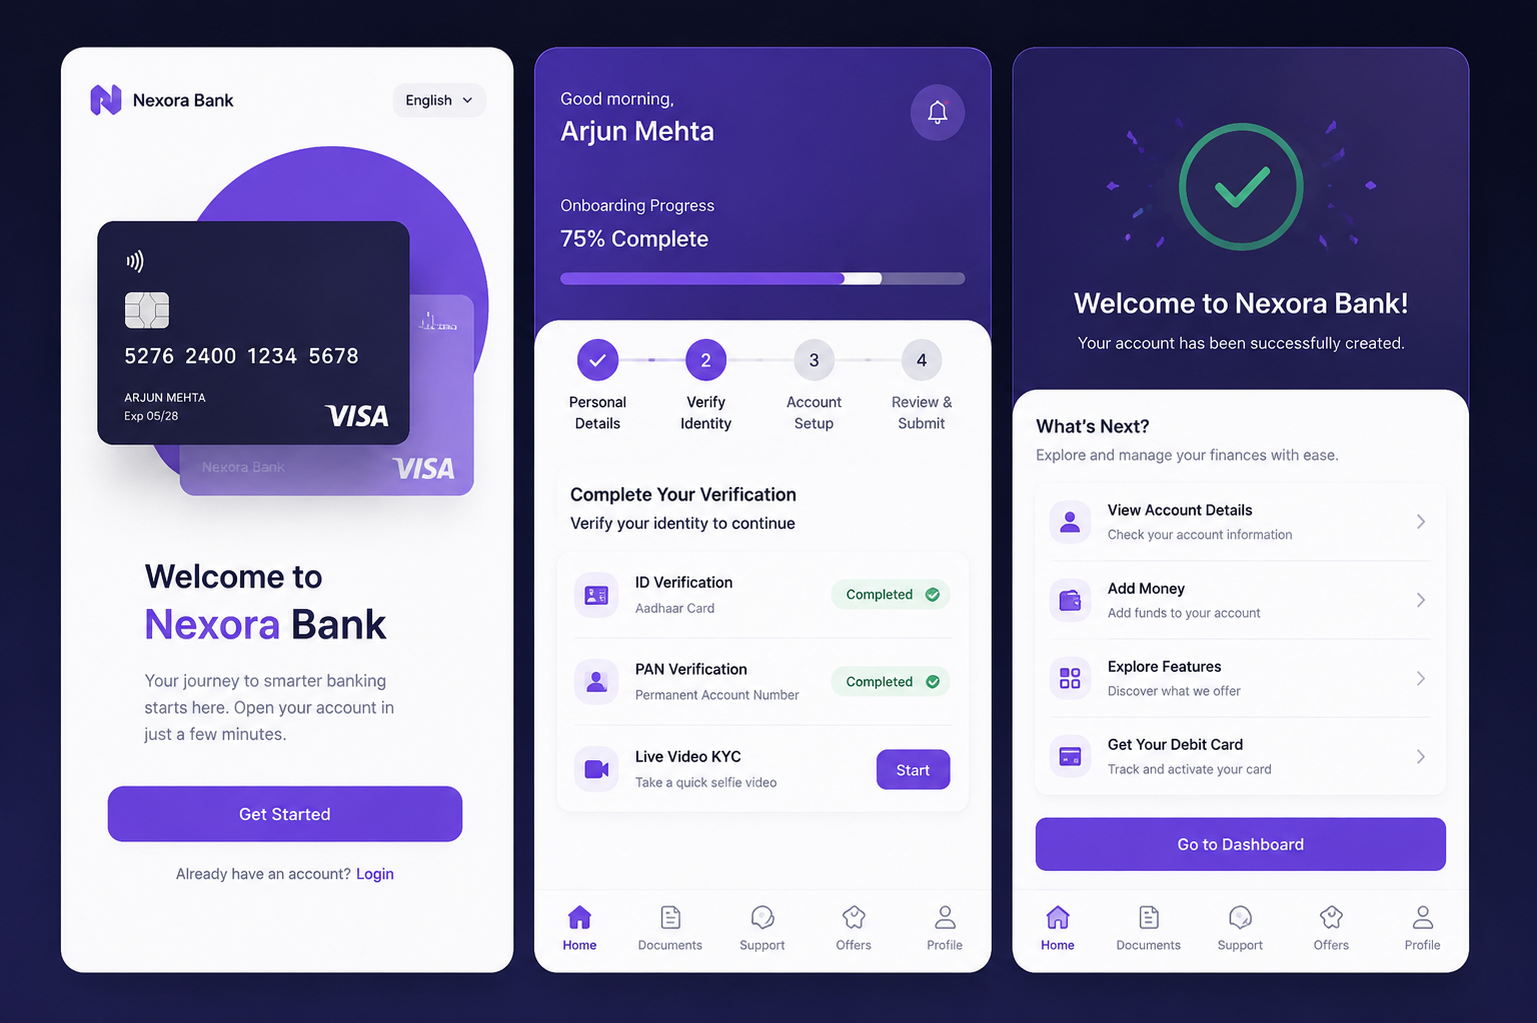
Straight-through KYC onboarding raised completion to 78%.
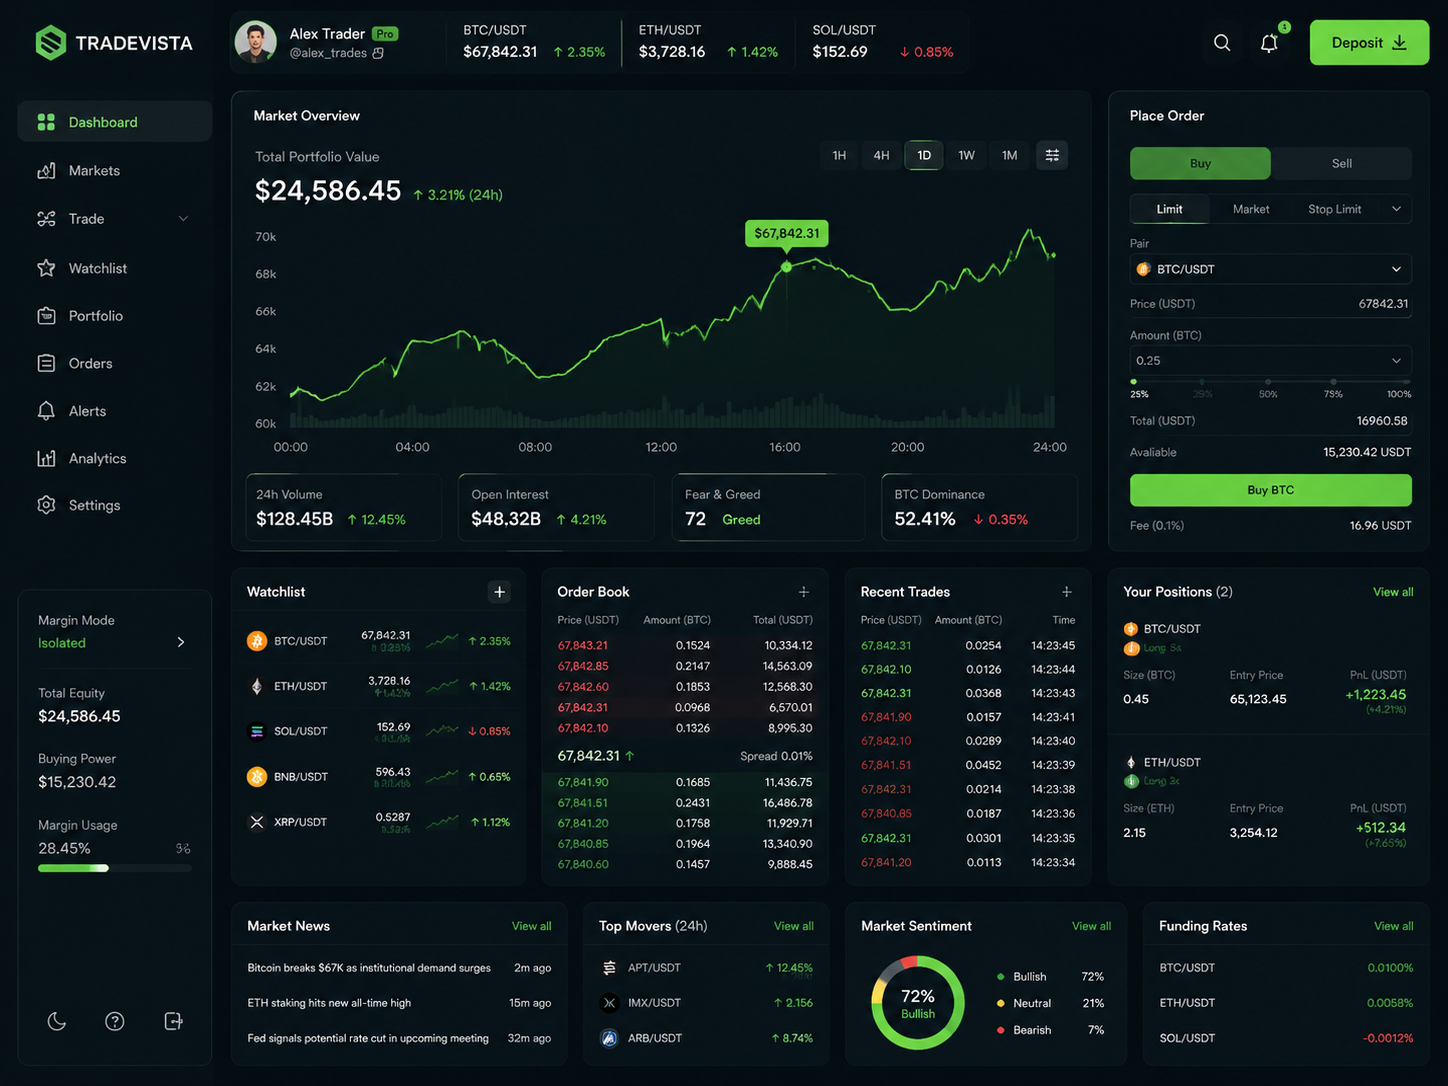
Sub-120ms streaming operations dashboard across 40 control desks for a logistics operator.
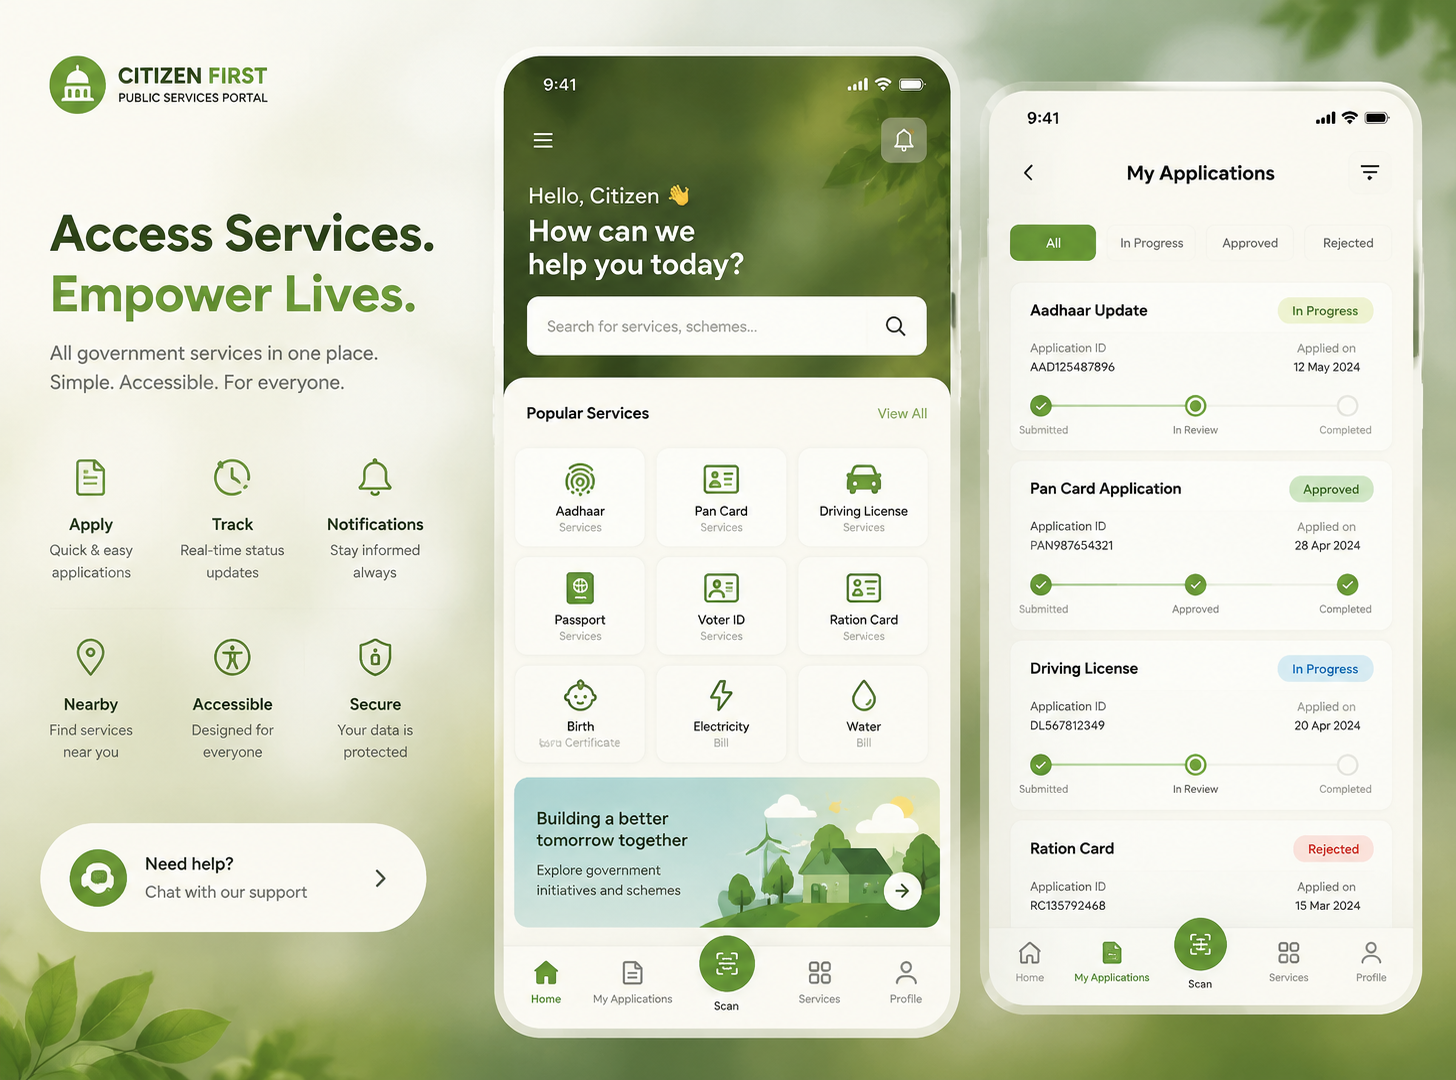
Rebuilt a citizen portal to WCAG 2.2 AA, cleared external audit first pass.
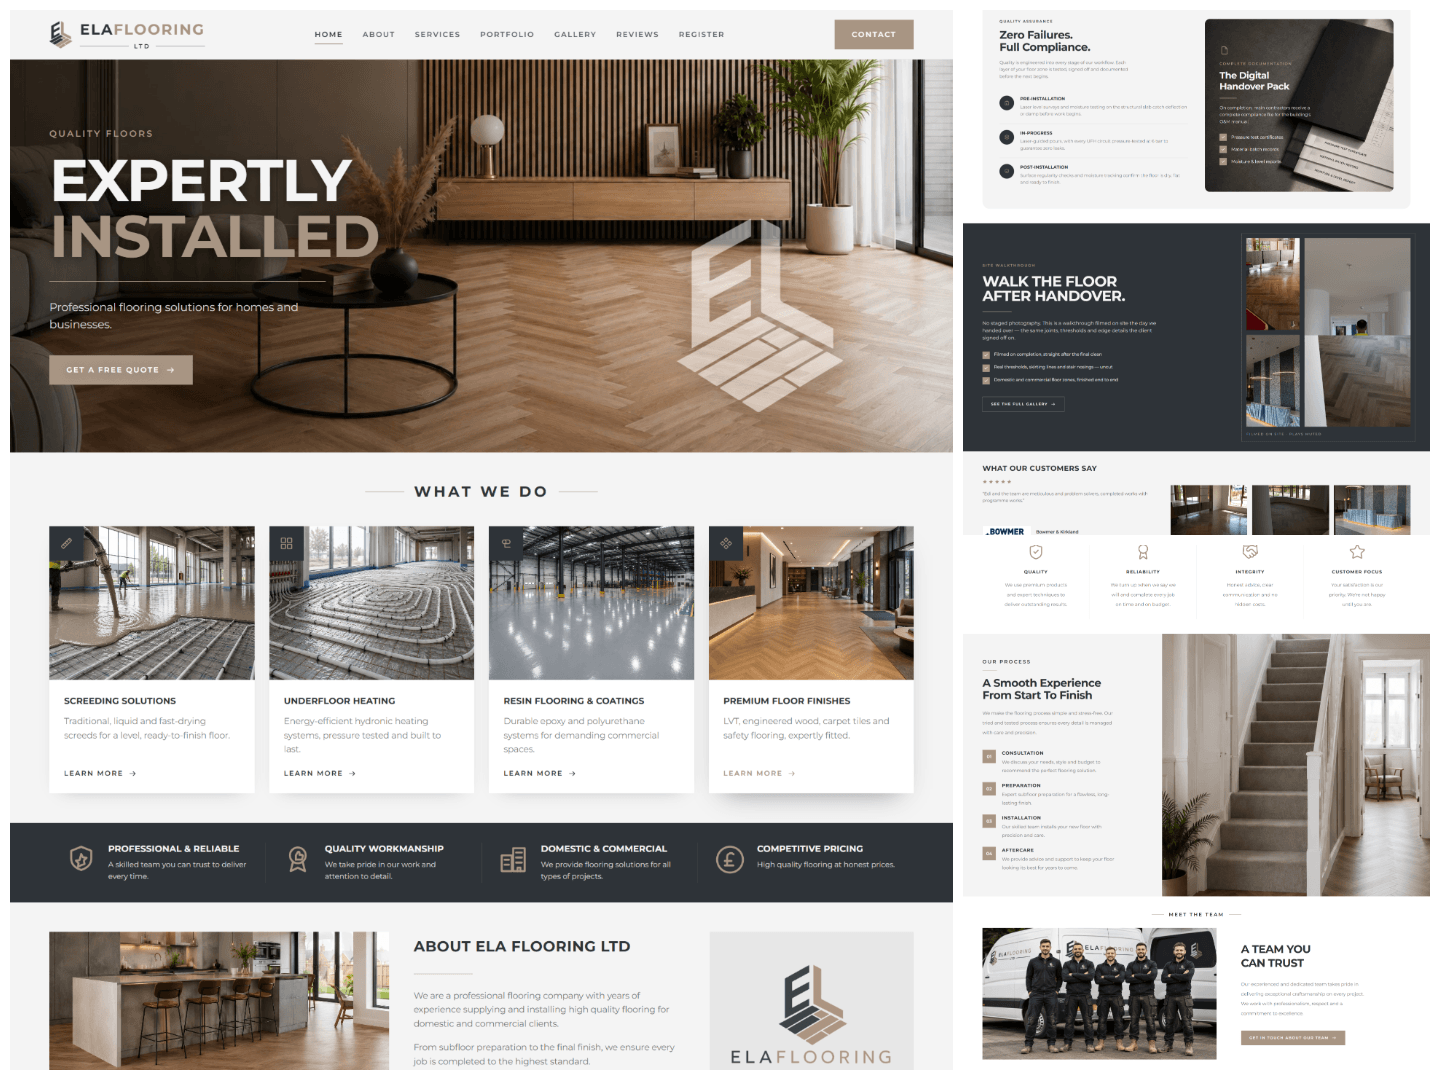
A 12-page static-exported brochure site with a PHP-based lead pipeline, shipped end to end in 9 days.
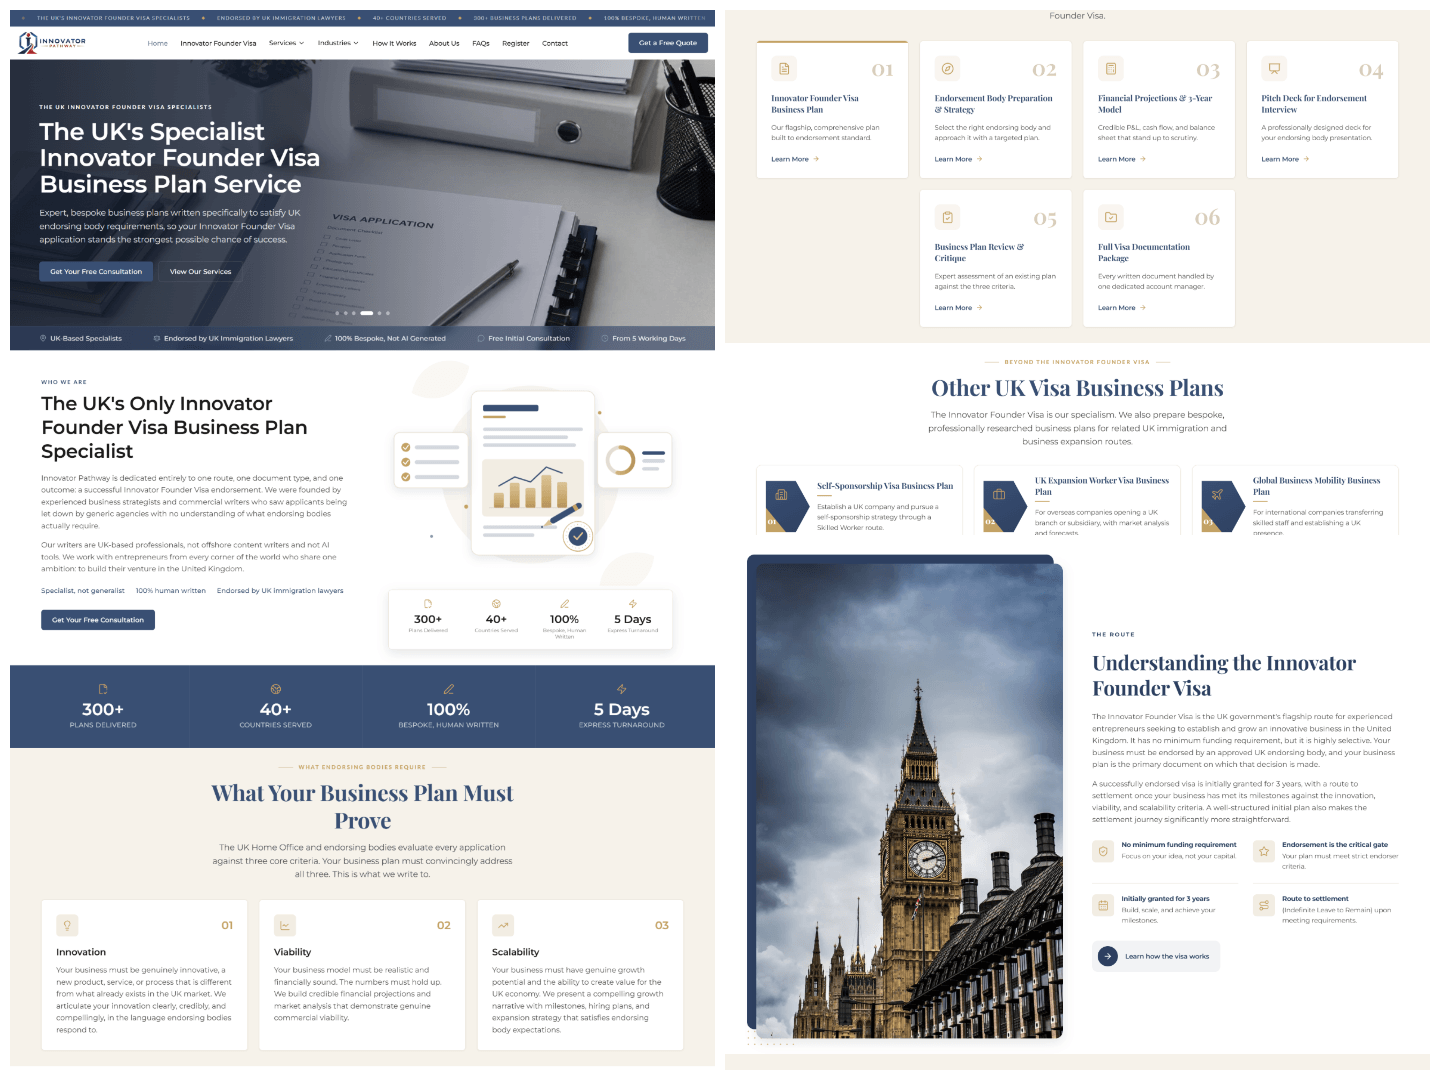
A taxonomy-driven services-and-industries catalogue with a Sheets-backed lead pipeline, shipped in 19 days.
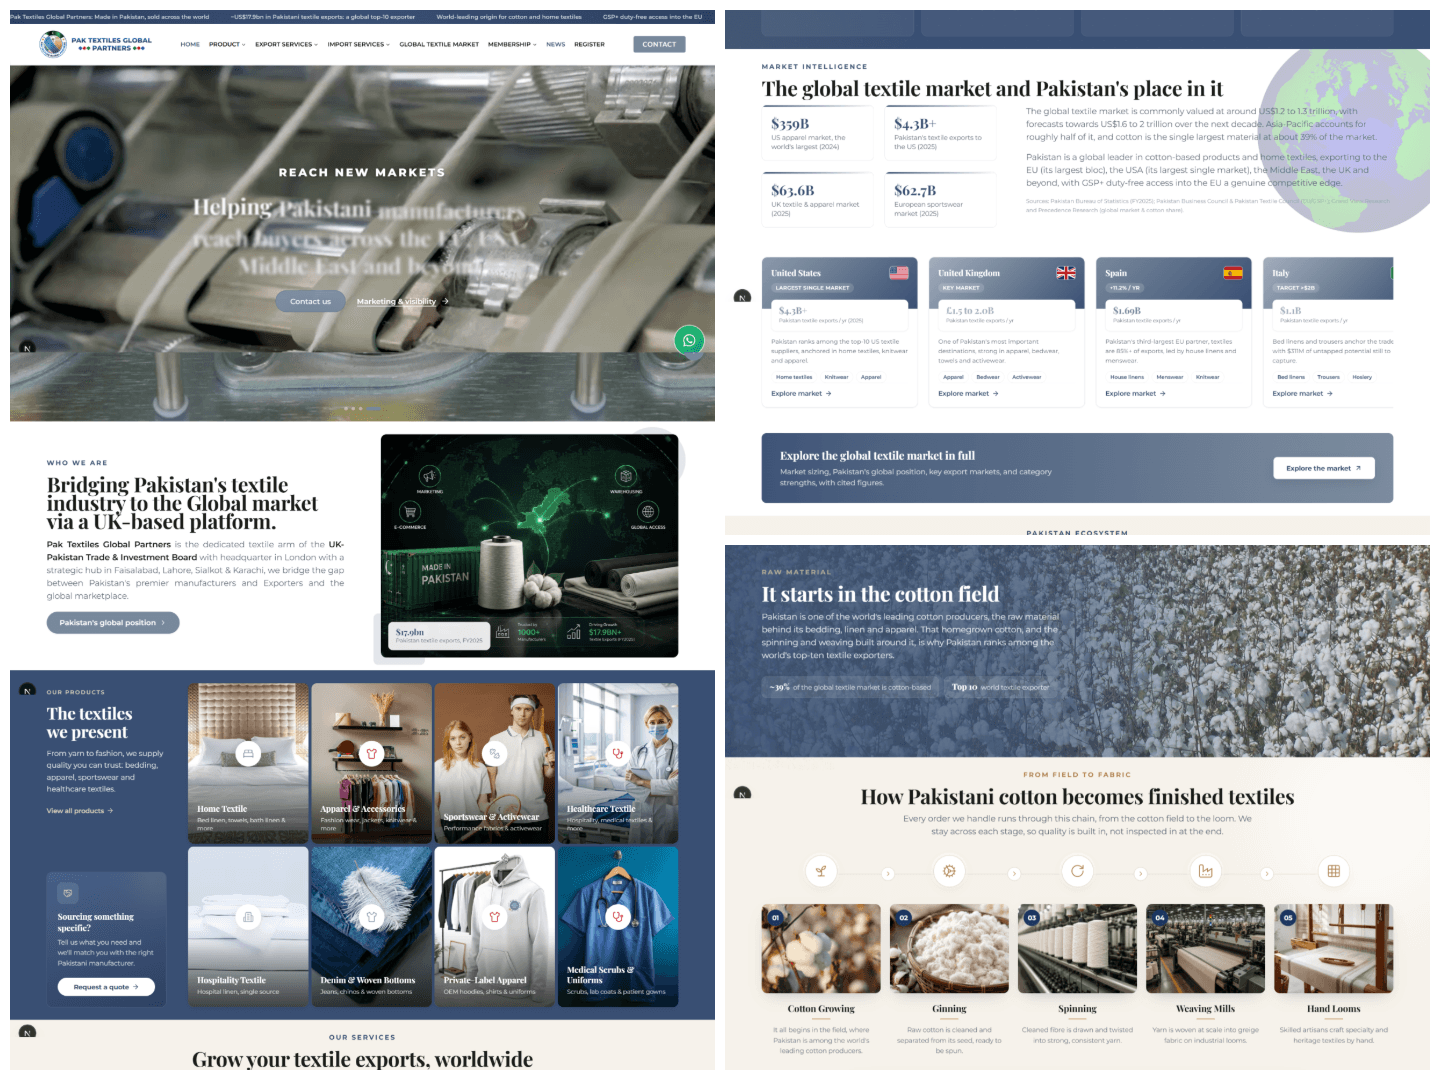
Re-themed and re-scoped an 80-route SaaS template into a 15-page global trade platform, with zero legacy brand colour left across 225 files.
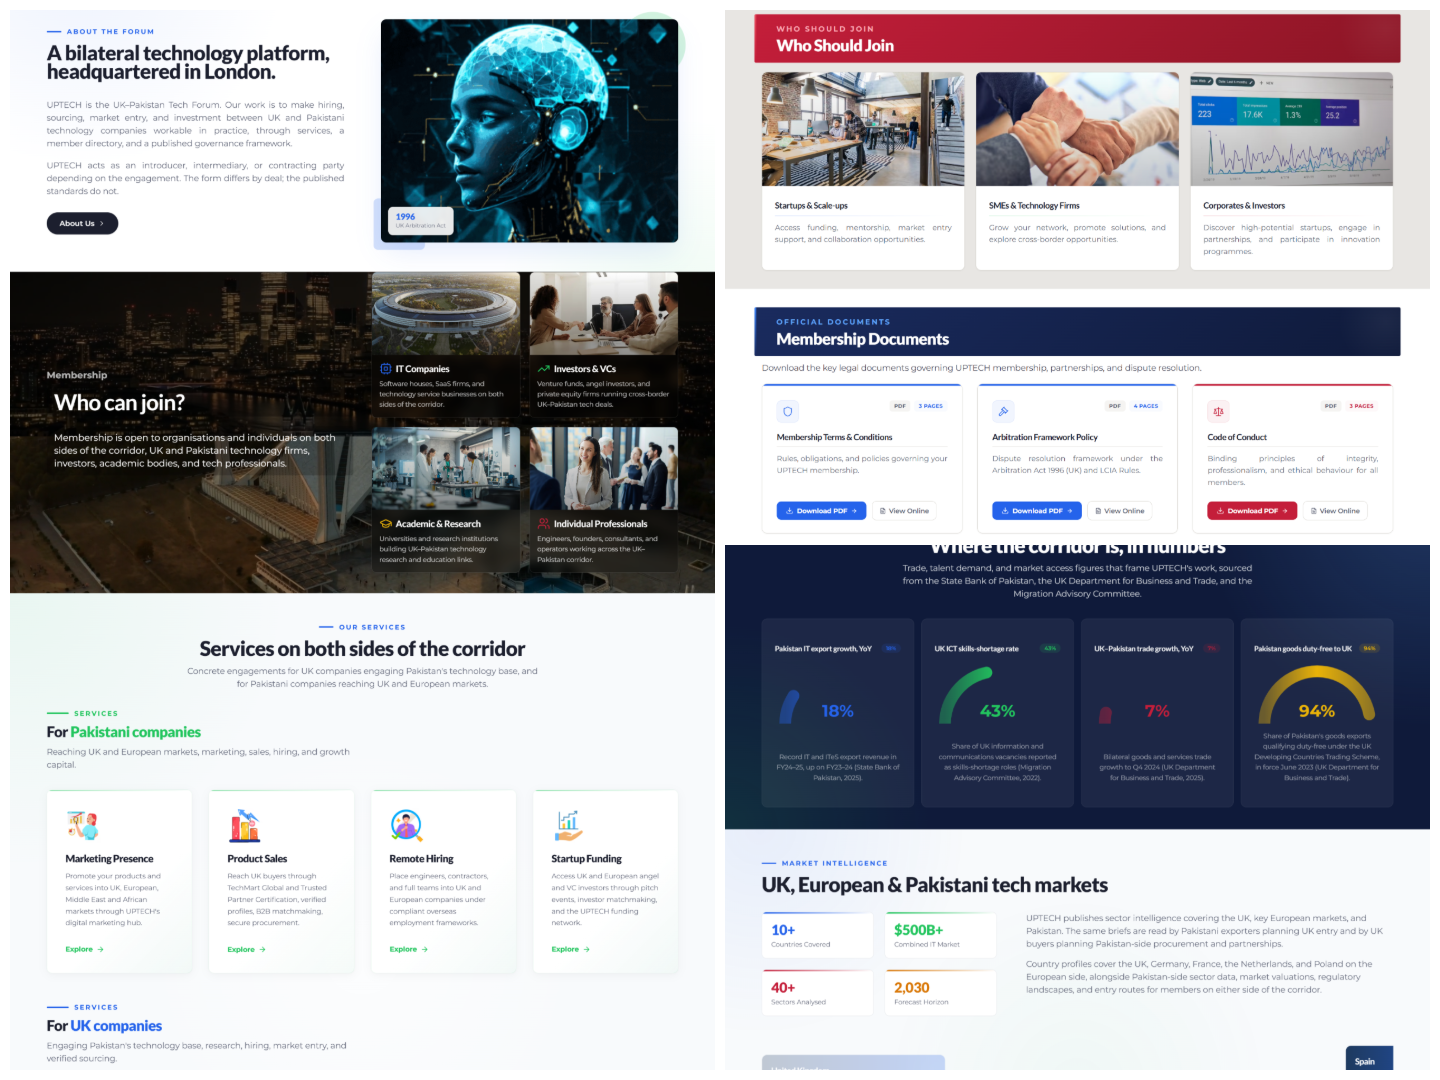
A membership and governance platform for a bilateral UK-Pakistan tech forum, complete with a downloadable governance-document library and a corridor market-intelligence dashboard.
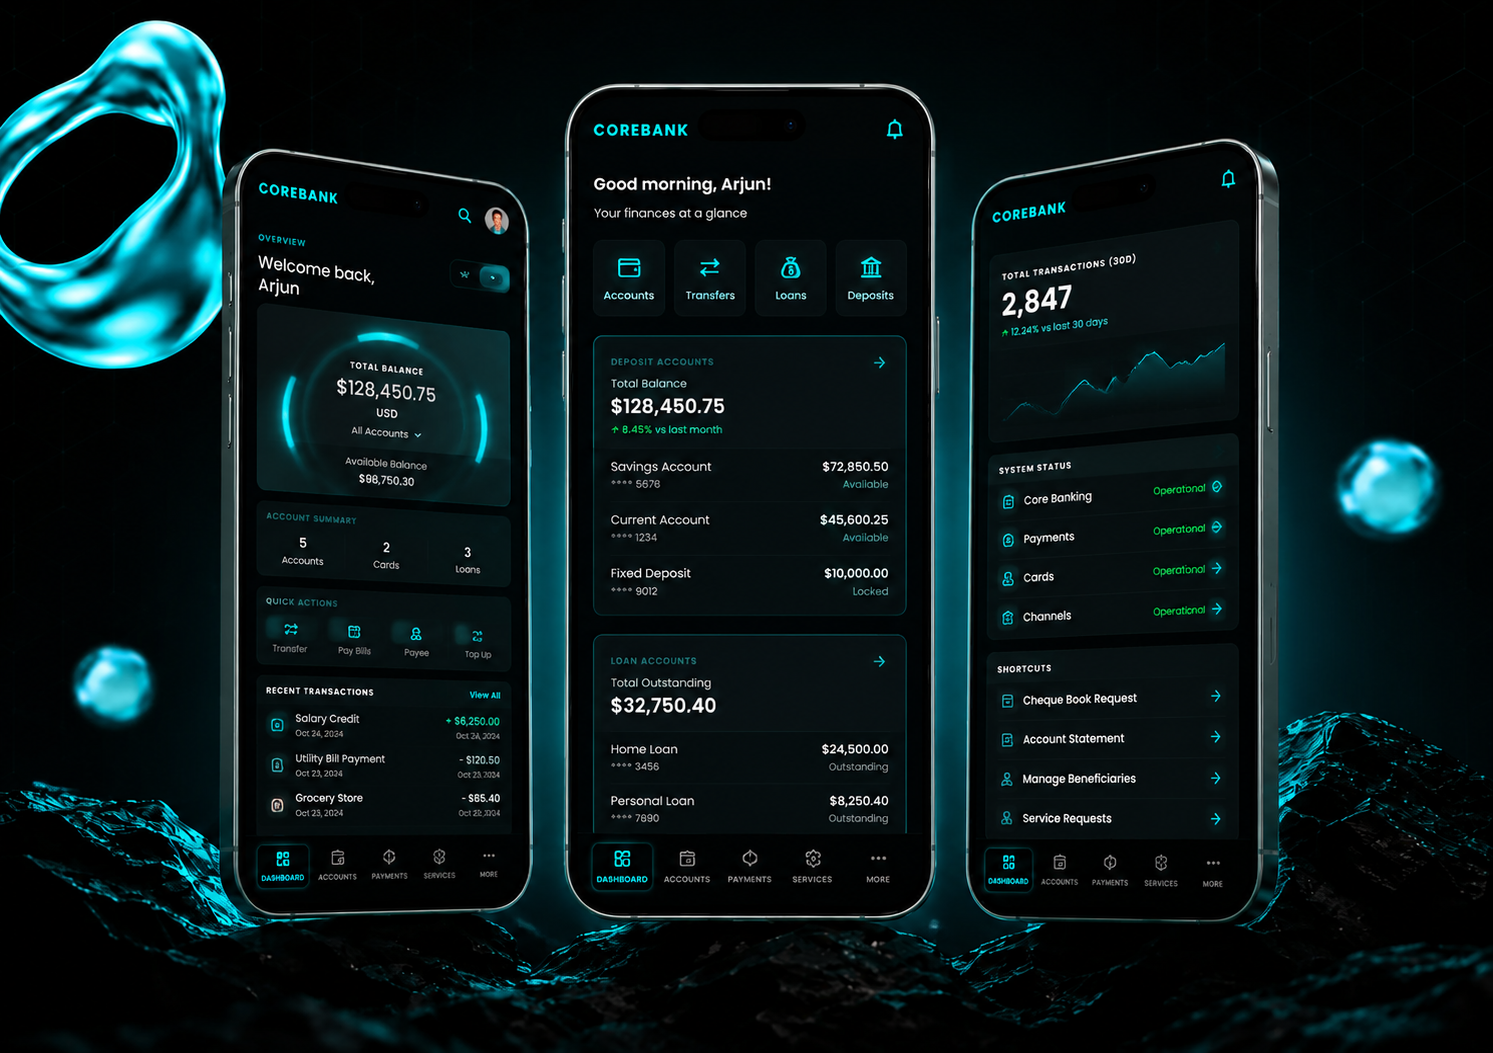
Ledger, accounts, and payment rails delivered to an FCA launch milestone in 9 months.
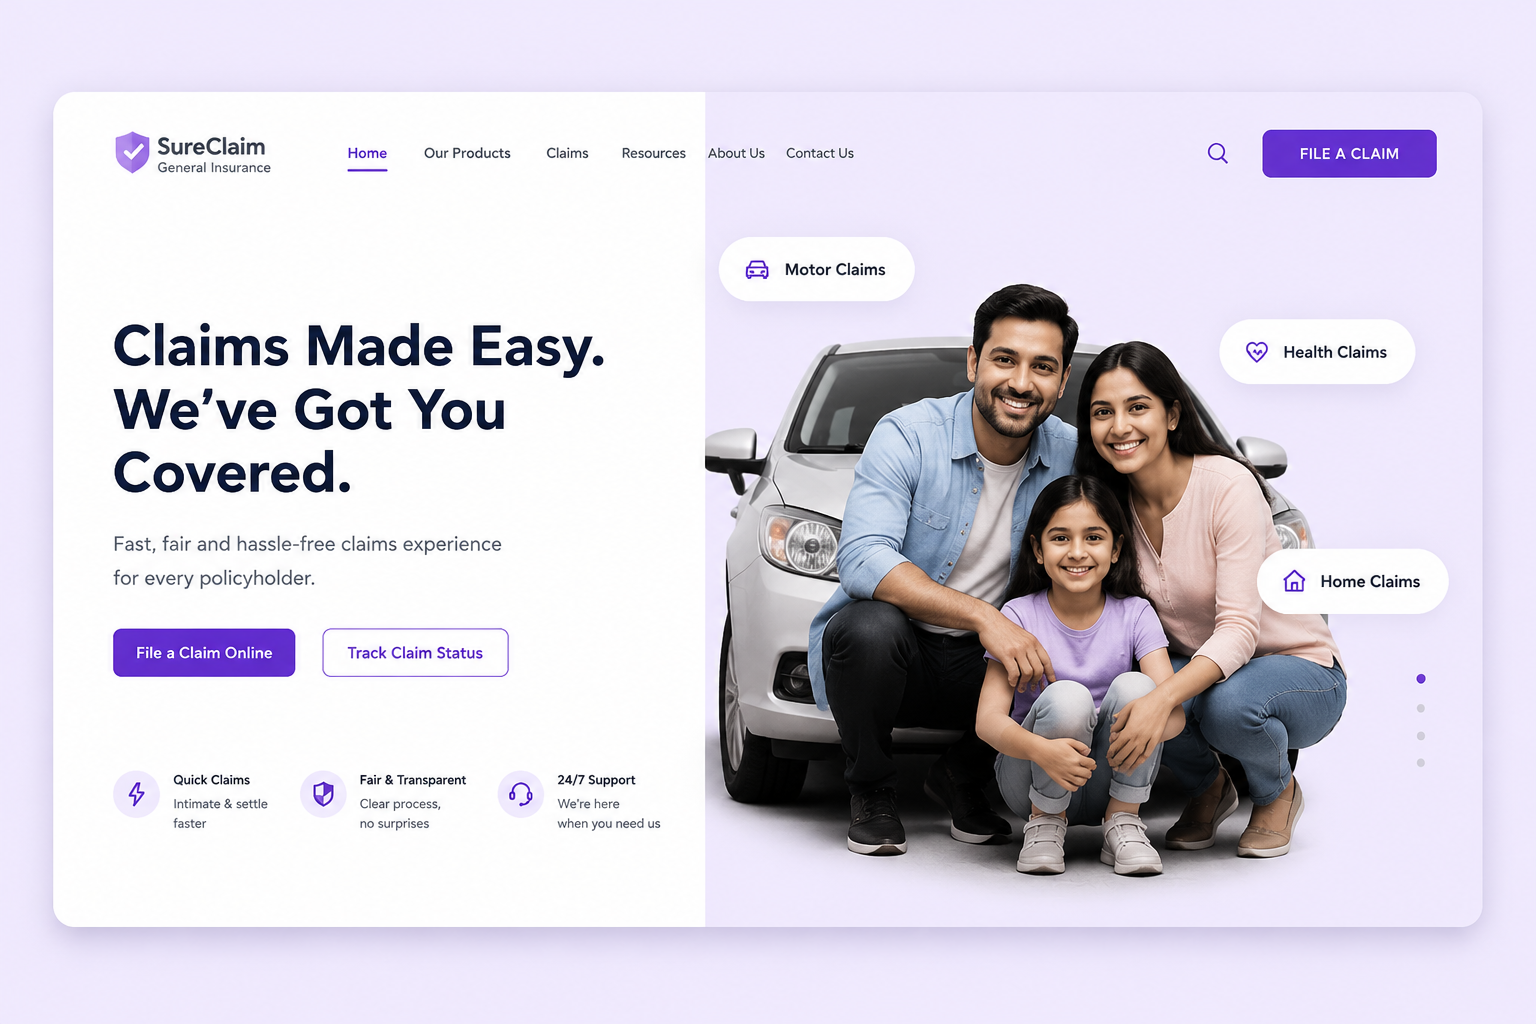
Replaced a 15-year-old claims system, tripling throughput per handler.
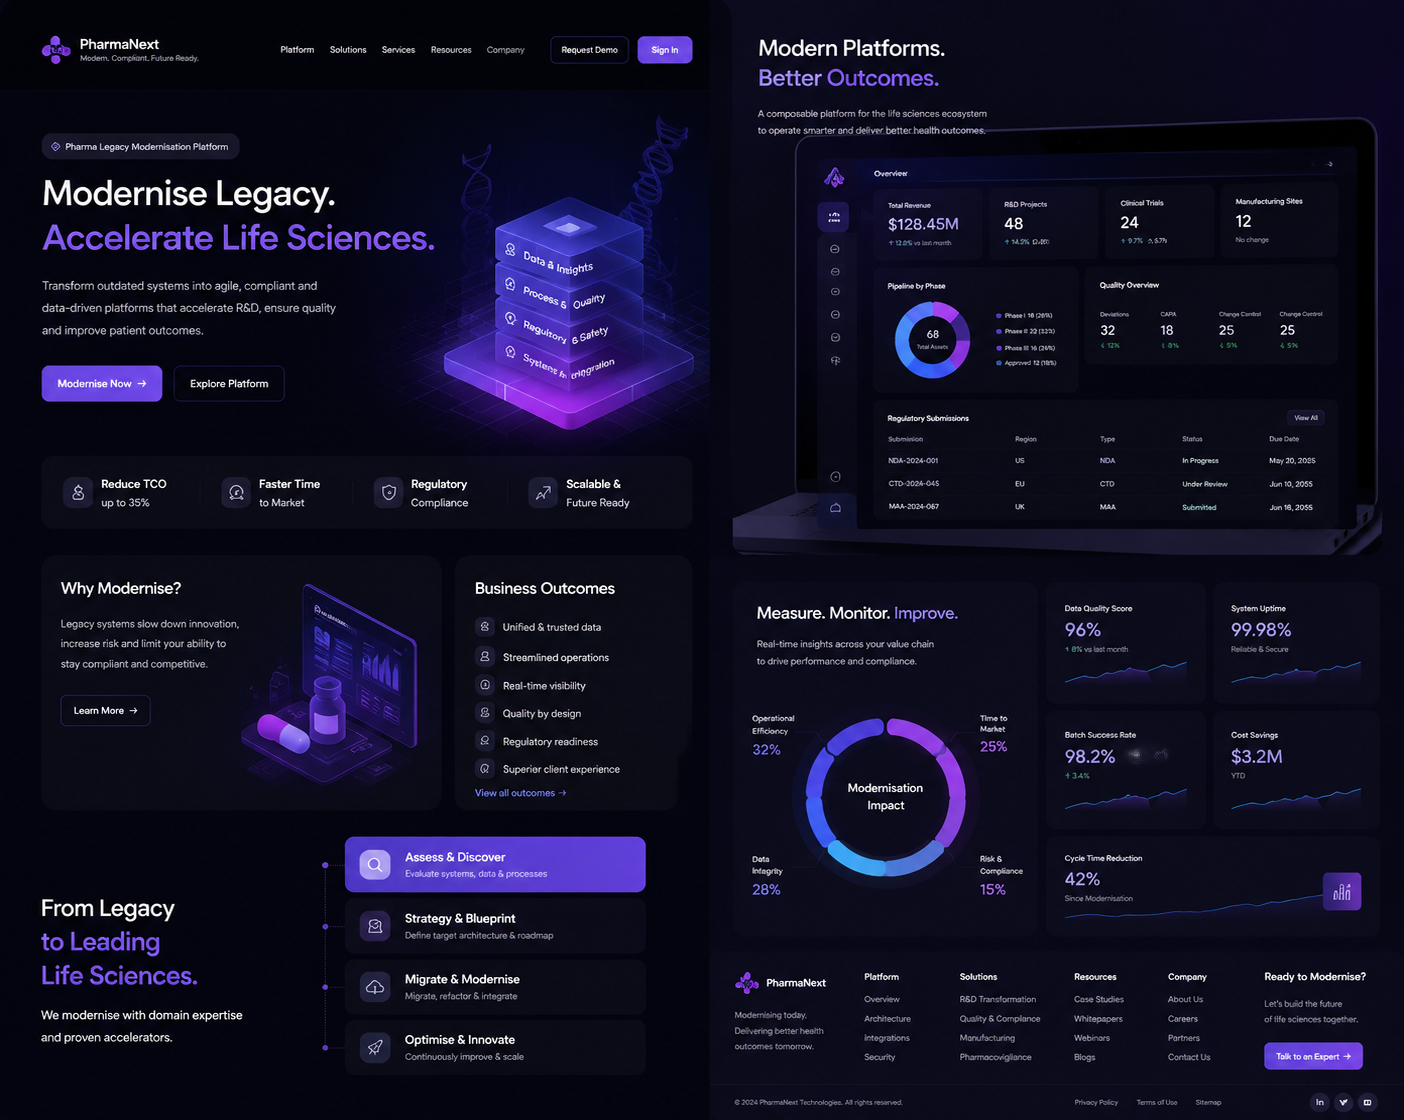
Strangled a validated legacy system into microservices, cutting change lead time 40% for a pharma manufacturer.
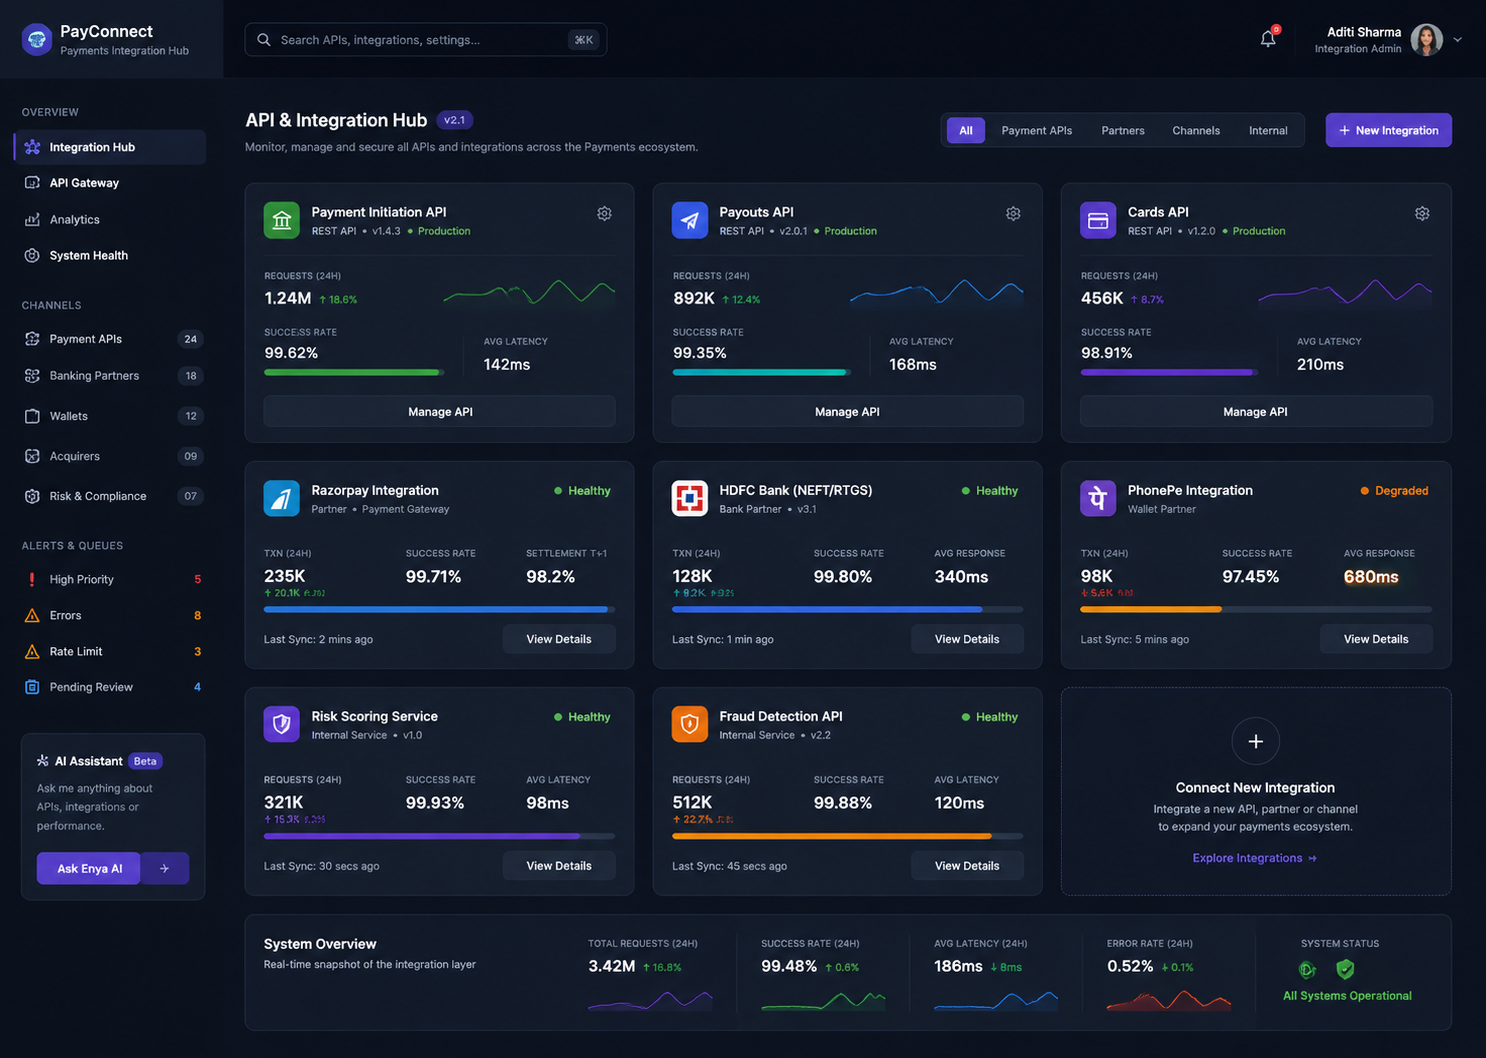
Unified 120+ partner integrations behind one governed API gateway.
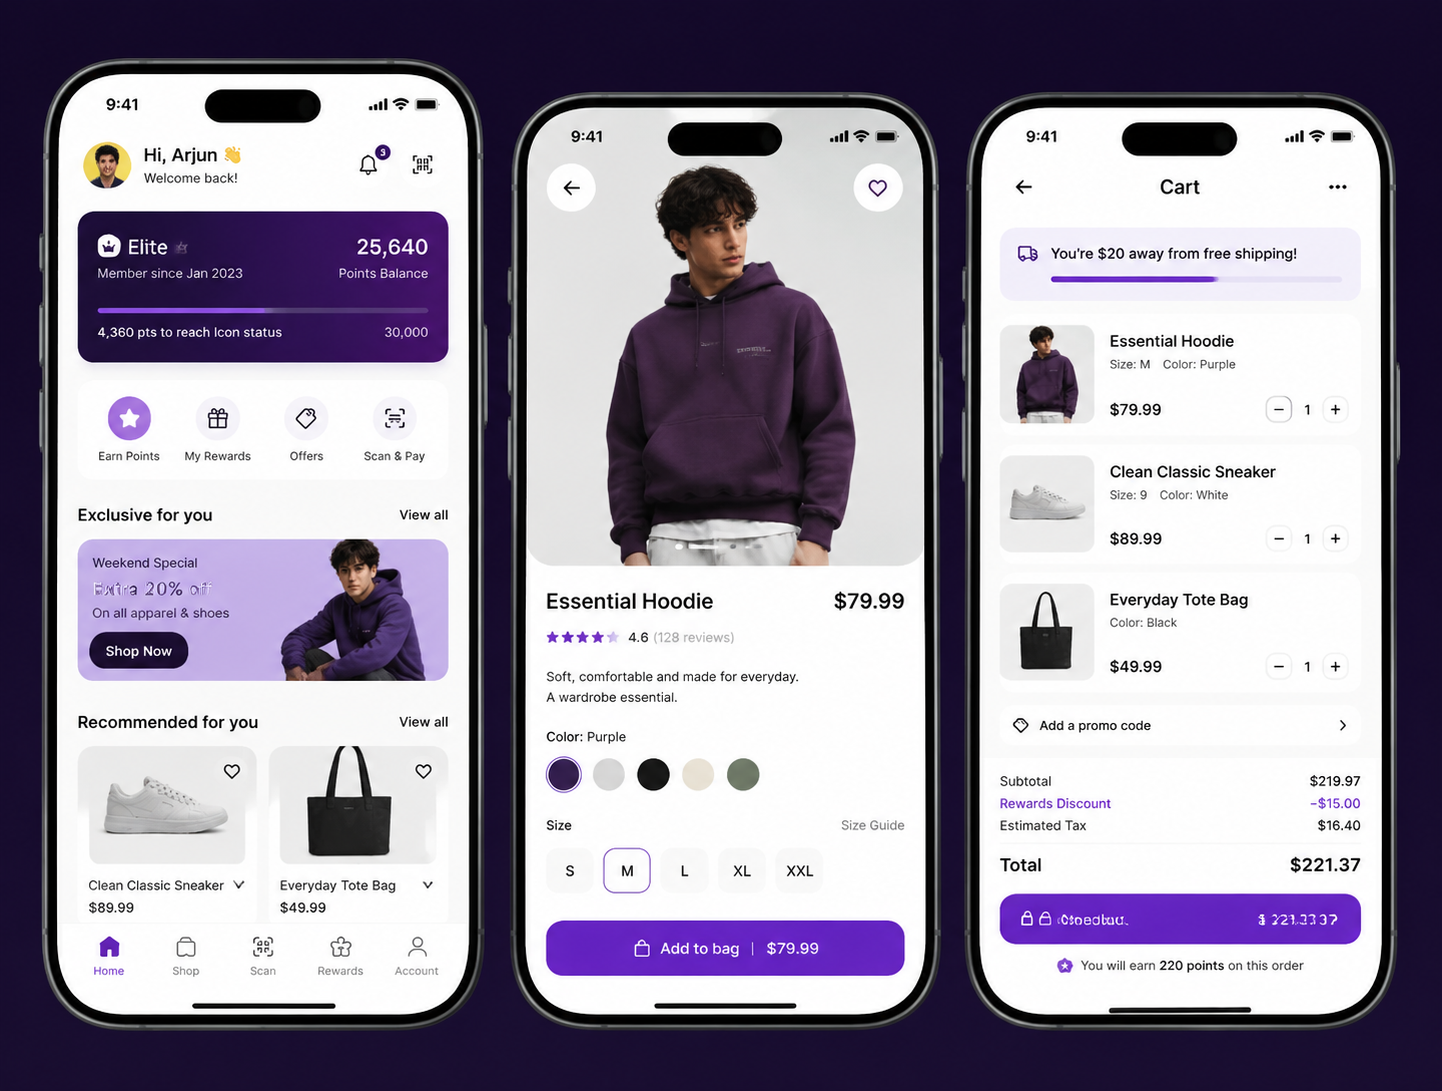
Launched a retail loyalty app to a 4.8-star rating and 200k users in 90 days.
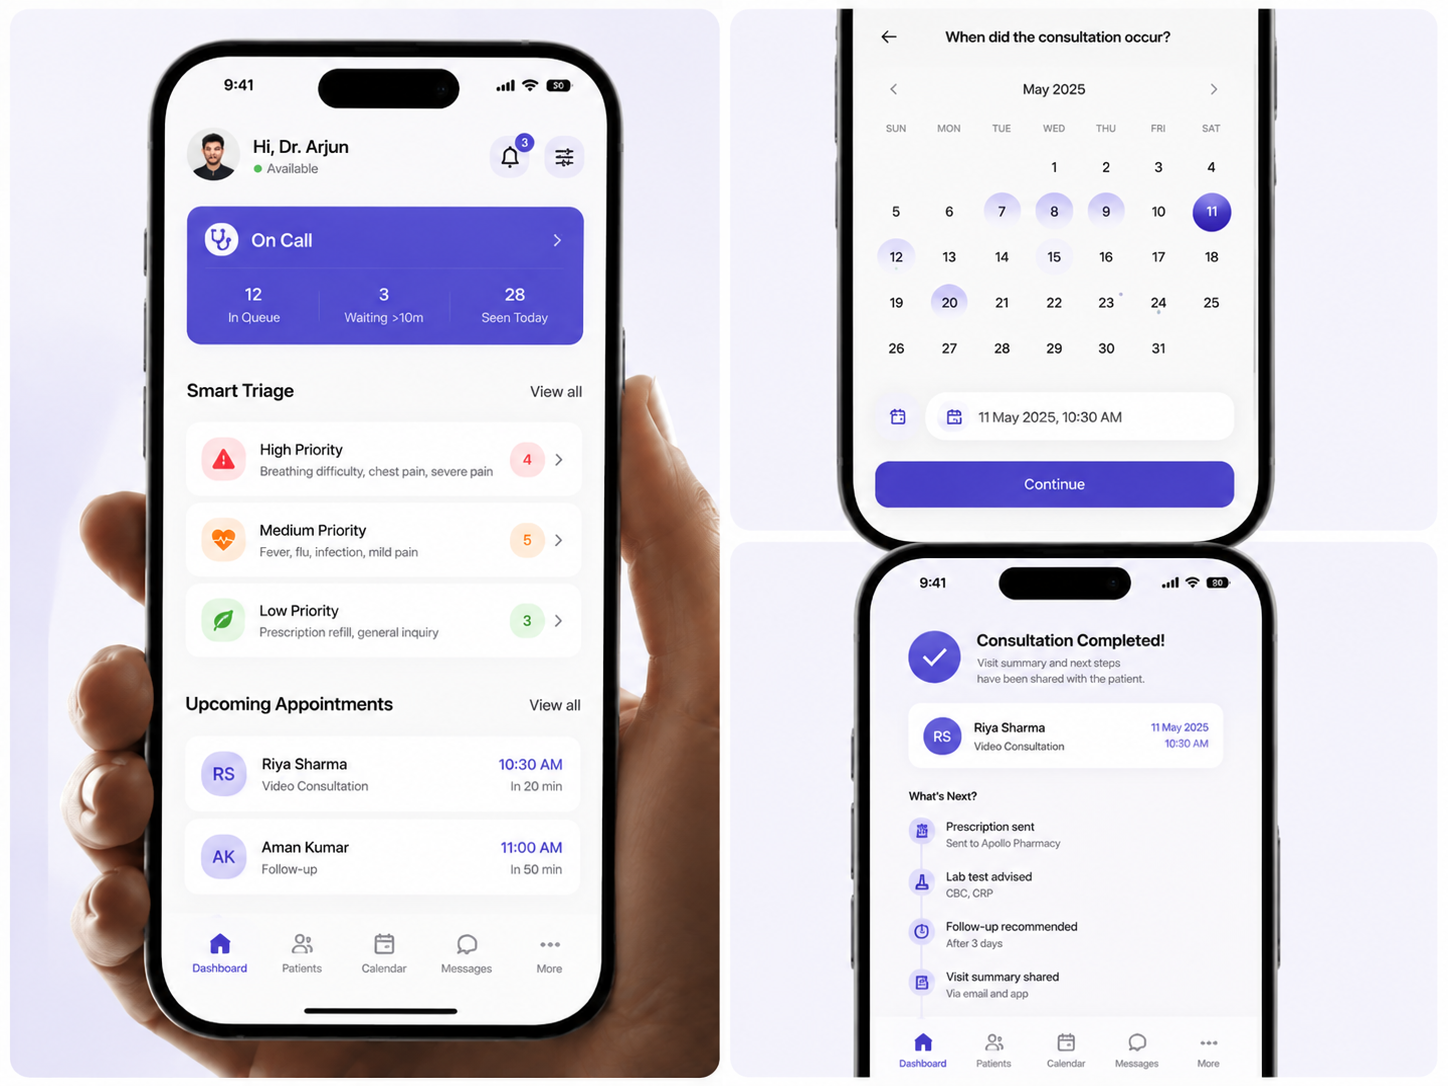
Photo-and-symptom-first triage app cut consultation prep time 54% for a telemedicine provider.
Offline-first engineer app cut job-completion admin 31% for a manufacturer's field team.
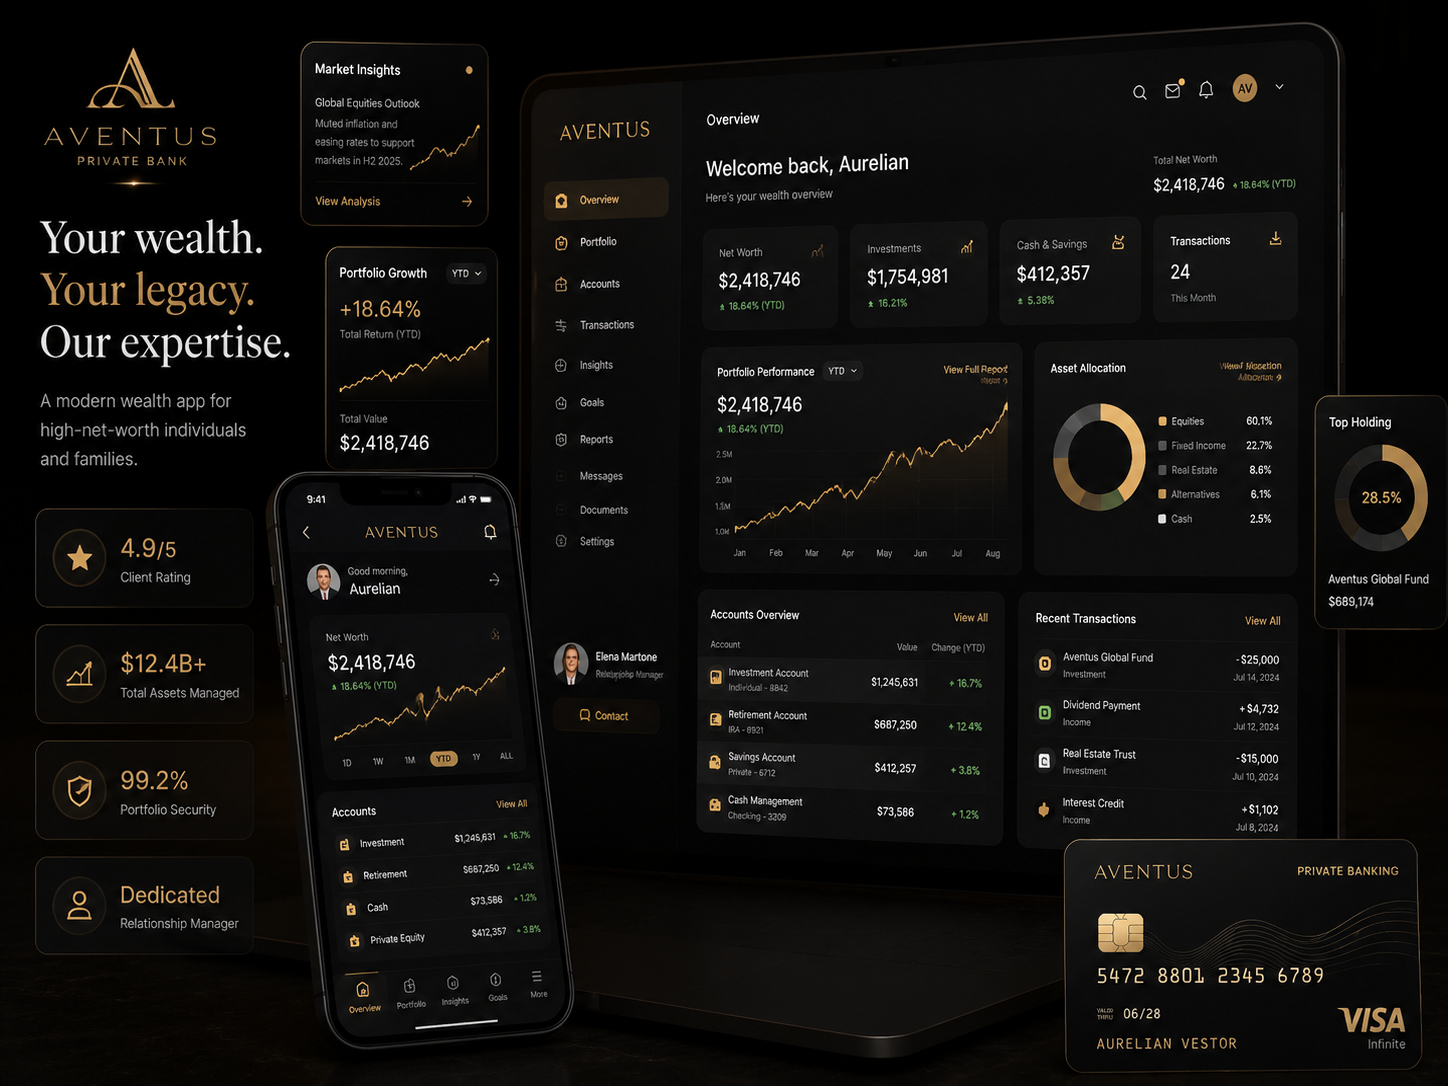
MiFID-compliant investing app doubled monthly active clients.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
We don't compete on lowest day-rate. We compete on shipped outcomes inside environments that have to clear audit.
Every engineer on every engagement is at least senior, typically eight to fifteen years deep in their craft. No bench rotations, no junior pyramid hidden behind a glossy proposal, no bait-and-switch after contract signature. The architect who scoped your engagement is the same person committing code by week three.
FCA, PRA, EBA, BaFin, FINMA, HIPAA, SOC 2 Type II: every framework we work under is treated as a design constraint from day one, not a final-stage gate. Evidence trails, model-risk packs, change-control artefacts, and pen-test reports ship alongside the code, ready for second-line review without a remediation sprint.
Small pods of three to seven engineers, each with a named delivery lead who owns scope, schedule, and outcomes from kickoff to hand-off, never a faceless team you have to chase for an answer. Weekly demos run against the signed scope, frequent verification gates catch regressions early, and quarterly outcome reviews measure real progress against the original business case rather than a moving target. Together those rituals catch scope drift before it has any chance to compound, so programmes that should take six months don't quietly stretch into eighteen, budgets stay anchored to what was agreed, and every milestone ships with a written, testable definition of done that both sides sign off before we move on.
We don't disappear the moment the engagement closes. Managed services, hypercare windows, named on-call rotations, or quarterly health checks: pick the depth that matches your operational risk profile. About seventy percent of clients return for a second programme, usually because the team that shipped the first one is still on the other end of the page.
Anonymous under MNDA. Each quote is from a senior buyer who owned the engagement end to end across the services catalogue.
“BritonOne Technology replaced two of our incumbent vendors with one team. Faster sprints, fewer status meetings, more code shipped per week.”