Penetration Test That Found Real Risk
“Their pen-test team surfaced two findings our previous vendor had marked clean. The retest was tight, the report was board-ready.”
Head of SecurityInsurance-tech scale-up, EU
Sixty senior engineers across AI, software, cloud, data, and security, composed into one accountable team, shipping under audit, ready in days not months.
Delivery inside regulated estates across the UK and EU
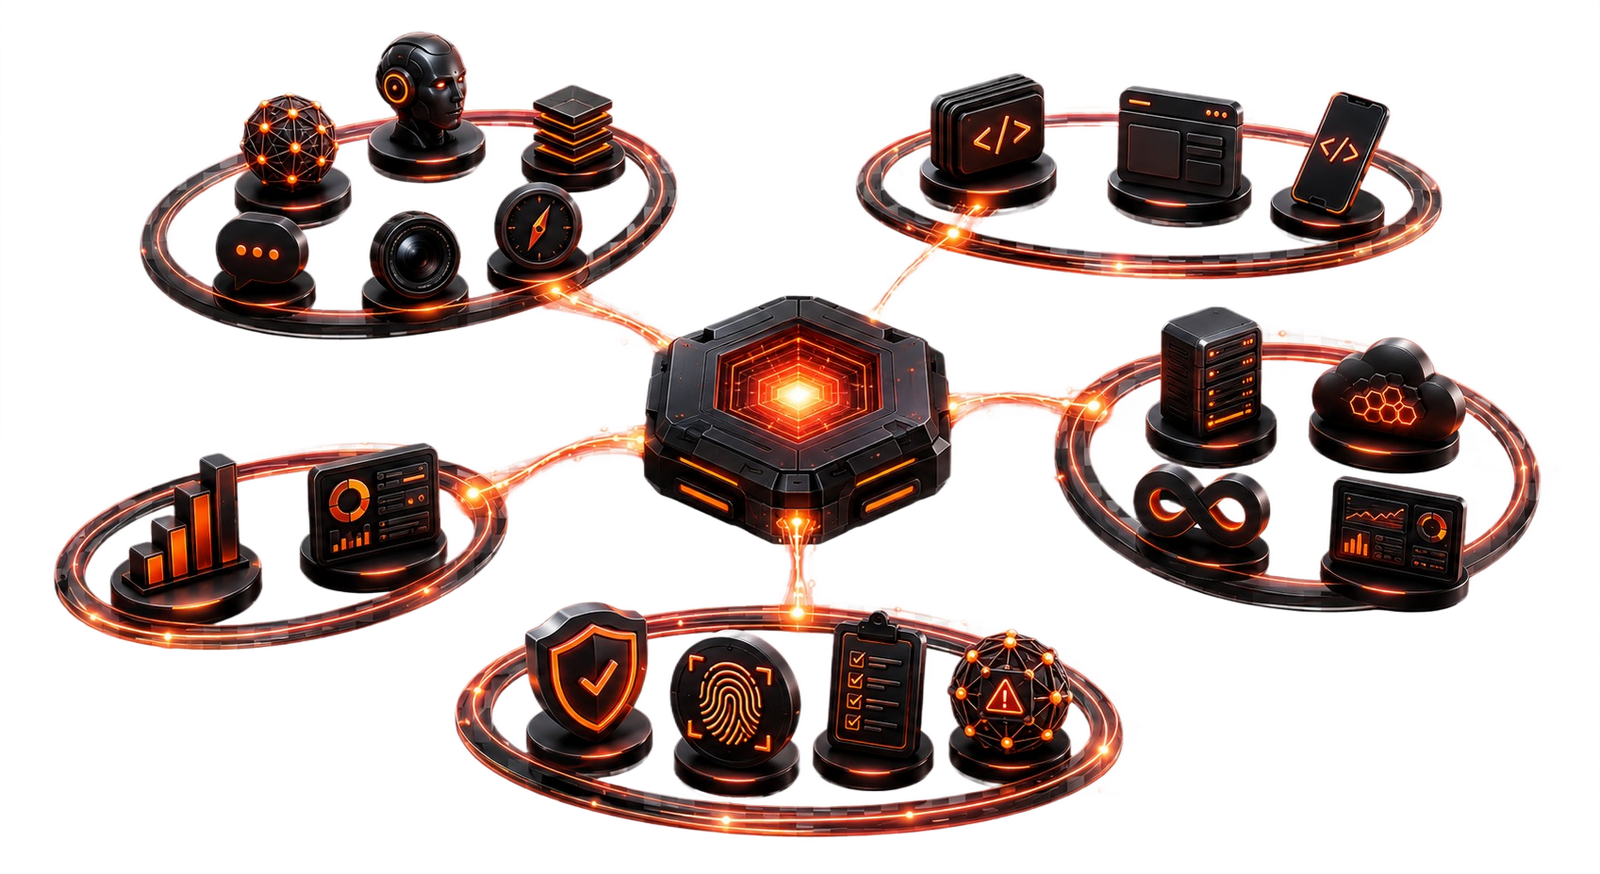
Two ways we engineer software: pick the discipline that fits your problem shape. Every engagement composes both where it pays for itself.
Structured, rule-based, deterministic. Built on proven human methodologies and explicit code that an auditor can read.
Experimental, adaptive, probabilistic. Data-driven models, continuous learning, and automated optimisation, engineered to clear audit.
Pick the discipline that matches your problem. Each category groups every sub-service we offer, composed under one accountable line.
Generative AI, agentic systems, machine learning, NLP, computer vision, and consulting, production-grade and audit-ready.
Custom software, web, and mobile builds, designed, engineered, and shipped end-to-end by senior product teams.
Cloud migration, platform engineering, DevOps, and managed operations on AWS, Azure, and GCP.
Data engineering, analytics, and business intelligence, pipelines that survive auditor scrutiny and BI that drives decisions.
Penetration testing, IAM and zero-trust, compliance, and threat modelling, security-by-design from day one.
Manual, automated, performance, API, and security testing, quality gates that catch the right defects at the right stage.
Blockchain development, smart contracts, DeFi, and advisory, engineered for regulated tokenisation and settlement.
These are the services we ship most often, each backed by senior specialists, reference architectures, and case studies you can read.
We pick the boring, proven option by default, and reach for novelty only where it pays for itself. These are the tools we run in production.
 OpenAI
 Anthropic
 PyTorch
 TensorFlow
 LangChain
 Hugging Face
 Pinecone
 scikit-learn
Switch between categories below to see every discipline we run. Click any service to open the detail page.
Production AI for regulated estates, from strategy to safety controls.
Every engagement walks the same path, sized to your problem, but with the same verification gates baked in.
Two-week paid sprint. Architect-led. Output: regulator map, costed roadmap, signed scope.
Pod composition, sequenced milestones, change-control governance, and risk register.
Reference architecture, threat model, design system, and acceptance criteria locked.
Weekly demos, trunk-based, CI/CD from day one. Code reviewed against spec at every gate.
Unit, integration, e2e, security, performance, and accessibility, automated and gated.
Blue-green or canary, observability live before launch, rollback rehearsed.
Managed services or hypercare hand-off. Defined SLOs, named on-call, monthly reviews.
Success stories
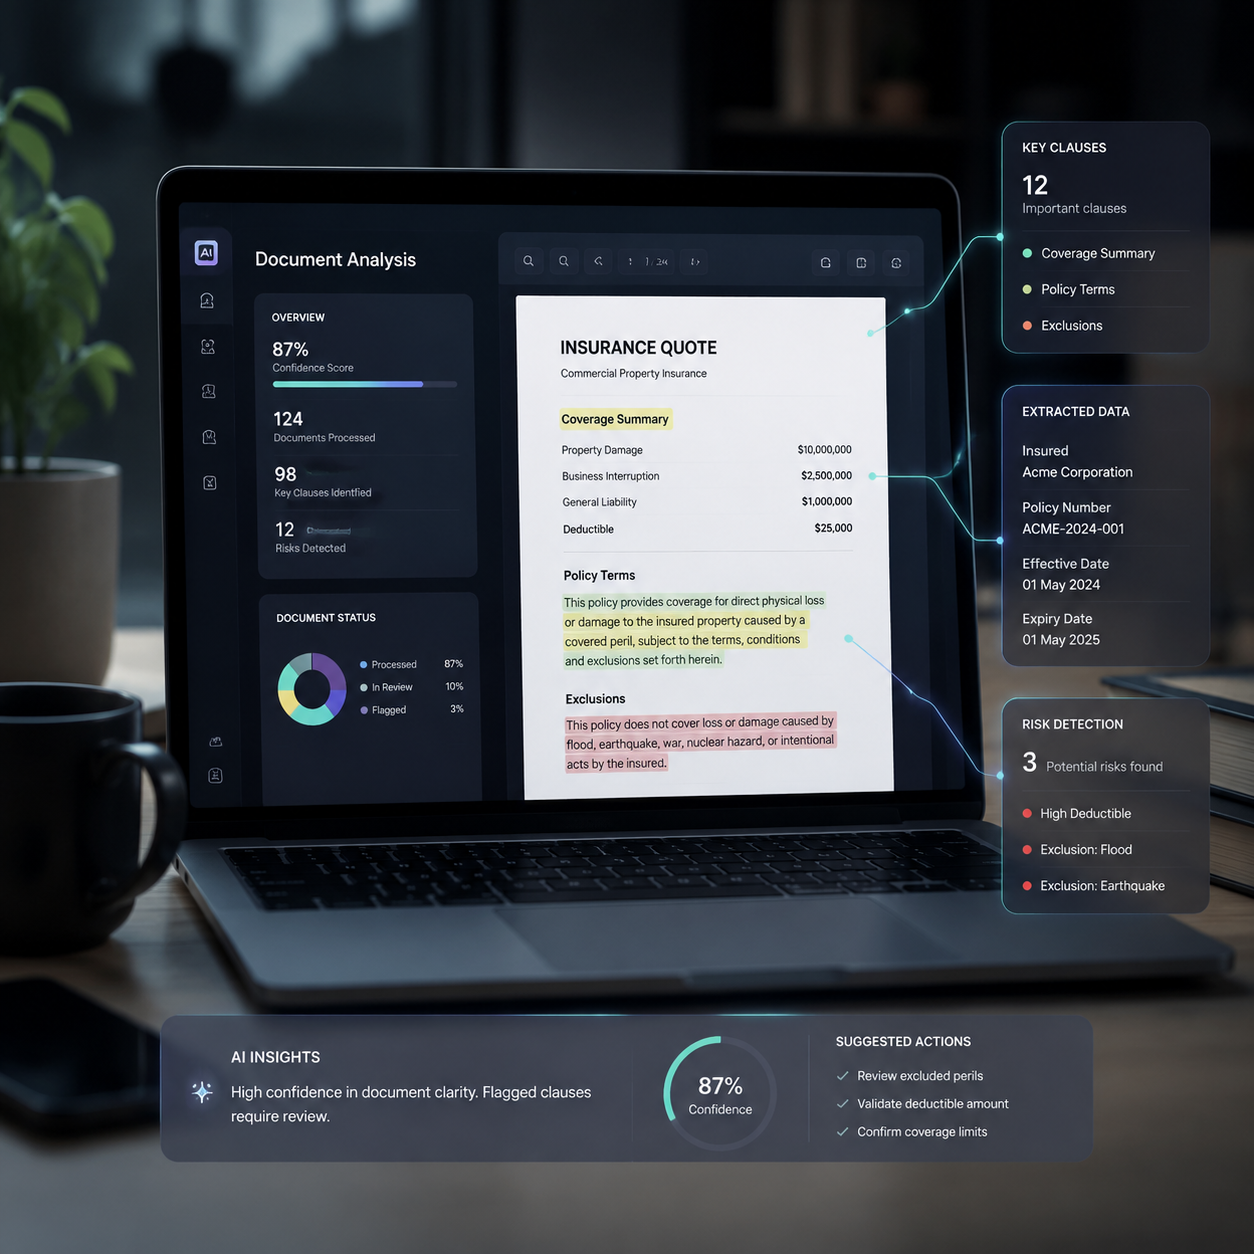
Drafted first-pass quotes from submission packs 3.1x faster, every clause cited back to the wording it came from.
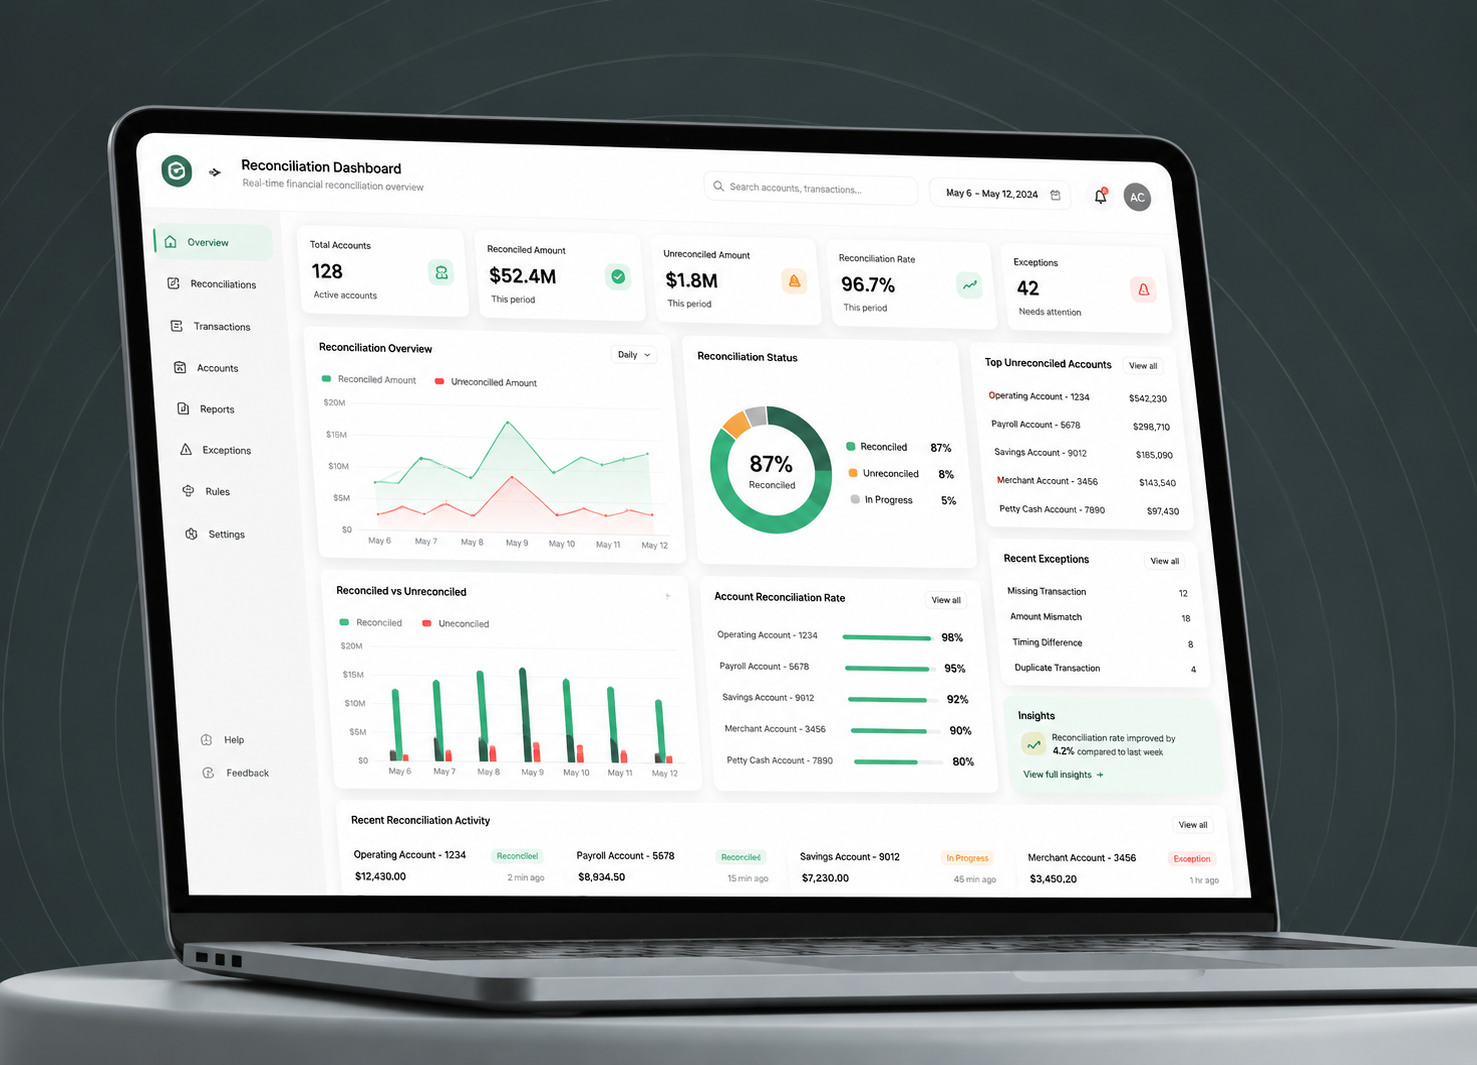
Resolved 89% of reconciliation breaks without a human, every action logged for audit.
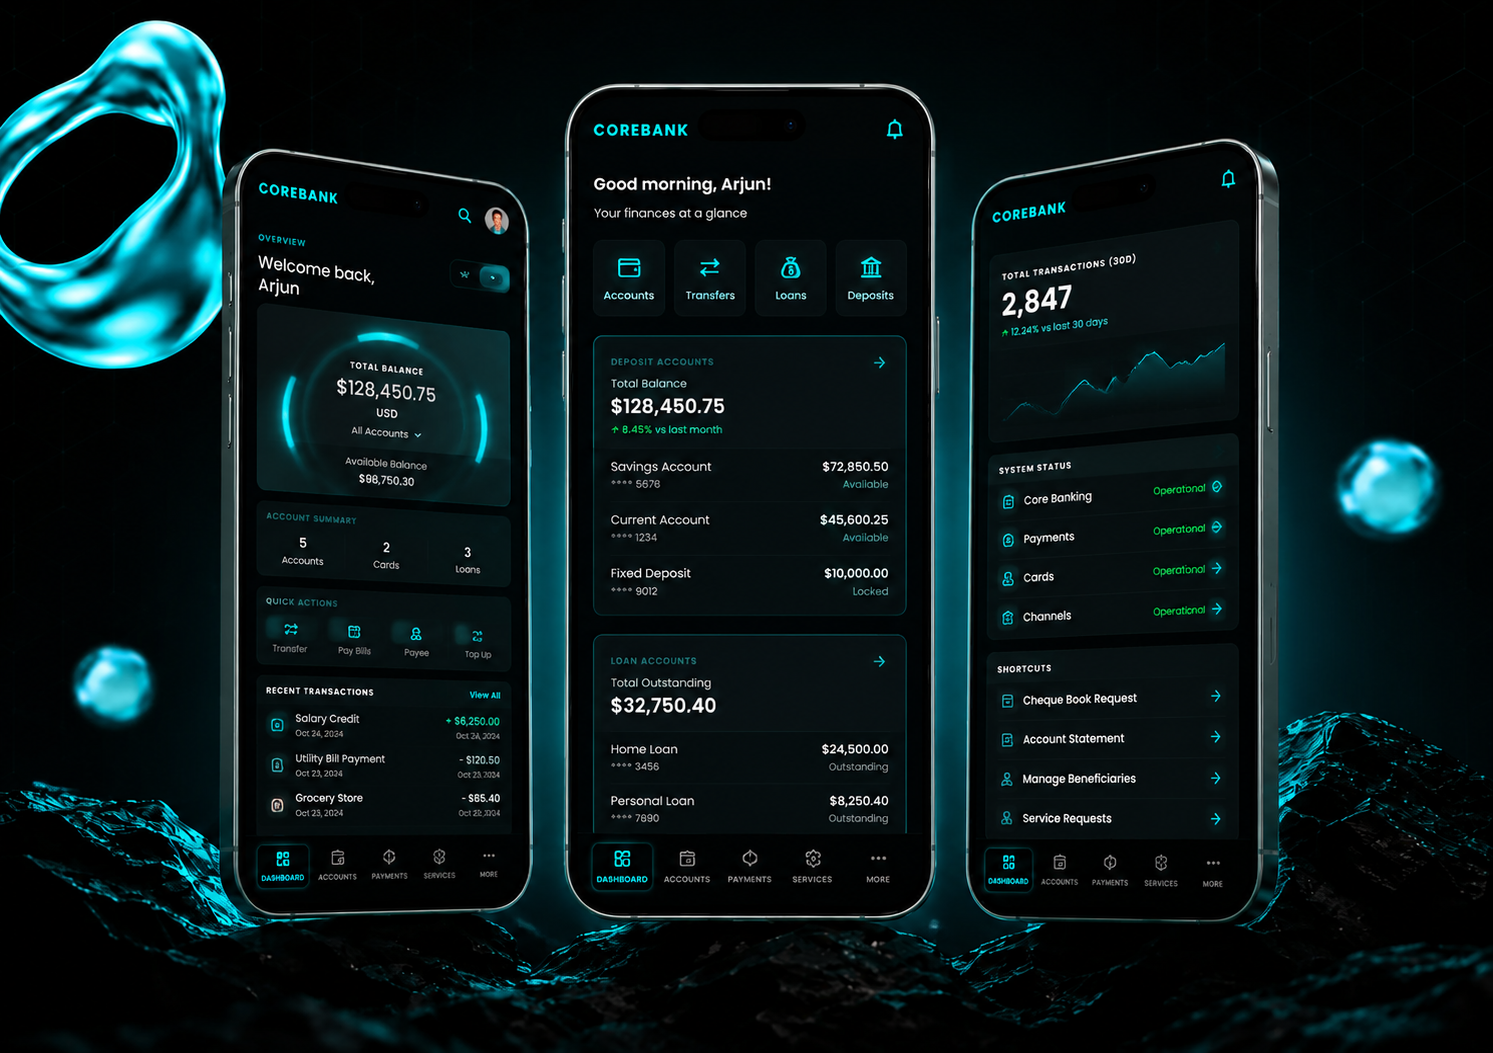
Ledger, accounts, and payment rails delivered to an FCA launch milestone in 9 months.
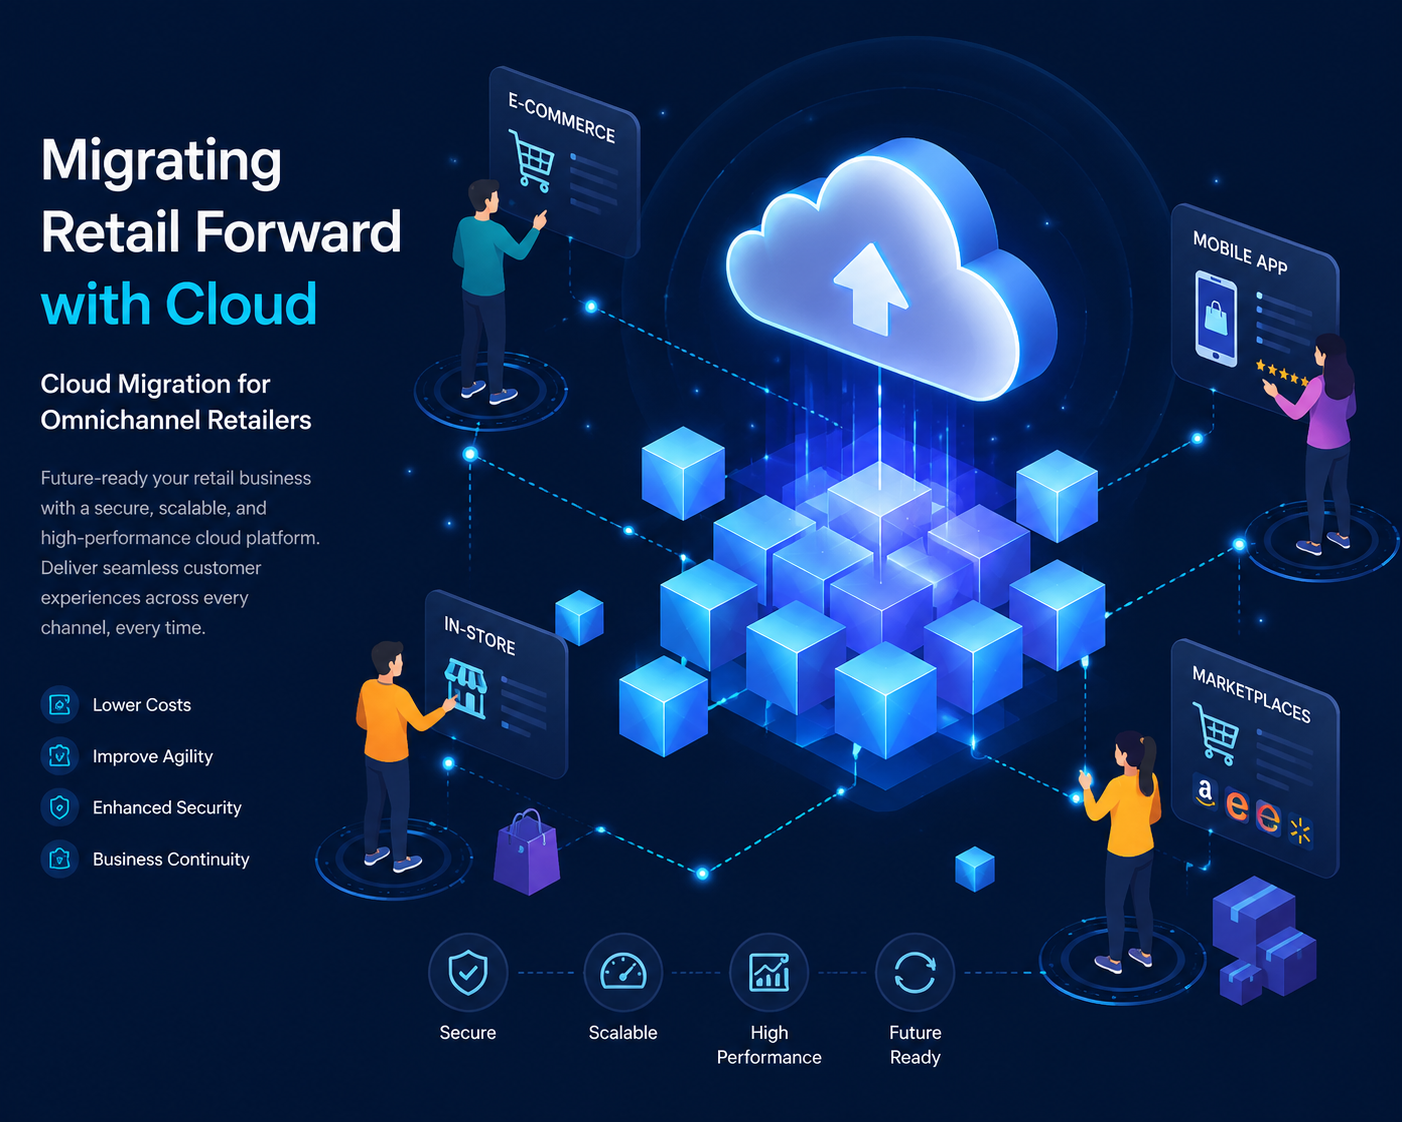
Re-platformed e-commerce to the cloud, holding availability through a record peak-season trading day.
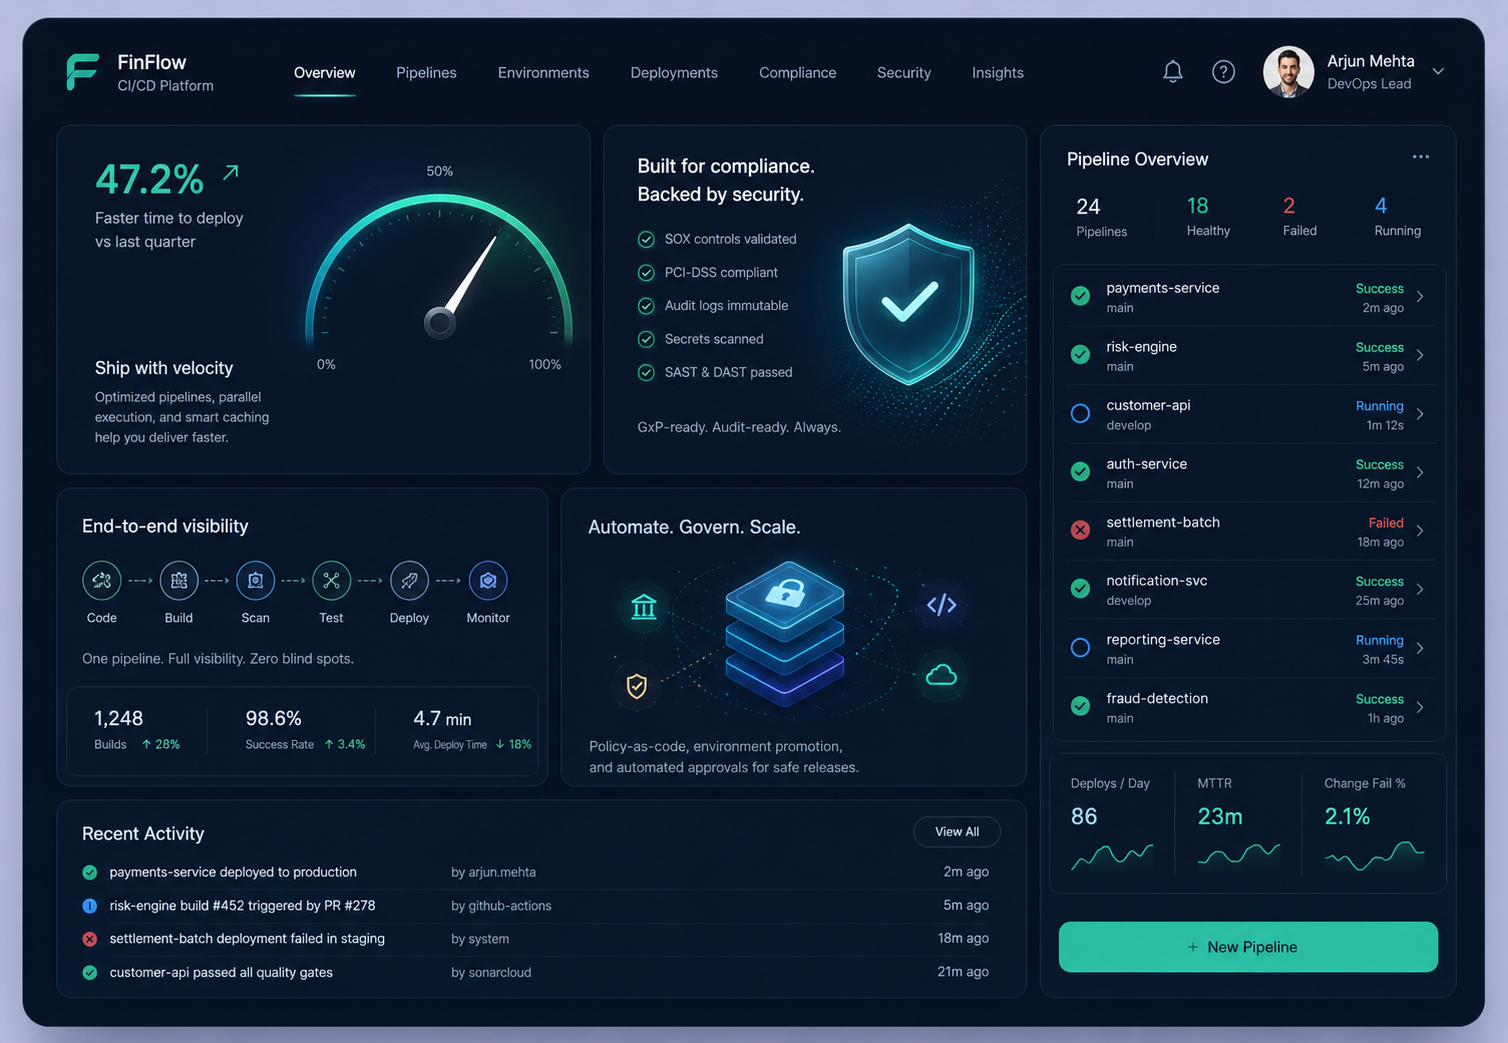
Lifted release frequency 15x with automated gates and one-click rollback.
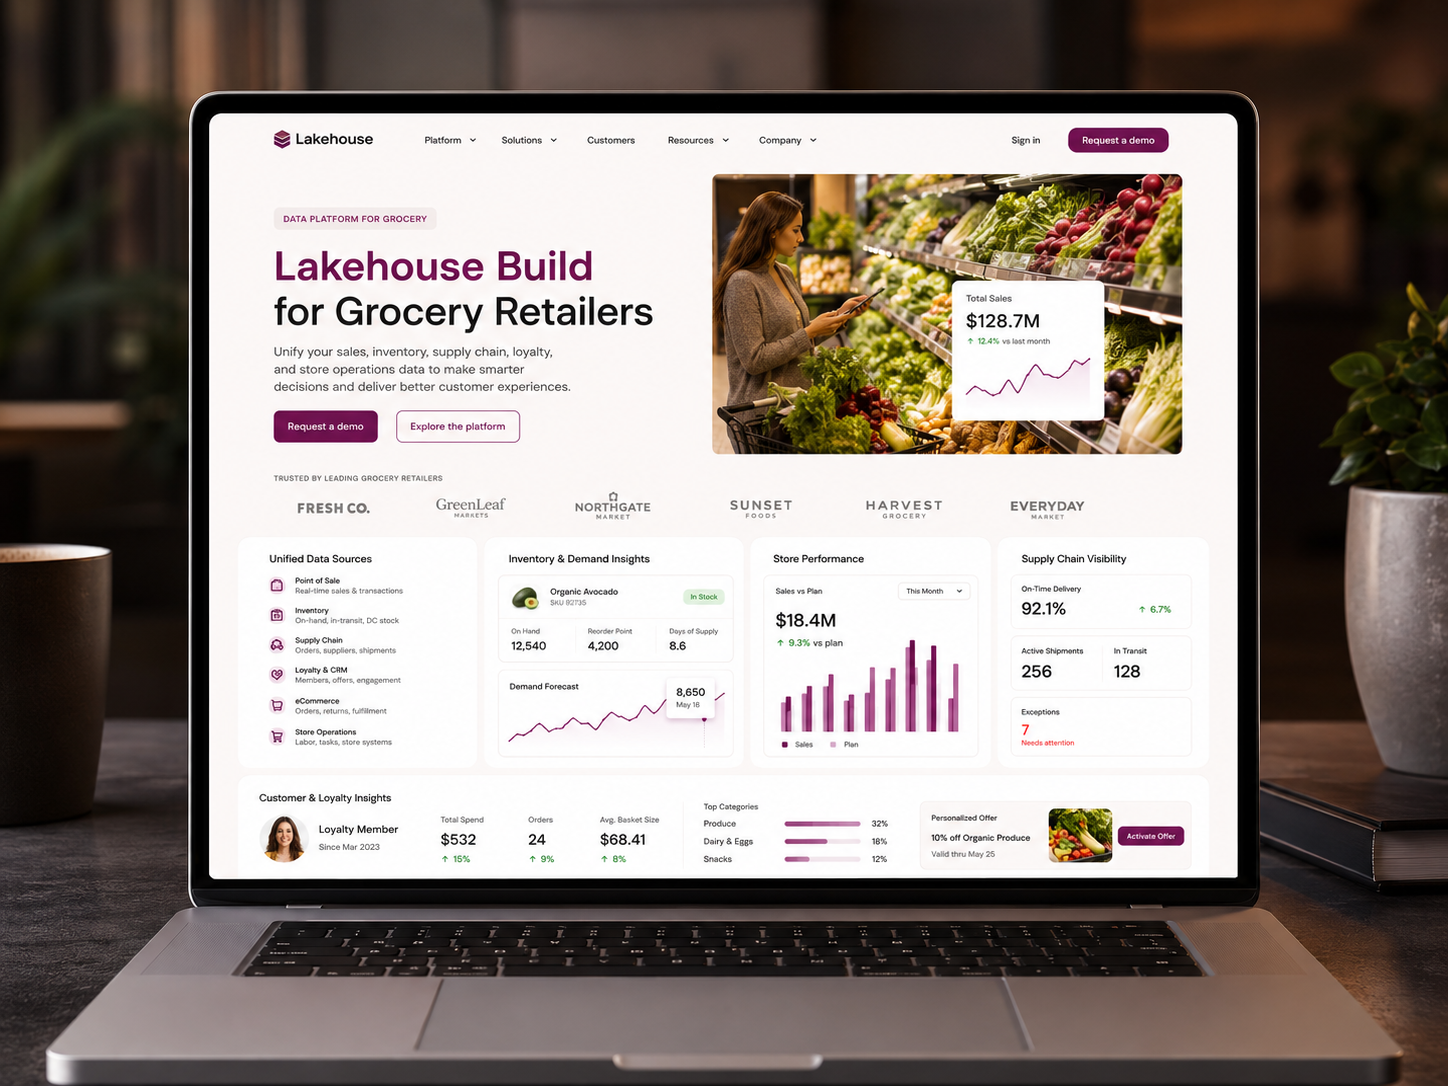
Unified 40 sources into a governed lakehouse, cutting report build time 60% for a grocery retailer.
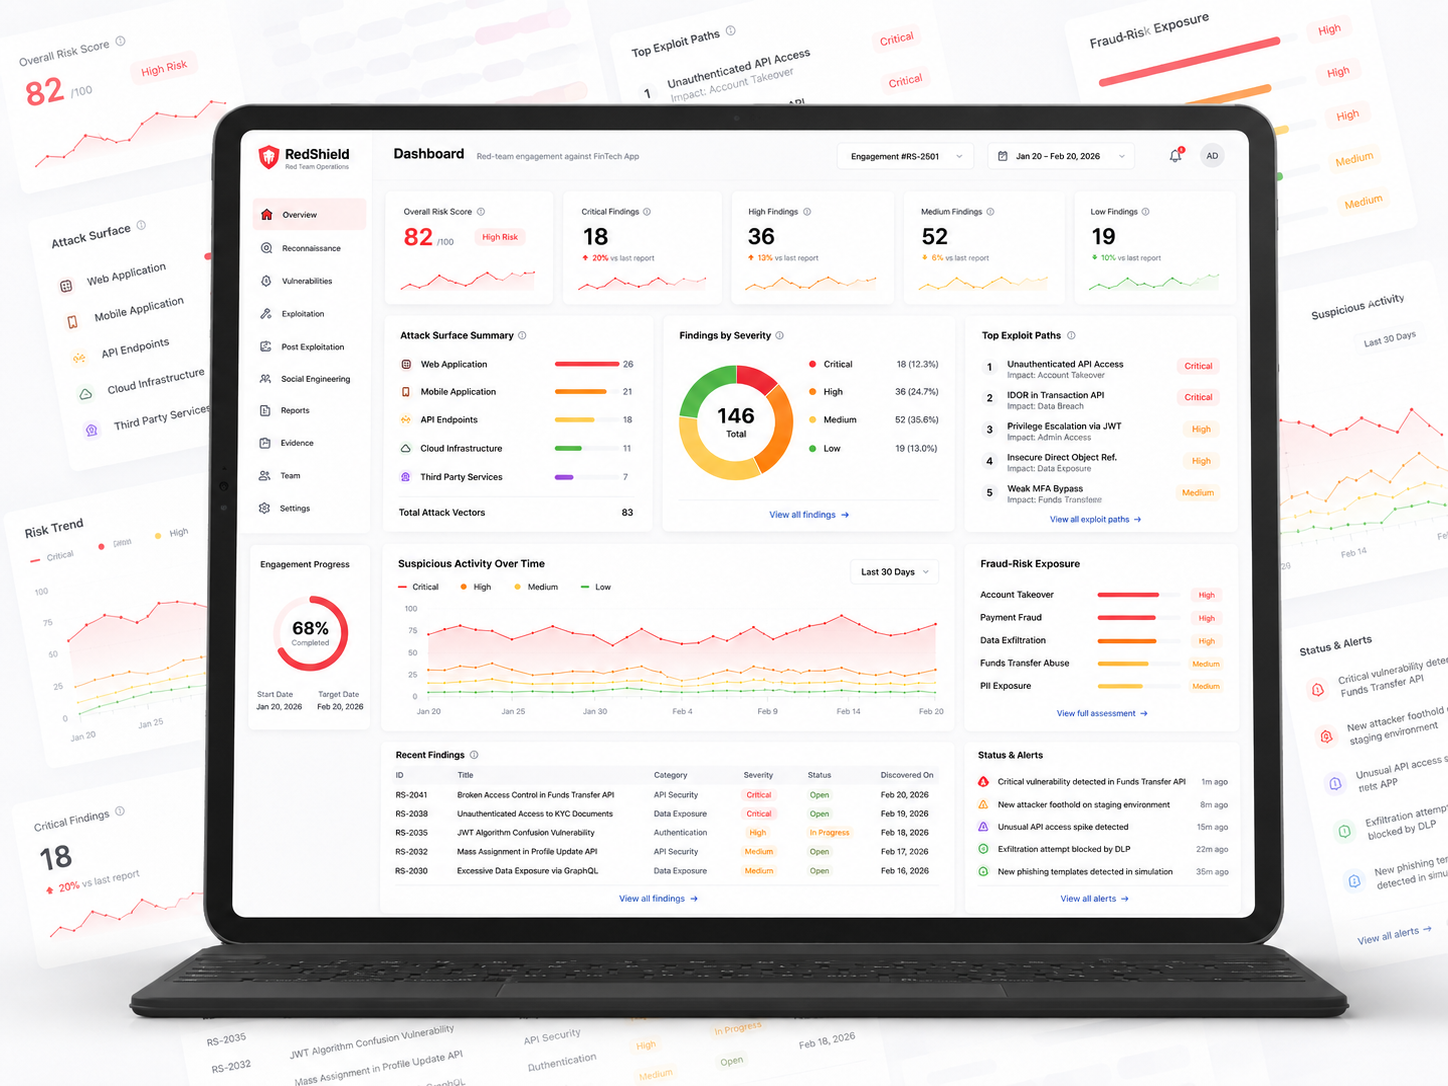
Found and helped close three account-takeover paths before a fintech's launch.
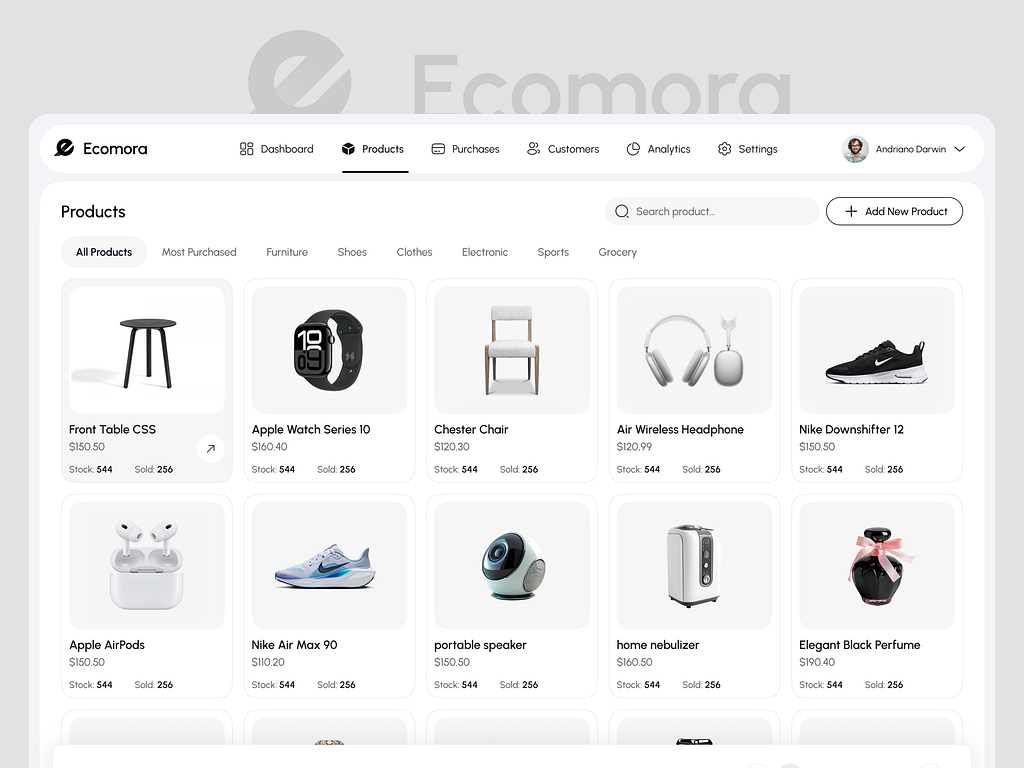
Functional and exploratory testing across catalogue, search, filters, and checkout caught layout and data defects before go-live, so a US retailer launched its new store with no customer-facing incidents.
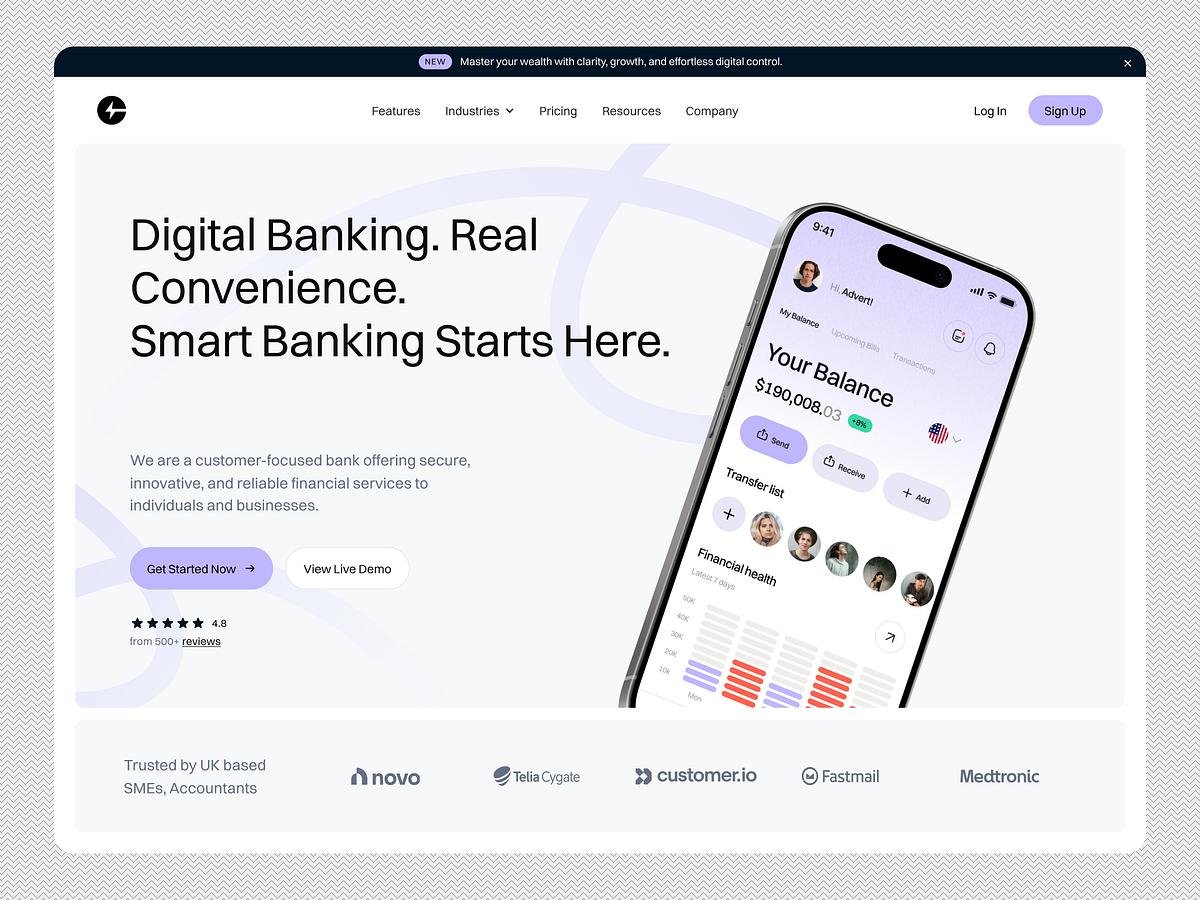
Delivered 10,000+ automated assertions across balance, transfer, and payment APIs, catching every schema and auth regression before release for a digital bank.
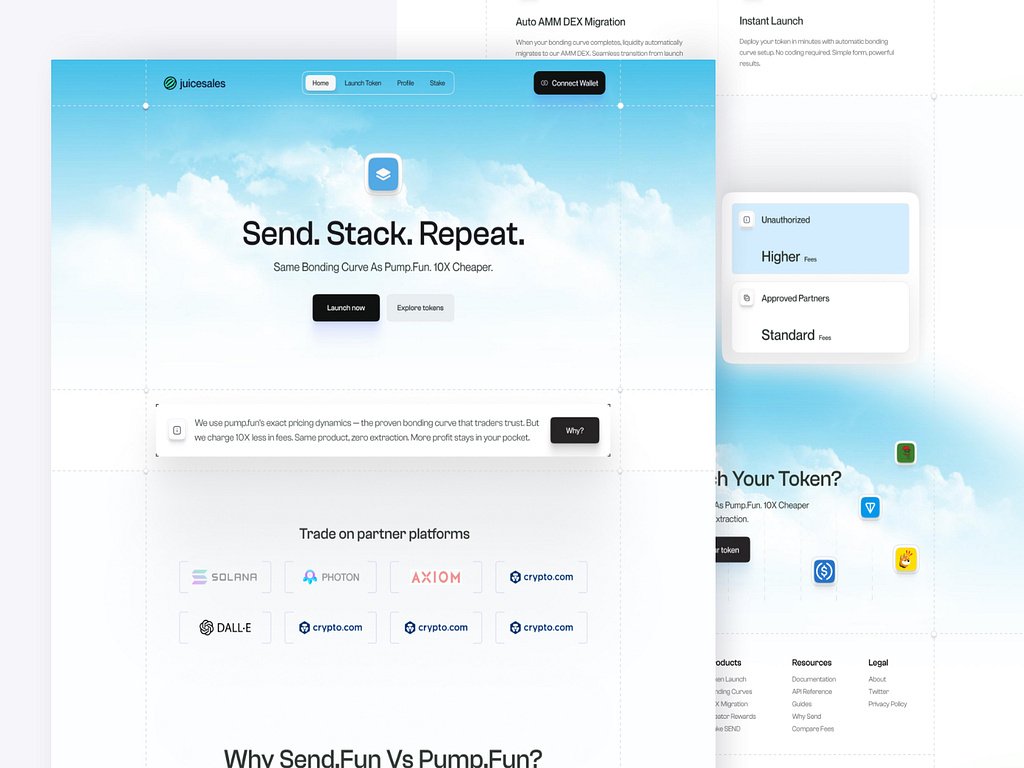
Shipped a bonding-curve launchpad with automated AMM migration and wallet-connected minting that cut issuance fees roughly tenfold for a digital-asset bank.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
We don't compete on lowest day-rate. We compete on shipped outcomes inside environments that have to clear audit.
Every engineer on every engagement is at least senior, typically eight to fifteen years deep in their craft. No bench rotations, no junior pyramid hidden behind a glossy proposal, no bait-and-switch after contract signature. The architect who scoped your engagement is the same person committing code by week three.
FCA, PRA, EBA, BaFin, FINMA, HIPAA, SOC 2 Type II: every framework we work under is treated as a design constraint from day one, not a final-stage gate. Evidence trails, model-risk packs, change-control artefacts, and pen-test reports ship alongside the code, ready for second-line review without a remediation sprint.
Small pods of three to seven engineers, each with a named delivery lead who owns scope, schedule, and outcomes from kickoff to hand-off, never a faceless team you have to chase for an answer. Weekly demos run against the signed scope, frequent verification gates catch regressions early, and quarterly outcome reviews measure real progress against the original business case rather than a moving target. Together those rituals catch scope drift before it has any chance to compound, so programmes that should take six months don't quietly stretch into eighteen, budgets stay anchored to what was agreed, and every milestone ships with a written, testable definition of done that both sides sign off before we move on.
We don't disappear the moment the engagement closes. Managed services, hypercare windows, named on-call rotations, or quarterly health checks: pick the depth that matches your operational risk profile. About seventy percent of clients return for a second programme, usually because the team that shipped the first one is still on the other end of the page.
Anonymous under MNDA. Each quote is from a senior buyer who owned the engagement end to end across the services catalogue.
“BritonOne Technology replaced two of our incumbent vendors with one team. Faster sprints, fewer status meetings, more code shipped per week.”