
Connected-vehicle cloud
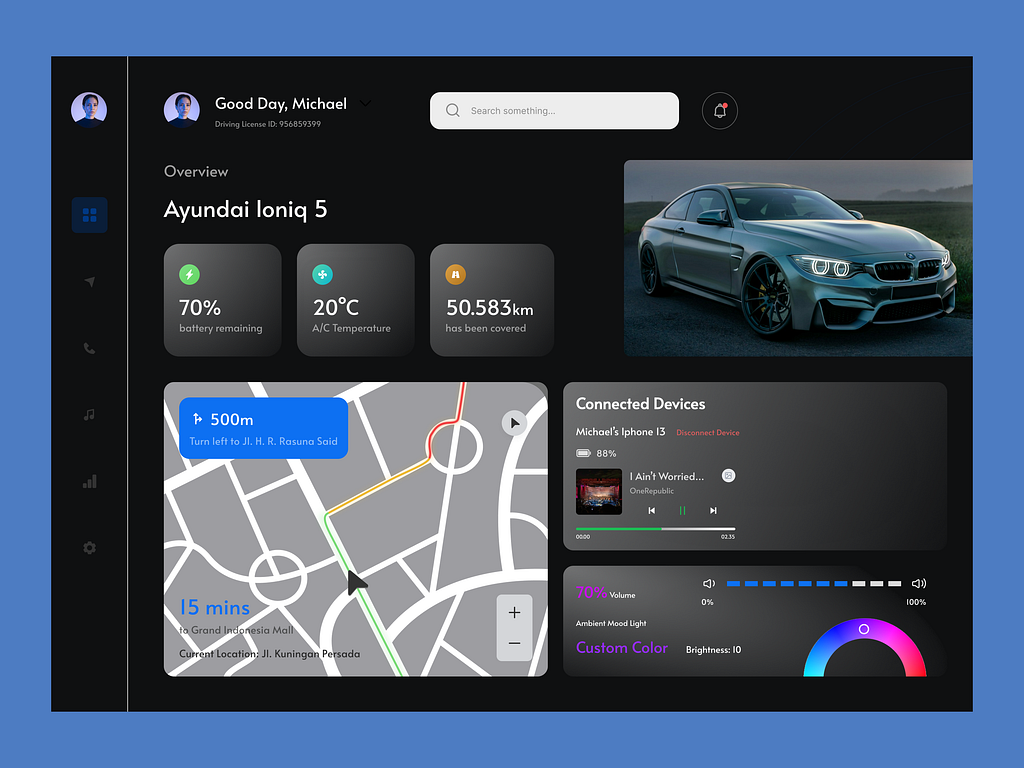
Live vehicle-state sync, telemetry, and remote diagnostics, battery, cabin, odometer, and navigation streamed to one cloud.
Connected-vehicle cloud, OTA, ADAS, dealer digital, and EV charging, built by senior teams behind 2M+ vehicle estates.
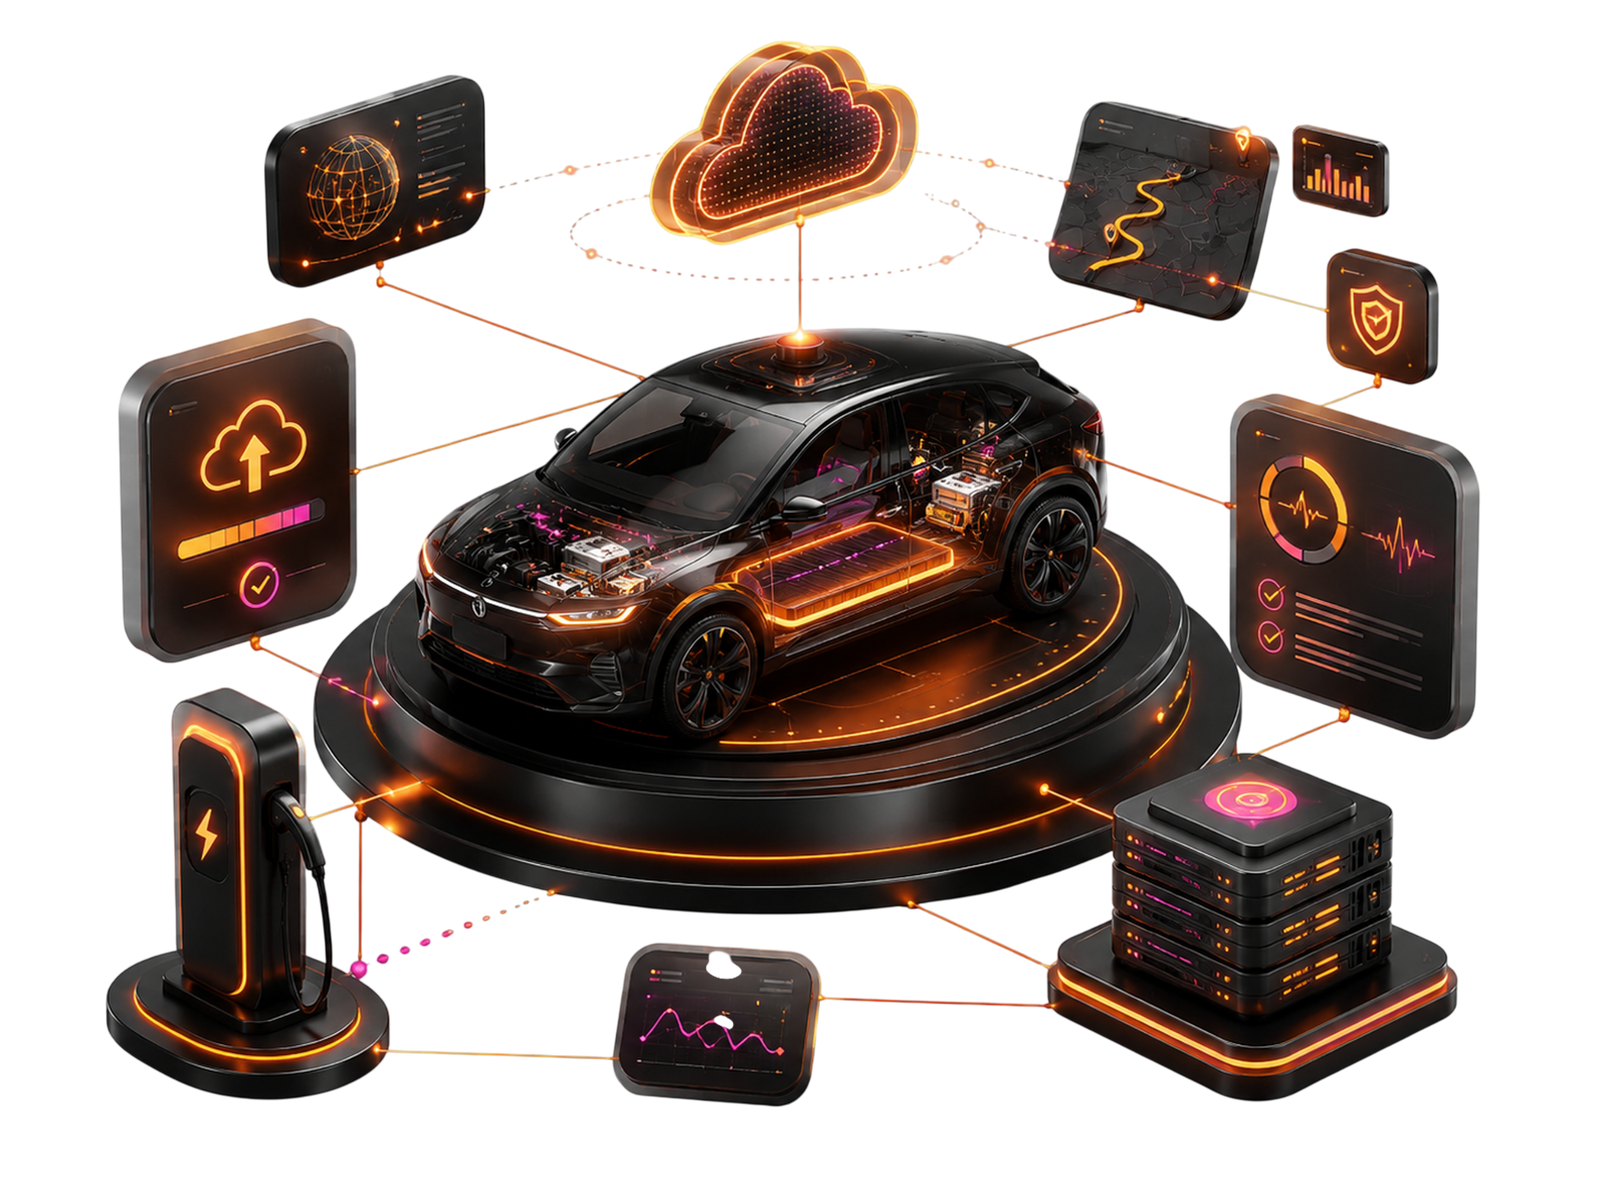
Cloud to vehicle to dealer floor, everything that keeps connected fleets safe, updated, and serviced, by one senior pod.
01 / 06Live vehicle-state sync, telemetry, and remote diagnostics, battery, cabin, odometer, and navigation streamed to one cloud.
Live vehicle-state sync, telemetry, and remote diagnostics, battery, cabin, odometer, and navigation streamed to one cloud.
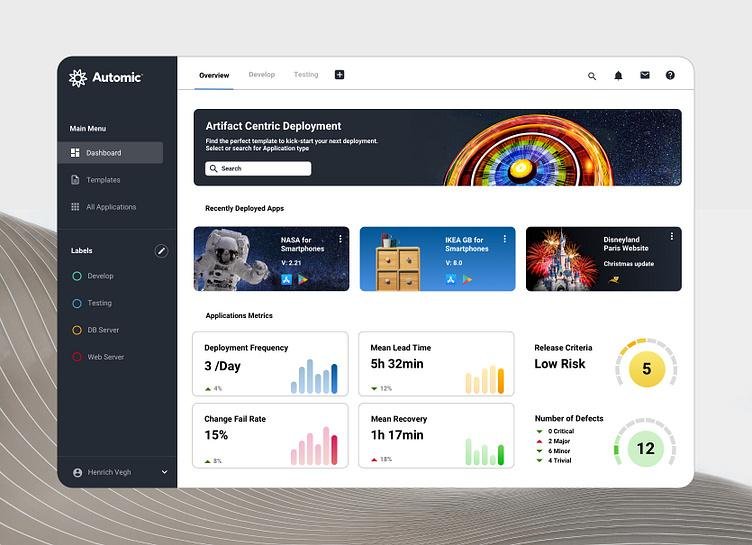
Signed, phased rollouts tracked on deployment-frequency, change-fail-rate, and recovery metrics, with a full UNECE R156 evidence trail.
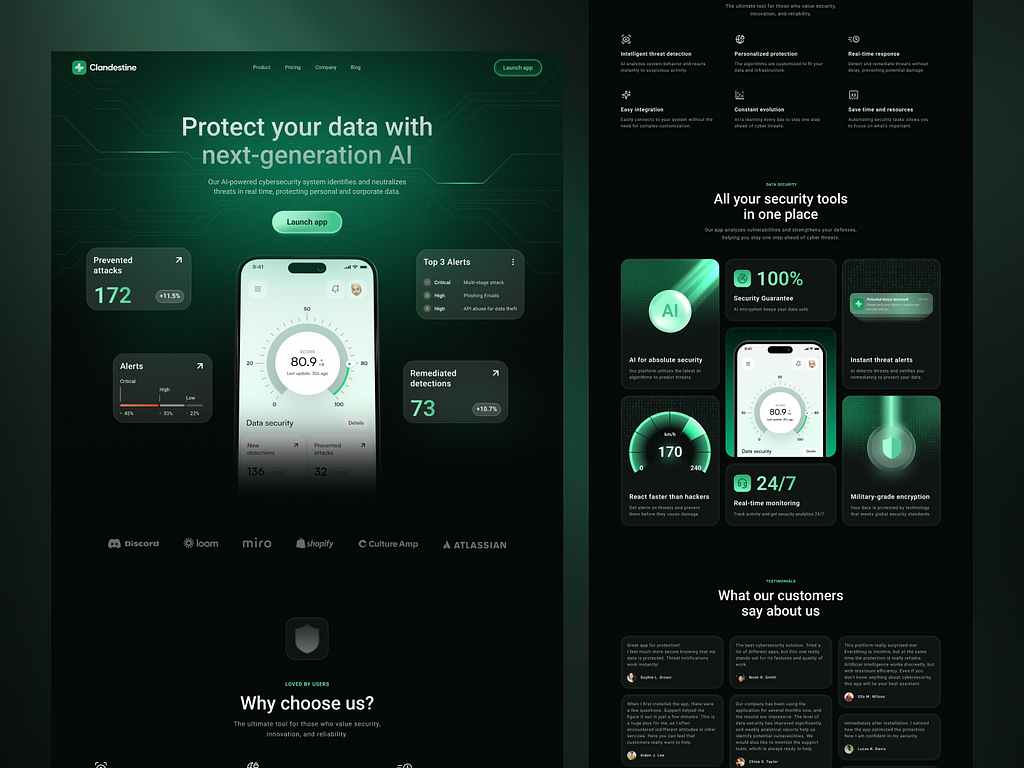
CSMS with AI-assisted threat detection, monitoring, and response, type-approval evidence and live counts on prevented attacks and remediations.
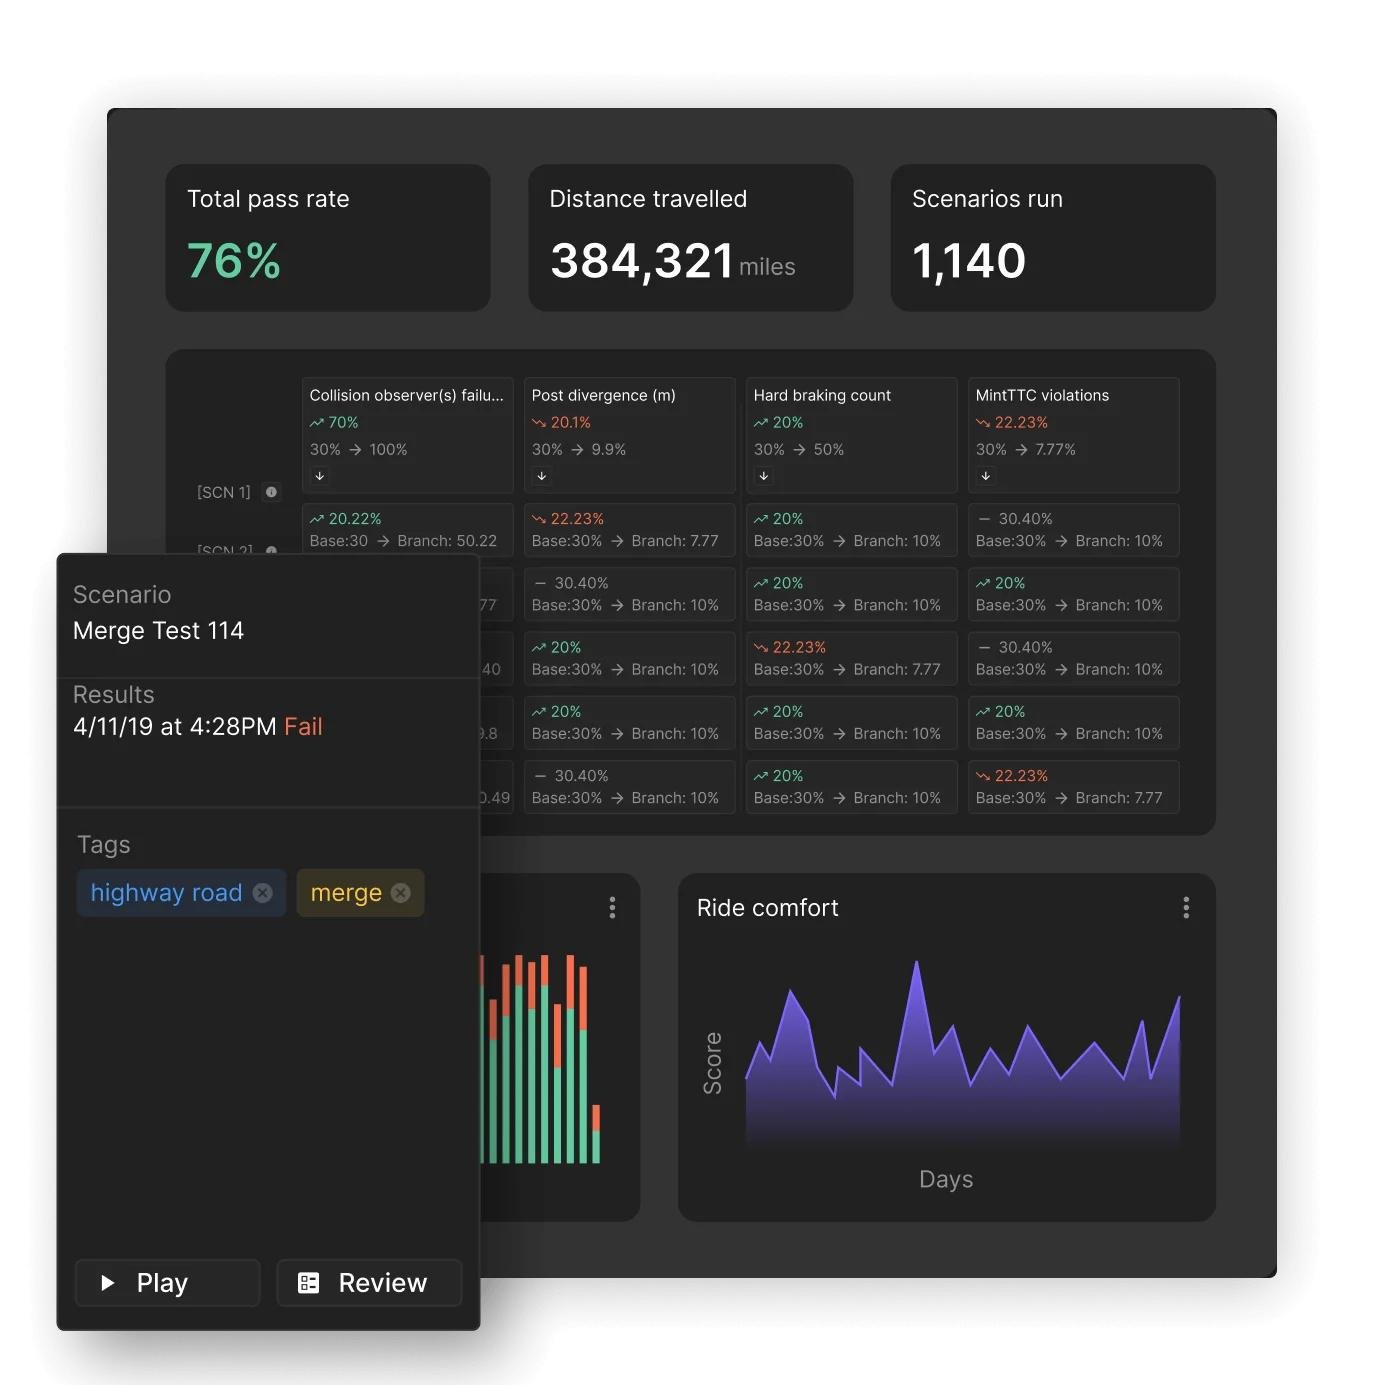
Scenario simulation and ASIL-D validation at scale, collision, time-to-collision, and hard-braking metrics across thousands of runs.
Dealer storefront, vehicle listings, and lead capture, wired to DMS, service booking, and predictive maintenance to lift conversion.
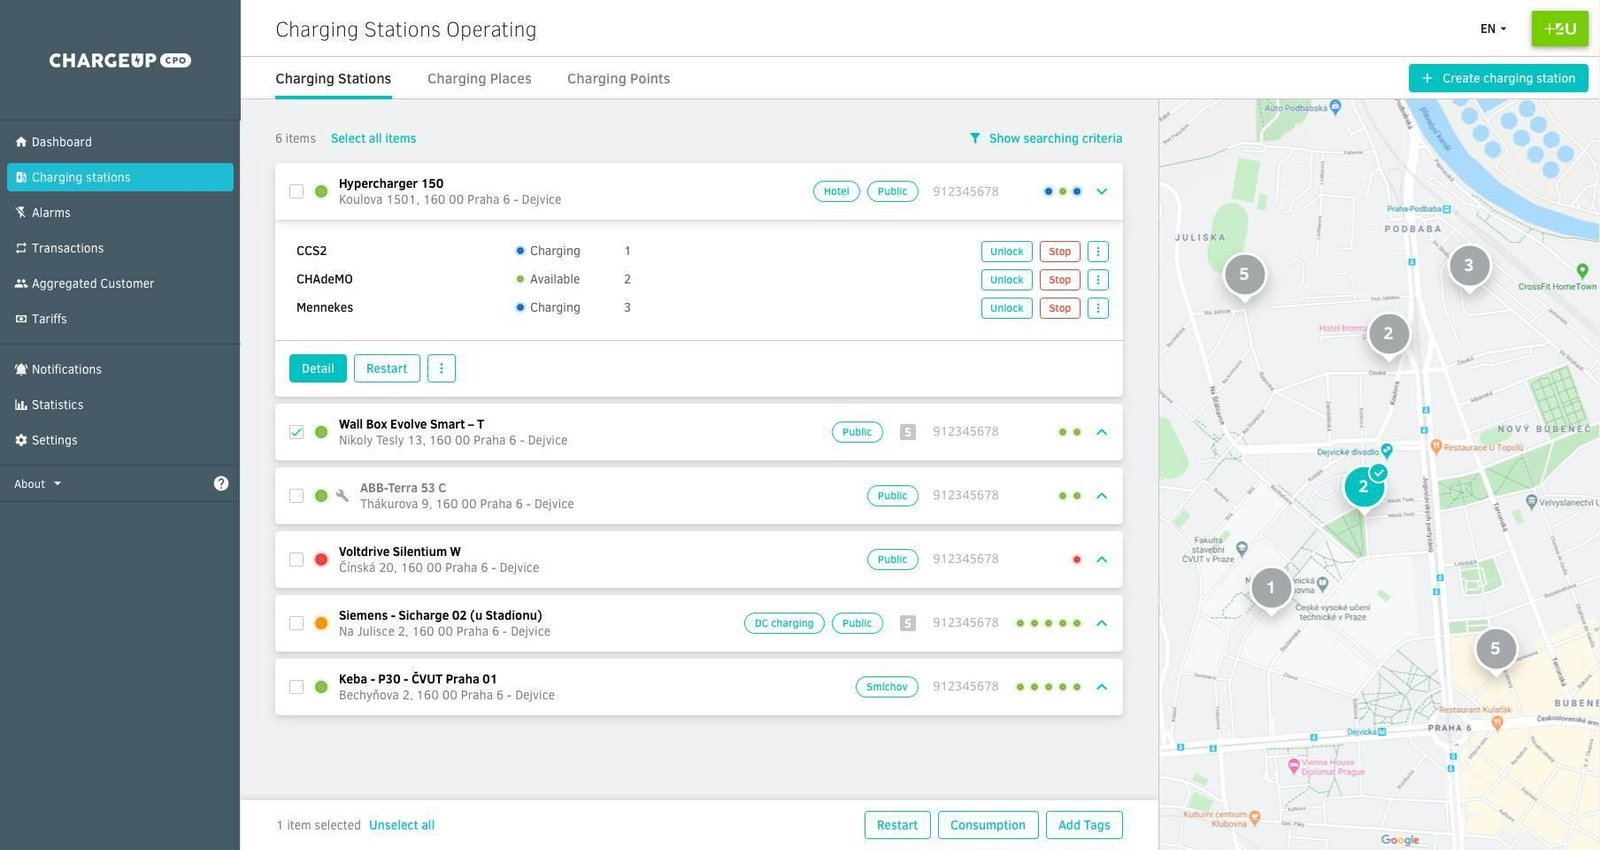
OCPP charge-point management with live connector status, remote start/stop, and site mapping across the charging estate.
Vehicle software is judged against type approval and functional safety. We build with the rigour to clear the audit on first submission.
CSMS and SUMS documentation produced as integrated engineering output, evidence-ready for the Type Approval Authority on first submission.
ISO 26262 ASIL classification and traceability from concept through production, safety artefacts, not a retrofit compliance exercise.
Dual-bank firmware, signed packages, canary cohorts, and automatic rollback on metric thresholds, every update history queryable for audit.
Connected-vehicle cloud and CPMS built for millions of vehicles and tens of thousands of concurrent sessions, with multi-region failover.
Selected programmes across OEMs, Tier-1 suppliers, charging operators, and mobility platforms, anonymised where required, specific on the outcome.
Telemetry, ADAS ingestion, and OTA orchestration on AWS Auto Cloud, the CSMS cleared type approval on first submission.
Defined and measured software lifecycle for ADAS firmware under ISO 26262 ASIL-D, OEM capability bar met on first independent assessment.
Charge-point management with plug-and-charge, OCPI roaming, and grid-aware load, 18,000 active sessions through peak demand.
Insurance-grade behaviour scoring and a driver companion app across a connected fleet, 96,000 vehicles live on one platform.
Service-booking platform integrated with dealer DMSes and predictive maintenance, service-conversion rate up 21%.
Car-club, bike, e-scooter, and transit integration with single-fare authentication and journey planning, 240,000 registered users.
We ship on the platforms OEMs and operators actually run: vehicle-side, cloud-side, and tool-chain, each layer integrated against the next.
The connected core: telemetry, vehicle-state sync, and over-air diagnostics with multi-region failover.
On-board architecture and simulation, AUTOSAR integration with ADAS validation pipelines.
Type-approval-grade CSMS and SUMS with signed packages, rollback, and a full evidence trail.
Charge-point management with plug-and-charge, roaming, and grid-aware load management.
Dealer DMS and CRM integration, service booking and connected-customer lifecycle wired to one stream.
Privacy-preserving, access-by-design vehicle-data APIs with consent-managed, scope-limited access.
Every engagement walks the same path, sized to your problem, but with the same verification gates baked in.
Two-week paid sprint. Architect-led. Output: regulator map, costed roadmap, signed scope.
Pod composition, sequenced milestones, change-control governance, and risk register.
Reference architecture, threat model, design system, and acceptance criteria locked.
Weekly demos, trunk-based, CI/CD from day one. Code reviewed against spec at every gate.
Unit, integration, e2e, security, performance, and accessibility, automated and gated.
Blue-green or canary, observability live before launch, rollback rehearsed.
Managed services or hypercare hand-off. Defined SLOs, named on-call, monthly reviews.
Success stories
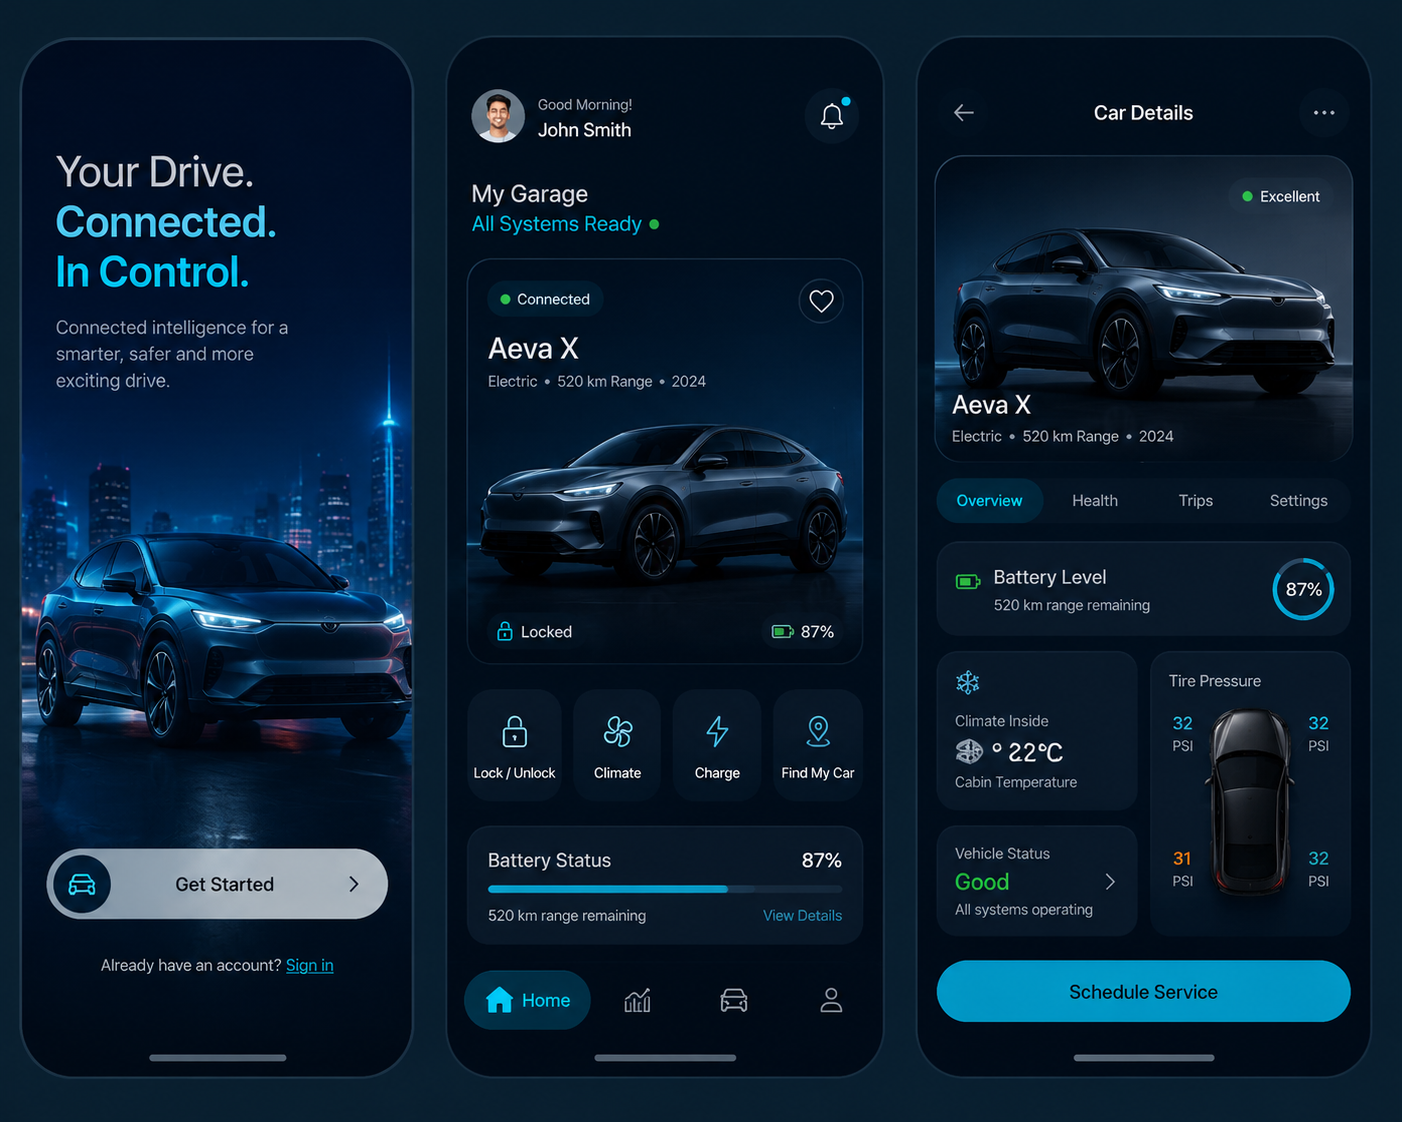
Built a cloud platform ingesting telemetry from 1.2M connected vehicles at scale.
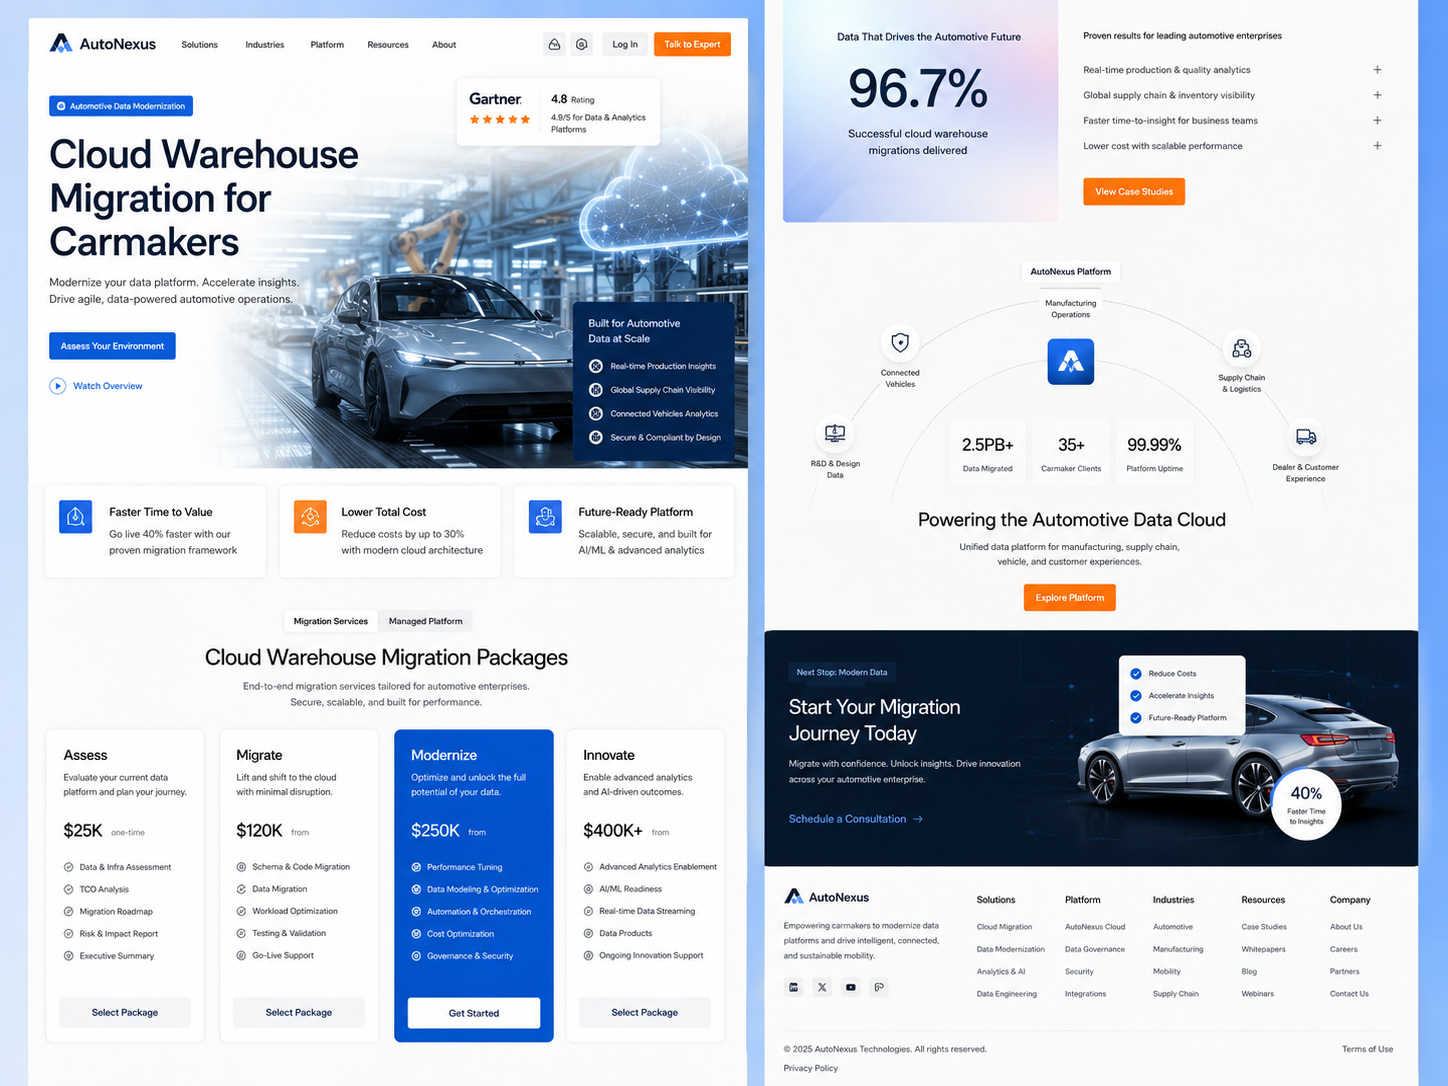
Migrated a legacy warehouse to the cloud, cutting query cost 45% for a carmaker.
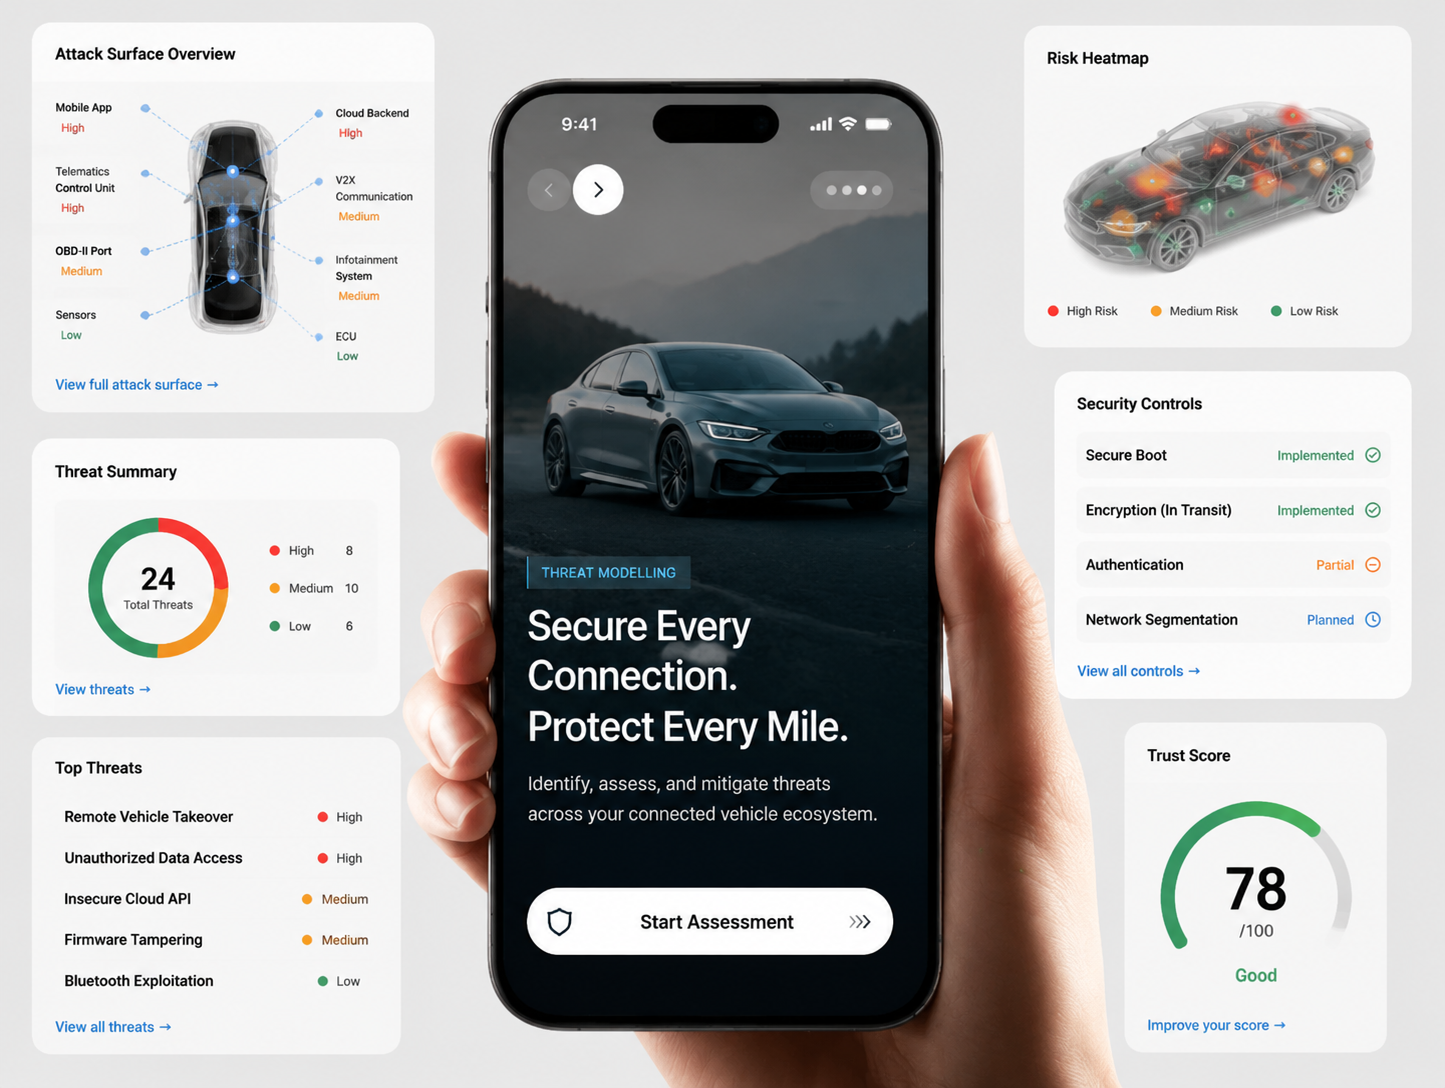
Mapped and mitigated attack paths for a UNECE R155-regulated connected vehicle.
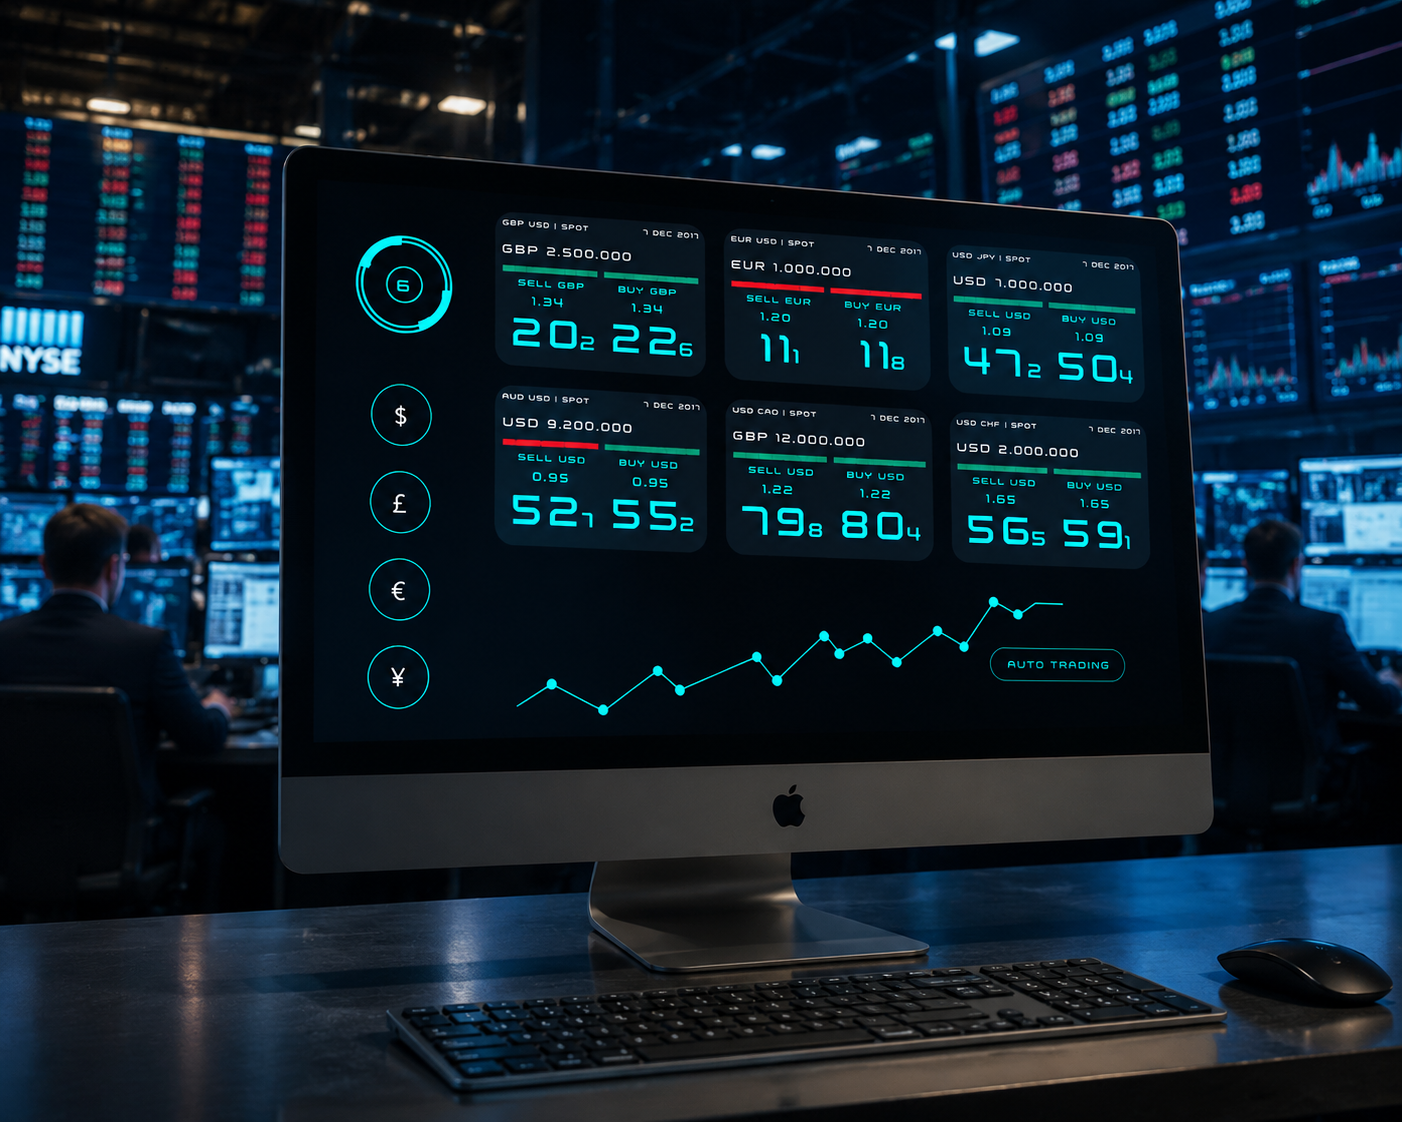
Cut median incident remediation from 41 to 7 minutes across a manufacturer's OT platform, with a human approval gate on every action.
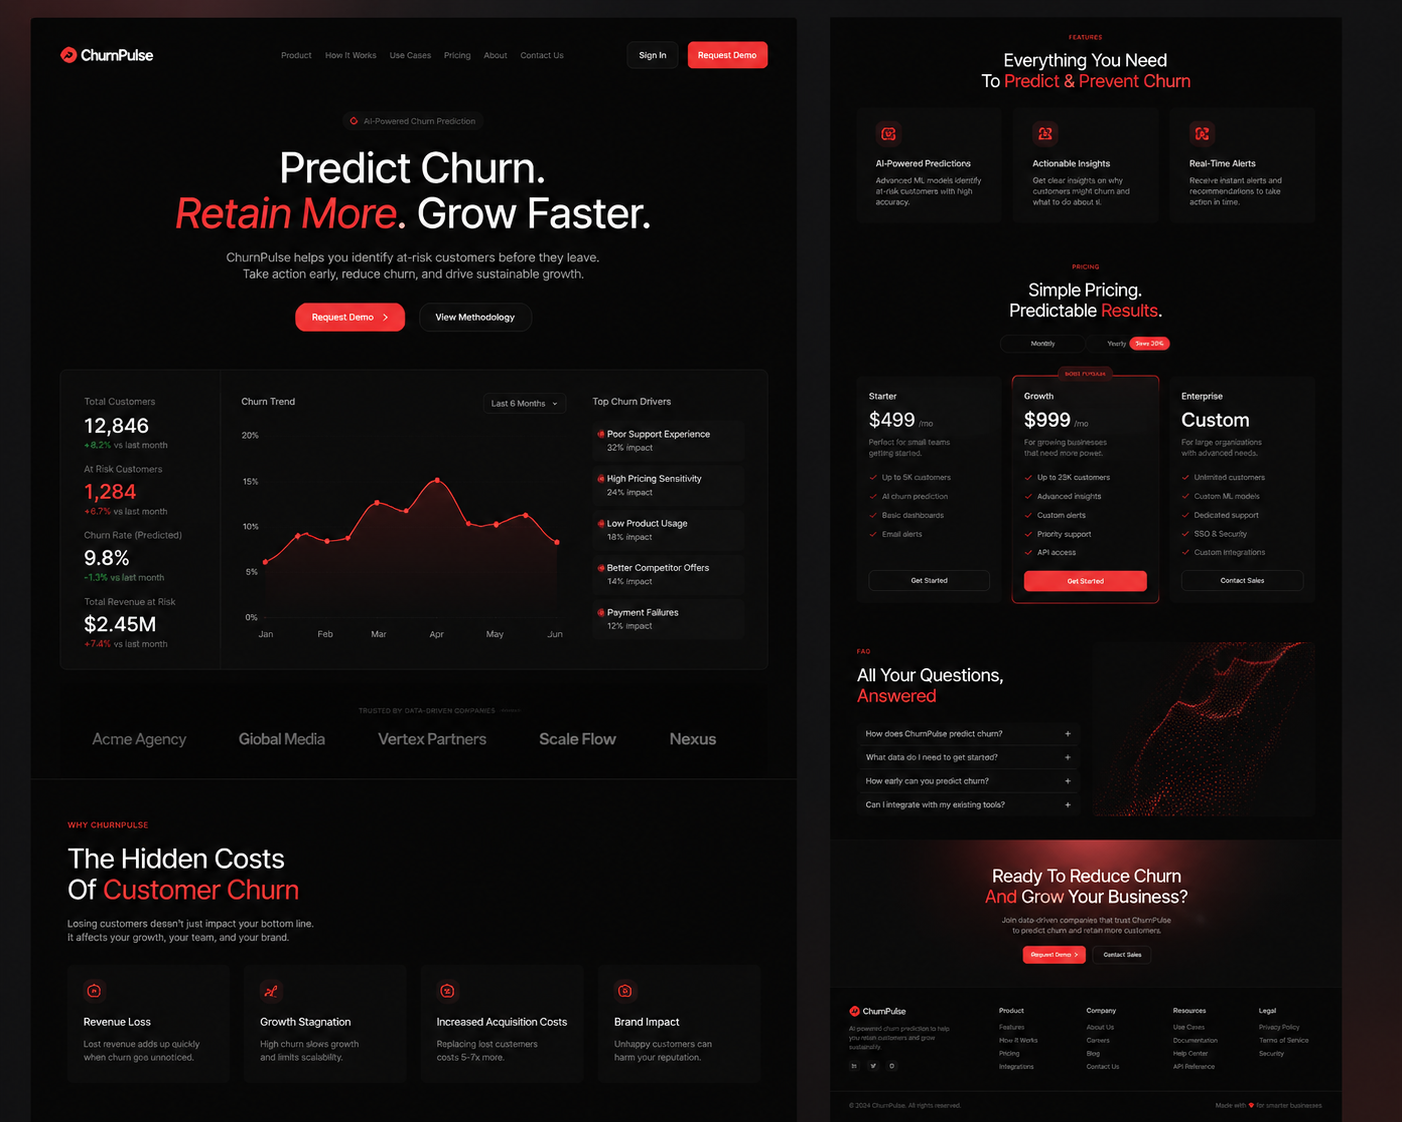
Cut voluntary churn 18% in two quarters with next-best-action scoring for a meal-subscription platform.
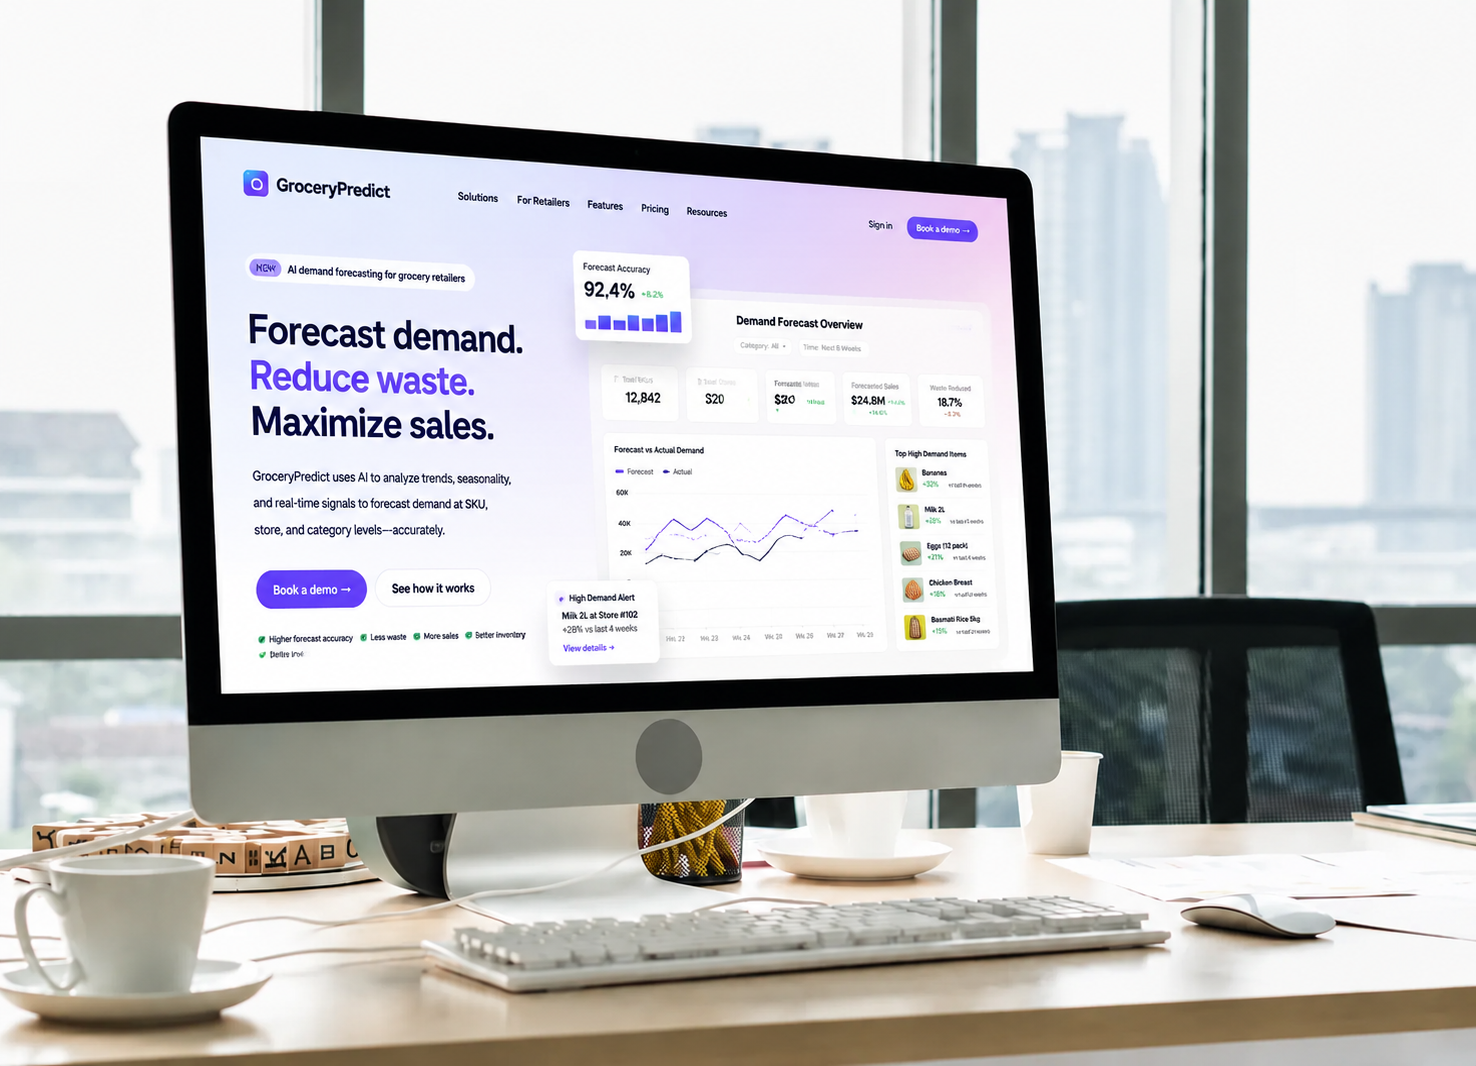
Cut waste 22% across 900 stores with SKU-level probabilistic forecasts.
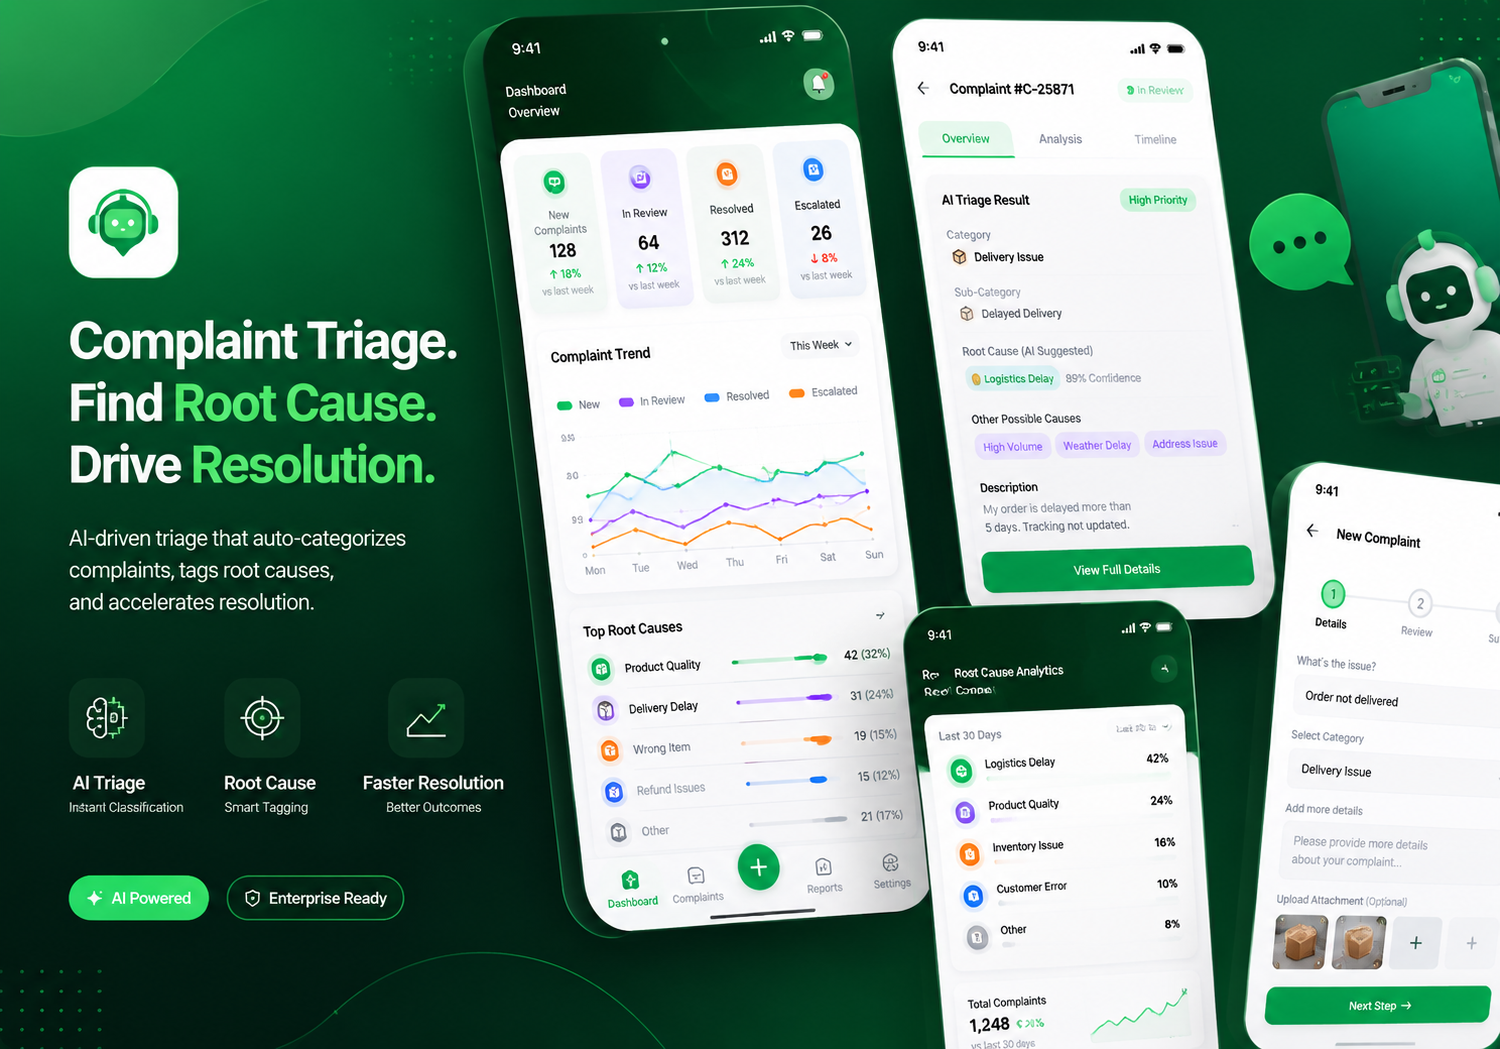
Auto-classified 58% of citizen complaints to root cause, feeding the department's reporting directly.
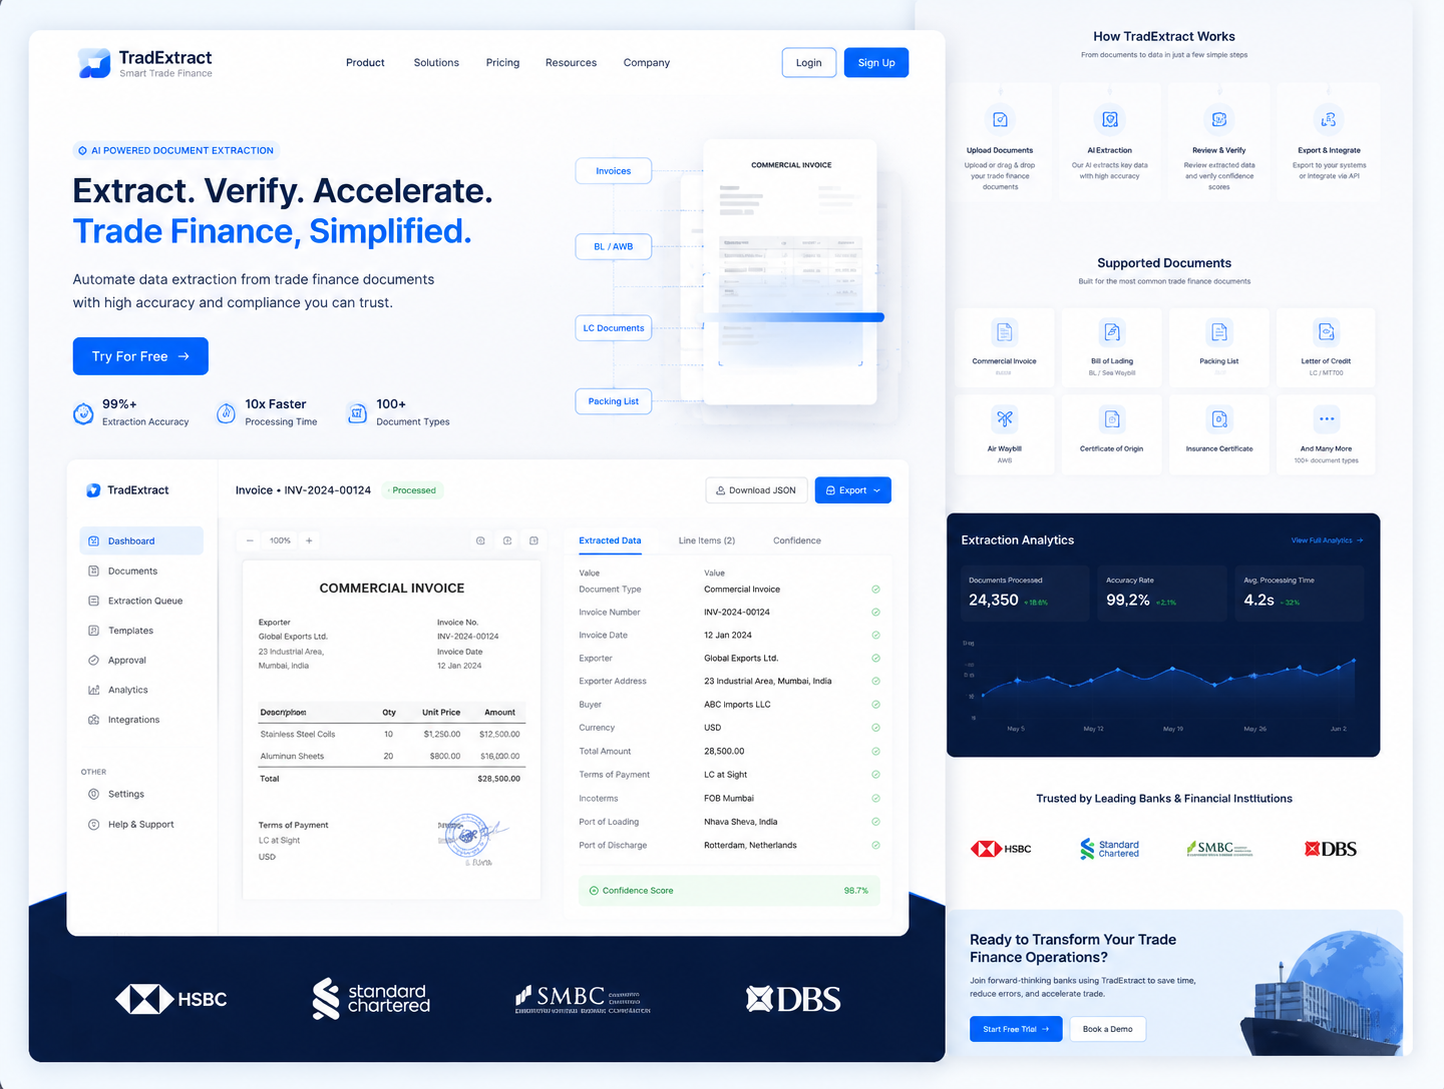
Achieved 94% straight-through extraction on bills of lading and customs paperwork for a logistics operator.
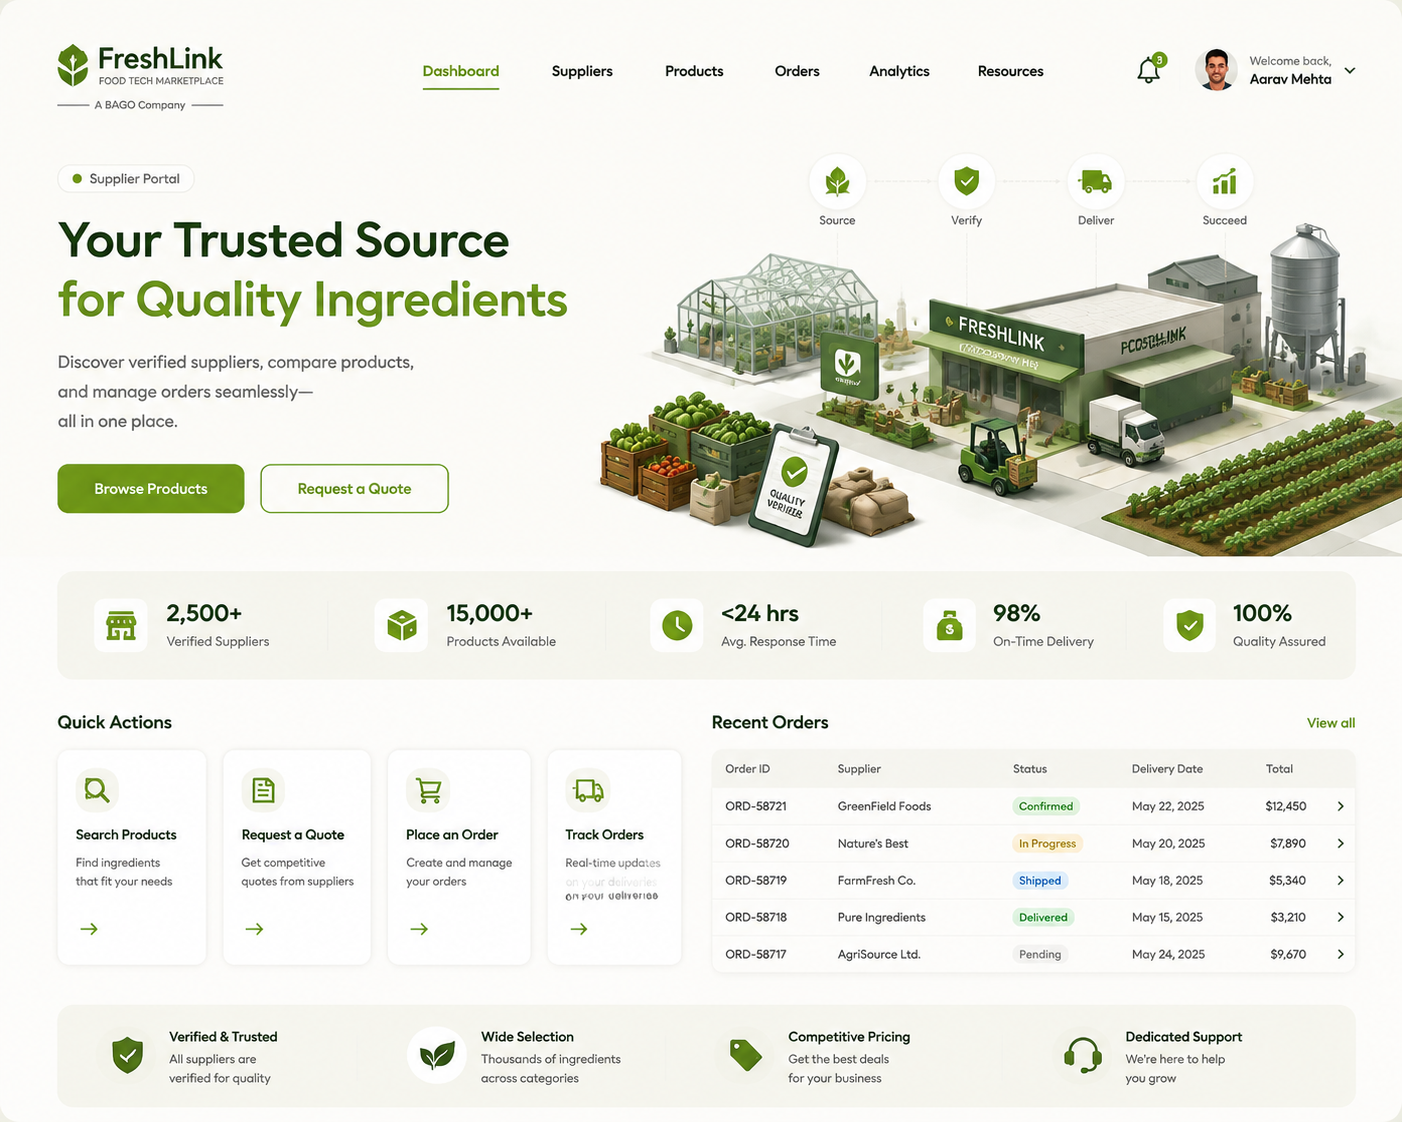
Self-service supplier portal lifted supplier adoption to 62% in one quarter for a foodtech marketplace.
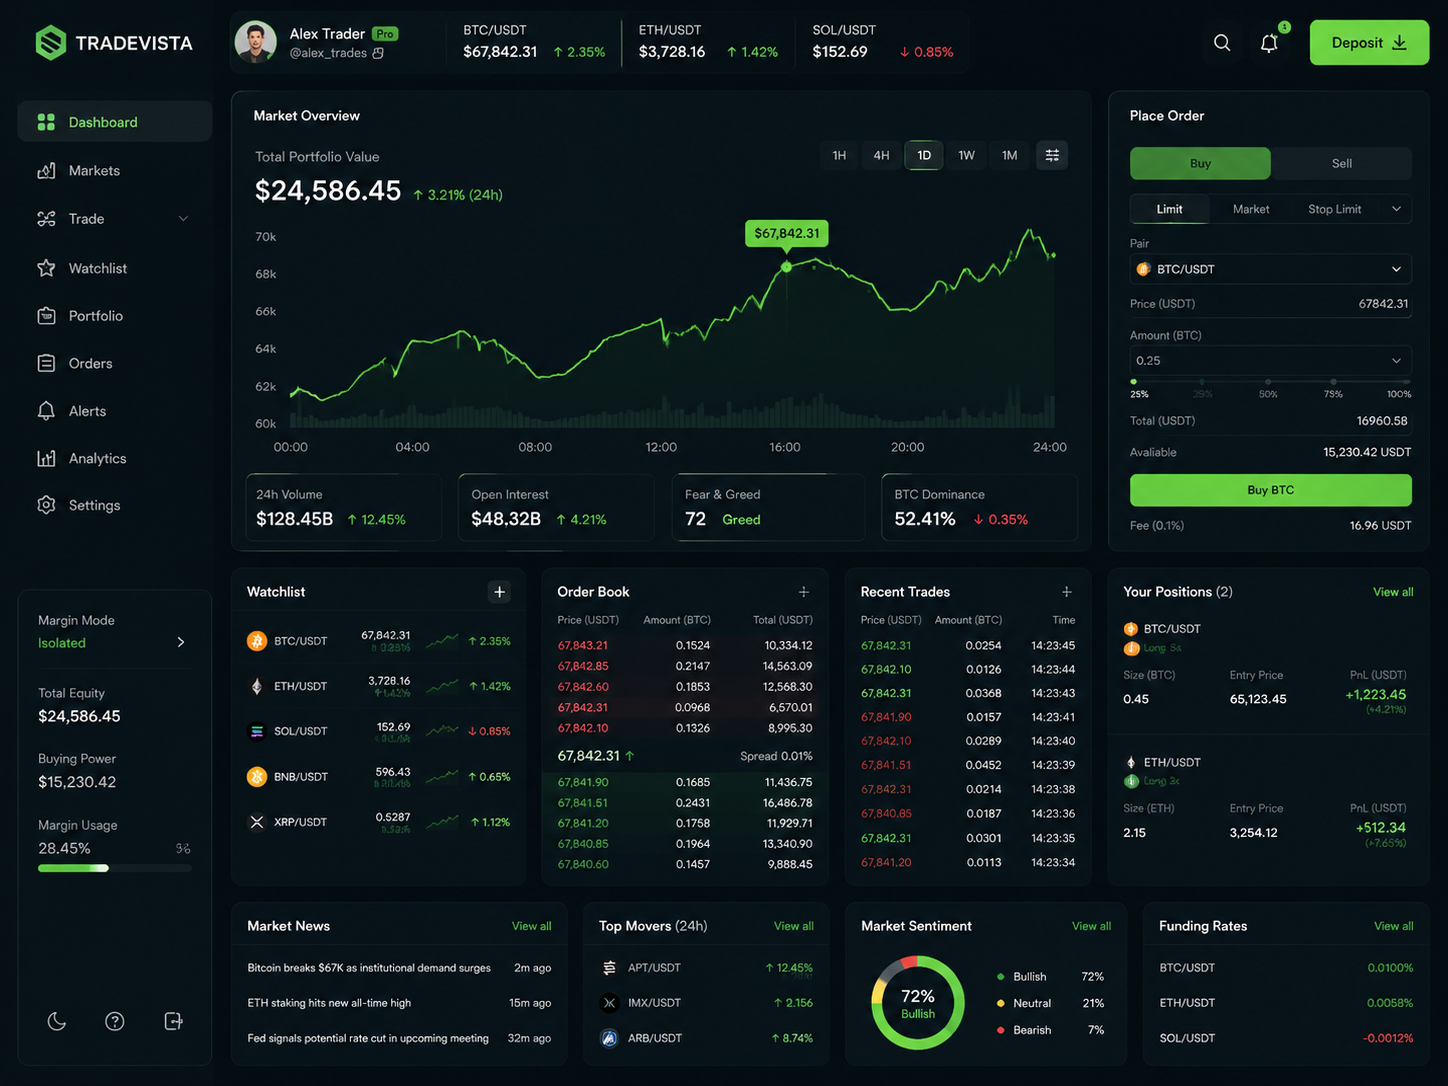
Sub-120ms streaming operations dashboard across 40 control desks for a logistics operator.
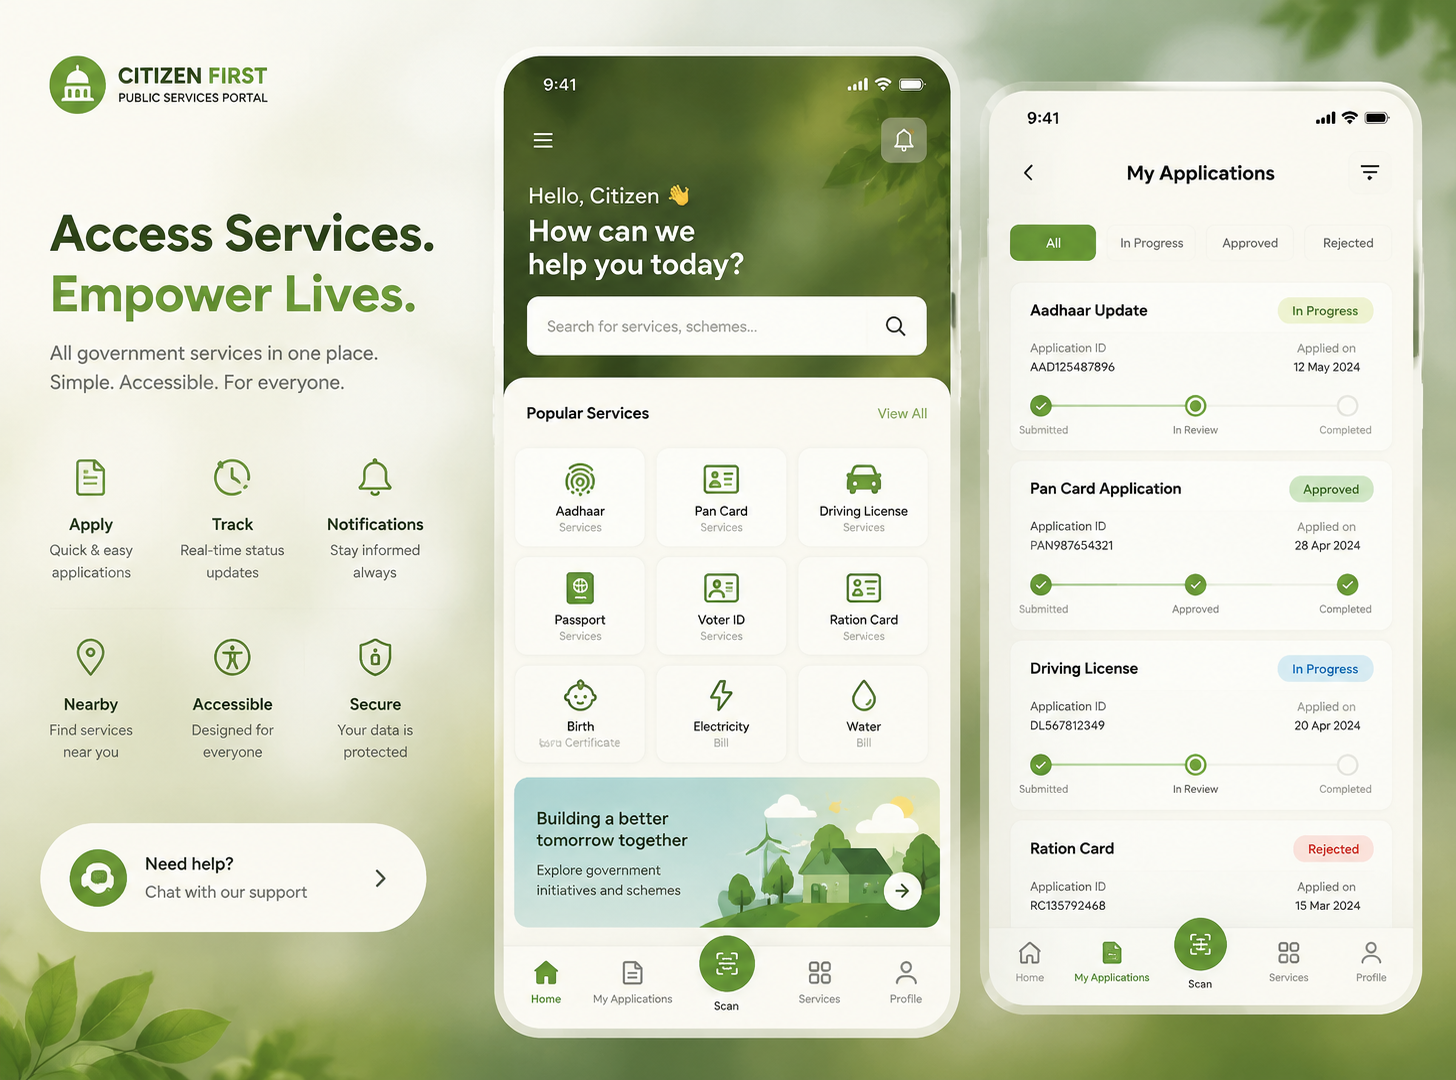
Rebuilt a citizen portal to WCAG 2.2 AA, cleared external audit first pass.
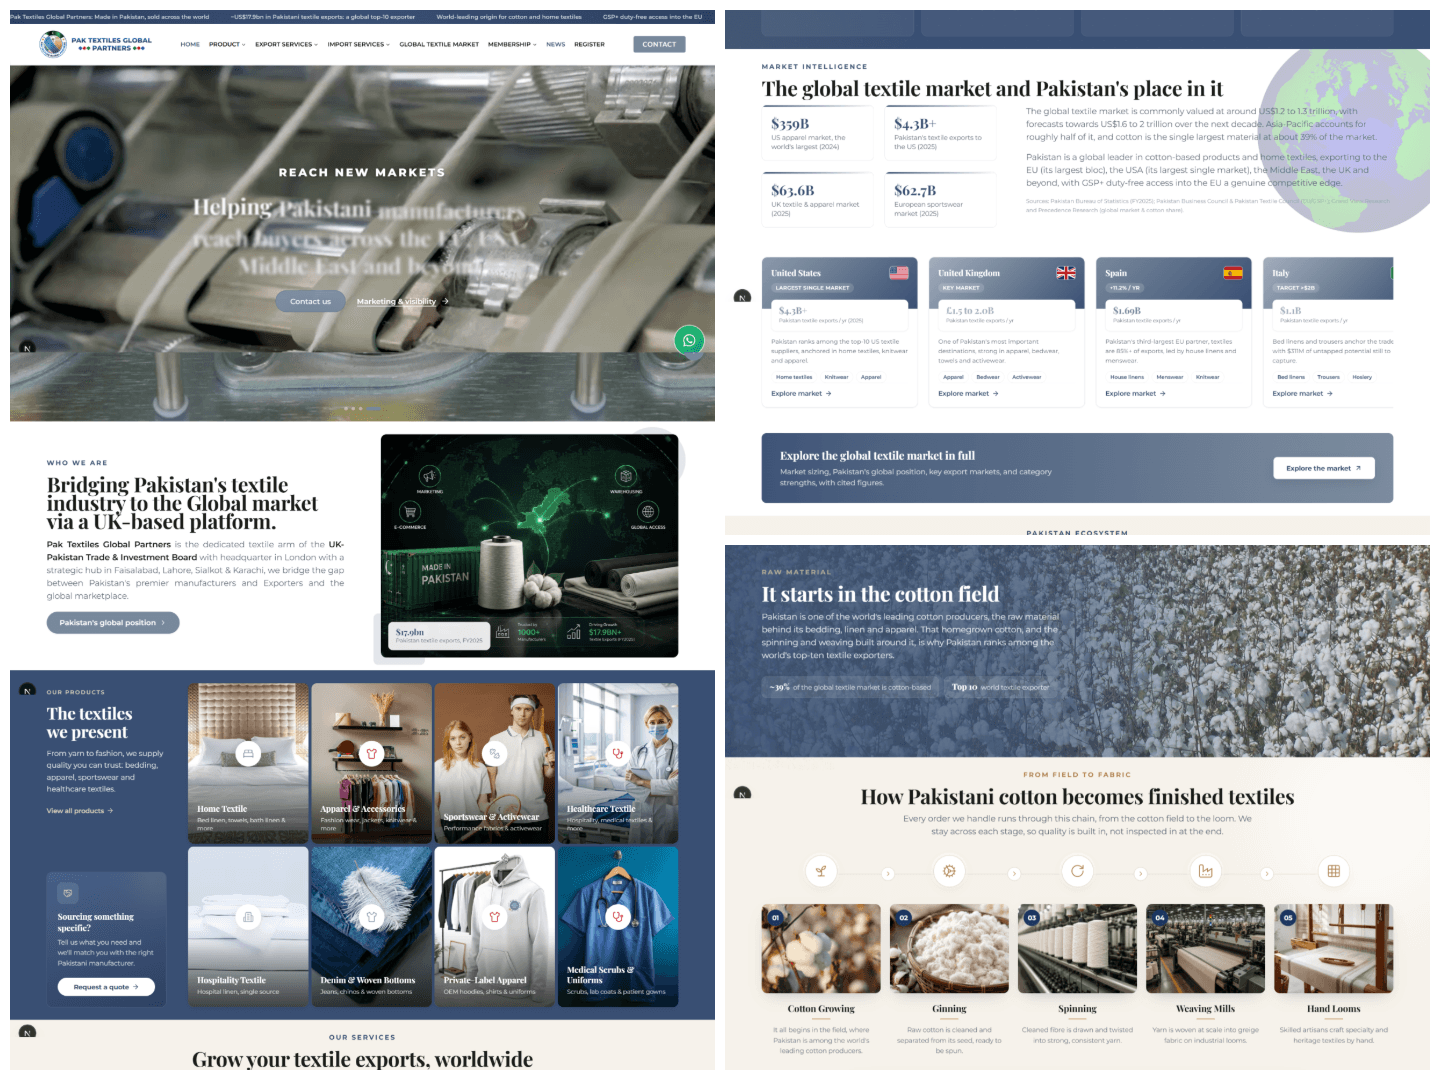
Re-themed and re-scoped an 80-route SaaS template into a 15-page global trade platform, with zero legacy brand colour left across 225 files.
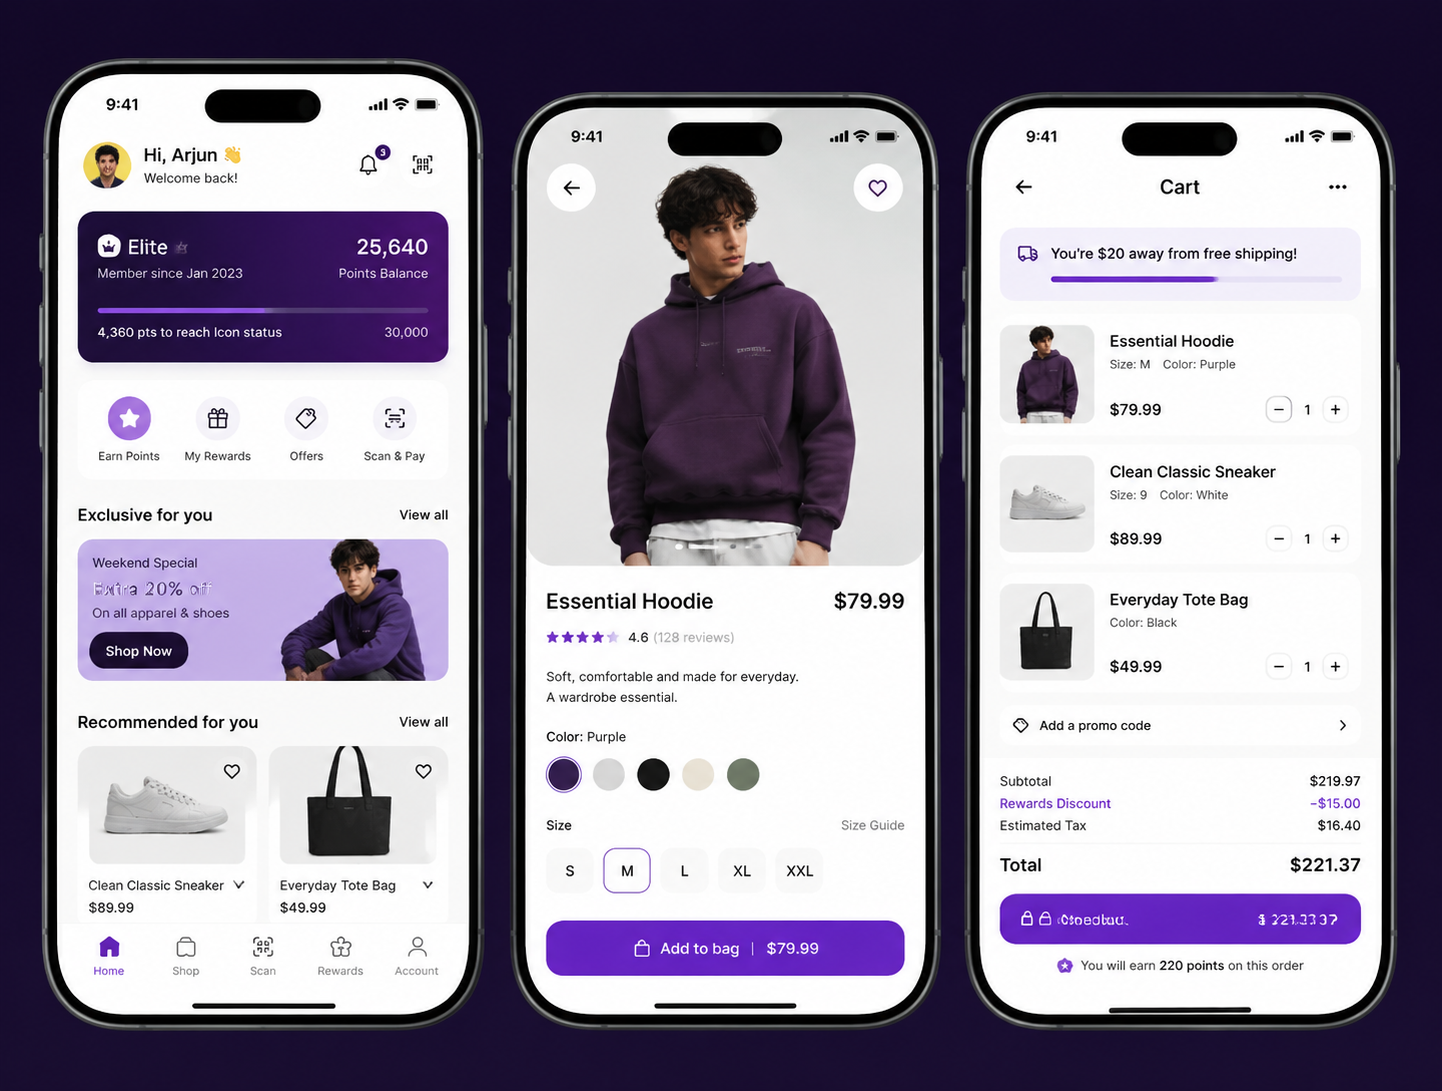
Launched a retail loyalty app to a 4.8-star rating and 200k users in 90 days.
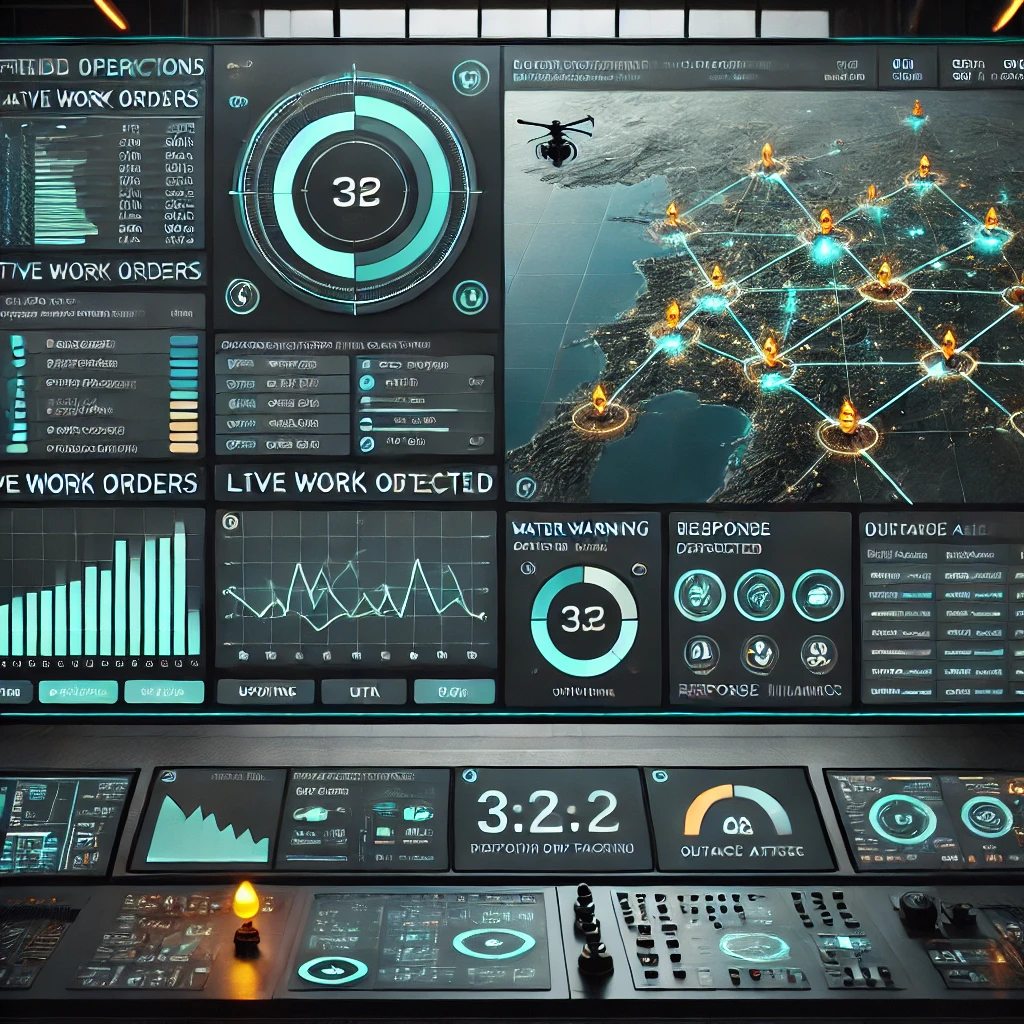
Offline-first engineer app cut job-completion admin 31% for a manufacturer's field team.
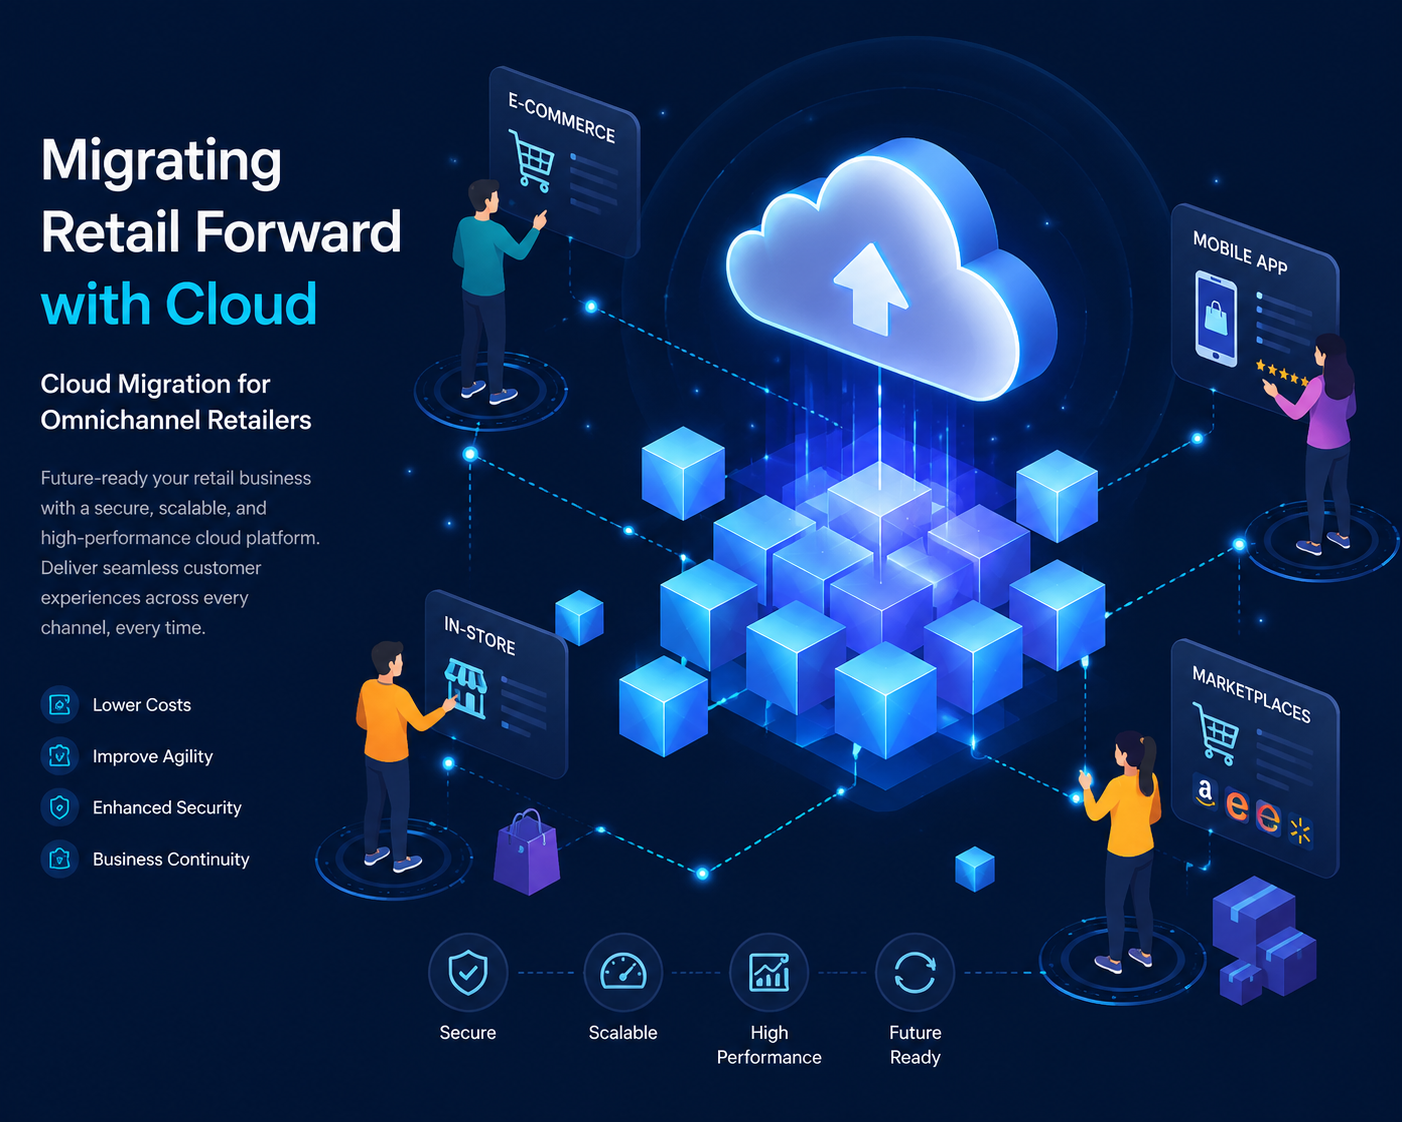
Re-platformed e-commerce to the cloud, holding availability through a record peak-season trading day.
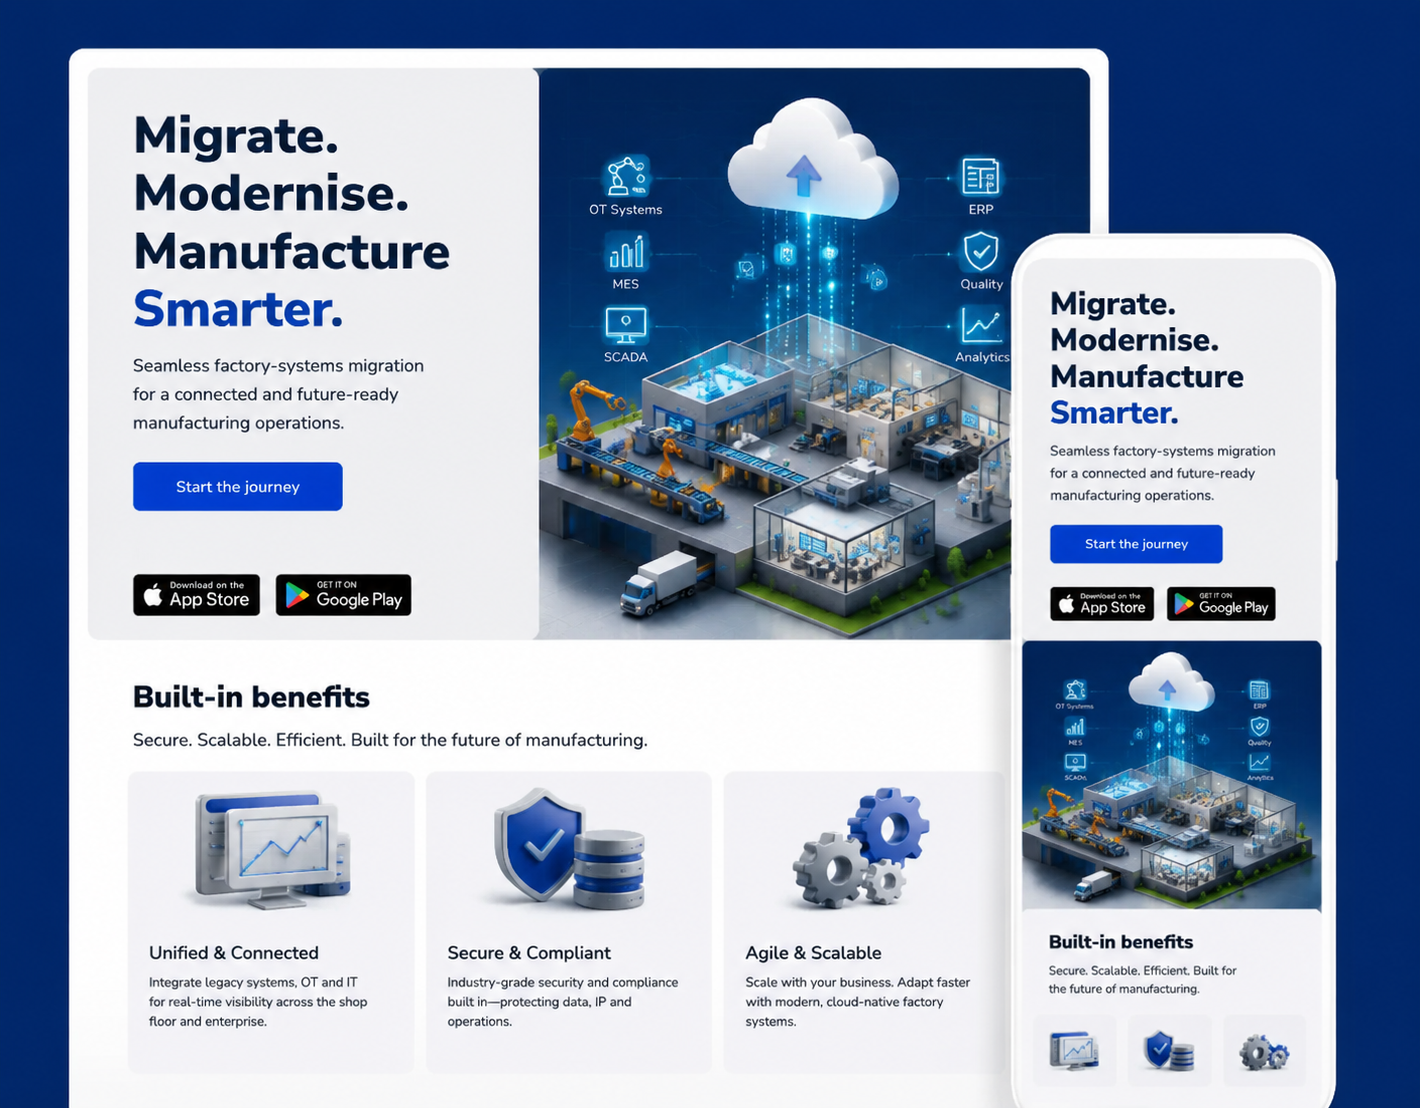
Lifted MES and quality systems to the cloud across nine plants, cutting infrastructure cost 34%.
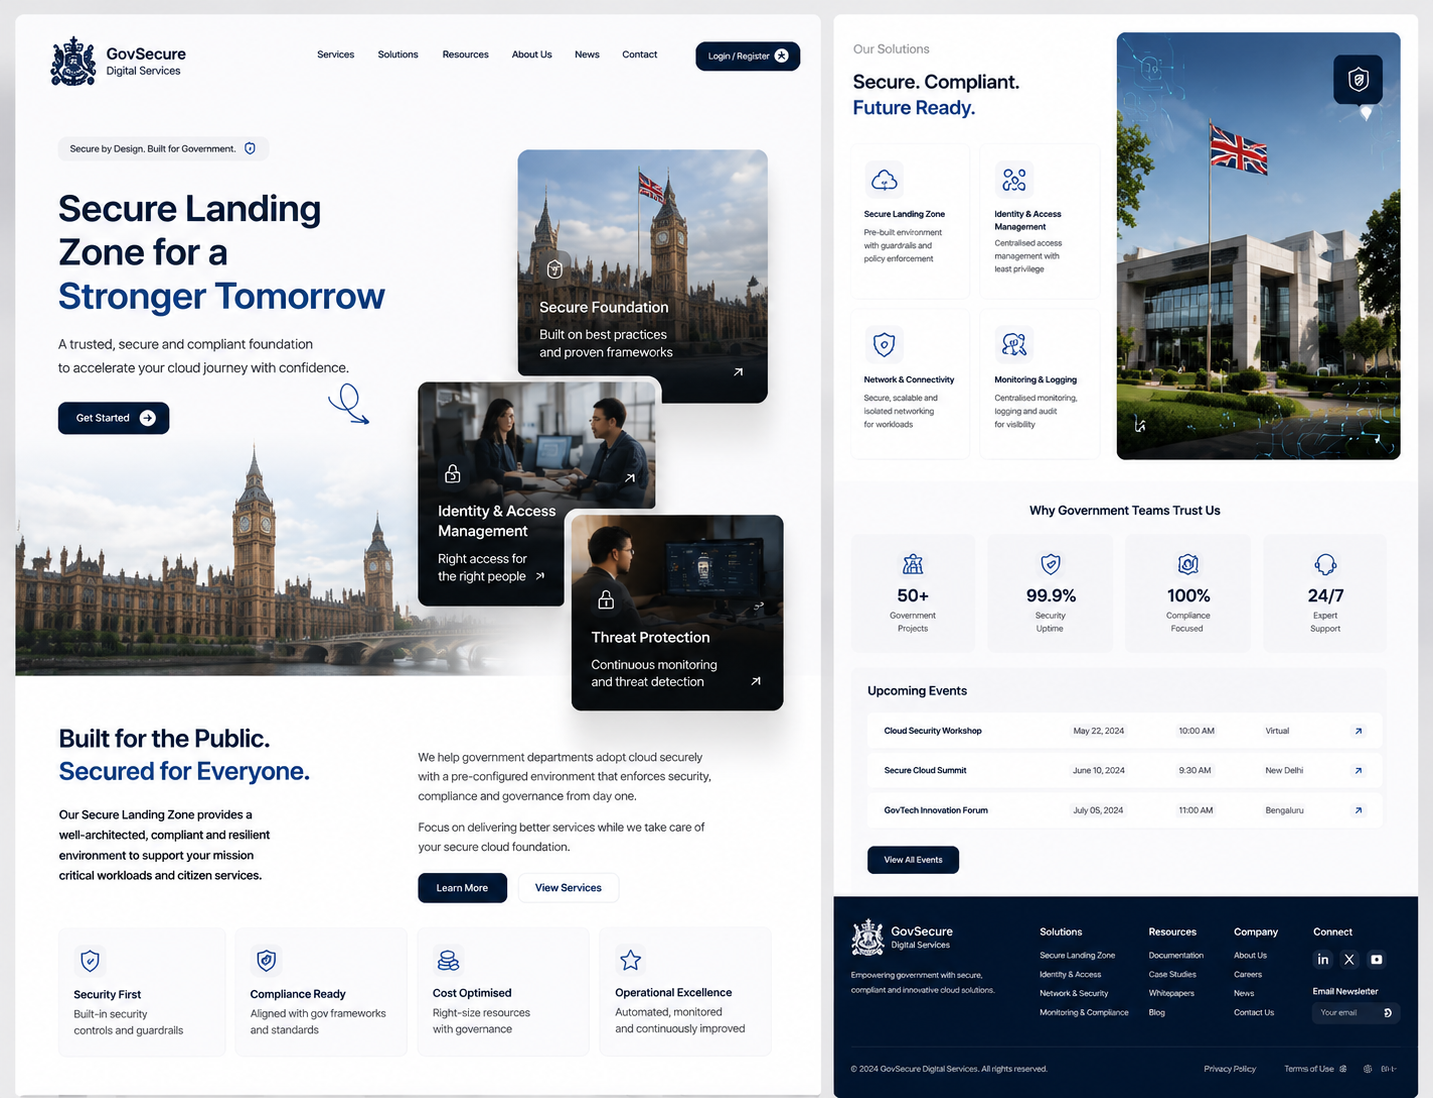
Stood up a compliant, multi-account landing zone for a government department in 7 weeks.
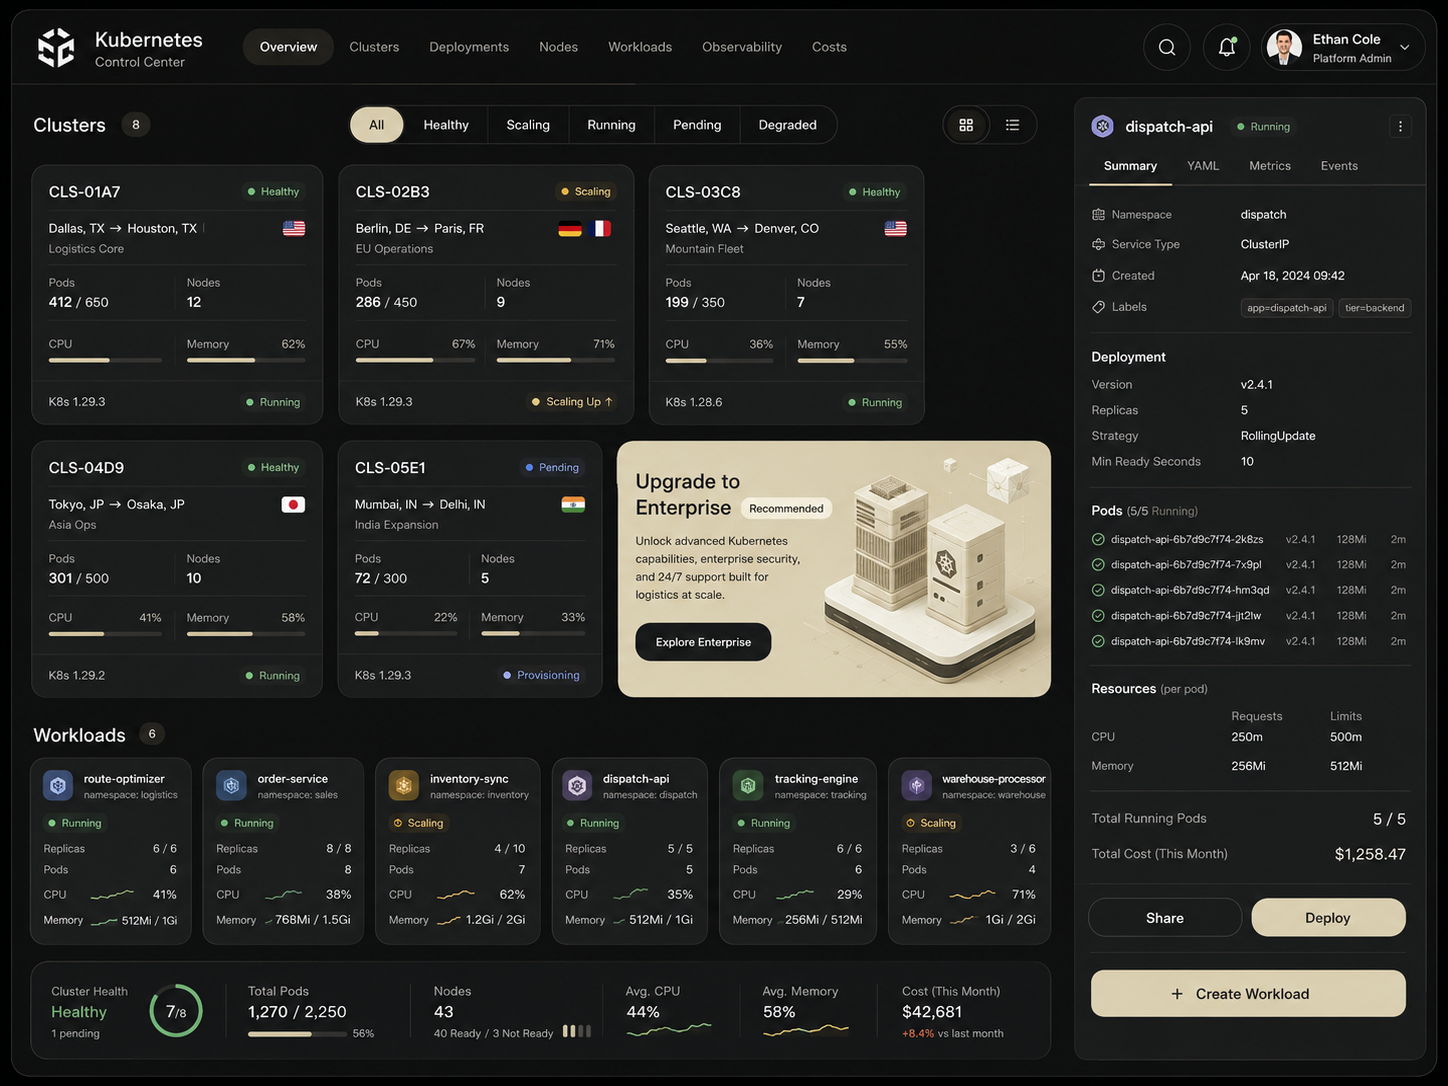
Consolidated 14 clusters to one governed platform, cutting ops toil 55% for a logistics operator.
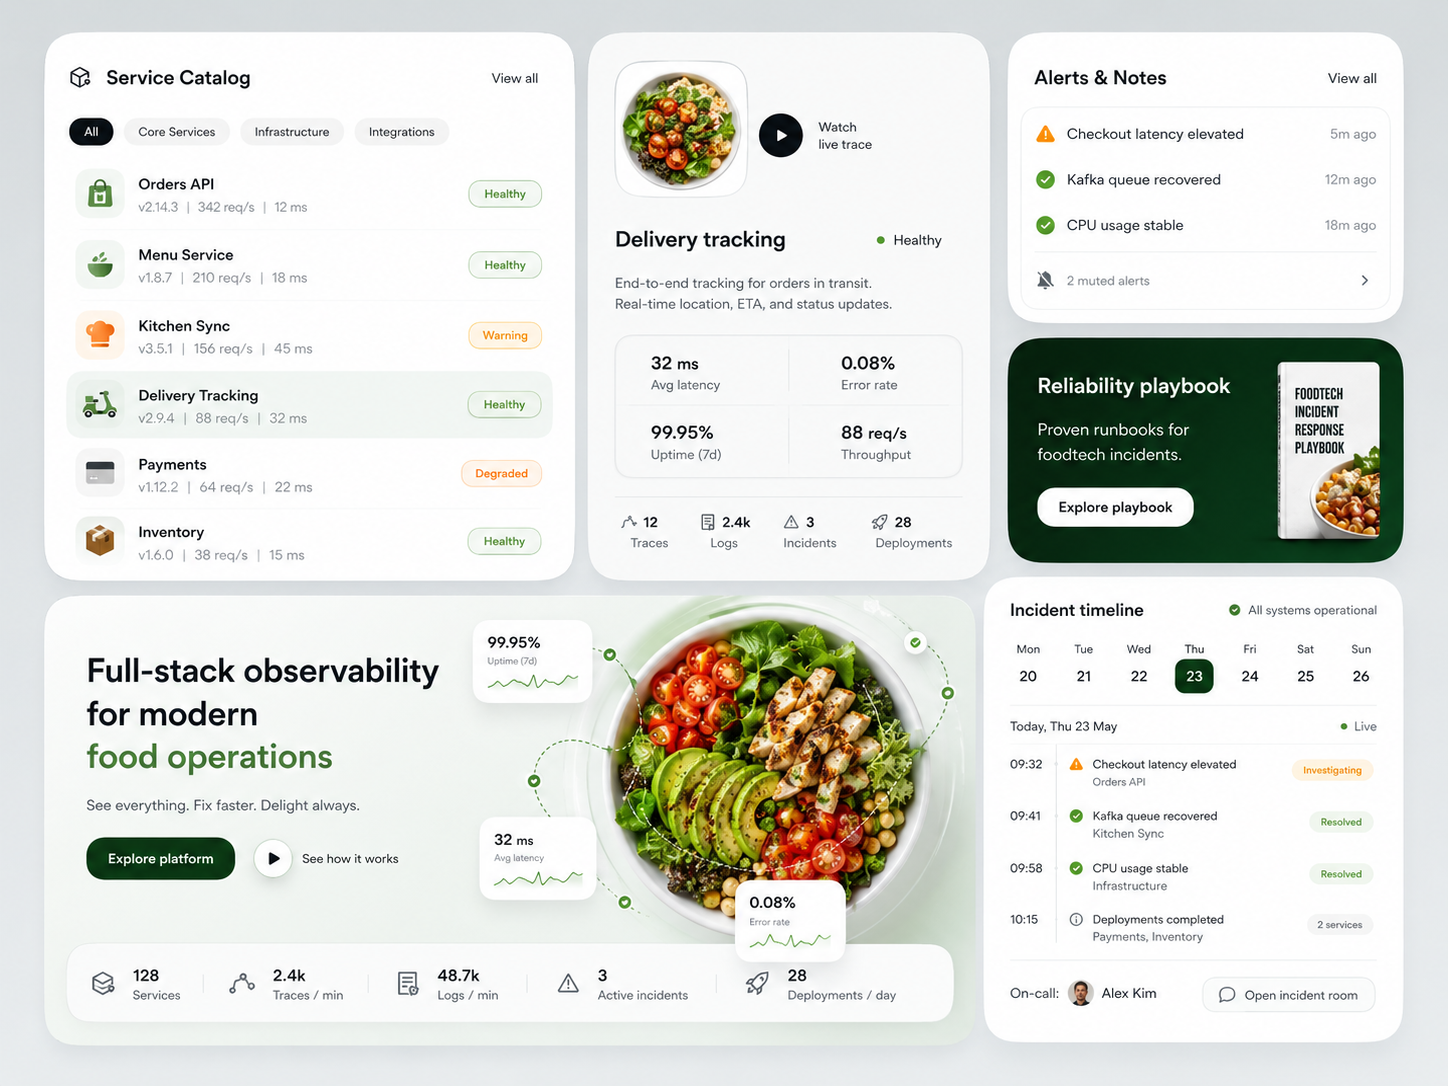
Cut mean-time-to-detect 72% for a food-delivery platform with unified tracing and SLOs.
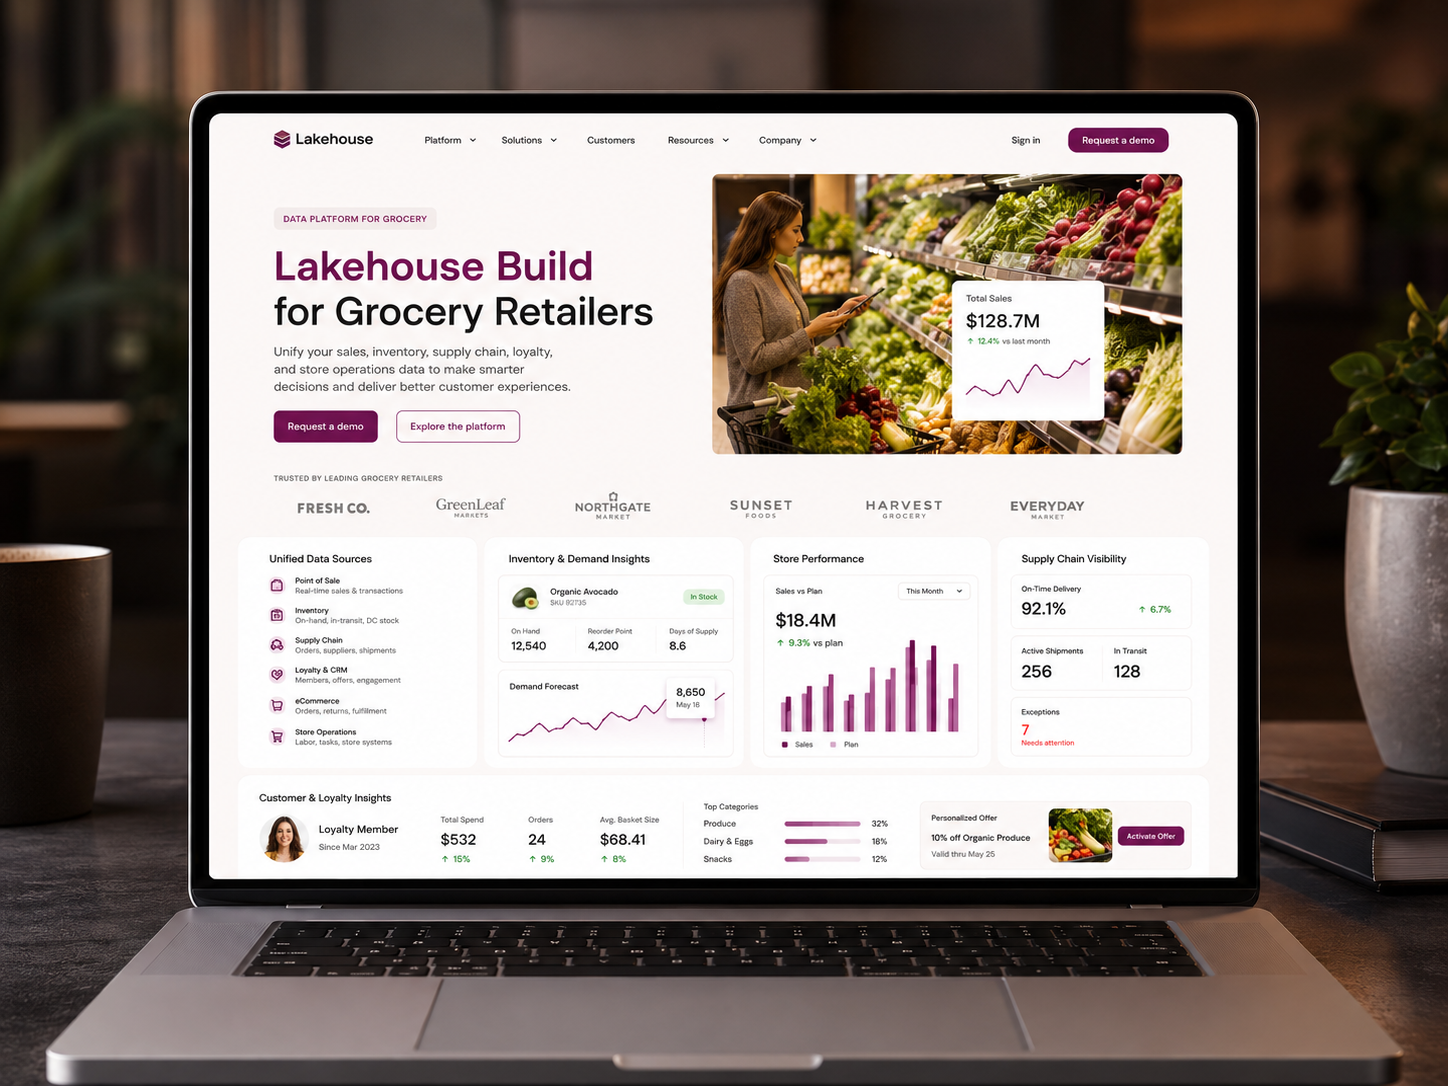
Unified 40 sources into a governed lakehouse, cutting report build time 60% for a grocery retailer.
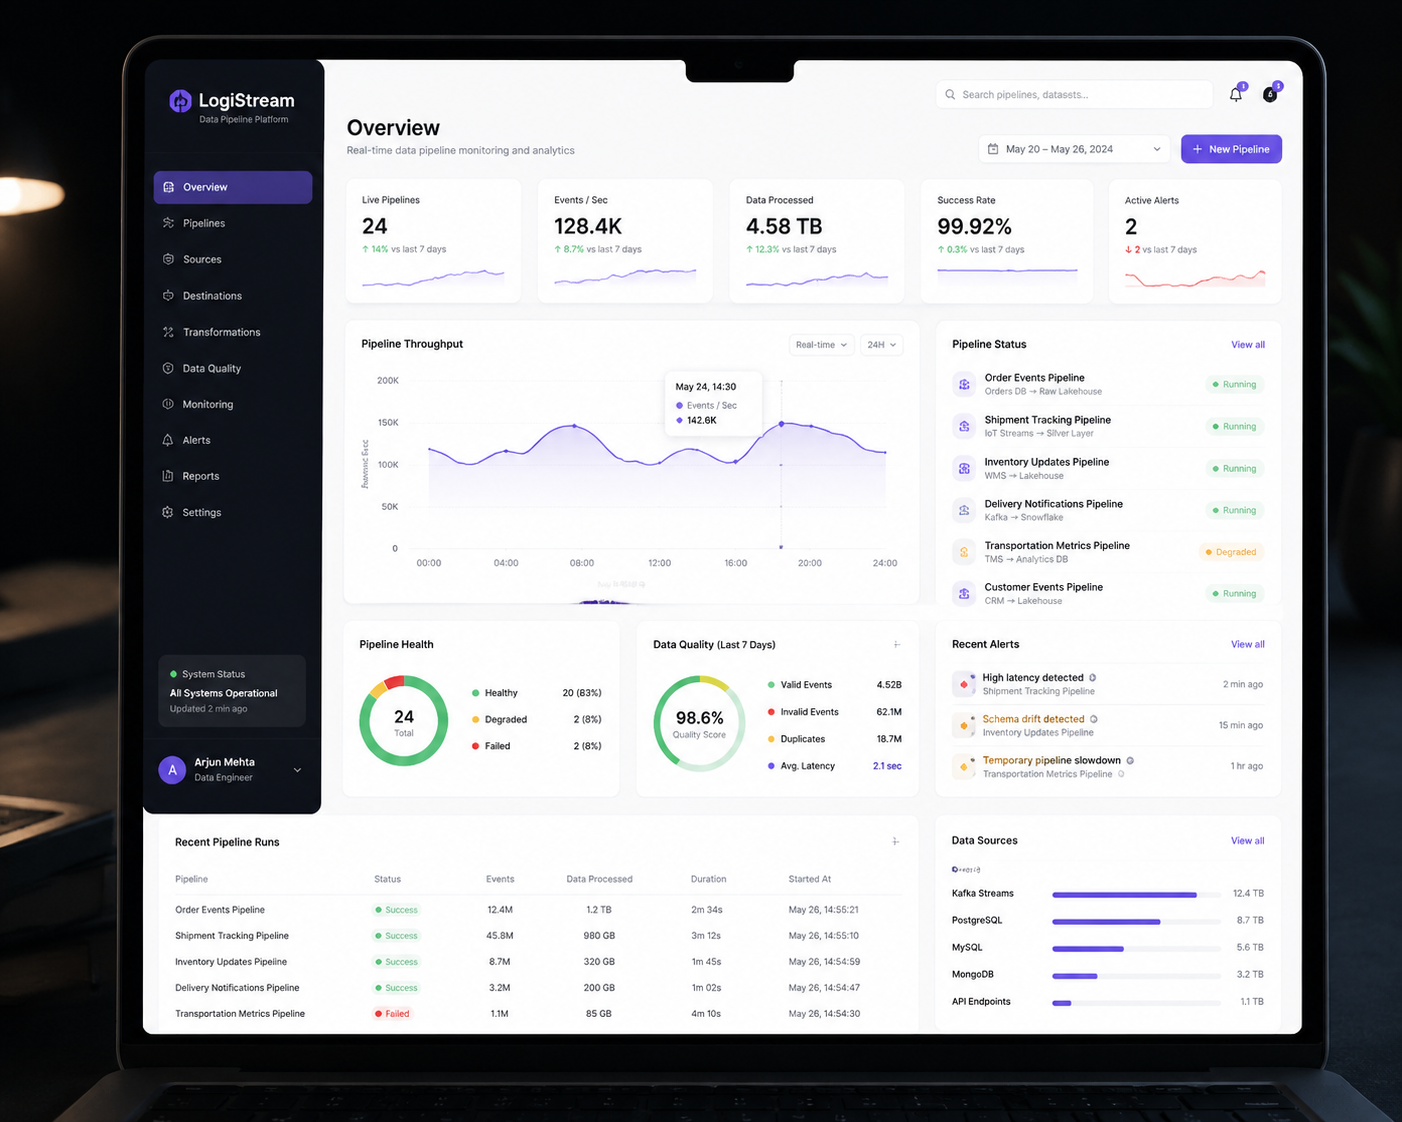
Delivered sub-second track-and-trace event data to 30 teams for a logistics operator.
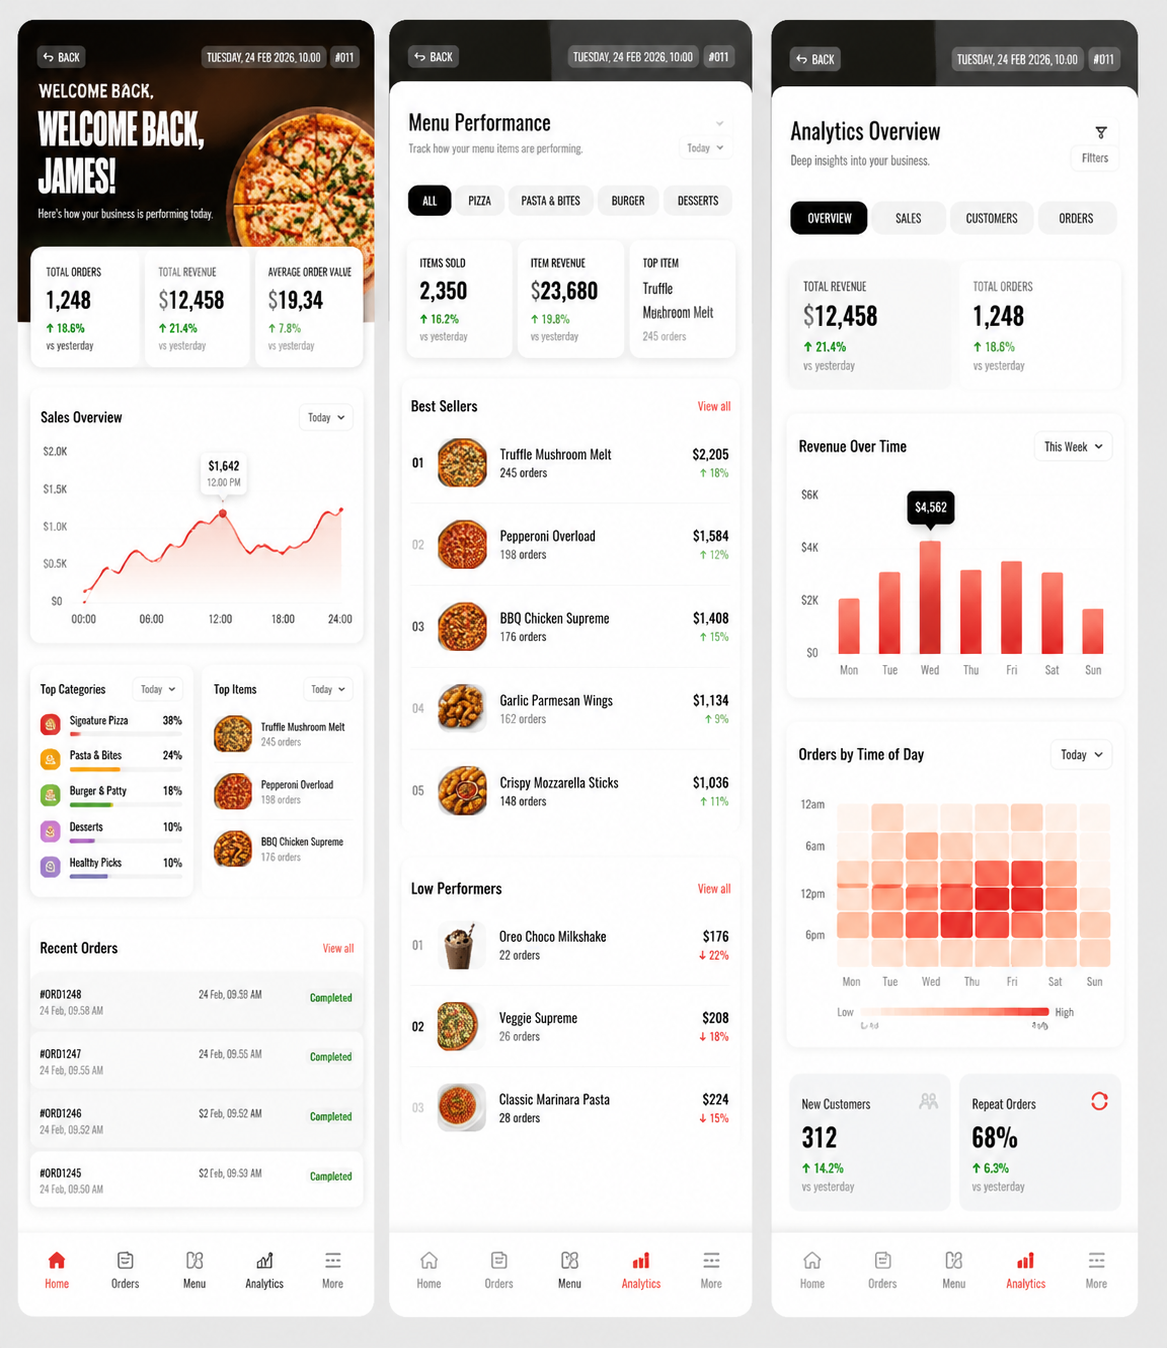
Self-service models tripled analyst throughput at a food-delivery platform.
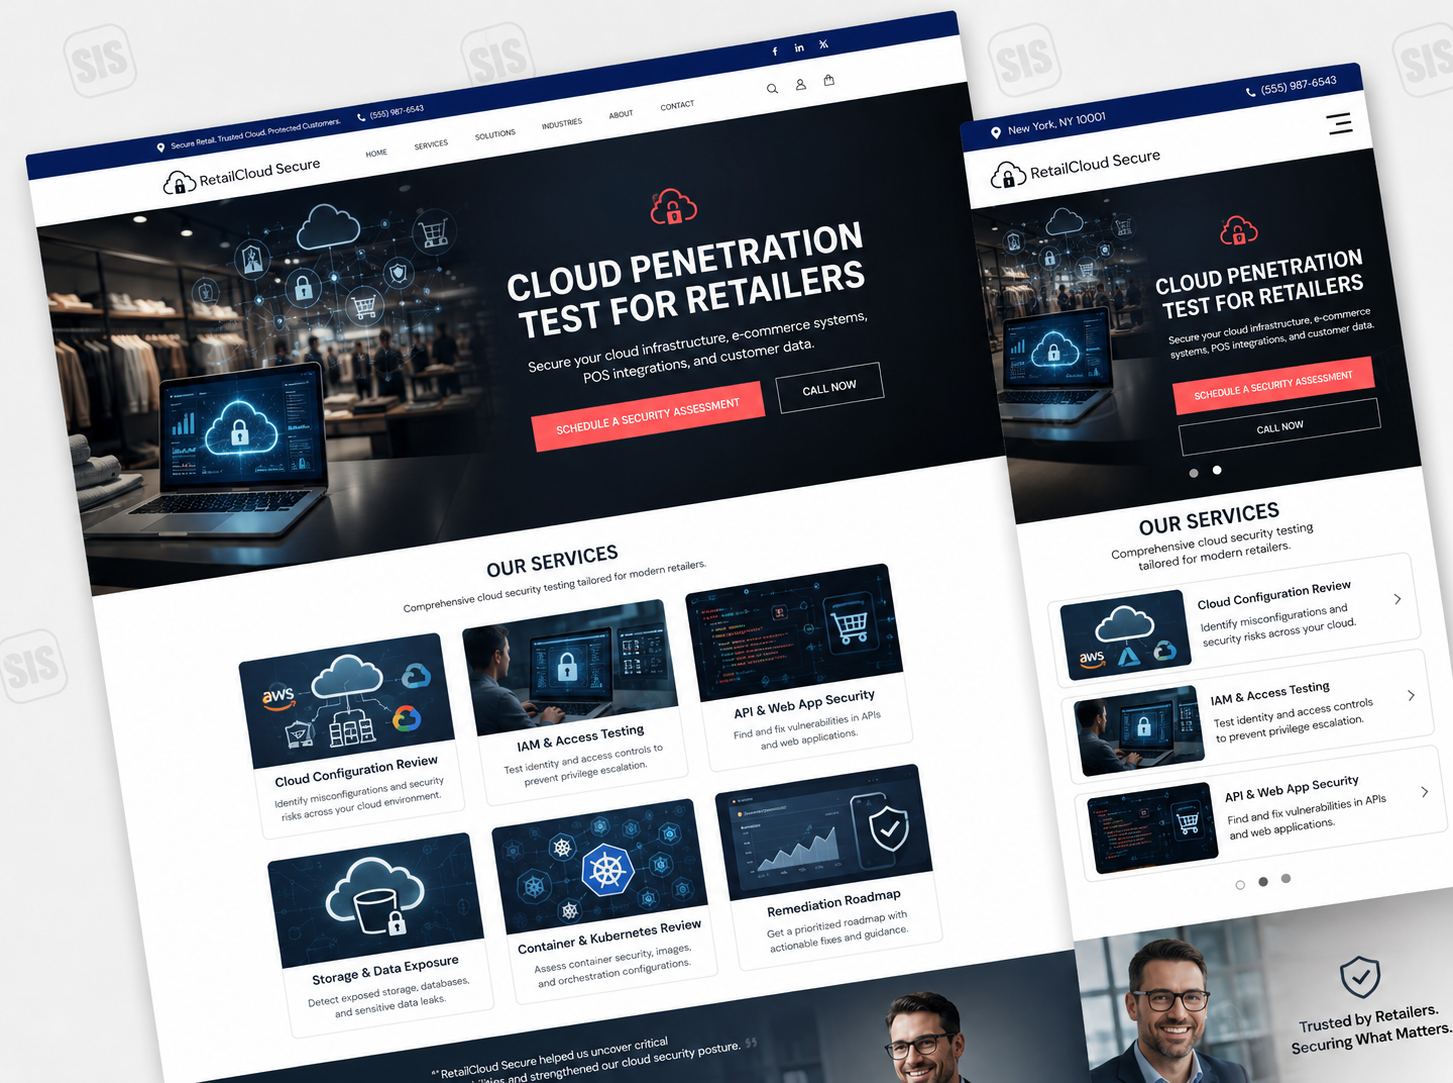
Surfaced 74 exploitable misconfigurations across a retailer's multi-account cloud estate.
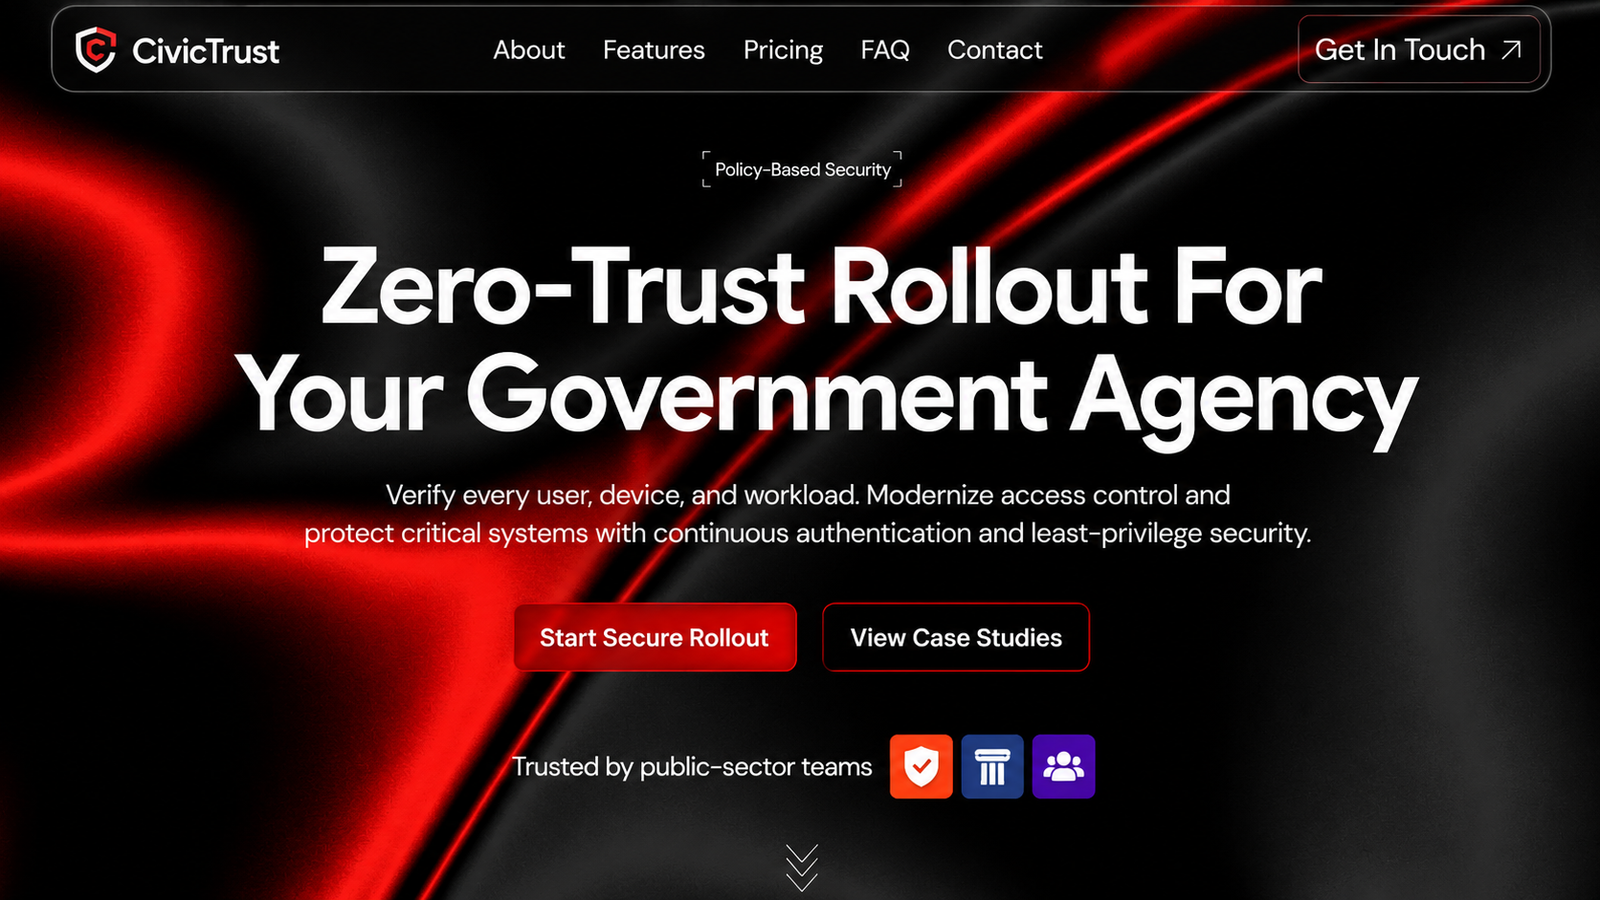
Rolled zero-trust access to 25,000 civil servants without a productivity dip.
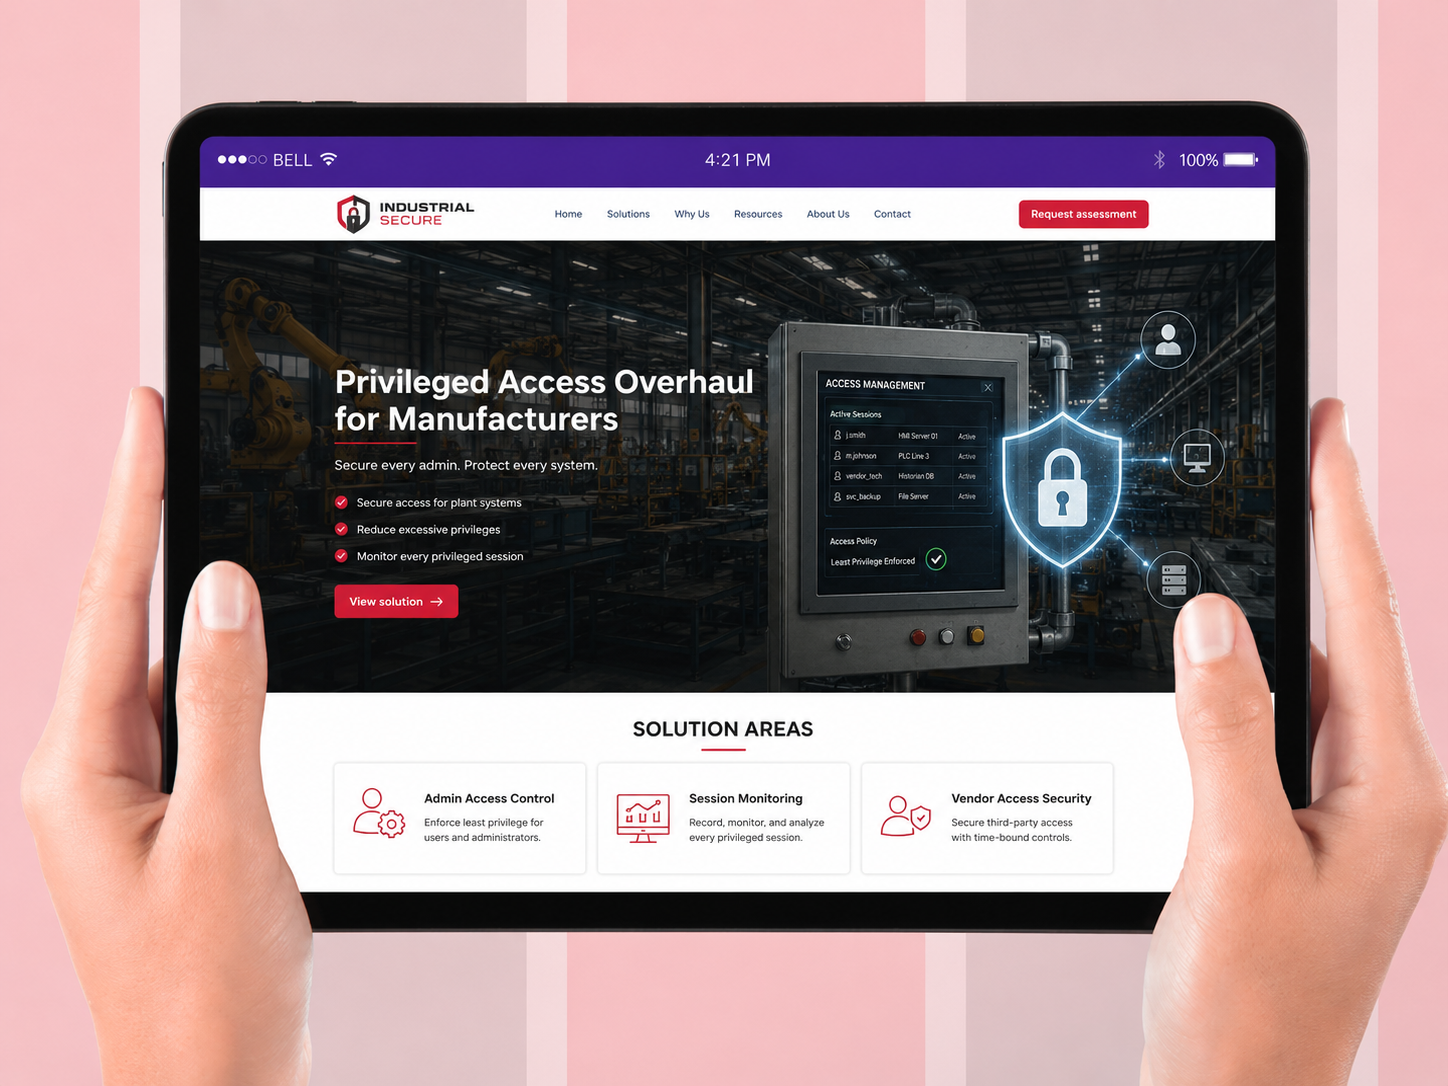
Cut standing privileged access 90% across a manufacturer's IT and OT estate.
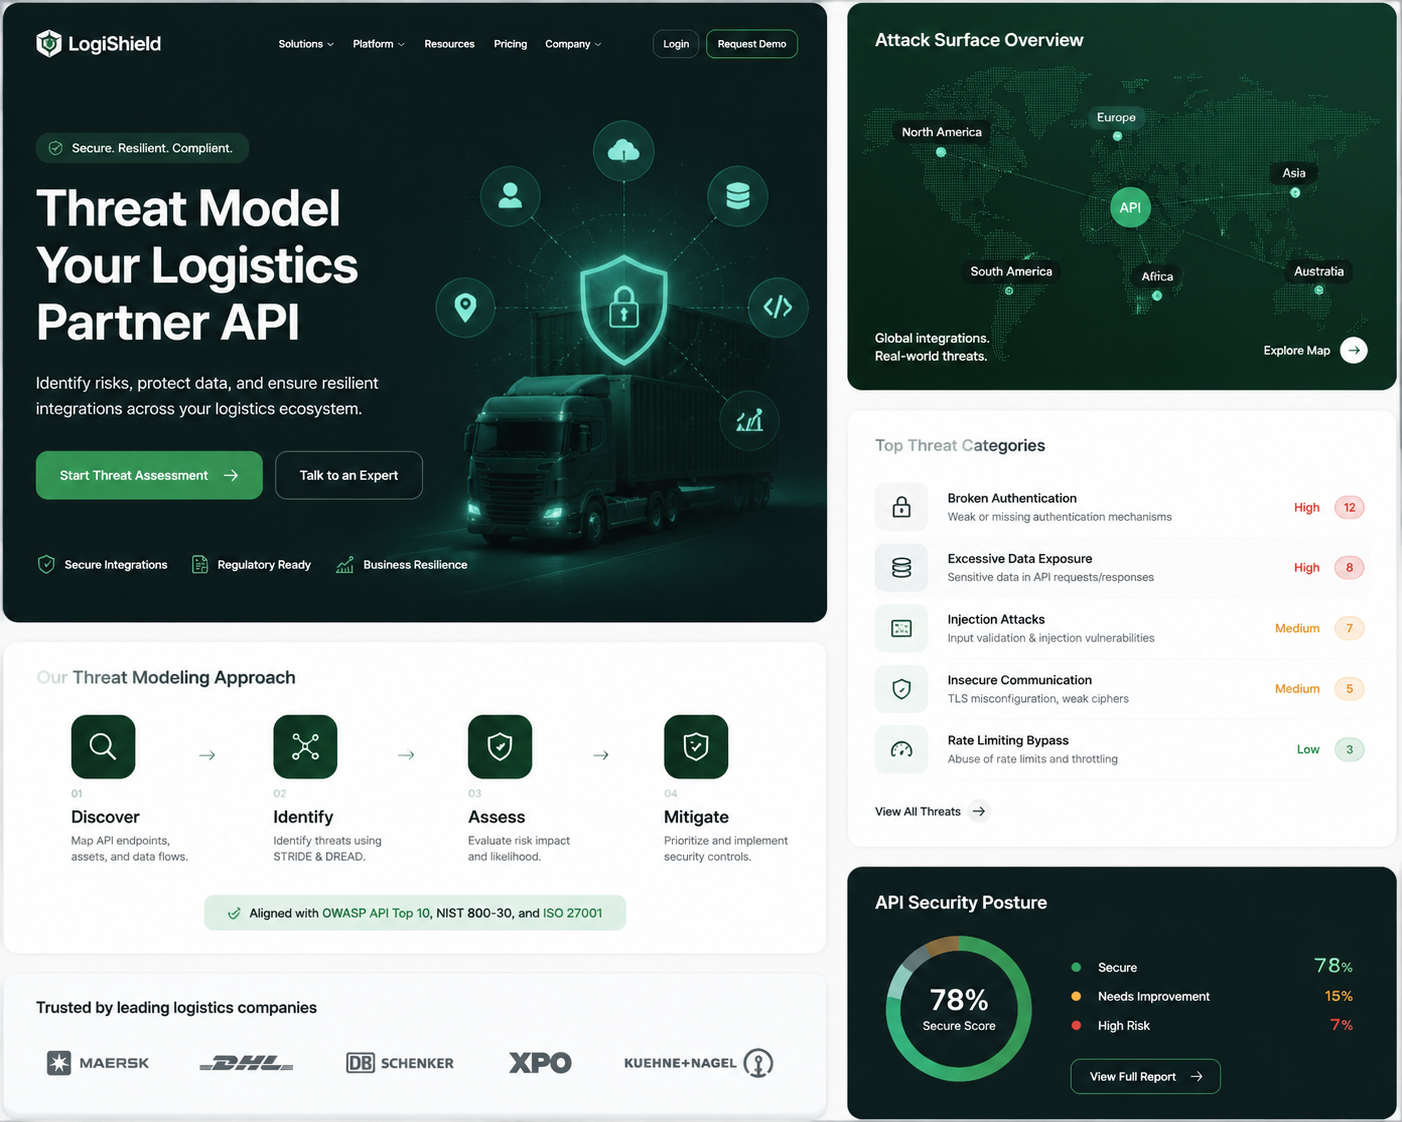
Hardened a logistics partner API against abuse before third-party onboarding.
Validated device, telemetry, and notification APIs under live conditions, shipping a release with zero contract breaks across connected consumers for an IoT platform.
Achieved full endpoint coverage across upload, playback, and monetisation APIs, with auth, rate limits, and error paths verified end to end for a streaming platform.
Contract and integration testing across hotel, flight, and car-rental APIs cut integration bugs 62% by catching schema and pricing mismatches before release.
Wired end-to-end suites into CI for a US e-commerce marketing platform, cutting regression time 90% and shipping every merge regression-clean.
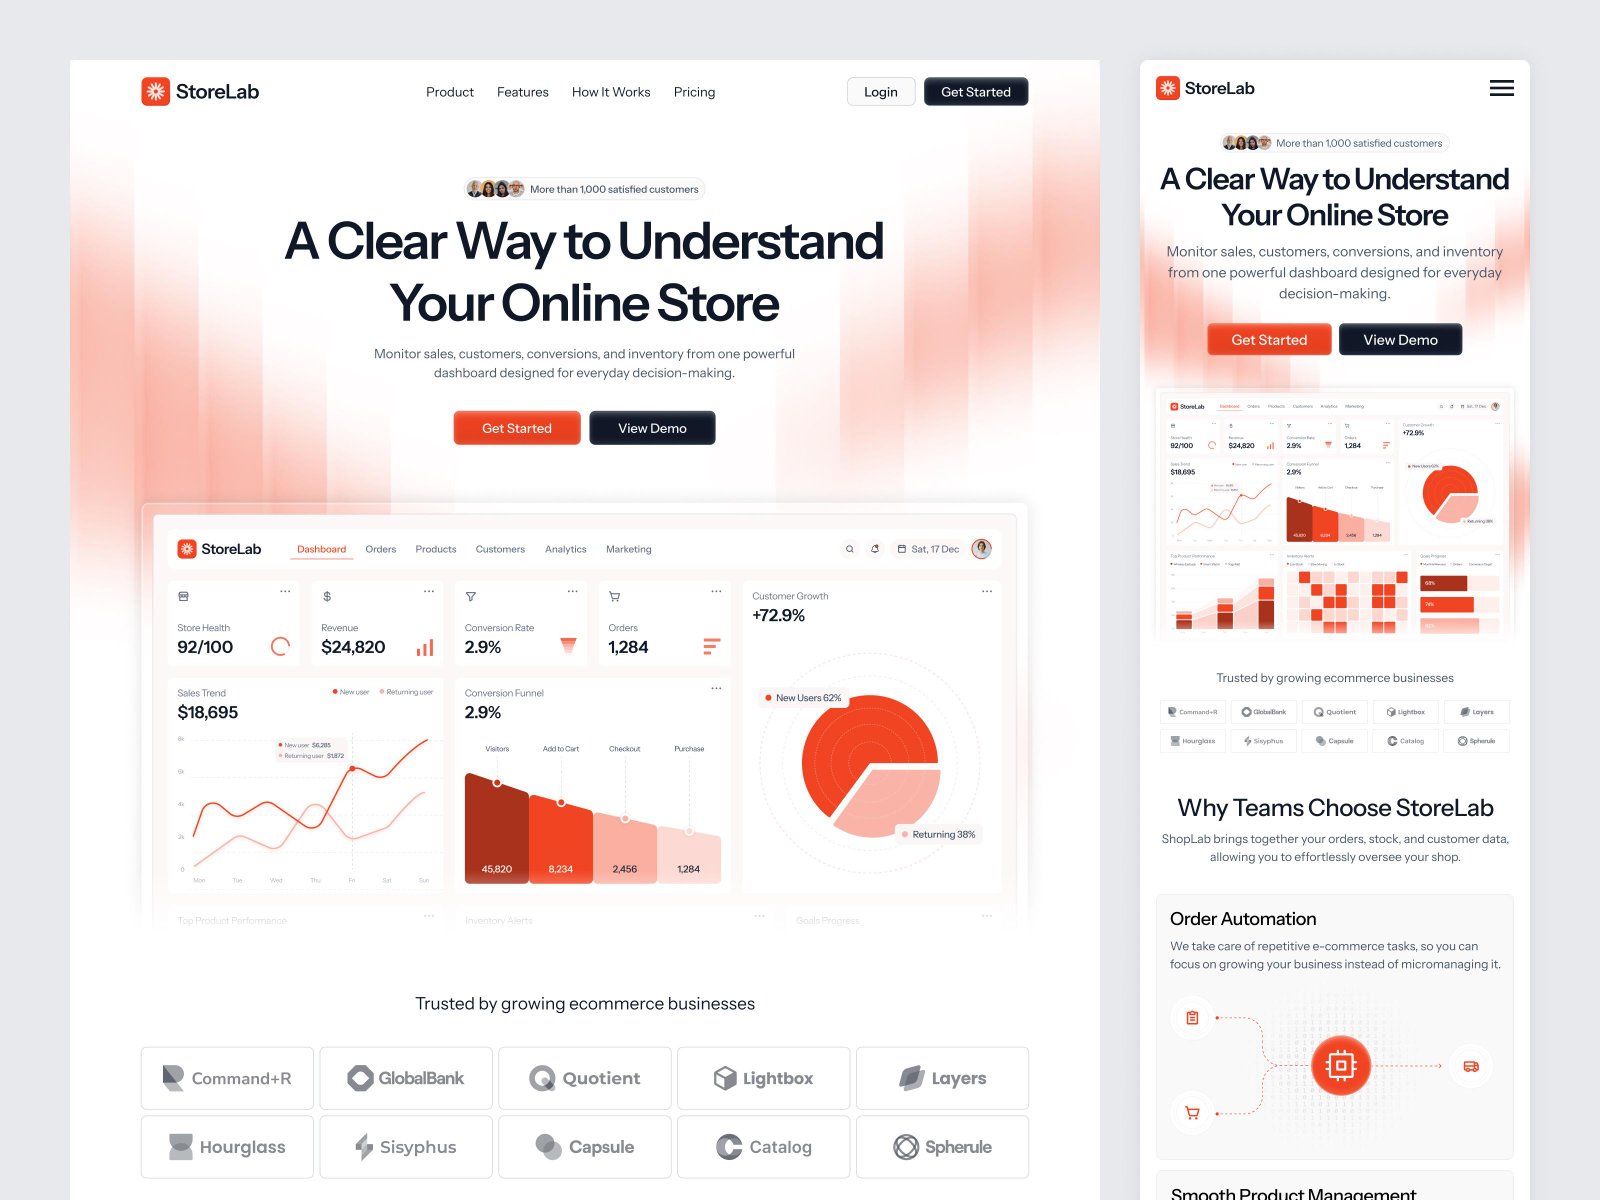
Delivered cross-browser E2E and API automation for a UK store analytics dashboard, catching orders, inventory, and reporting regressions before every release.
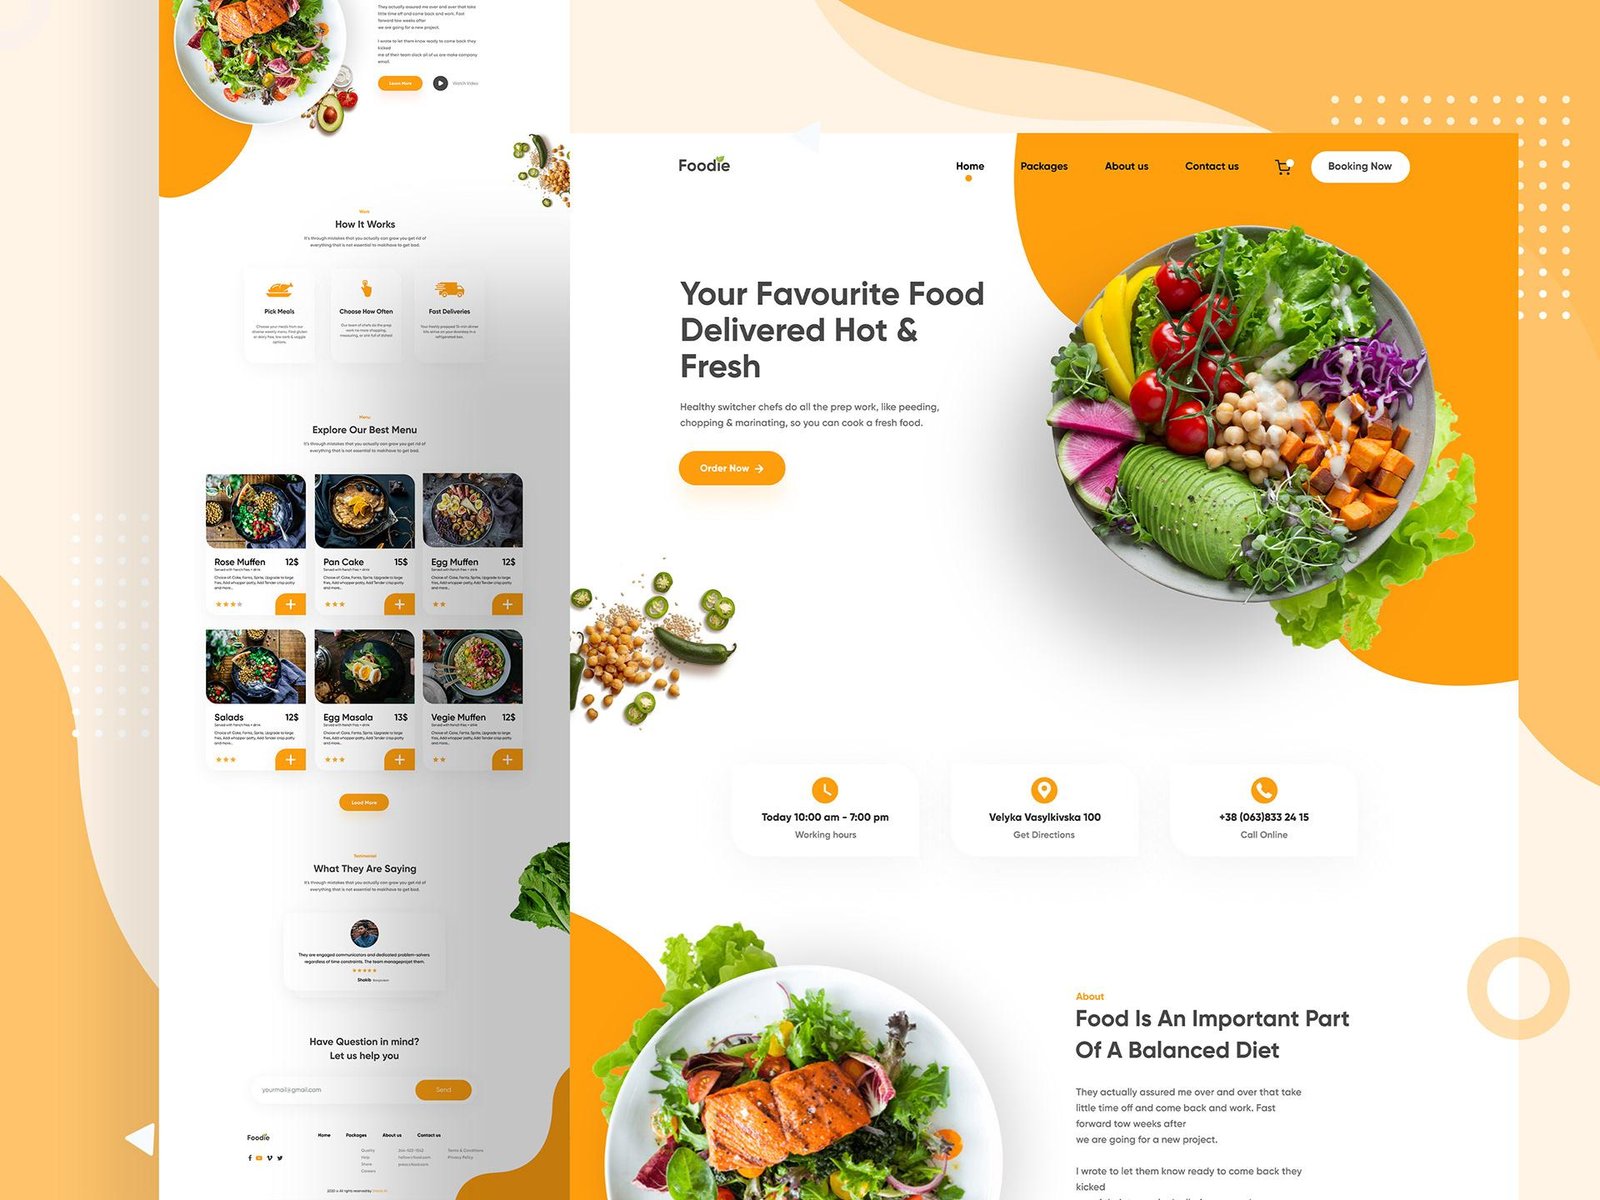
Automated ordering, cart, and checkout on real devices for a UAE food-delivery platform, cutting manual regression from days to minutes per release.
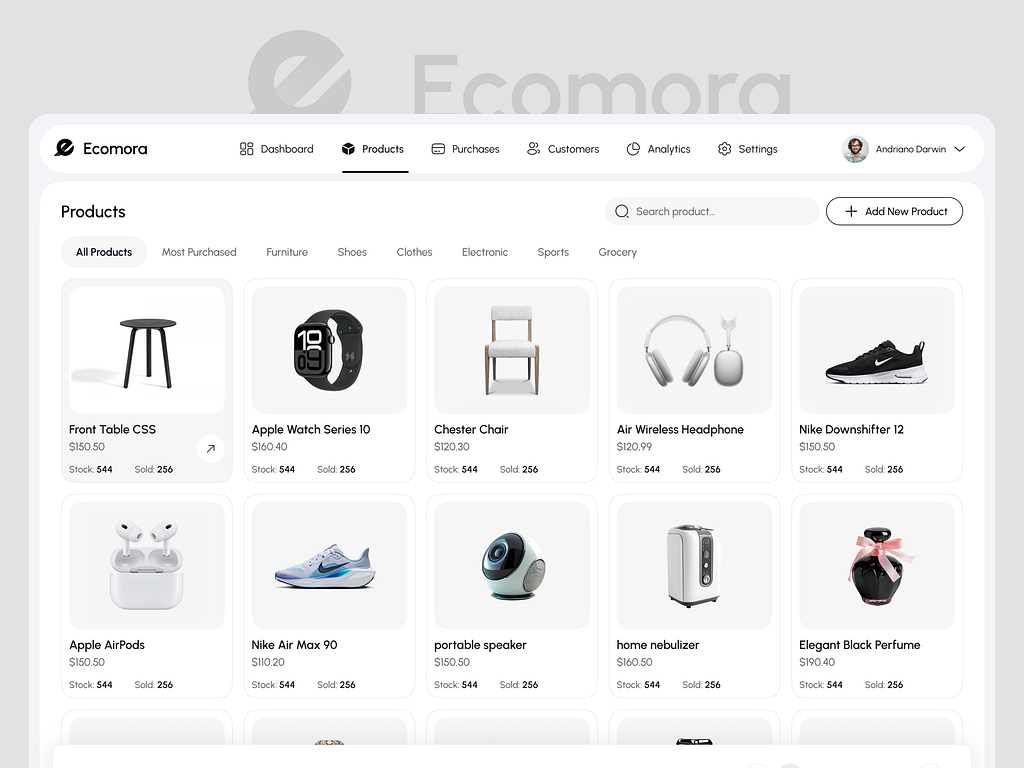
Functional and exploratory testing across catalogue, search, filters, and checkout caught layout and data defects before go-live, so a US retailer launched its new store with no customer-facing incidents.
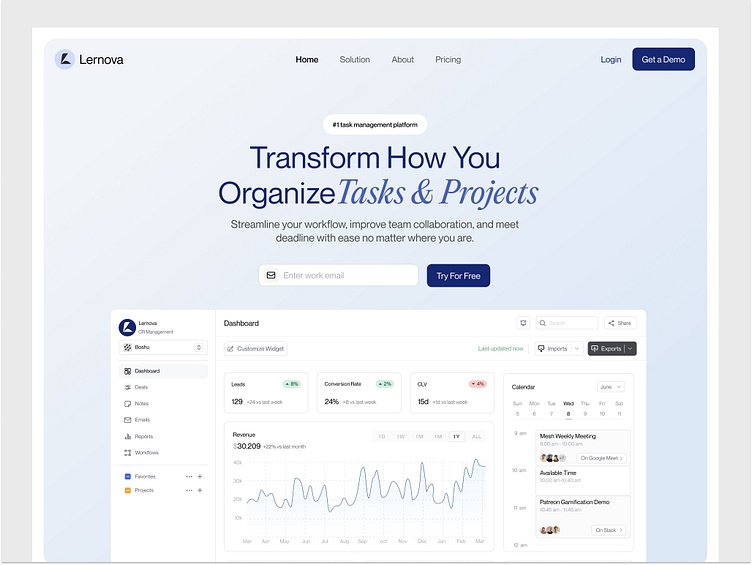
Hands-on regression and exploratory testing of boards, dashboards, and role-based workflows kept every critical path stable through fortnightly releases, holding critical-path coverage at 100% for a UK logistics-operations SaaS.
Real-device usability and hands-on accessibility testing with assistive technology took a public-sector learning app to a clean WCAG 2.2 AA launch with no post-release remediation sprint.
Validated a 99.9% uptime SLA under peak load, so the cloud portal and provisioning APIs held through demand spikes without incident.
Isolated the true checkout bottleneck and produced a validated capacity model showing three times the throughput headroom the platform believed it had.
Proved stable ingestion throughput and latency at over a million device messages an hour, so the platform could onboard new fleets with confidence.
Delivered OWASP-aligned application and API testing that closed the exploitable paths and left the platform with zero critical findings at release.
Tested login, SSO, and token flows end to end and hardened the identity layer against real abuse cases before rollout.
Scoped a focused credentialing pilot over a full rebuild, narrowing the programme 60% for a workforce management platform.
Turned raw on-chain data into a self-service intelligence dashboard that surfaces suspicious wallet activity in seconds for a public financial-intelligence unit.
Wired the proposal-to-execution lifecycle straight into on-chain voting and treasury actions, tripling the speed of a Web3 organisation's proposal cycles.
Fuzz- and invariant-tested escrow that holds buyer funds until both parties confirm delivery meant no funds were ever left stuck for a marketplace platform.
On-chain carbon-credit issuance and retirement contracts gave auditors tamper-proof evidence and cut reporting data errors by 94% for an ESG reporting platform.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
We don't compete on lowest day-rate. We compete on shipped outcomes inside environments that have to clear audit.
Every engineer on every engagement is at least senior, typically eight to fifteen years deep in their craft. No bench rotations, no junior pyramid hidden behind a glossy proposal, no bait-and-switch after contract signature. The architect who scoped your engagement is the same person committing code by week three.
FCA, PRA, EBA, BaFin, FINMA, HIPAA, SOC 2 Type II: every framework we work under is treated as a design constraint from day one, not a final-stage gate. Evidence trails, model-risk packs, change-control artefacts, and pen-test reports ship alongside the code, ready for second-line review without a remediation sprint.
Small pods of three to seven engineers, each with a named delivery lead who owns scope, schedule, and outcomes from kickoff to hand-off, never a faceless team you have to chase for an answer. Weekly demos run against the signed scope, frequent verification gates catch regressions early, and quarterly outcome reviews measure real progress against the original business case rather than a moving target. Together those rituals catch scope drift before it has any chance to compound, so programmes that should take six months don't quietly stretch into eighteen, budgets stay anchored to what was agreed, and every milestone ships with a written, testable definition of done that both sides sign off before we move on.
We don't disappear the moment the engagement closes. Managed services, hypercare windows, named on-call rotations, or quarterly health checks: pick the depth that matches your operational risk profile. About seventy percent of clients return for a second programme, usually because the team that shipped the first one is still on the other end of the page.
Anonymous under MNDA. Each quote is from a senior automotive buyer who owned the engagement end to end.
“BritonOne Technology treated the R155 CSMS as engineering output, not paperwork. The evidence trail was ready when the Type Approval Authority asked, and we cleared it on the first submission across 2.1M vehicles.”
Direct answers to what procurement, security, and delivery leads weigh before signing: compliance, integration, and the accountability we put in writing.
Yes. We build the Cyber Security Management System and Software Update Management System as integrated engineering output, mapped to ISO/SAE 21434, with the threat analysis, risk assessment, and update-campaign records the Type Approval Authority expects. The evidence pack is produced per release, not reconstructed before audit, and it is designed to clear on first submission.