EHR Integration & FHIR
HL7 v2, FHIR R4 and SMART-on-FHIR against Epic, Cerner, Meditech and TPP/EMIS, audit-ready by default.
EHR integration, clinical AI, telehealth, and population-health, shipped by senior teams, with the clinical safety case and DPIA in the box.
One accountable senior pod owns the whole stack end to end: architecture, build, clinical safety and handover.
HL7 v2, FHIR R4 and SMART-on-FHIR against Epic, Cerner, Meditech and TPP/EMIS, audit-ready by default.
Ambient scribes and summarisation, clinician-edited before commit, DSPT-compliant from day one.
Booking, video consult, results and secure messaging, NHS Digital and HIPAA grade, accessible by default.
Risk scores, early-warning and triage, explainable, drift-monitored, cleared at safety review.
Pseudonymised lakehouses on Databricks and Snowflake, lineage-tracked, OneLondon and TRE-ready.
HIPAA, DSPT and DCB0129/0160 evidence built in, handed over every release, not after the gate.
Every BritonOne Technology build ships clinical safety, DPIA and DCB0129/0160 evidence with the code, not months after the gate. Platforms clear DSPT first time, and clinicians get their hours back.
Hand-written HL7 v2 shims silently drop fields each EHR release.
Clinicians type instead of listen; coding windows slip.
Black-box scores, no drift monitoring, rejected at clinical review.
Six forensic weeks per submission; the same findings recur yearly.
Versioned contracts and pinned mappings catch breaking changes before release.
Ambient drafts they edit, not write: hours of typing returned each week.
Explainable, drift-monitored early-warning scores, signed off at review.
DSPT and DCB0129/0160 evidence lands with each build. Submission's a checkbox.
Selected work across NHS trusts, US health systems and digital-first providers, anonymised where required, specific on the result.
Ambient drafts for 600 clinicians across outpatients, A&E and wards, DCB0129 and DPIA shipped with the build; 95% of notes hit the coding window.
Real-time early-warning score wired into Epic, explainable, drift-monitored and MHRA SaMD-evidenced; sepsis lead time cut 27% on acute wards.
Booking, results, secure messaging and PROMs in one HIPAA-grade app, wired to the EHR with a full FHIR audit trail; 61% adoption in year one.
End-to-end telehealth from booking to prescribing, at NHS Digital and HIPAA grade, nine-minute median wait across every launch market.
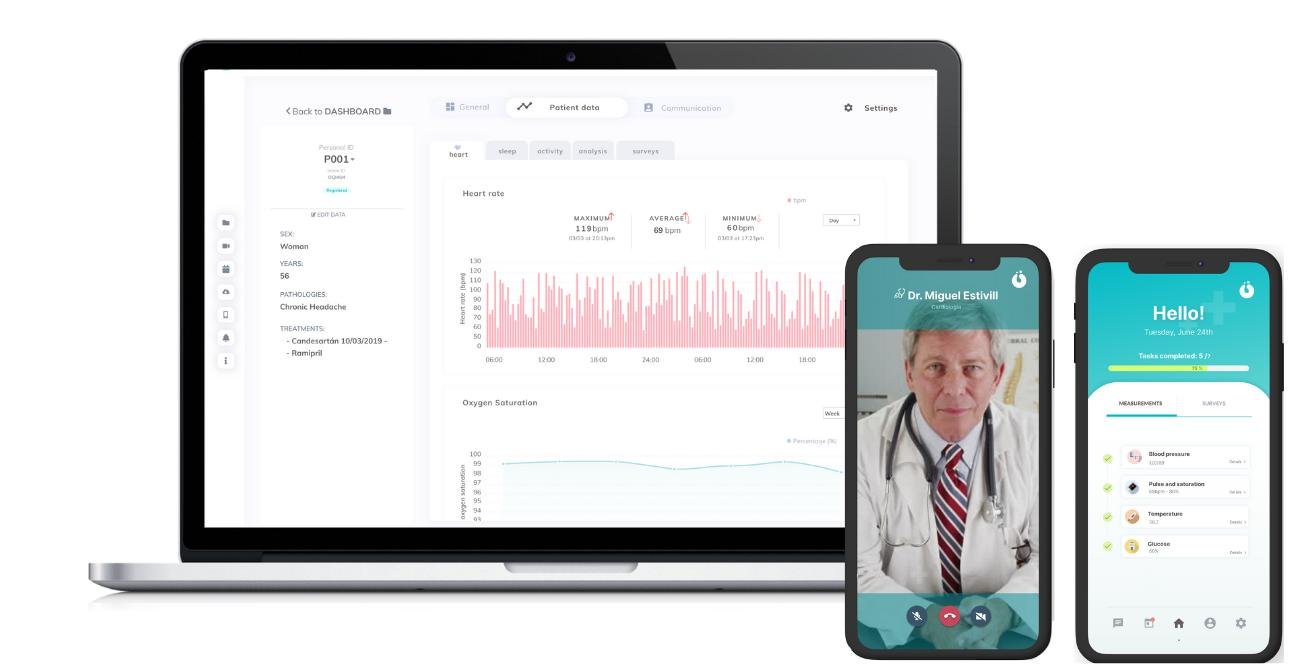
Pseudonymised lakehouse spanning 2.4M lives, OneLondon-aligned and lineage-tracked, with IG sign-off in days rather than months.
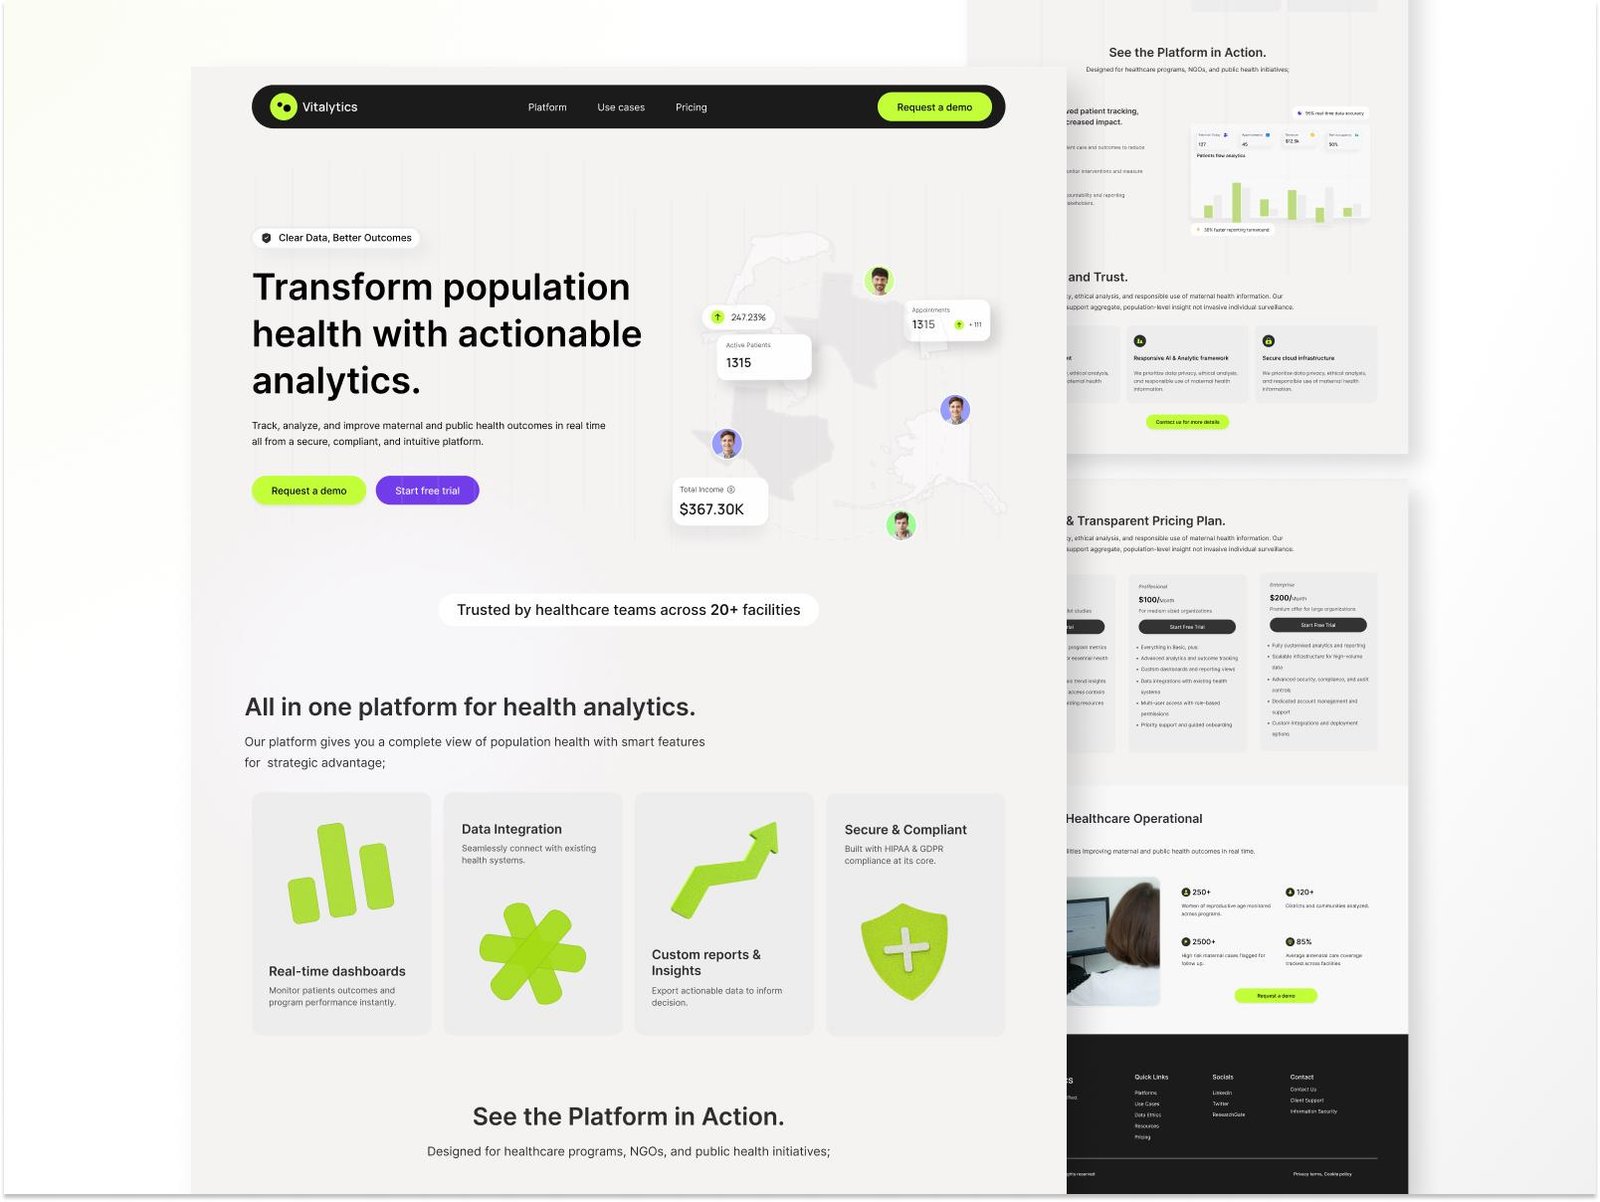
SMART-on-FHIR app live across four EHRs (Epic, Cerner, Meditech and TPP) in nine months, on typed and CI-gated profiles.
Production integrations against every major EHR: clinician workflows, patient data and analytics wired into a single audit-ready surface.
Connected. Unified. Audit-ready.
Typed FHIR profiles, conformance-tested in CI. Changes flow through PRs and reviewed migrations, no midnight pages on EHR upgrades.
DCB0129 hazard log opens at architecture; DCB0160 evidence emits per release, both signed off first review.
Per-encounter trail: user, action, payload diff and safety classification, exportable to IG on demand.
Every engagement walks the same path, sized to your problem, but with the same verification gates baked in.
Two-week paid sprint. Architect-led. Output: regulator map, costed roadmap, signed scope.
Pod composition, sequenced milestones, change-control governance, and risk register.
Reference architecture, threat model, design system, and acceptance criteria locked.
Weekly demos, trunk-based, CI/CD from day one. Code reviewed against spec at every gate.
Unit, integration, e2e, security, performance, and accessibility, automated and gated.
Blue-green or canary, observability live before launch, rollback rehearsed.
Managed services or hypercare hand-off. Defined SLOs, named on-call, monthly reviews.
Success stories
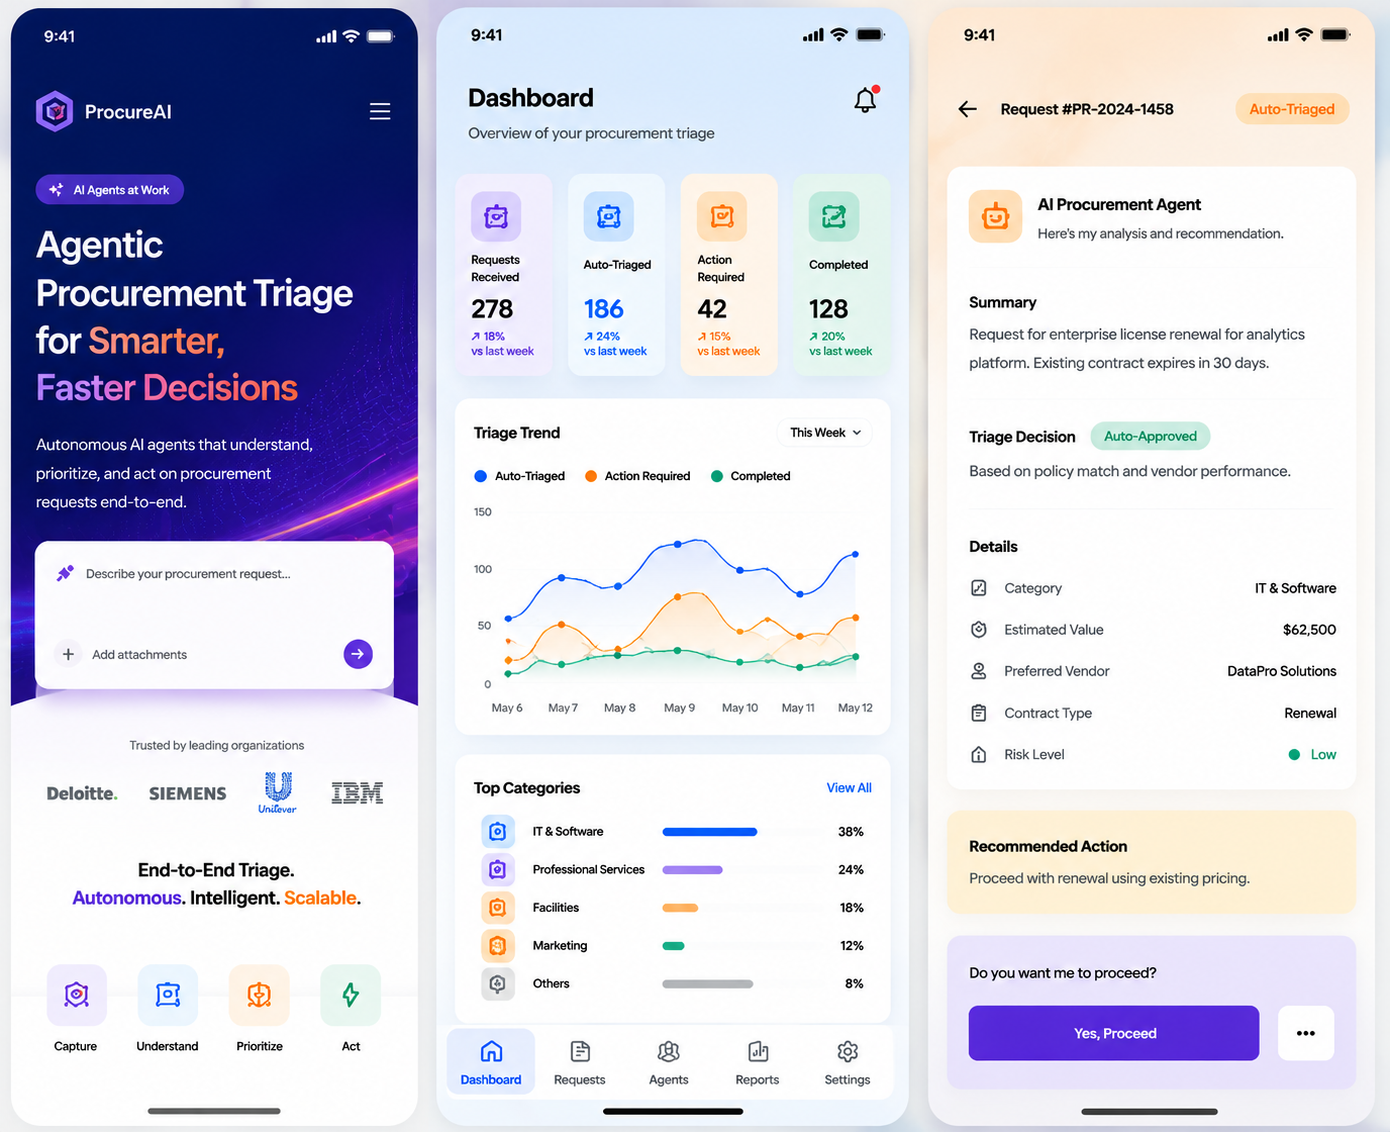
Routed and matched 73% of purchase requests end to end, escalating only genuine exceptions.
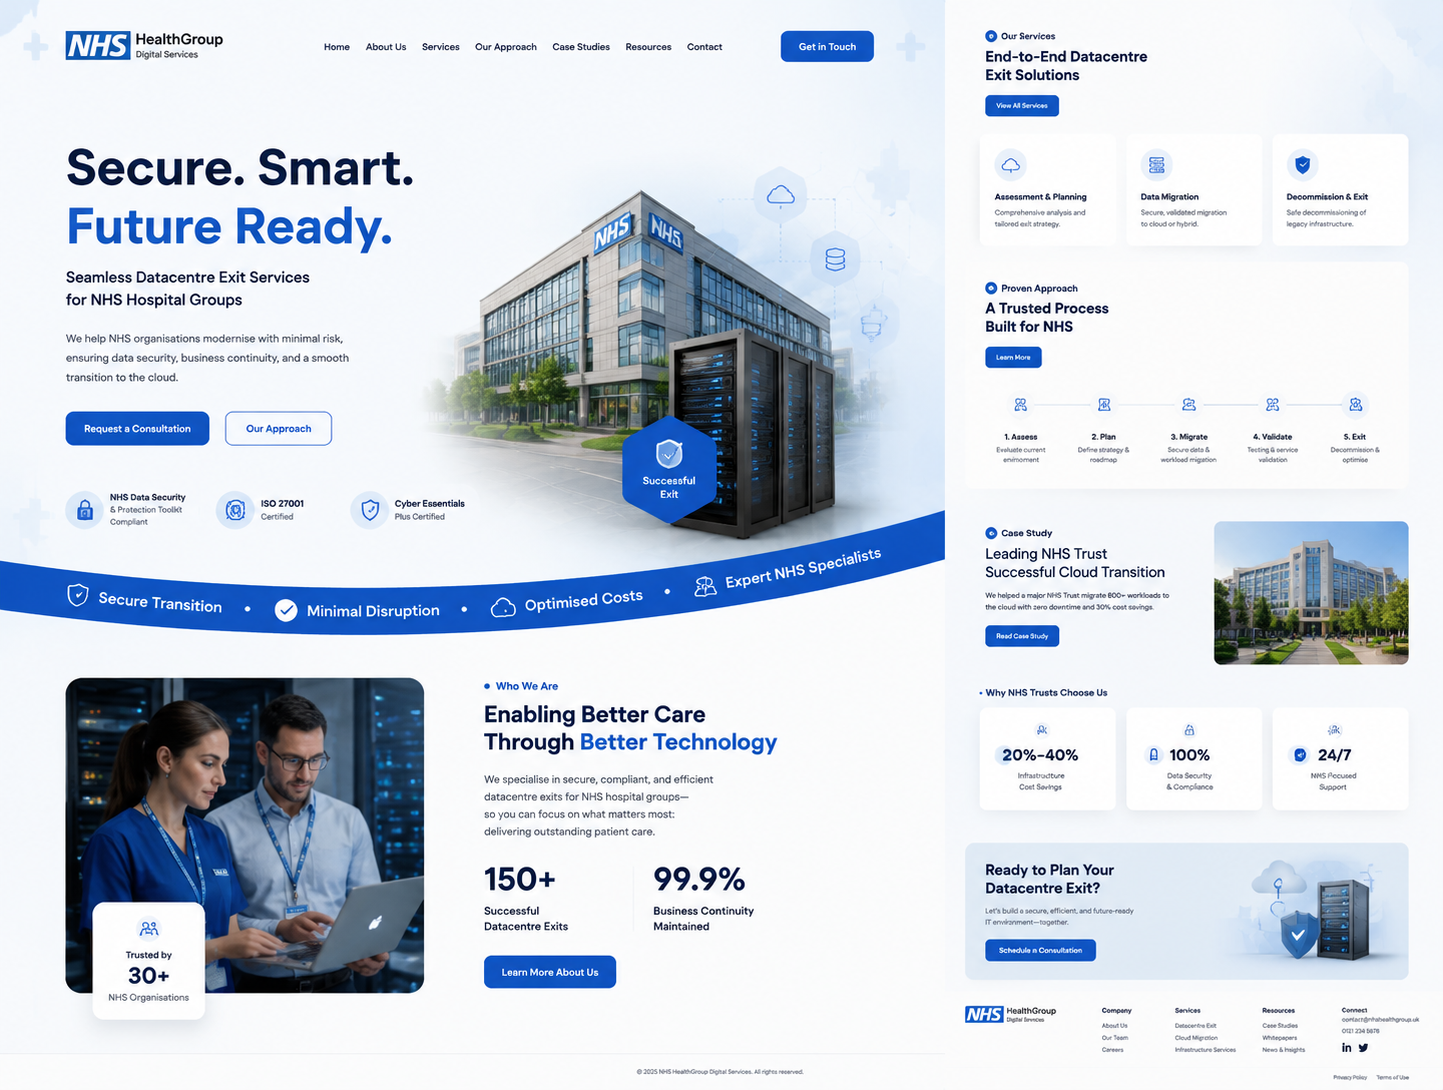
Migrated 900 clinical workloads off two datacentres to the cloud with zero downtime on patient-facing systems.
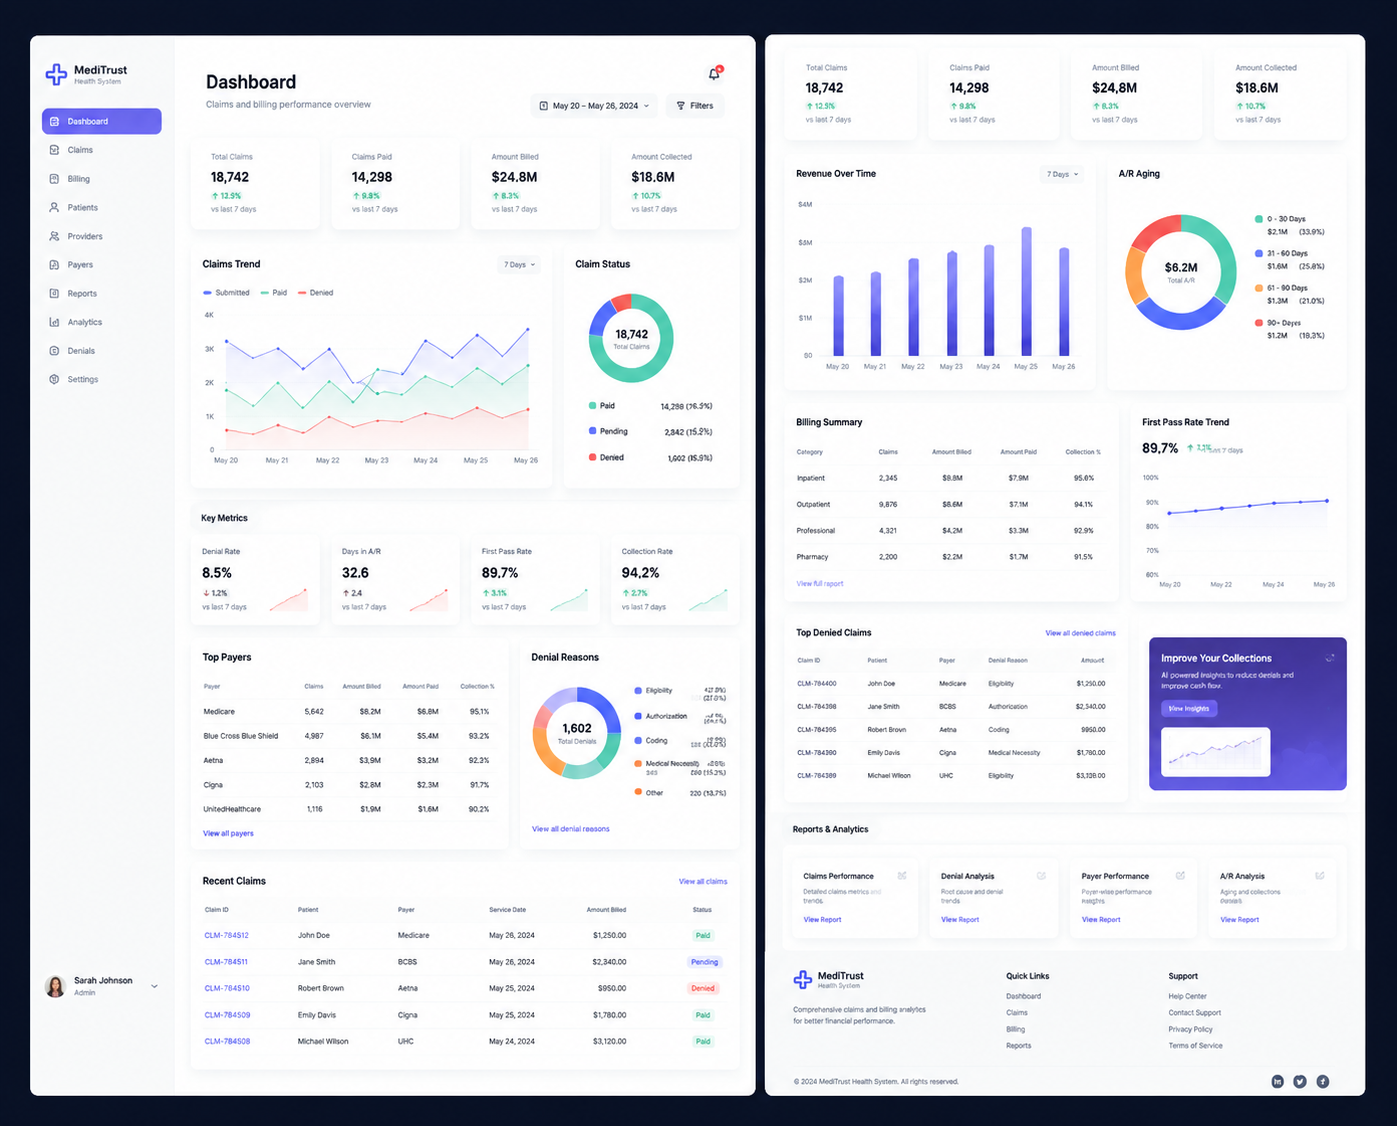
Unified claims and billing data, cutting rejected-claim rework 38% for a hospital group.
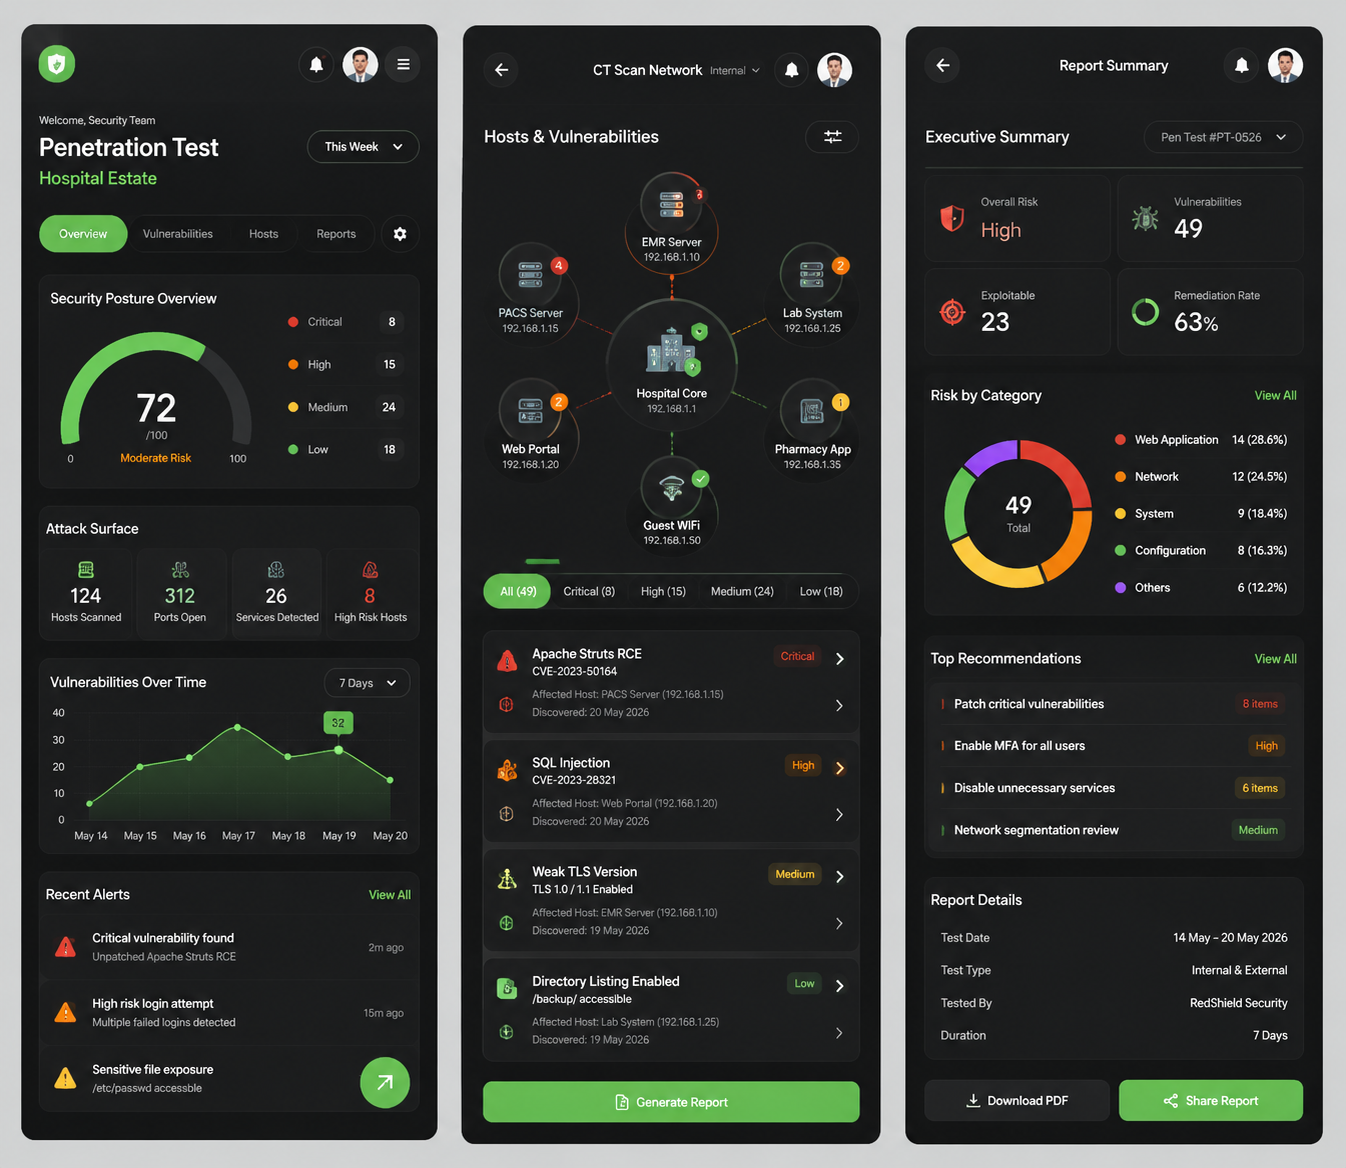
Surfaced 61 exploitable paths across a hospital estate, prioritised by patient-safety impact.
Penetration-tested the credential vault and its sync, verifying encryption and access controls end to end so stored secrets stayed protected.
Delivered an audit-ready blockchain architecture for tamper-evident patient records and consent, cleared against HIPAA and GDPR before build.
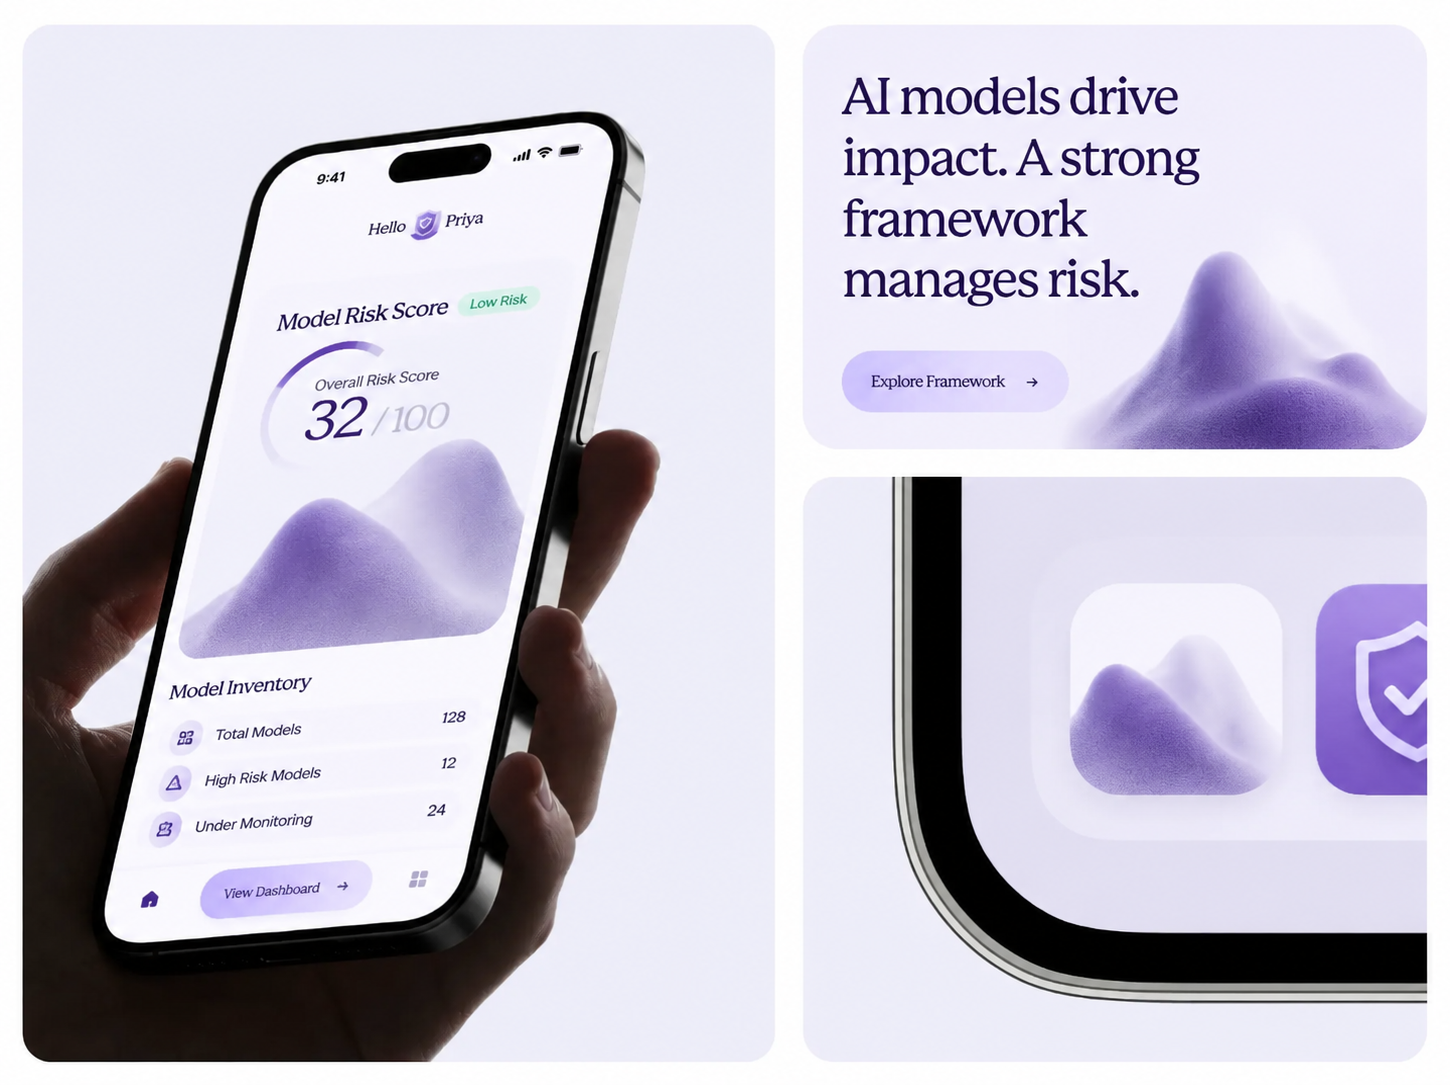
Stood up a board-ready AI governance and model-risk framework for a pharma company in 9 weeks, cleared at first internal audit.
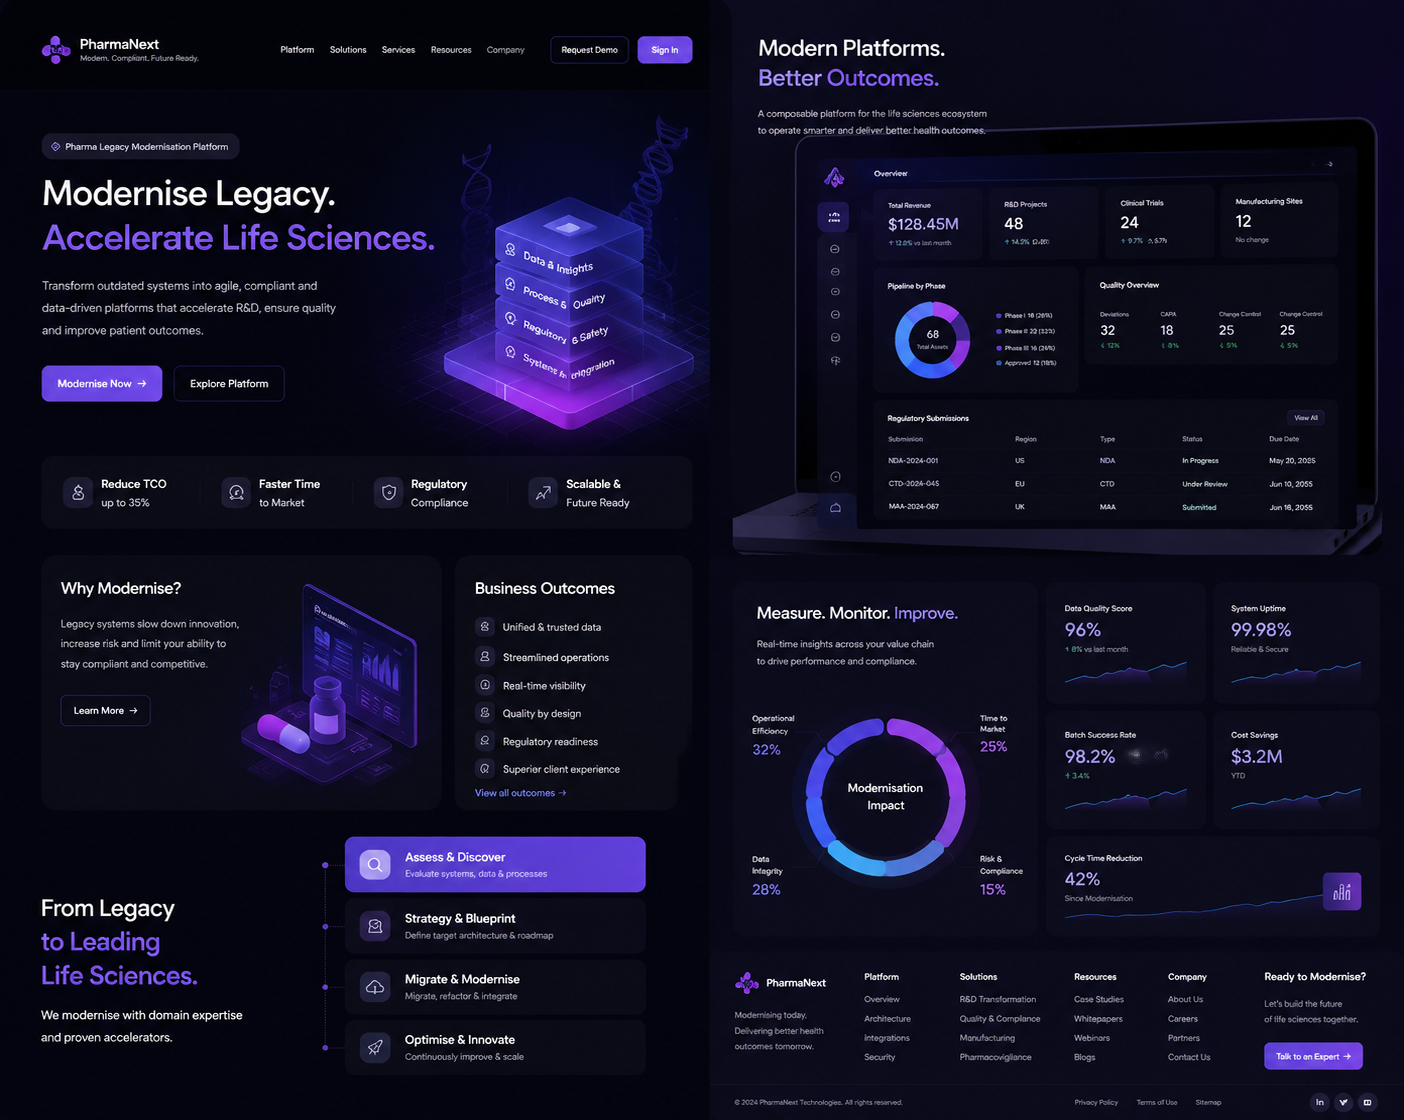
Strangled a validated legacy system into microservices, cutting change lead time 40% for a pharma manufacturer.
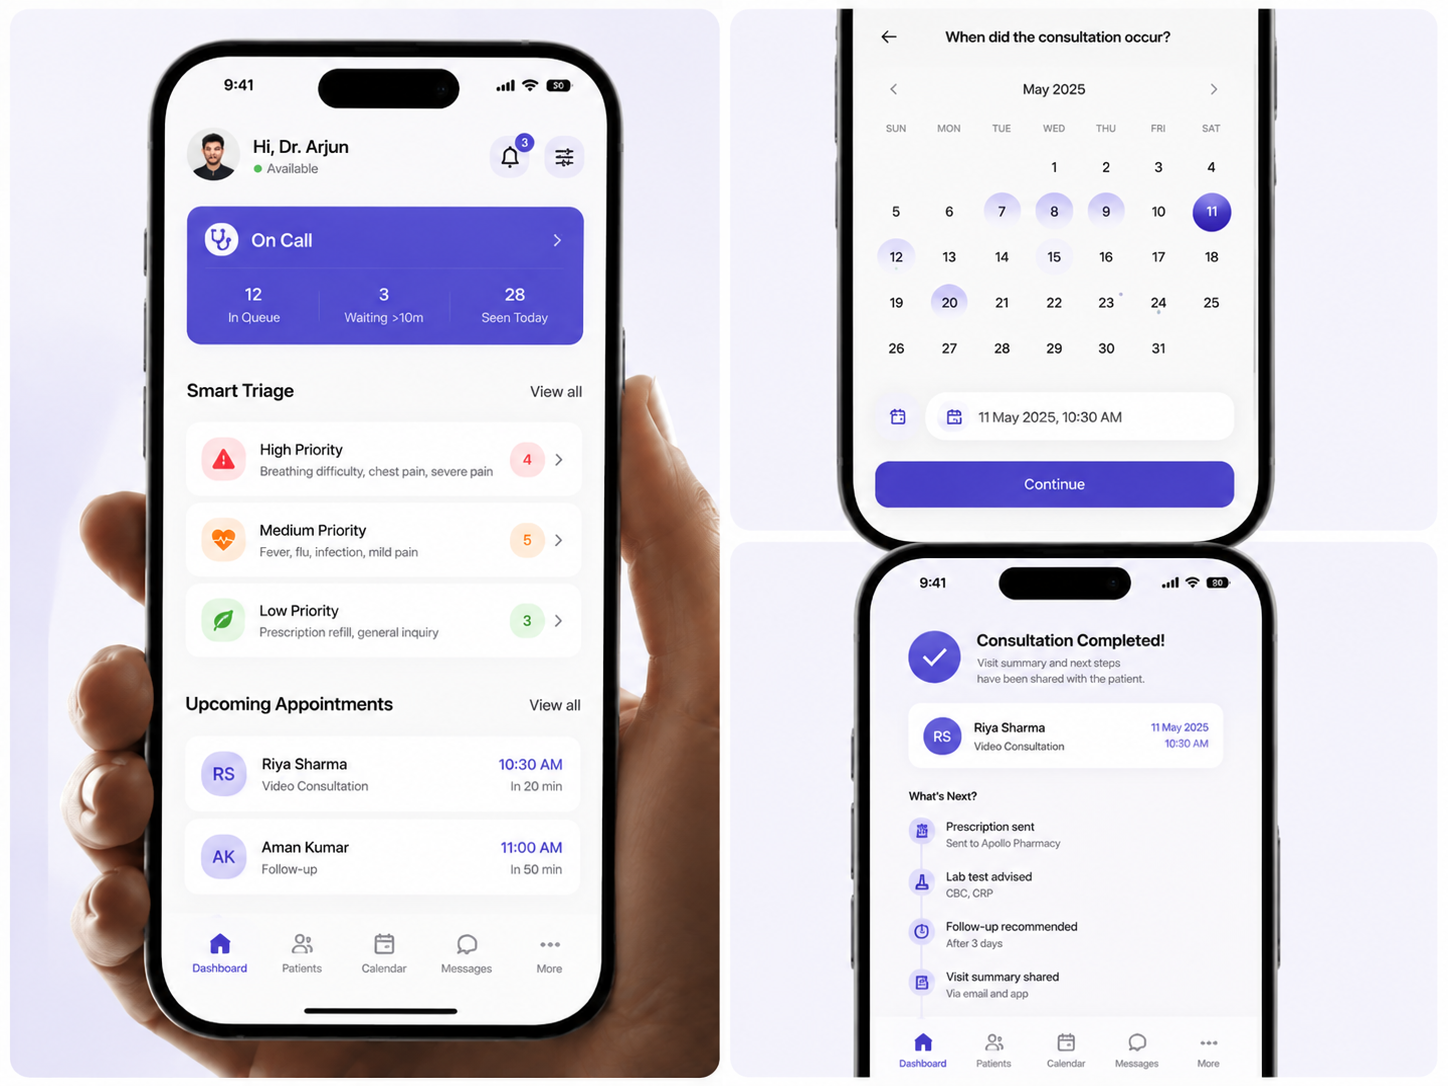
Photo-and-symptom-first triage app cut consultation prep time 54% for a telemedicine provider.
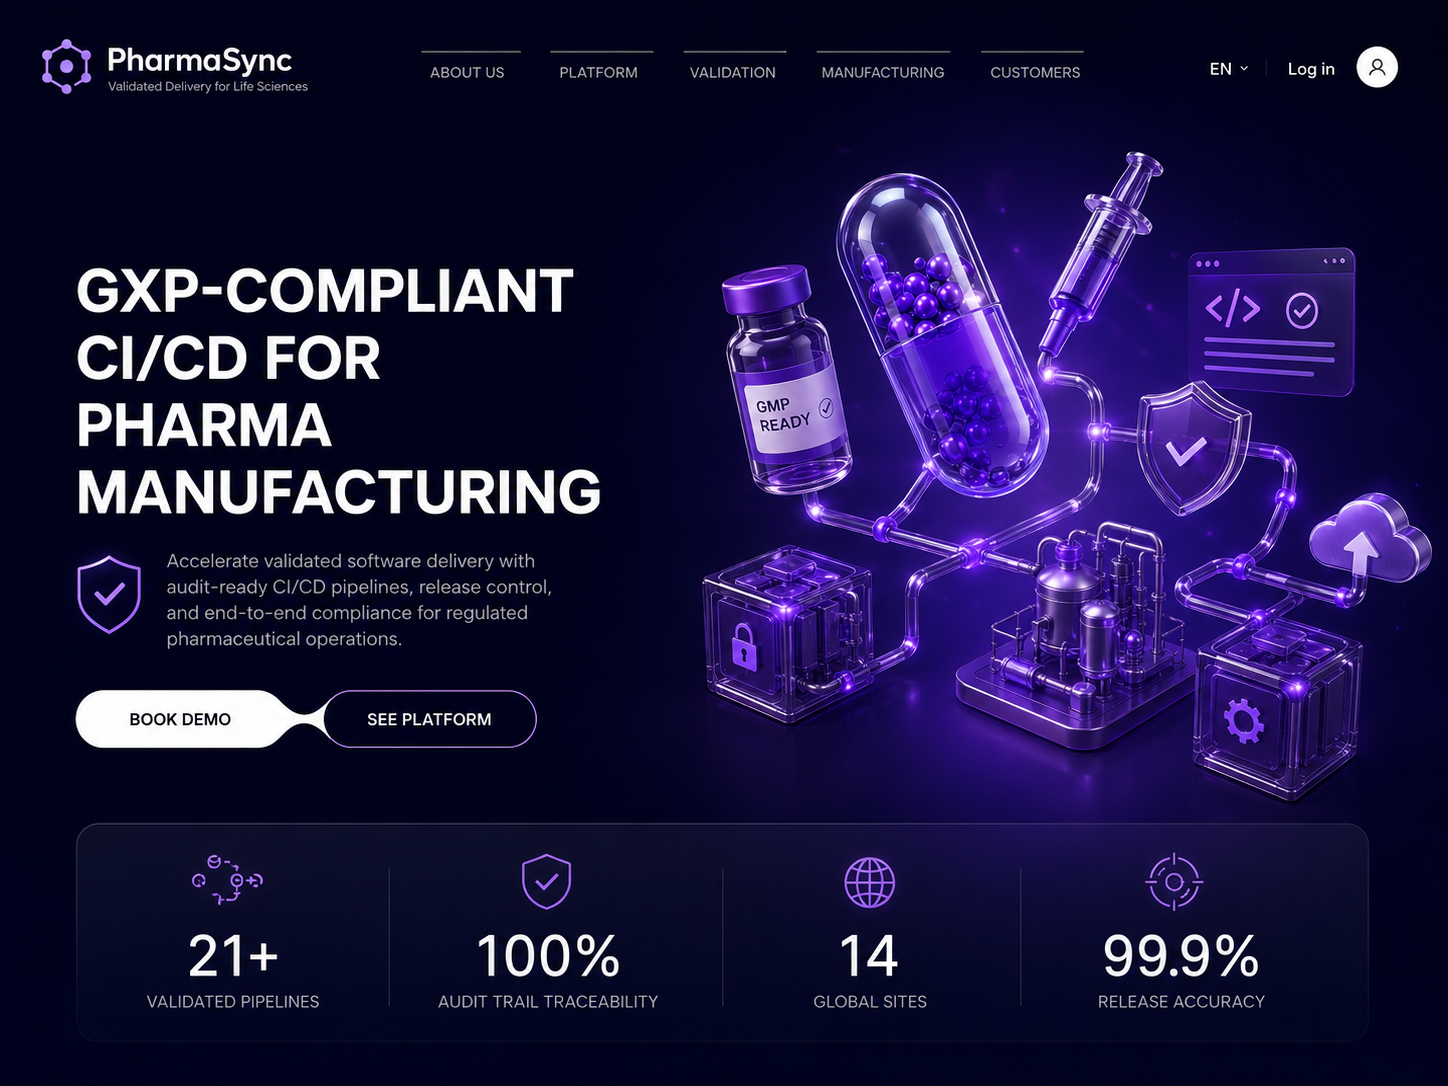
Delivered validated, GxP-compliant CI/CD, cutting release lead time 8x with full audit evidence.
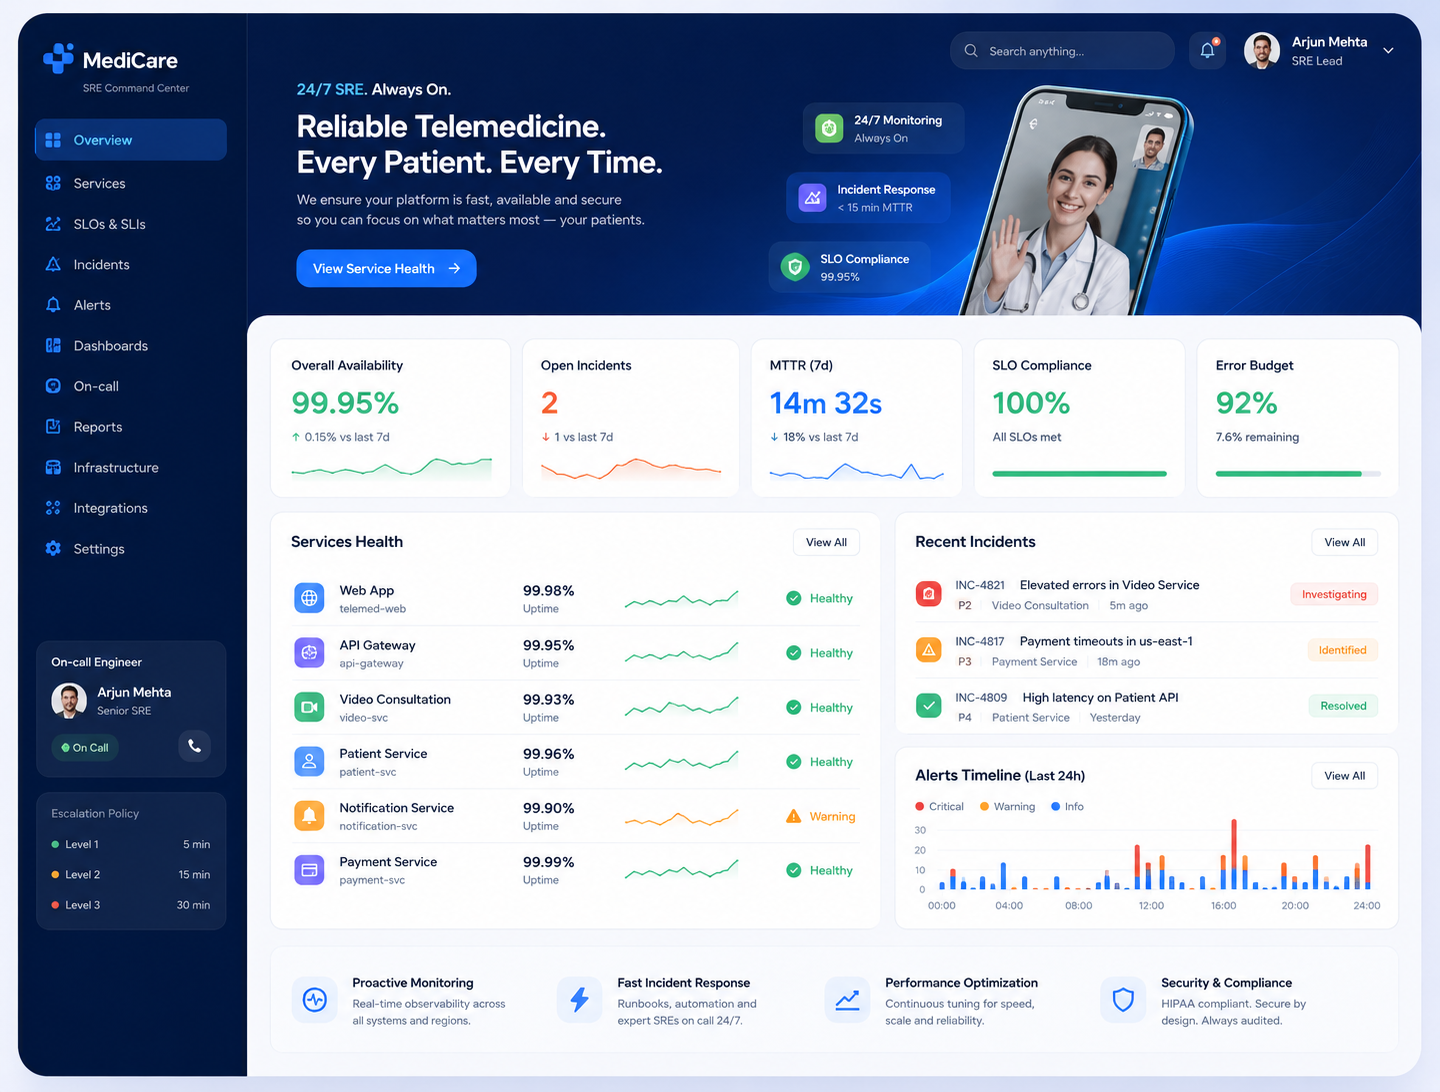
Ran a telemedicine platform to a 99.98% SLO with a follow-the-sun on-call.
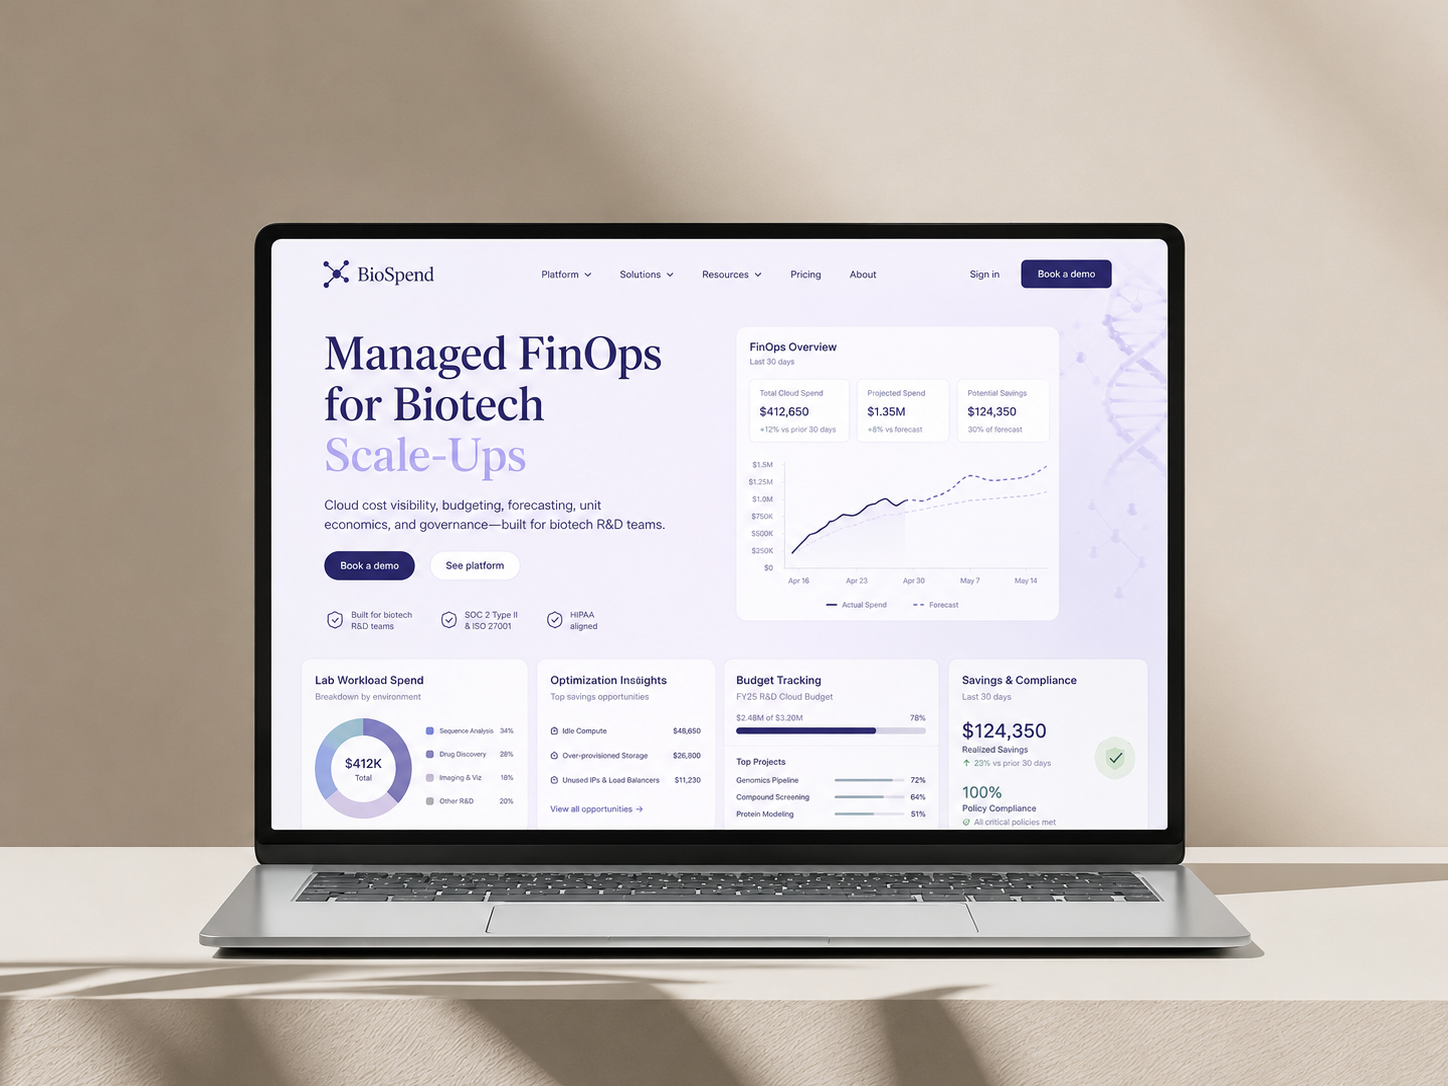
Cut monthly cloud spend 37% for a genomics biotech without slowing a single pipeline.
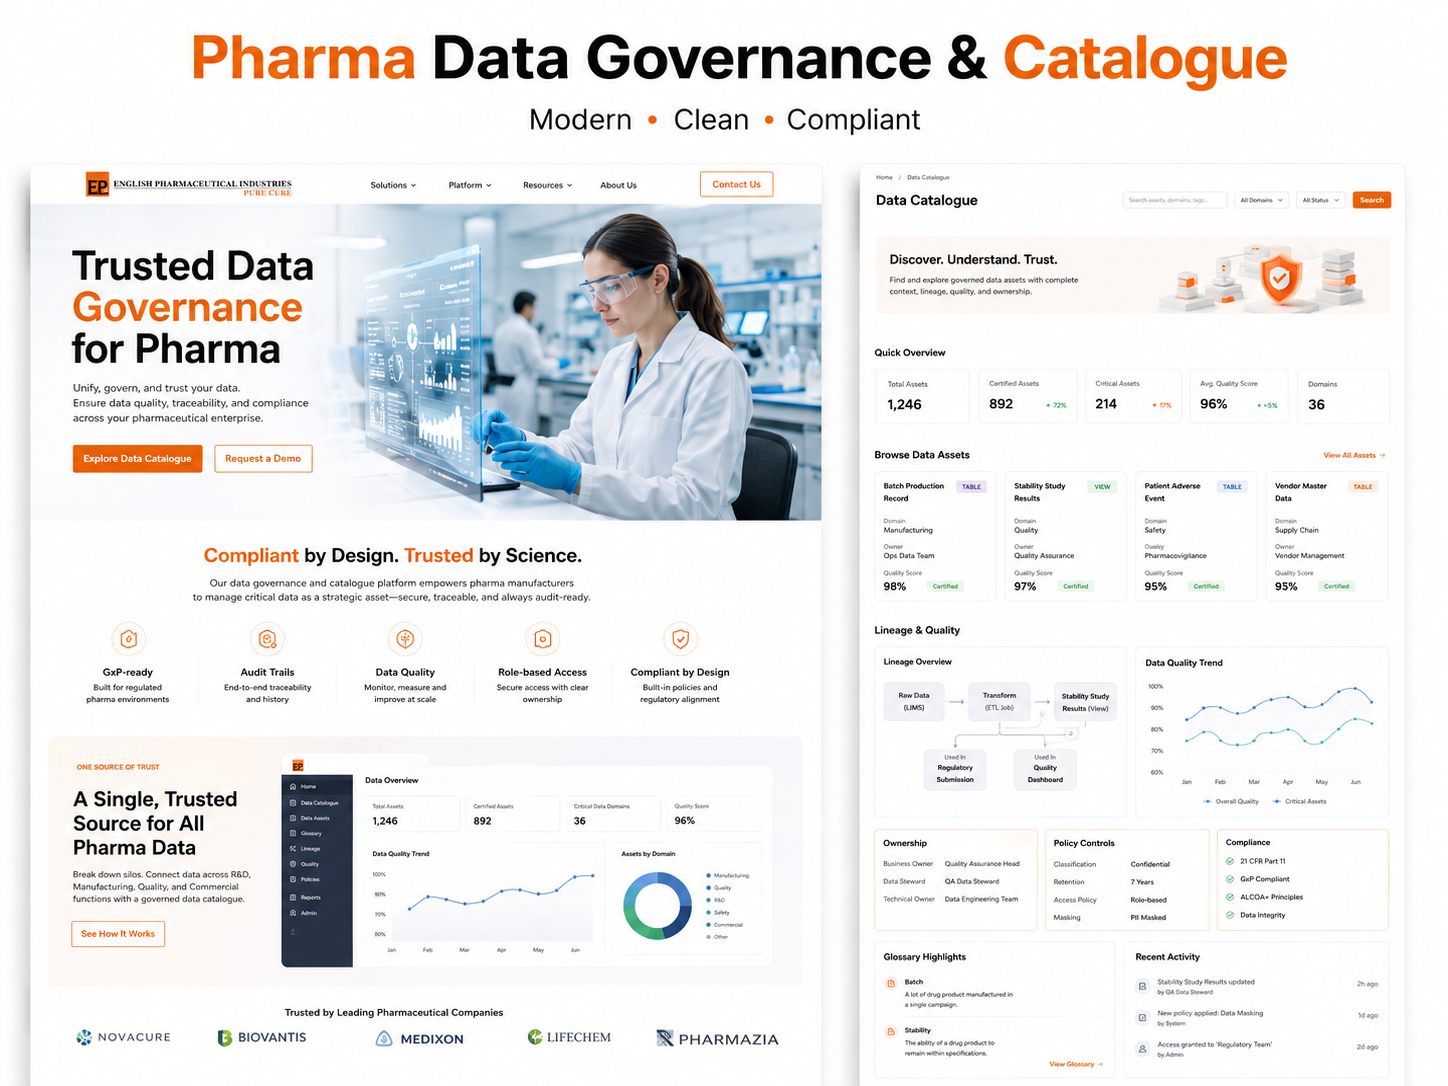
Catalogued and lineage-traced 100% of GxP-regulated data domains for a pharma manufacturer.
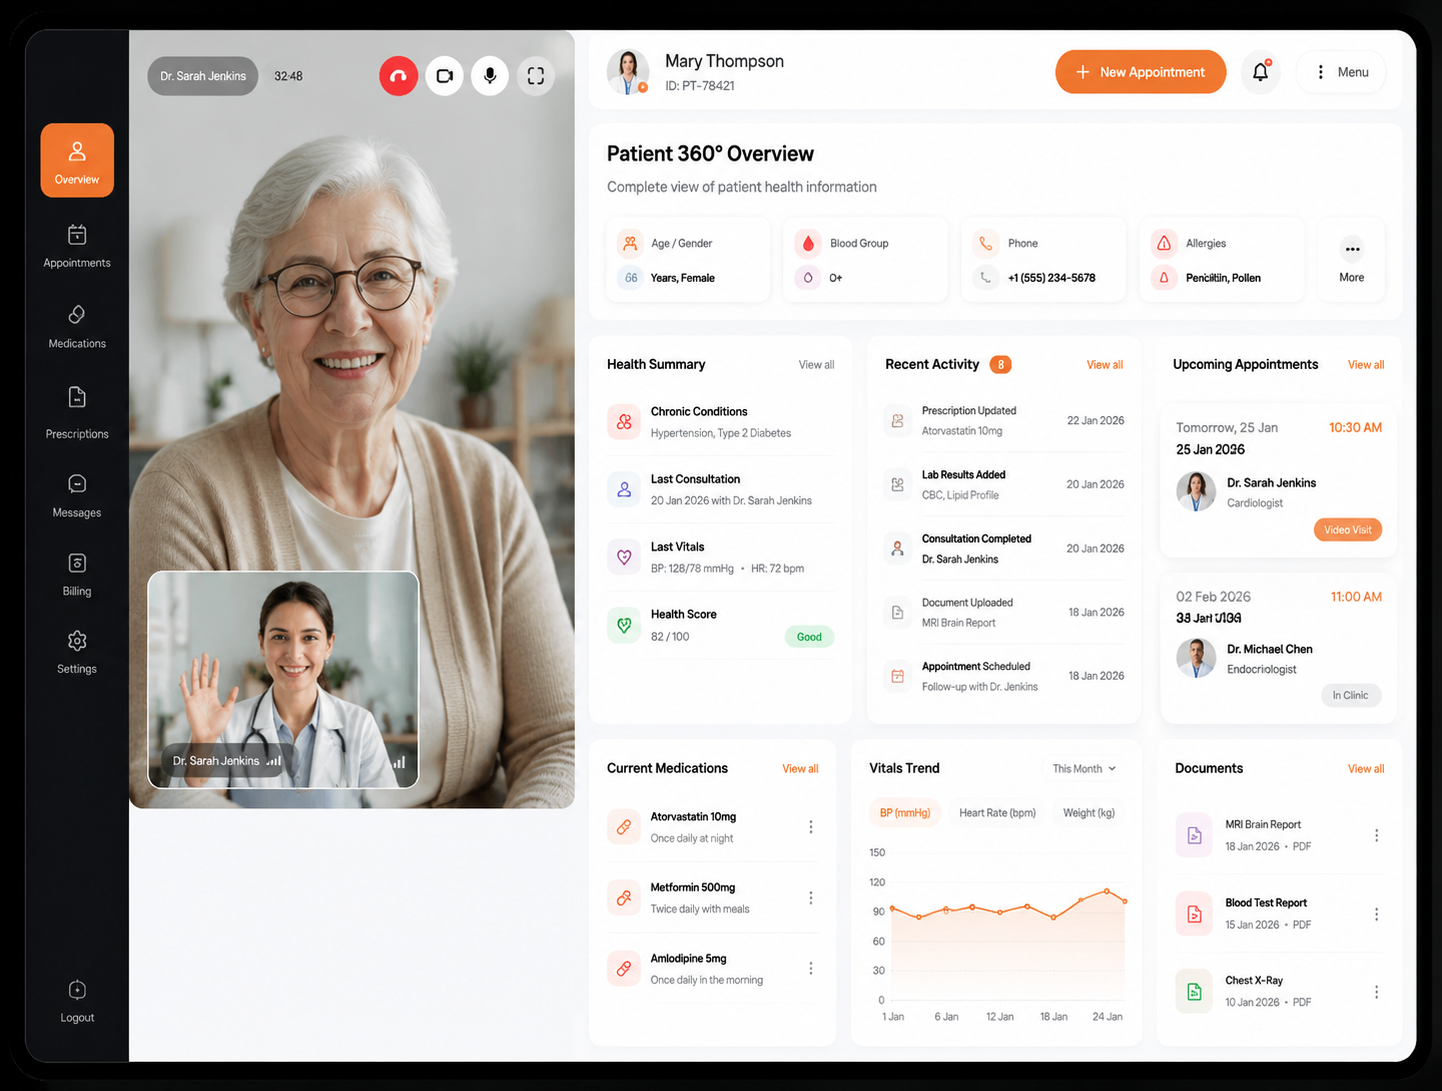
Unified a fragmented patient view, lifting care-team efficiency 24% at a telemedicine provider.
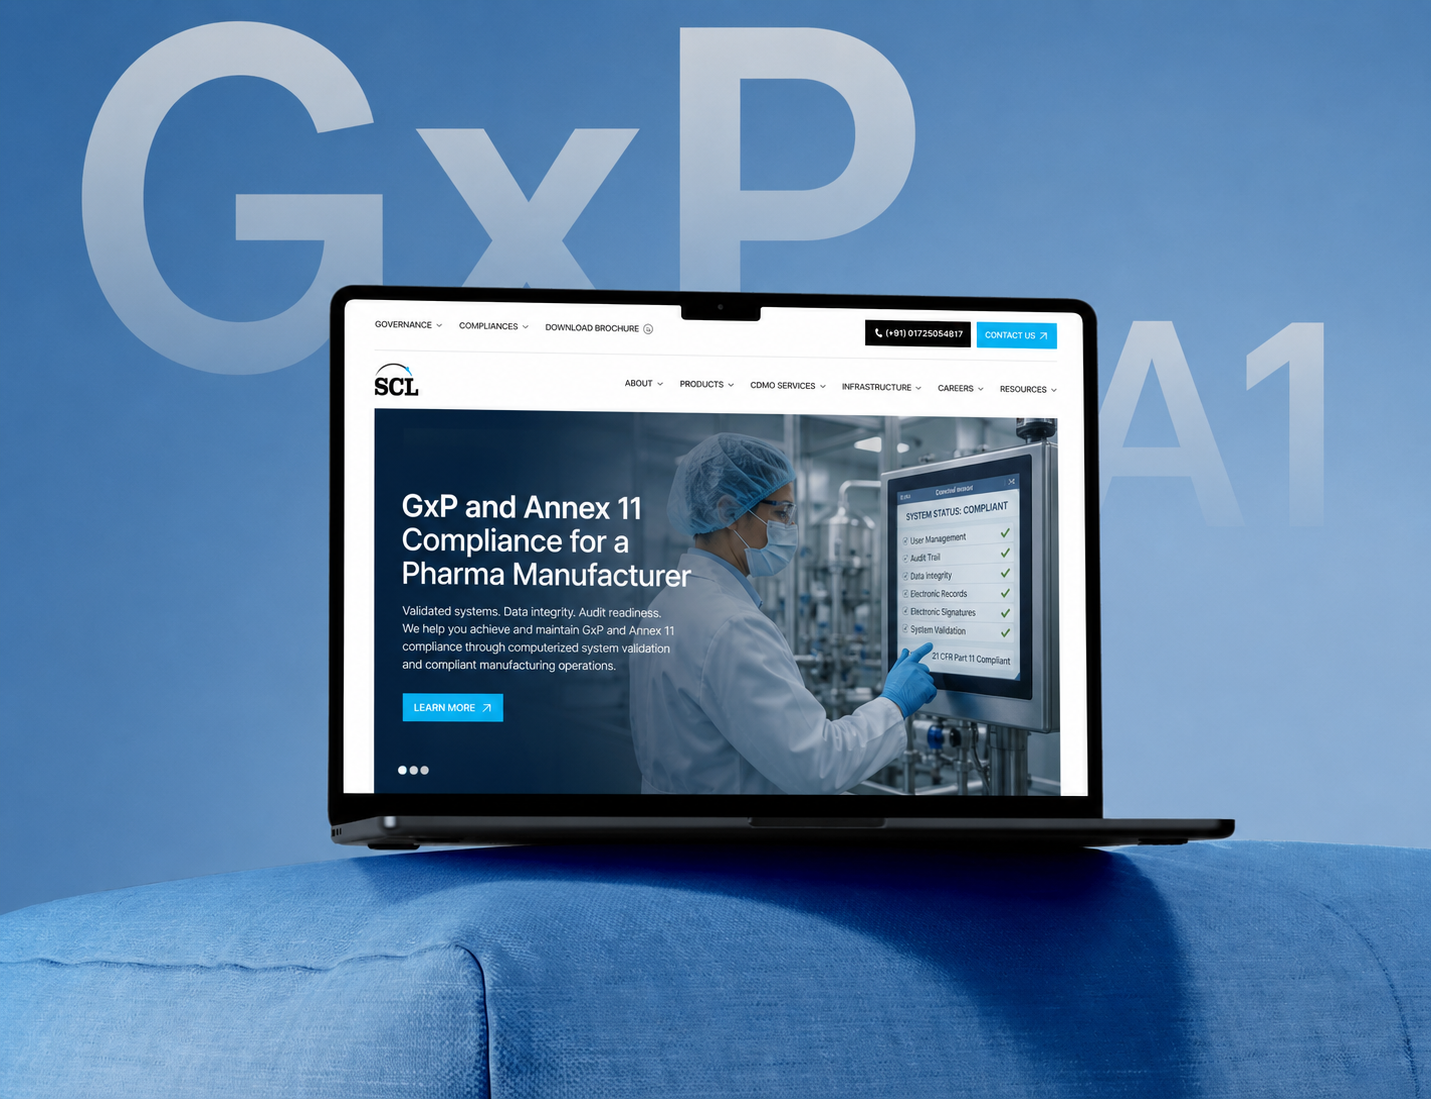
Reached validated Annex 11 compliance for a pharma manufacturer in 12 weeks.
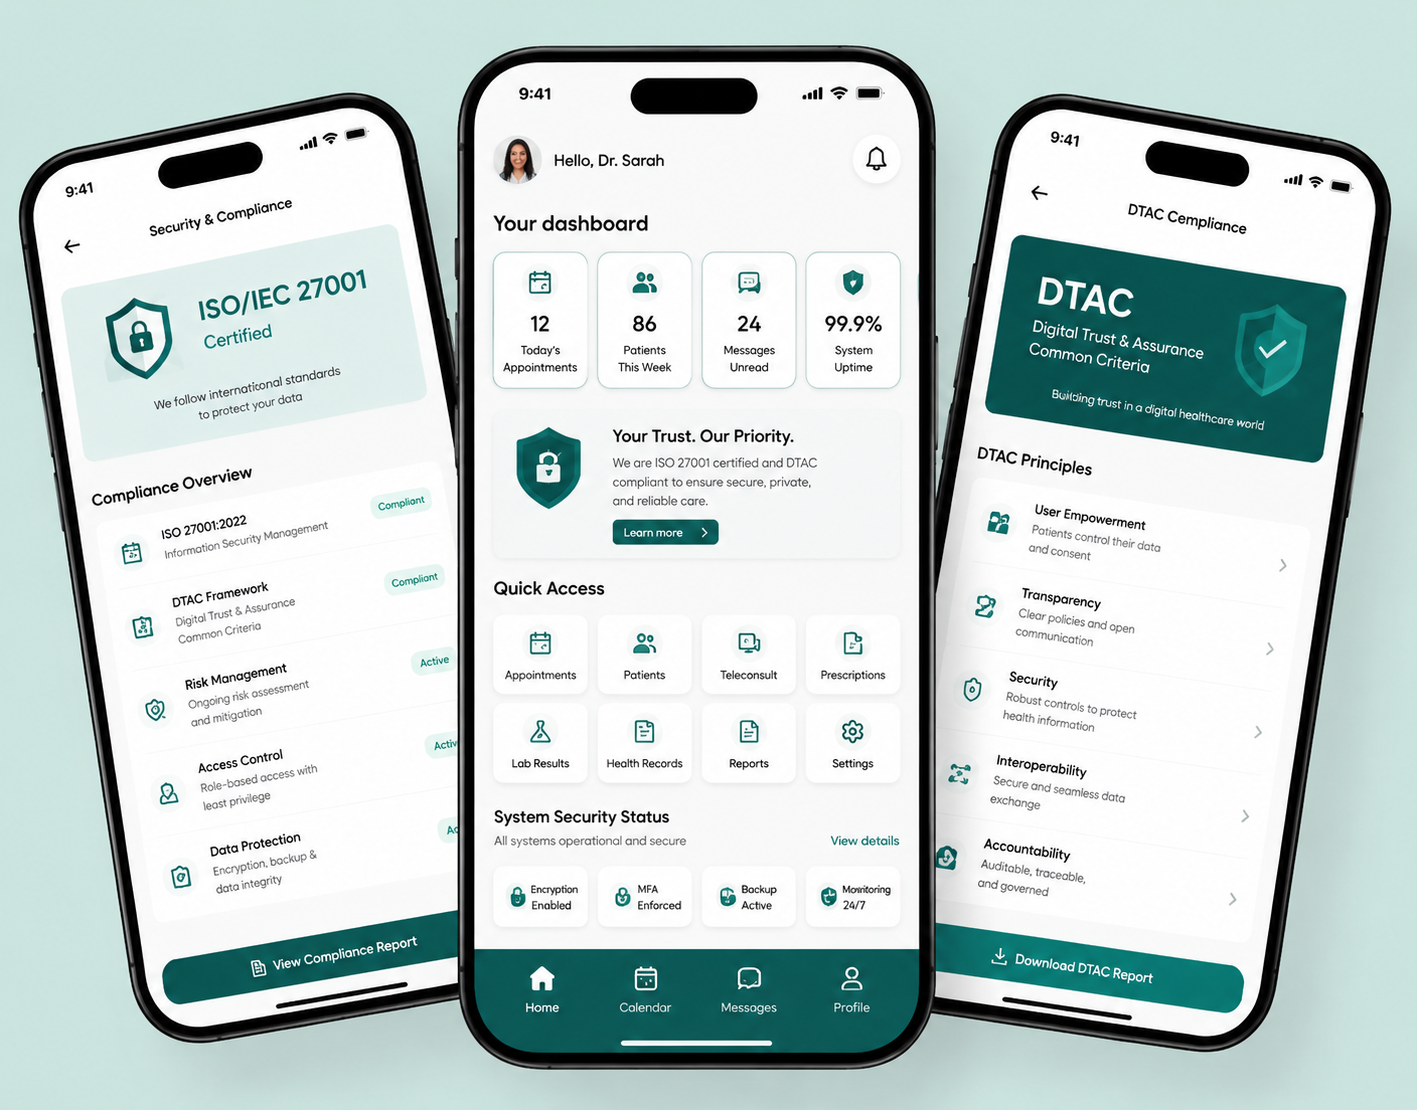
Achieved ISO 27001 and NHS DTAC assurance at first assessment for a telemedicine platform.
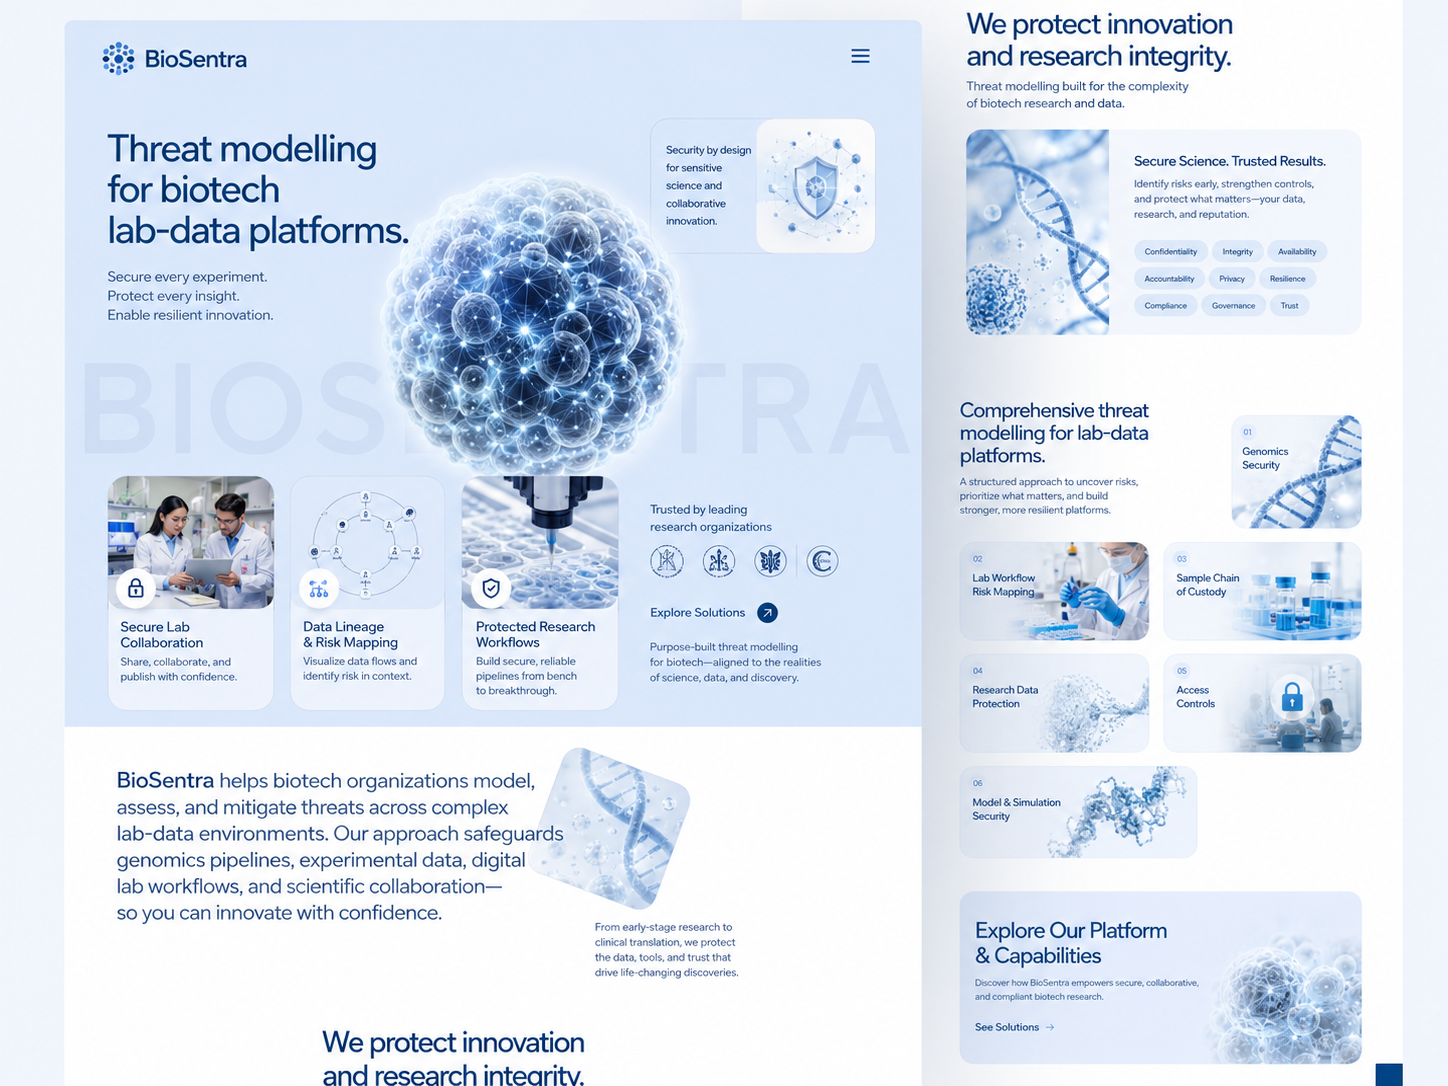
Identified nine design-level risks in a biotech's lab-data platform before build.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
We don't compete on lowest day-rate. We compete on shipped outcomes inside environments that have to clear audit.
Every engineer on every engagement is at least senior, typically eight to fifteen years deep in their craft. No bench rotations, no junior pyramid hidden behind a glossy proposal, no bait-and-switch after contract signature. The architect who scoped your engagement is the same person committing code by week three.
FCA, PRA, EBA, BaFin, FINMA, HIPAA, SOC 2 Type II: every framework we work under is treated as a design constraint from day one, not a final-stage gate. Evidence trails, model-risk packs, change-control artefacts, and pen-test reports ship alongside the code, ready for second-line review without a remediation sprint.
Small pods of three to seven engineers, each with a named delivery lead who owns scope, schedule, and outcomes from kickoff to hand-off, never a faceless team you have to chase for an answer. Weekly demos run against the signed scope, frequent verification gates catch regressions early, and quarterly outcome reviews measure real progress against the original business case rather than a moving target. Together those rituals catch scope drift before it has any chance to compound, so programmes that should take six months don't quietly stretch into eighteen, budgets stay anchored to what was agreed, and every milestone ships with a written, testable definition of done that both sides sign off before we move on.
We don't disappear the moment the engagement closes. Managed services, hypercare windows, named on-call rotations, or quarterly health checks: pick the depth that matches your operational risk profile. About seventy percent of clients return for a second programme, usually because the team that shipped the first one is still on the other end of the page.
Anonymous under MNDA. Each quote is from a senior healthcare buyer who owned the engagement end to end.
“First production AI feature we have launched that cleared DCB0129 on the first attempt. The hazard log and the eval evidence landed alongside the model, not three months after.”
Direct answers to what procurement, security, and delivery leads weigh before signing: compliance, integration, and the accountability we put in writing.
Yes. We engineer to DSPT mandatory evidence from day one (Cyber Essentials Plus, ISO 27001, access controls, audit trails, and data-flow mapping) and we hand over the evidence pack alongside each release. Most clients use the artefacts we ship as the body of their annual submission.