
Penetration test for a hospital estate
Surfaced 61 exploitable paths across a hospital estate, prioritised by patient-safety impact.
61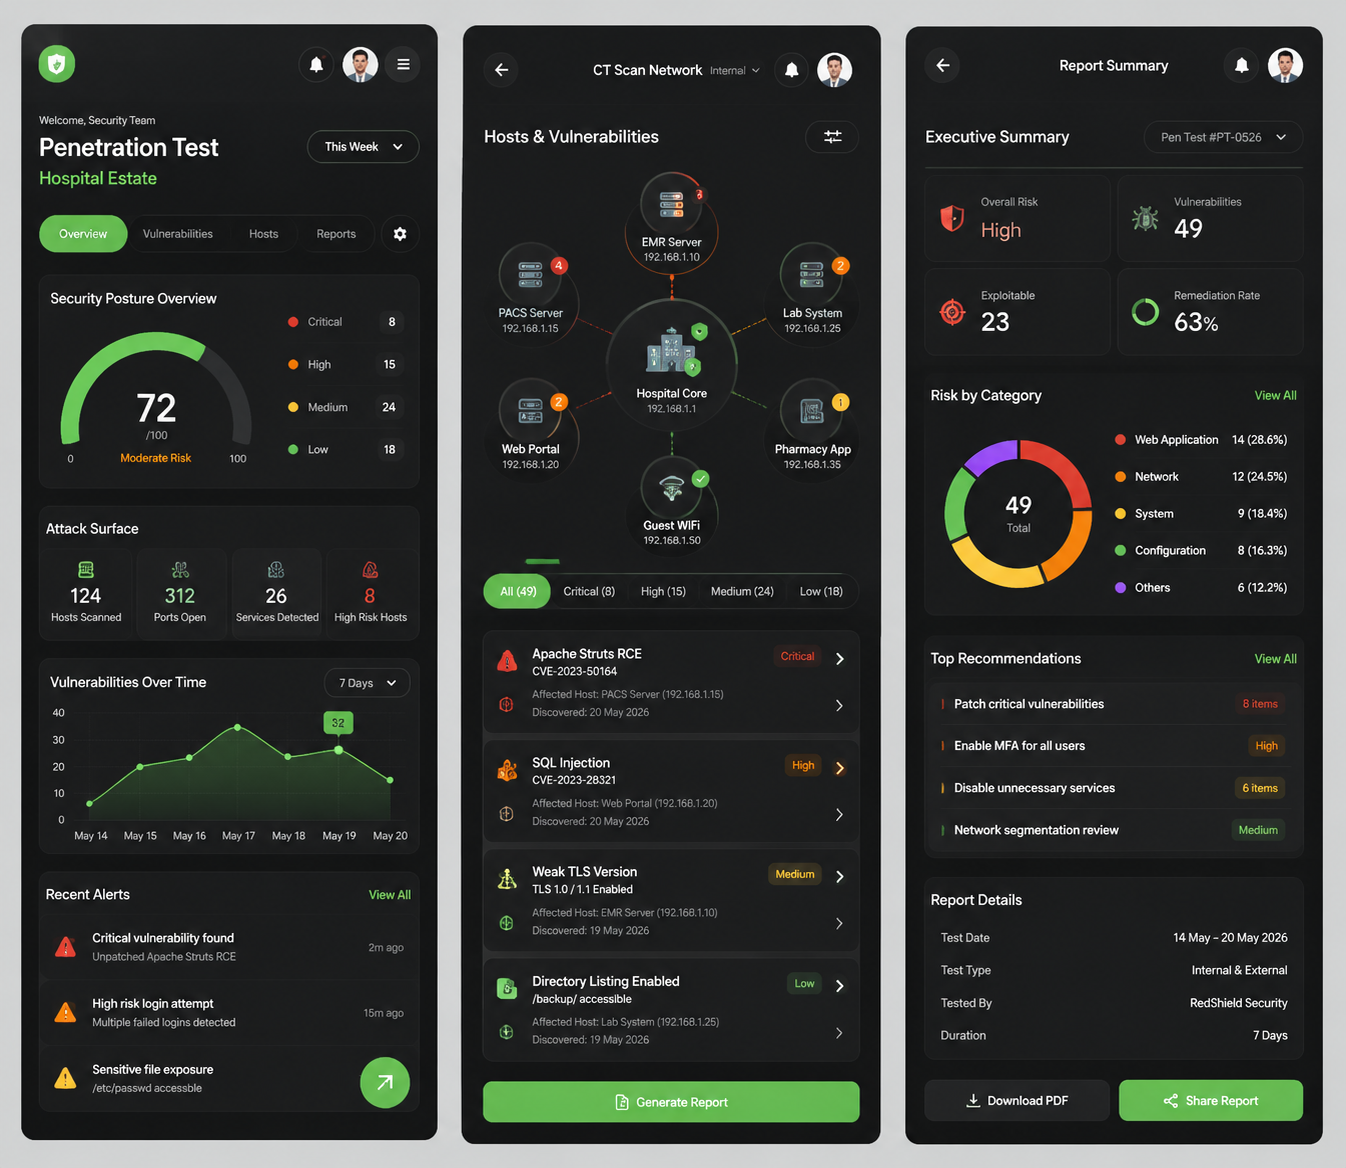
Problem, approach, and the outcome
The client is a UK hospital trust running a sprawling clinical network that had grown for years without an end-to-end security test. Here, a breach can touch patient safety, not just data: connected medical devices share the estate with ordinary IT.
Leadership needed an honest, prioritised picture of real exposure that clinical teams could actually act on.
A sprawling clinical network had grown for years but had never been tested end to end. Its true exposure was genuinely unknown.
A breach here could touch patient safety, not just data: connected medical devices and clinical systems sit on the same estate as ordinary IT. The blast radius of a compromise could reach care itself.
Leadership needed an honest, prioritised picture of real exposure, not a thousand-line scanner dump nobody could action. Usefulness to clinical teams mattered as much as thoroughness.
We assessed the estate for genuinely exploitable paths across identity, network, and medical-device segments, testing how far an attacker could actually move. Testing real movement, not just listing vulnerabilities, is what produces an actionable picture.
Every finding was ranked by real blast radius and, crucially, by patient-safety impact rather than raw severity score. Prioritising by patient safety is what made the results meaningful to a trust.
We validated exploitability rather than reporting theoretical issues, so the trust could trust the list, and the output was a remediation plan sequenced so clinical teams could run it without specialist security staff. The plan was built to be executed.
- 61 exploitable paths surfaced
- Prioritised by patient-safety impact
- Findings validated as exploitable, not theoretical
- A remediation plan the trust could run itself
More Cybersecurity case studies
Red-team engagement against a fintech app
Found and helped close three account-takeover paths before a fintech's launch.
Read the full case study
Cloud penetration test for a retailer
Surfaced 74 exploitable misconfigurations across a retailer's multi-account cloud estate.
Read the full case study
Zero-trust rollout for a government agency
Rolled zero-trust access to 25,000 civil servants without a productivity dip.
Read the full case studyGet a senior architect on the call, first time, every time.
No SDR gauntlet. 30 minutes with an engineer who can scope the problem, name the risks, and give you an honest feasibility call.