
Penetration Test That Found Real Risk
“Their pen-test team surfaced two findings our previous vendor had marked clean. The retest was tight, the report was board-ready.”
Head of SecurityInsurance-tech scale-up, EU
We build, modernise, and run the systems that banks, insurers, and health platforms can't afford to break. Senior-only teams. Outcome-anchored. Audit-ready by design.
Regulated environments we build and evidence within. Frameworks our clients operate under, not accreditations we hold.
We don't sub-contract between disciplines. The architect on your kickoff call is the engineer in your retro. The compliance posture ships with the code.
 BritonOne TechnologyAI & Machine Learning
Agentic systems · RAG · Fine-tuning
Production AI on regulated estates. EU AI Act-aligned. RAG advisors, agentic workflows, fine-tuned domain models, built where the audit trail matters.
We architect, build, and scale regulated workloads across the AWS ecosystem: secure landing zones, data platforms, and analytics engineered to pass audit, not just pass review.
AWS delivery experience
Production-grade AI on regulated estates: RAG, agents, fine-tuning. EU AI Act-aligned by default.
View All Services01 / 07
Where the problem is well-known, the architecture should be too. These are the cross-cutting builds we have delivered inside FCA-, BaFin-, and HIPAA-regulated estates.
Drive innovation with a partner that understands your business goals.
Team up with a senior team that gets the business side. We pair strategic insight with deep technical depth. Our engineers each bring 9+ years of hands-on experience across regulated estates, so you ship polished, audit-ready products while the window of opportunity is wide open.
Every programme is scoped against a business outcome you can measure, agreed before the first sprint and reported against at handover.
Fixed-price programmes or dedicated-team retainers, agreed up front. Change orders are one-page documents you approve before we proceed.
Every engagement is staffed by engineers who have shipped inside FCA-, PRA-, or HIPAA-regulated estates before.
Selected from the last 24 months. Names anonymised under MNDA; the numbers are real.
How we source and verify these figuresCut adviser research time by 47%, zero compliance breaches in 9 months.
Routed 68% of motor claims automatically; £4.2M annual loss-adjuster cost saved.
Lifted suitability-engine completion to 78%, halved drop-off across MiFID II flows.
Caught 92% of card-not-present fraud at 38ms decision latency. £6.1M saved year one.
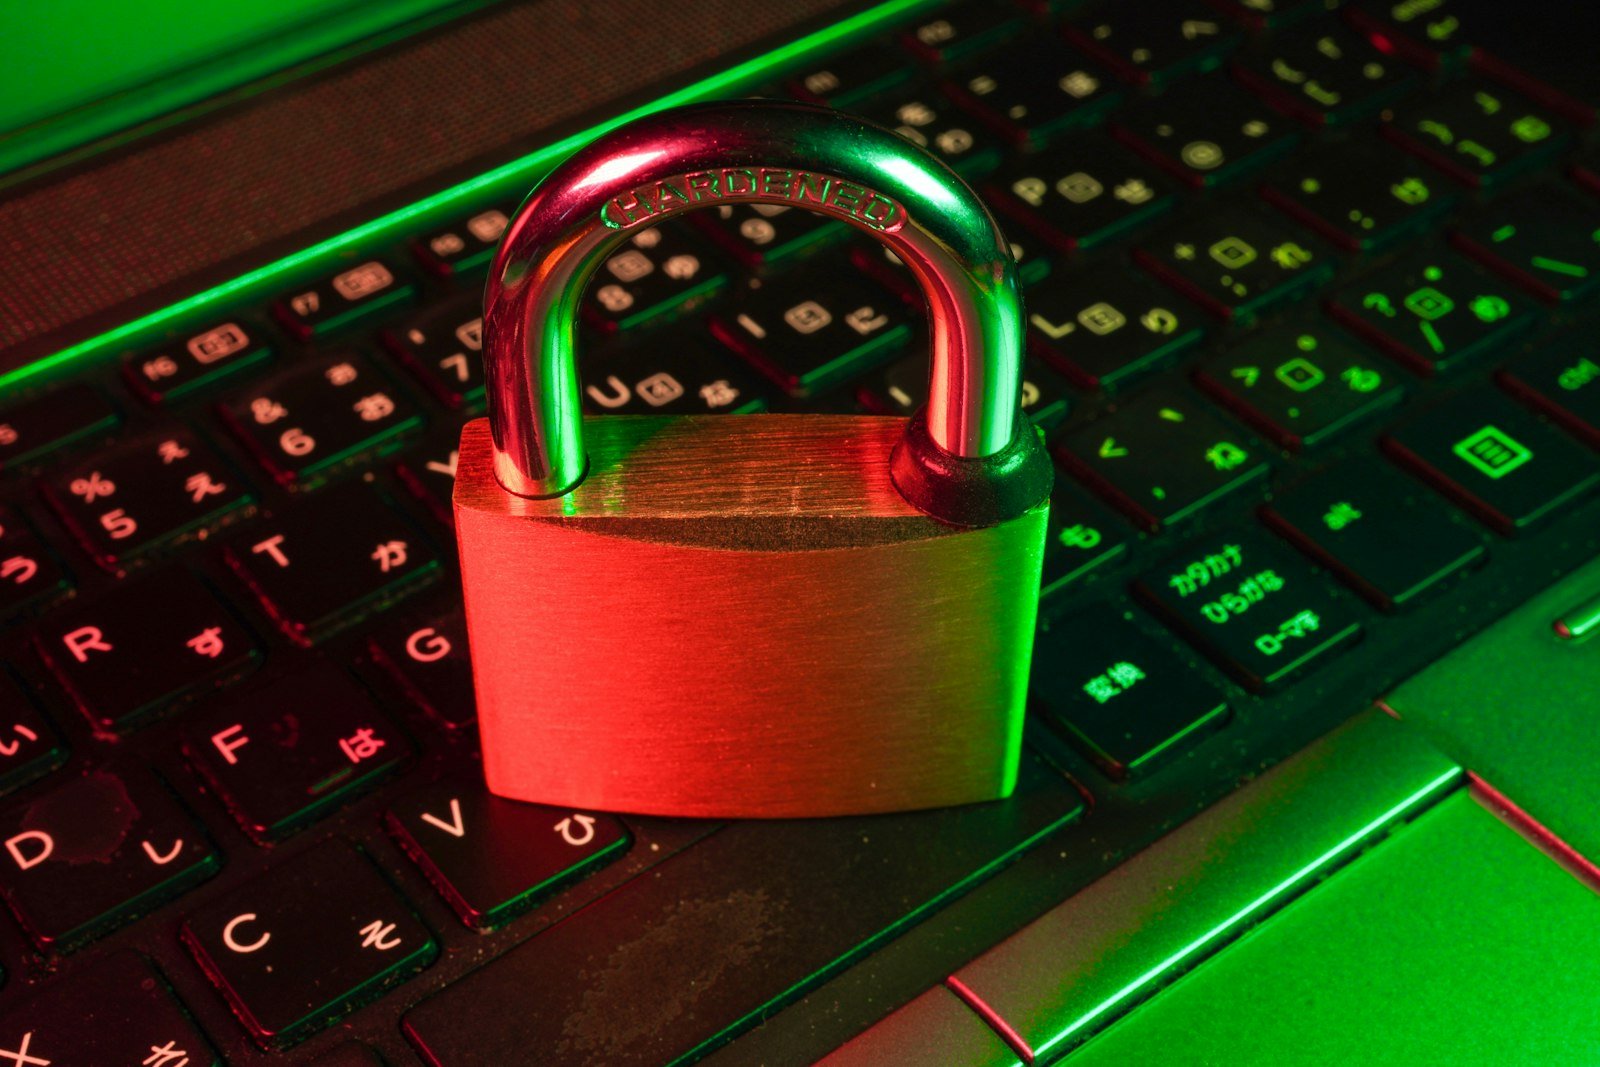
Stood up a board-ready AI governance and model-risk framework for a pharma company in 9 weeks, cleared at first internal audit.
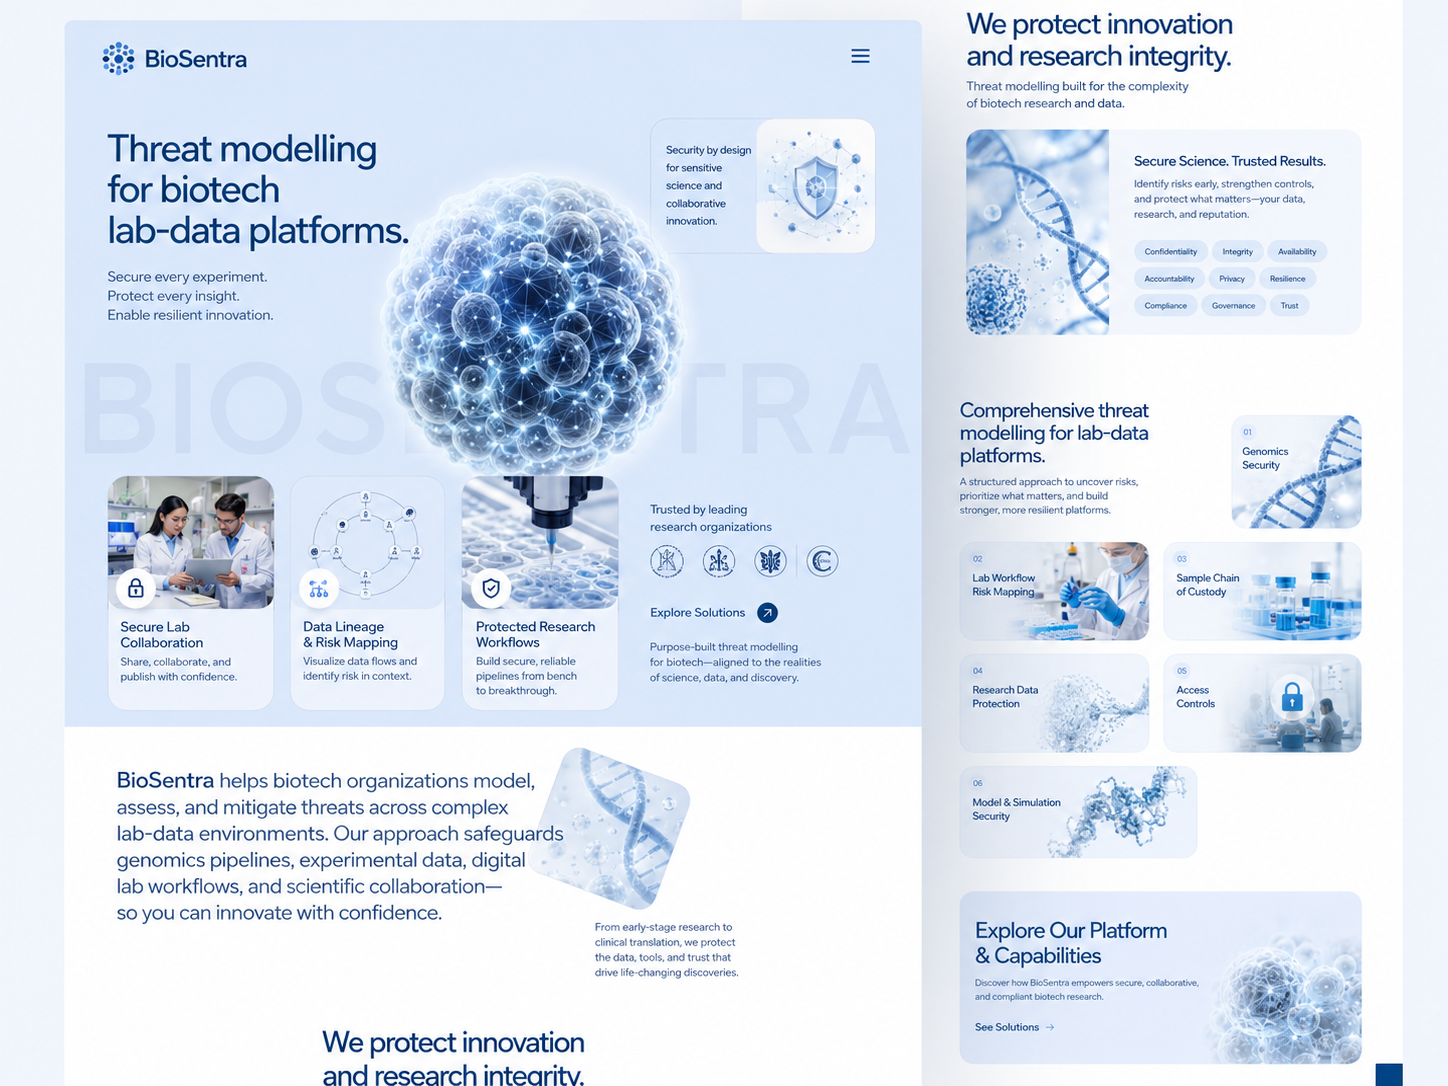
Identified nine design-level risks in a biotech's lab-data platform before build.
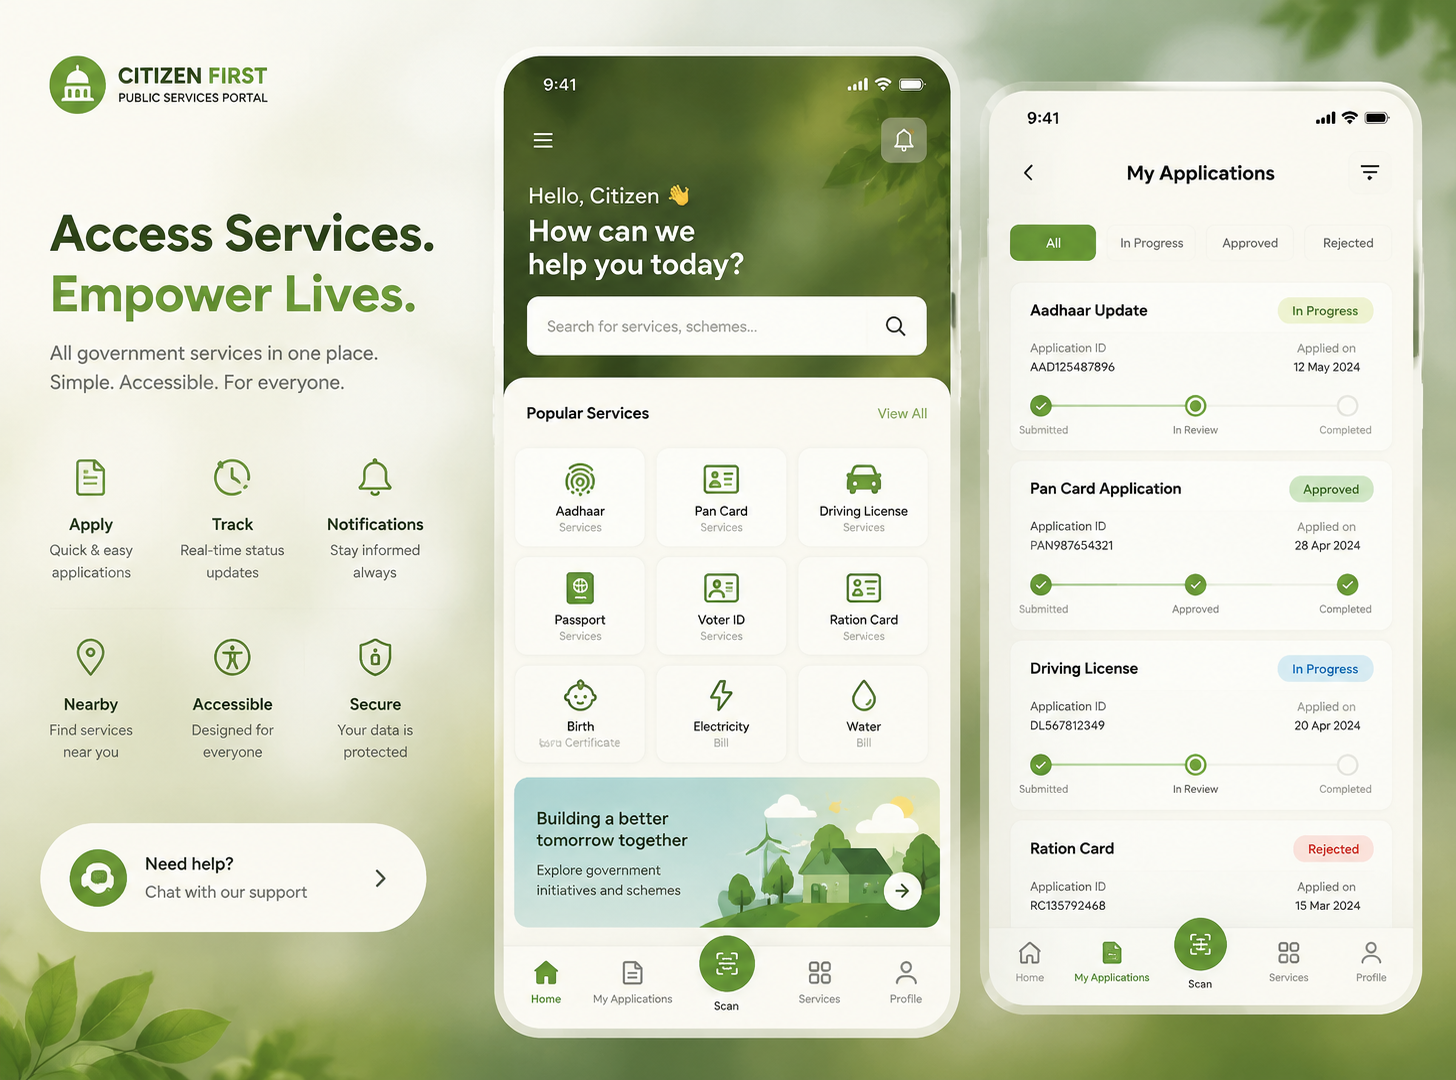
Rebuilt a citizen portal to WCAG 2.2 AA, cleared external audit first pass.
Cut documentation time 41% across 600 clinicians, DSPT-compliant from day one.
Anonymous under MNDA. Each quote is from a senior buyer who owned the engagement end to end across the services catalogue.
How we anonymise client quotes“BritonOne Technology replaced two of our incumbent vendors with one team. Faster sprints, fewer status meetings, more code shipped per week.”
Two ways to engage, both agreed before work starts. No day-rate drip, no discovery invoice, no line items you find out about later.
Scope, milestones, and cost agreed up front. You approve the number before the first sprint starts.
A named senior team at a flat monthly rate. The same engineers stay through to handover.
Any change to scope is a one-page document you approve before we proceed, never an invoice you discover afterwards.
No SDR gauntlet. 30 minutes with an engineer who can scope the problem, name the risks, and give you an honest feasibility call.