
Core systems & payments rails
Ledger design, double-entry accounting, idempotent rails, ISO 20022 messaging, and reconciliation engineering, production-grade from the first commit.
Core modernisation, real-time payments, fraud and AML, and regulatory reporting, built by senior teams who have shipped inside Tier-1 banks and FCA challengers, with the evidence pack alongside the code.
Pick a single workstream or compose them into a multi-quarter programme. Every engagement is architect-led, senior-staffed, and runs to a signed scope your risk committee will accept.
Strangler-fig migration, coexistence patterns, and progressive cutover for Temenos, Mambu, Thought Machine, and Finastra estates, engineered without ledger downtime. From the first event-bridge proof of concept through to the final legacy decommission, a single architect-led pod owns the programme end to end, with rollback rehearsed at every gate and the change-record evidence pack ready for PRA SS2/21 attestation.
Straight-through onboarding with sanctions, PEP, and adverse-media screening, built to PSD2 strong customer authentication and JMLSG good practice, with the audit evidence pack handed over alongside the build.
Faster Payments, SEPA Instant, Pay.UK, ISO 20022 migration, and confirmation-of-payee rails, engineered for 24/7 settlement.
Real-time transaction monitoring with behavioural analytics and ML-scored alert triage.
COREP, FINREP, MIFIR, EMIR, and AnaCredit, lineage tracked end-to-end, attested to source.
Audit-ready GenAI over your policy stack, cleared through model risk on first review.
Ledger design, double-entry accounting, idempotent rails, ISO 20022 messaging, and reconciliation engineering, production-grade from the first commit.
SS1/23 model risk, EU AI Act, Basel III/IV capital impact, JMLSG, FCA SYSC, and EBA GL, translated into design constraints before the build plan is drawn.
AWS, Azure, and GCP landing zones for regulated estates, datacentre exits, ledger workloads, and tier-1 batch jobs cut over without breaching change-control windows.
Important Business Service mapping, impact tolerances, severe-but-plausible scenarios, and third-party concentration, operational resilience built in, not bolted on.
Banking programmes only stand up under regulator scrutiny when the engineering underneath is unimpeachable. These are the disciplines our delivery teams bring to every engagement.
Selected programmes across retail, challenger, wealth, investment, commercial, and mutual lenders, anonymised where required, specific on the outcome.
Production GenAI grounded on six years of policy, procedure, and product docs, cleared second-line model risk on first review with the eval harness and risk pack shipped alongside the build. 100% first-pass clearance.
Mobile app, KYC, core integration, and payments rails delivered to a non-negotiable regulatory milestone, a single architect-led pod from discovery through to live operations under SLO, with paid acceptance at every gate. 9 months end-to-end.
Rebuilt the HNW onboarding journey from broker submission through to a funded custody account. Sanctions and PEP screening, source-of-wealth attestation, MiFID II suitability, and intermediary entitlements consolidated behind a single orchestration layer that replaced eight legacy hand-offs with a deterministic state machine. Cleared MiFID II suitability on the first audit and cut the median journey from 11 days to 38 hours across direct and intermediated channels, without expanding the ops team. 38 hrs median onboarding.
Lineage-tracked pipeline across 14 trading systems, rebuilt to clear ESMA recon thresholds without manual exception queues, source-attested at every hop, with second-line evidence packs handed over alongside the cutover. 98.7% recon match rate.
ML-scored monitoring at 38ms latency. £6.1M saved.
Legacy mortgage estate lifted to AWS. 0 unplanned outages.
Production integrations against every major core estate buyers ask us about: coexistence layers, event-stream choreography, strangler-fig cutovers, and bespoke modules where the platform stops.
Tier-1 deployments of T24 and Transact with custom modules, event-stream coexistence, and Infinity digital channel integration.
Capabilities we deliver
Every engagement walks the same path, sized to your problem, but with the same verification gates baked in.
Two-week paid sprint. Architect-led. Output: regulator map, costed roadmap, signed scope.
Pod composition, sequenced milestones, change-control governance, and risk register.
Reference architecture, threat model, design system, and acceptance criteria locked.
Weekly demos, trunk-based, CI/CD from day one. Code reviewed against spec at every gate.
Unit, integration, e2e, security, performance, and accessibility, automated and gated.
Blue-green or canary, observability live before launch, rollback rehearsed.
Managed services or hypercare hand-off. Defined SLOs, named on-call, monthly reviews.
Success stories
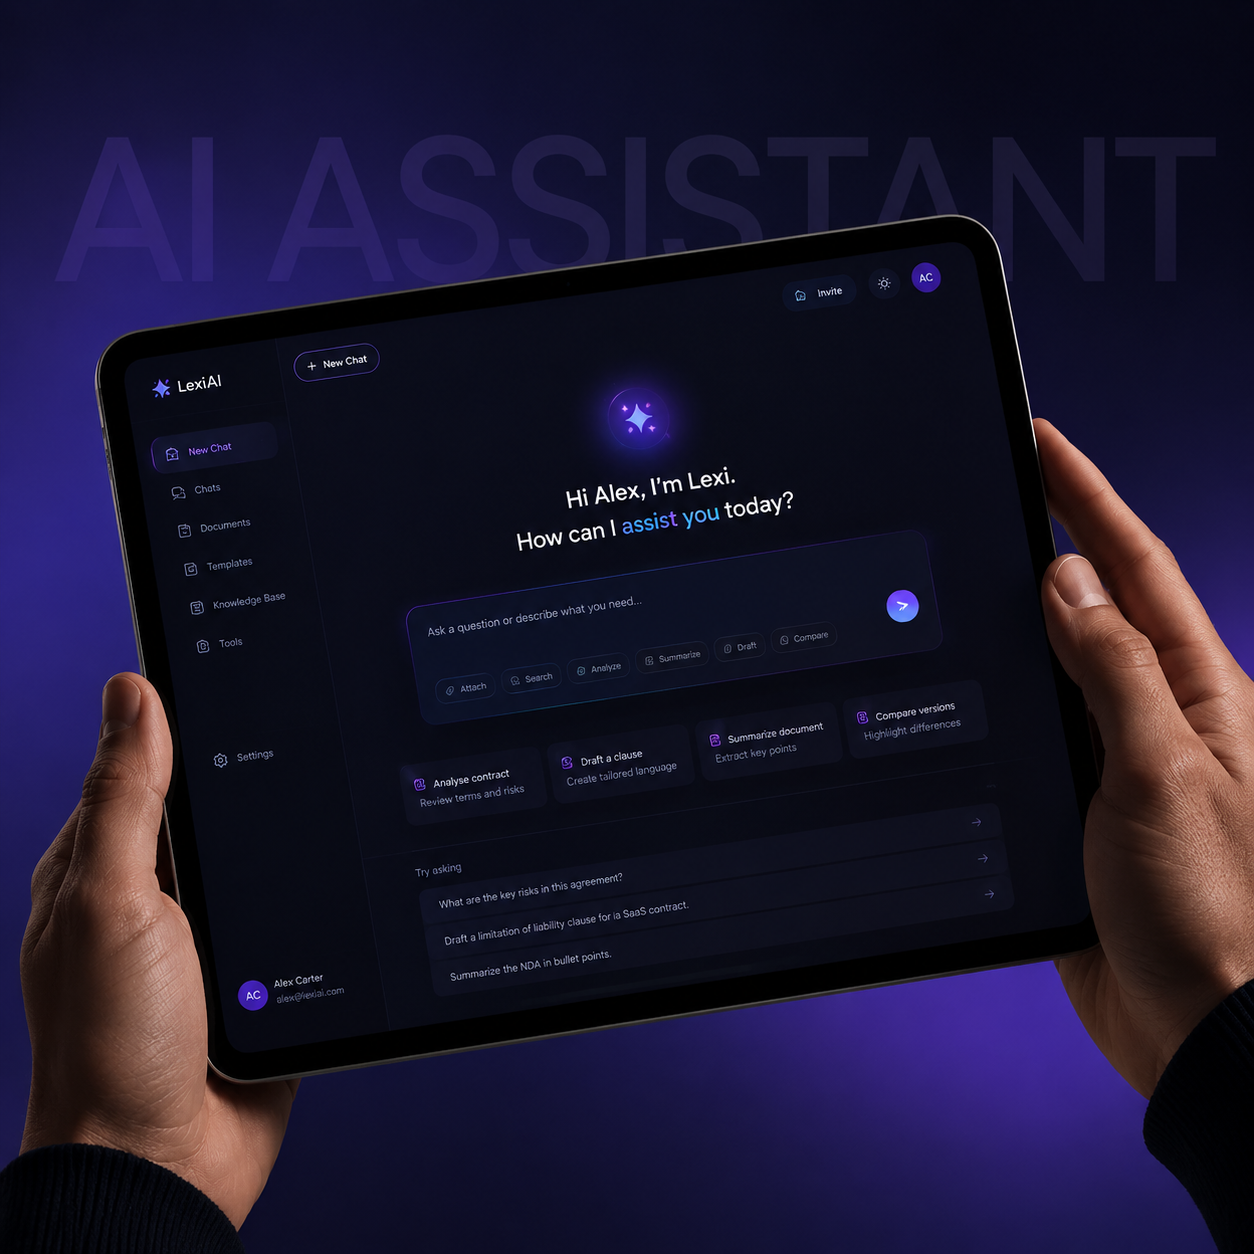
Cut average handle time 44% across 2,600 agents, with answers grounded in approved policy only.
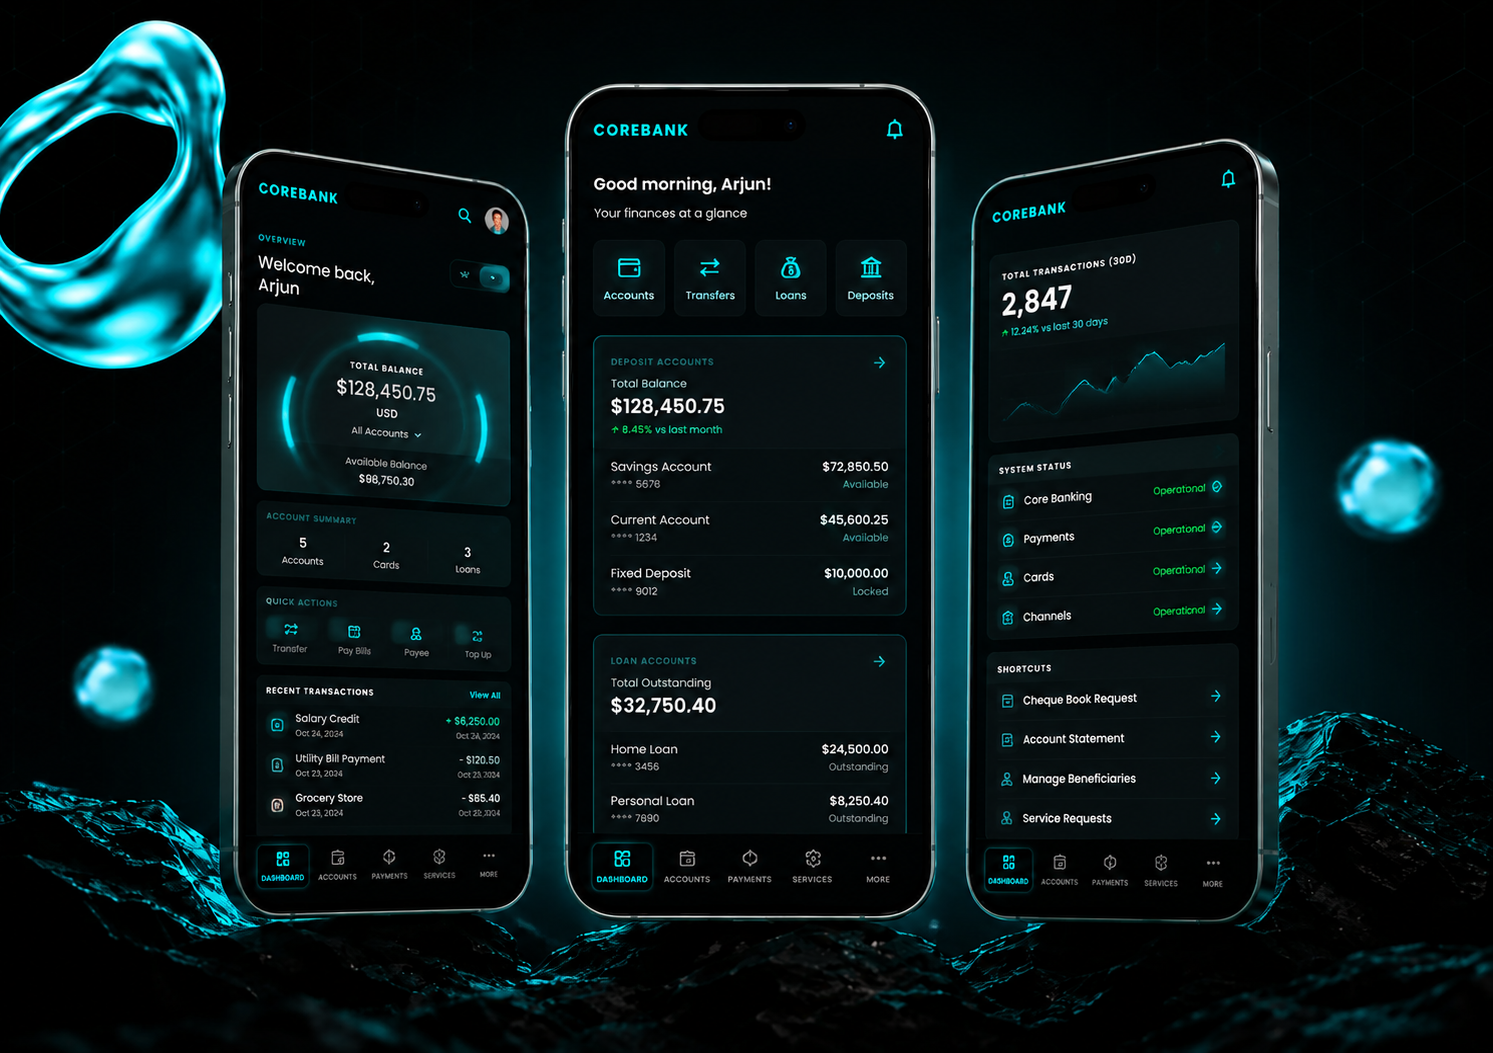
Ledger, accounts, and payment rails delivered to an FCA launch milestone in 9 months.
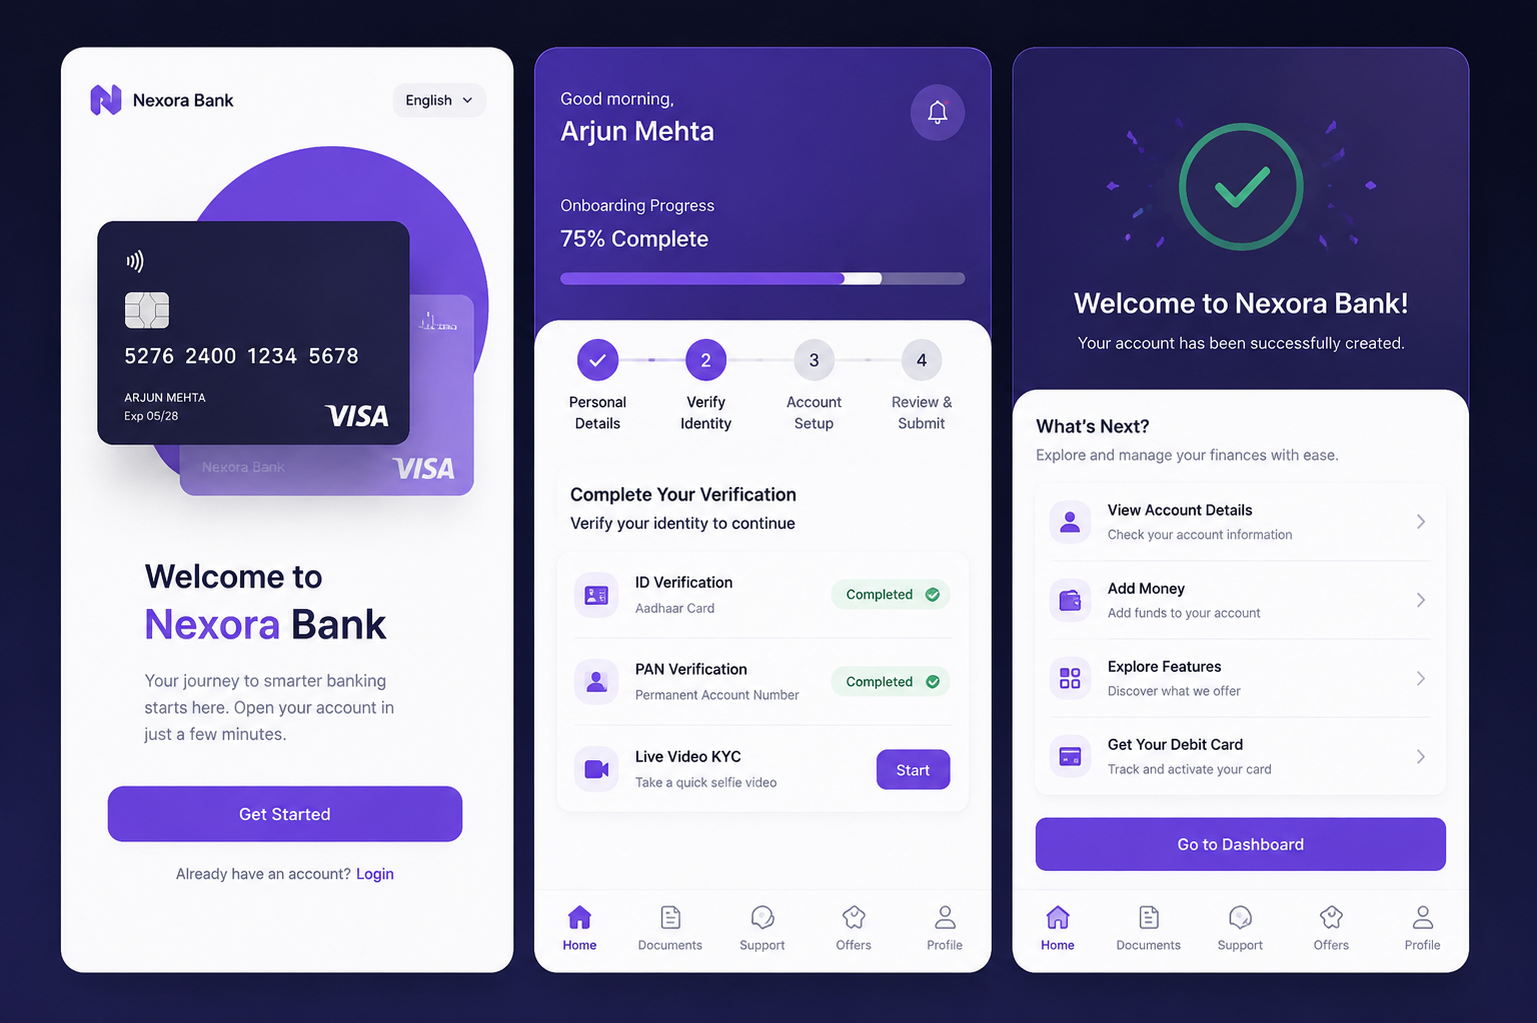
Straight-through KYC onboarding raised completion to 78%.
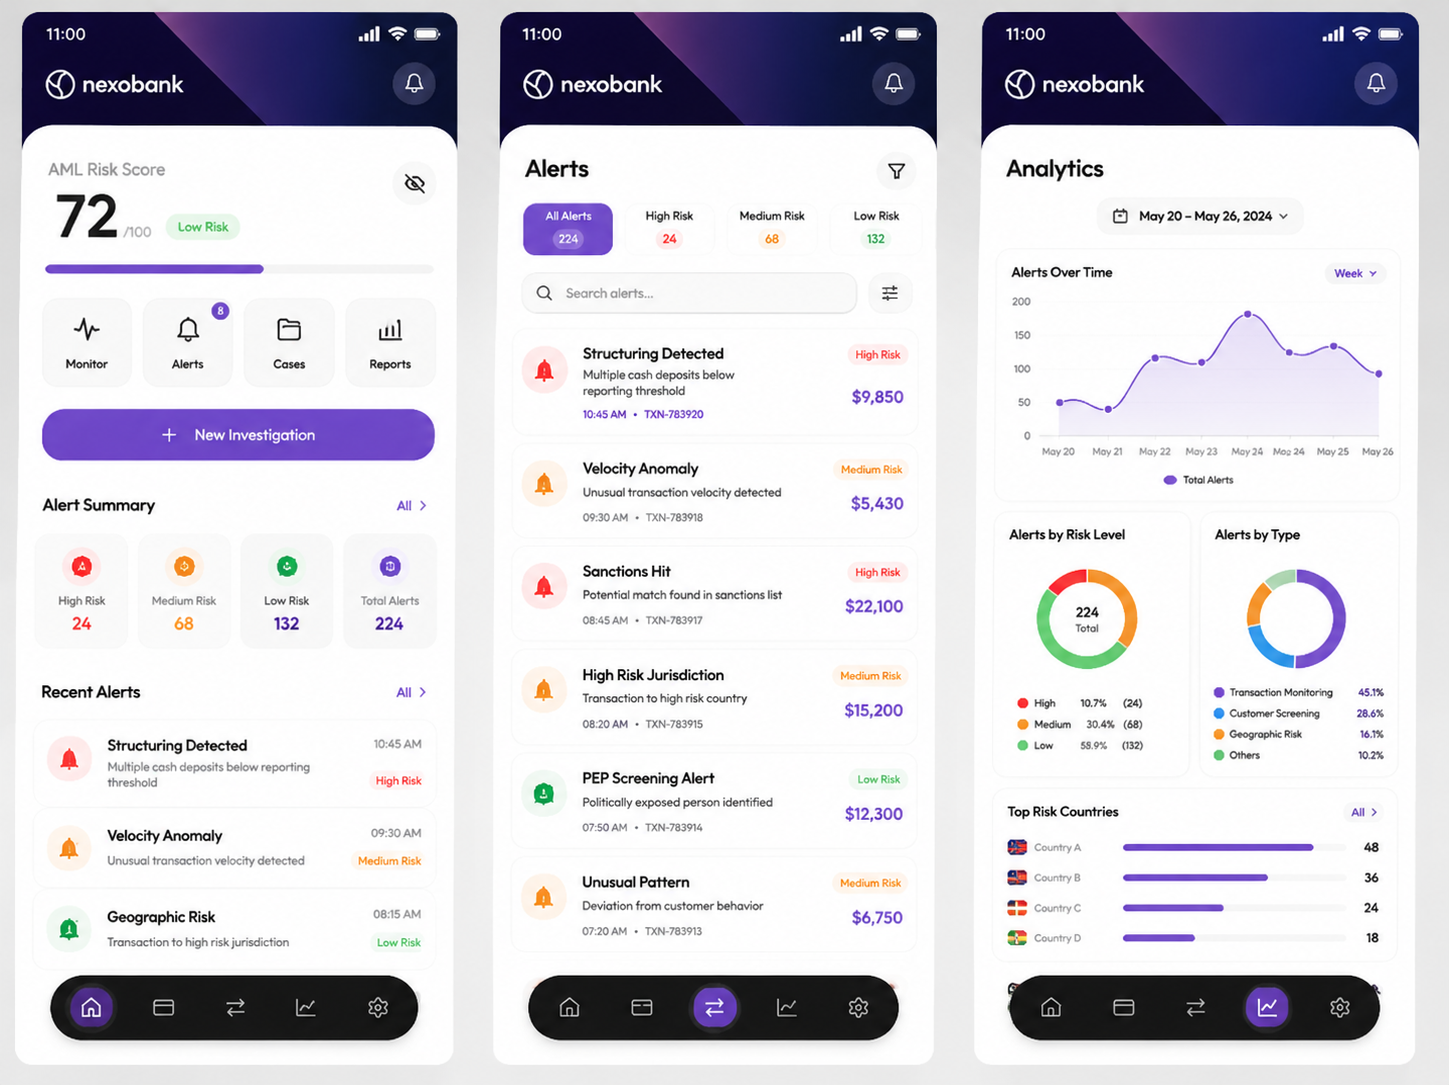
Cut false-positive AML alerts 44% at a bank while catching more genuine risk.
Delivered 10,000+ automated assertions across balance, transfer, and payment APIs, catching every schema and auth regression before release for a digital bank.
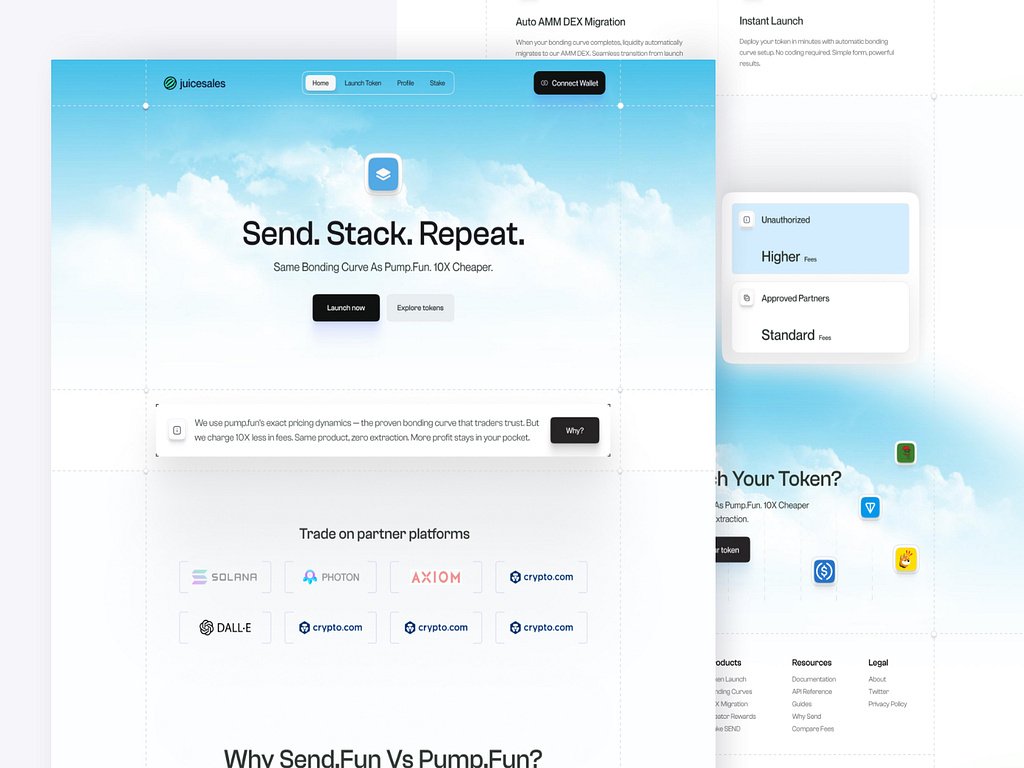
Shipped a bonding-curve launchpad with automated AMM migration and wallet-connected minting that cut issuance fees roughly tenfold for a digital-asset bank.
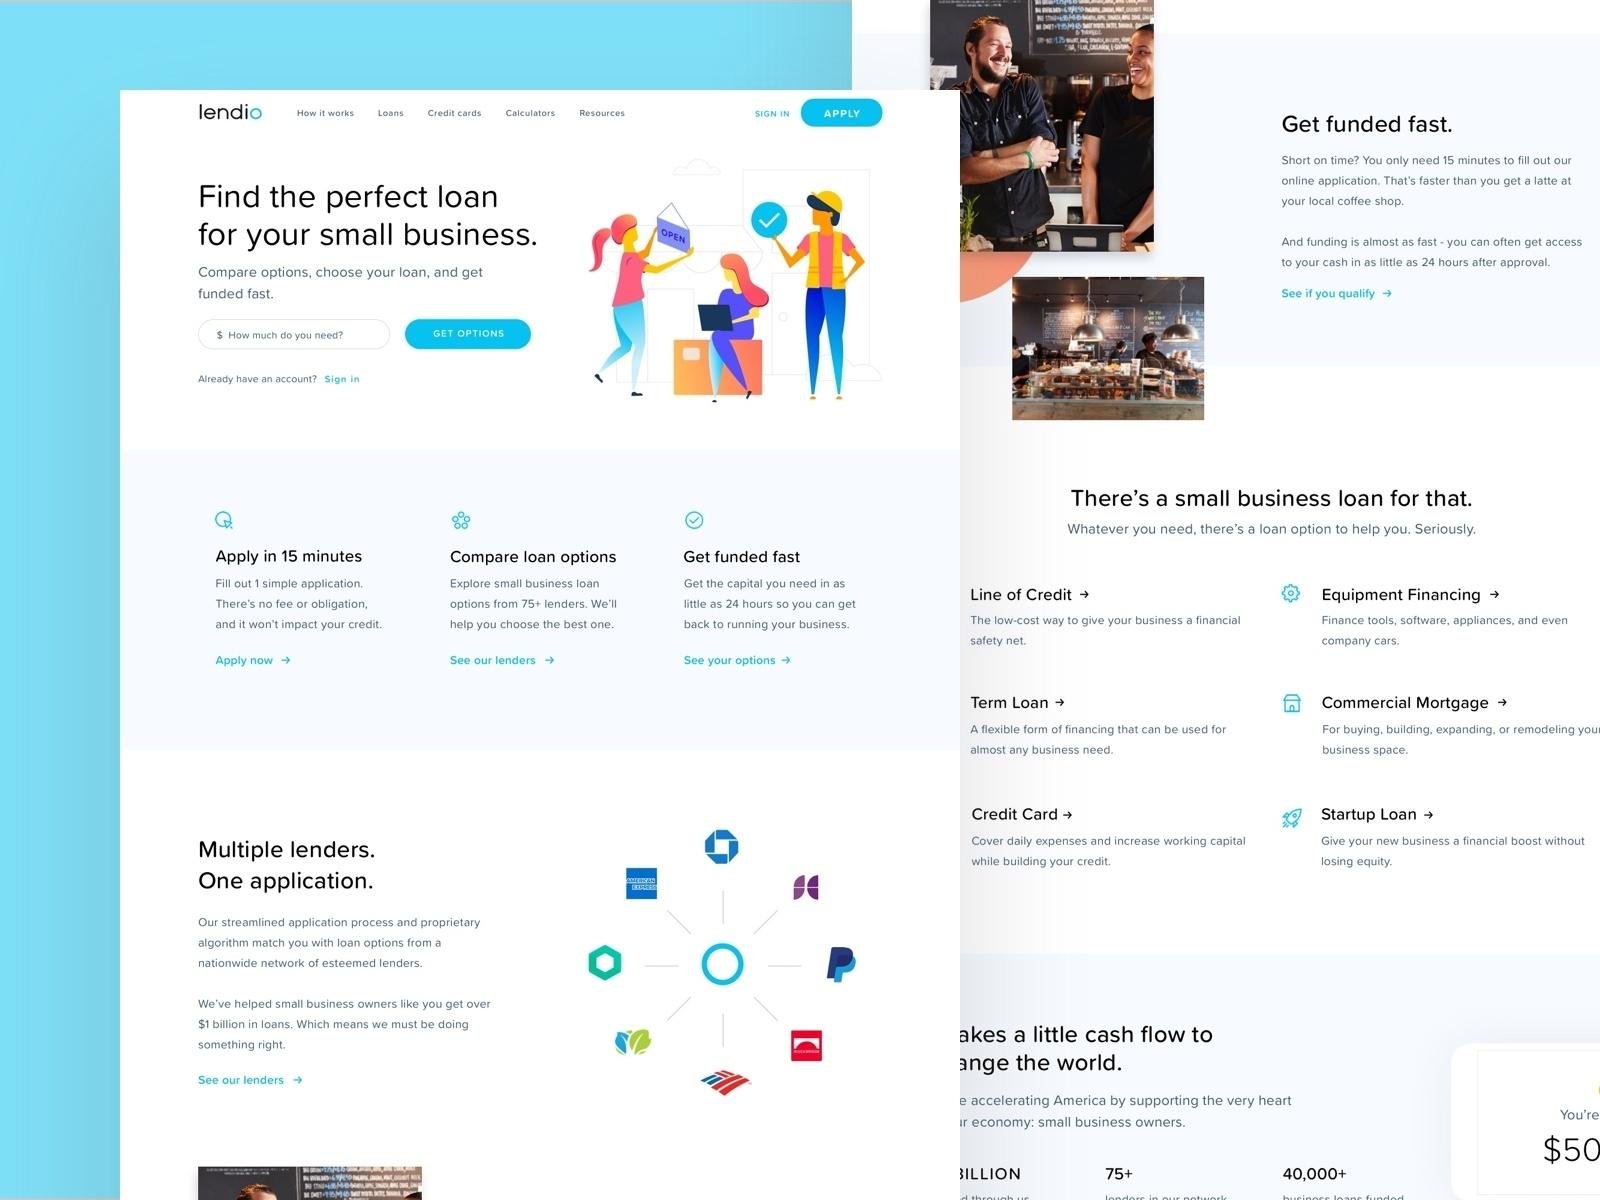
Matched borrower demand to non-custodial money markets through a single application, routing more than a billion dollars in loans across lines of credit and term loans.
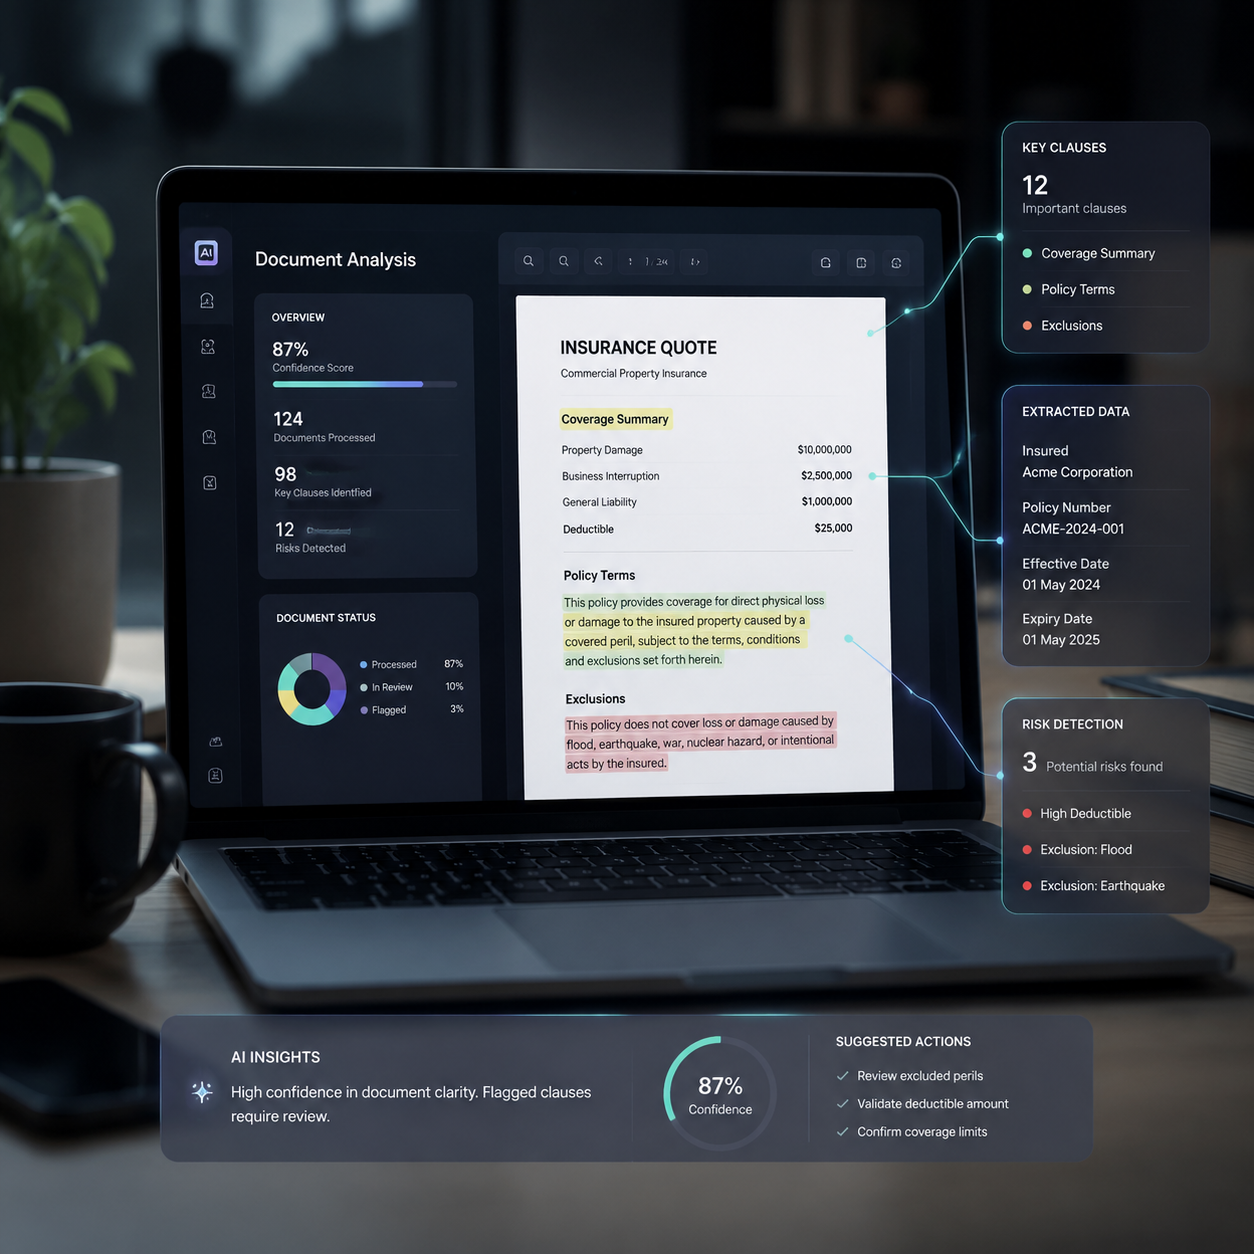
Drafted first-pass quotes from submission packs 3.1x faster, every clause cited back to the wording it came from.
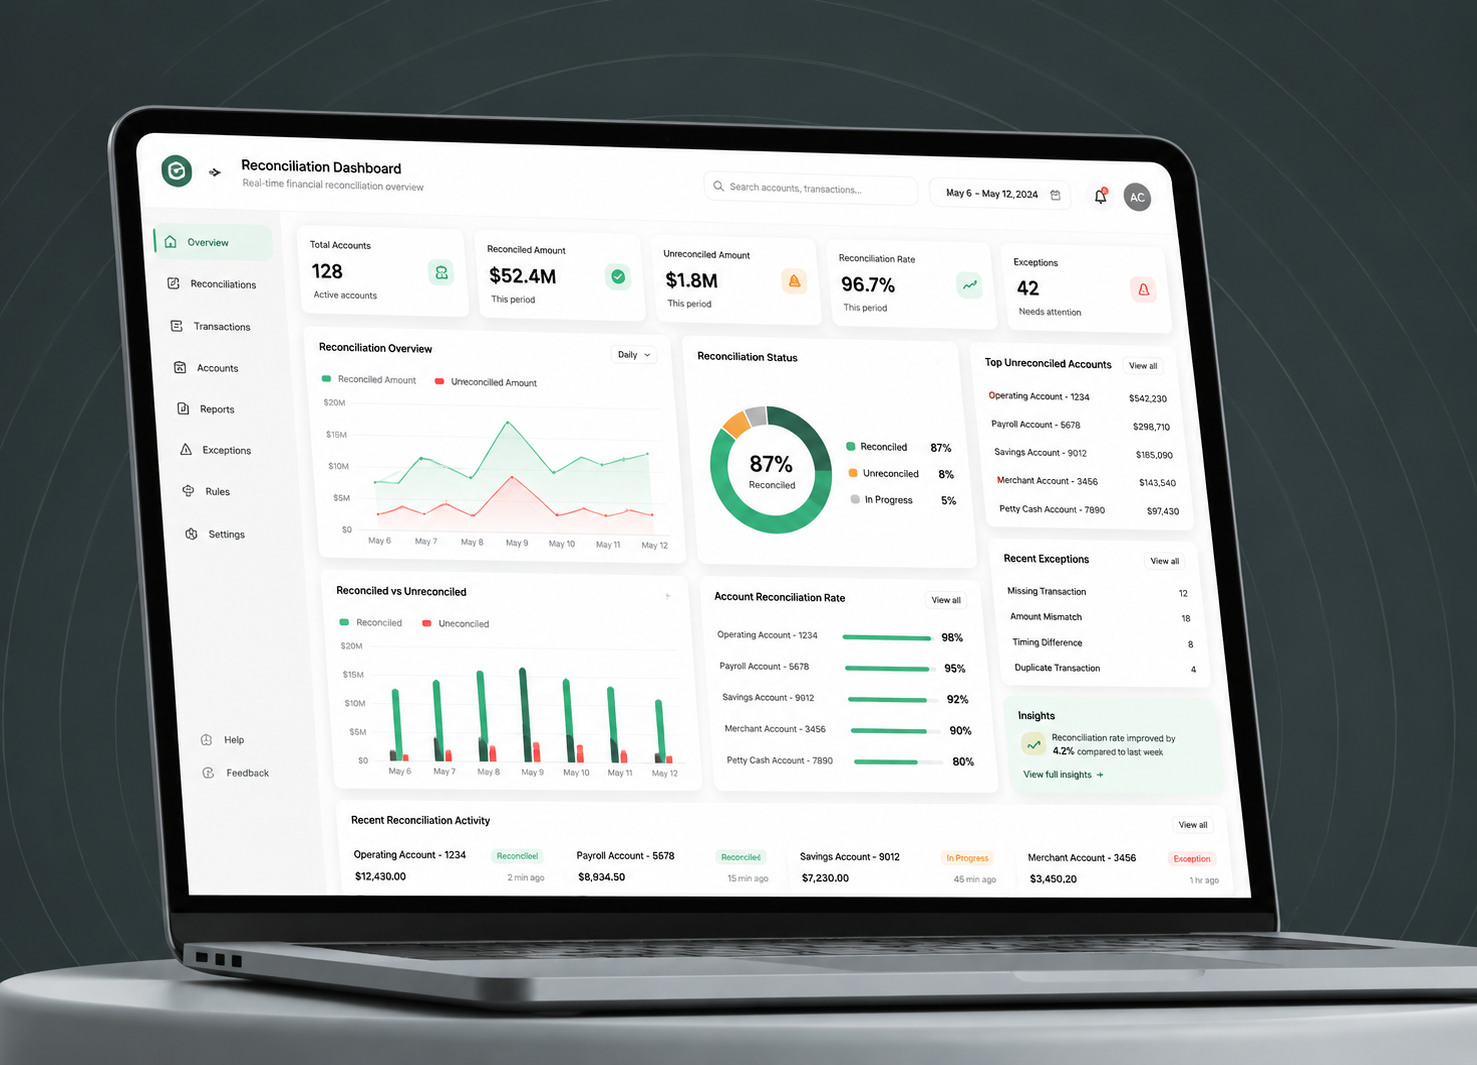
Resolved 89% of reconciliation breaks without a human, every action logged for audit.
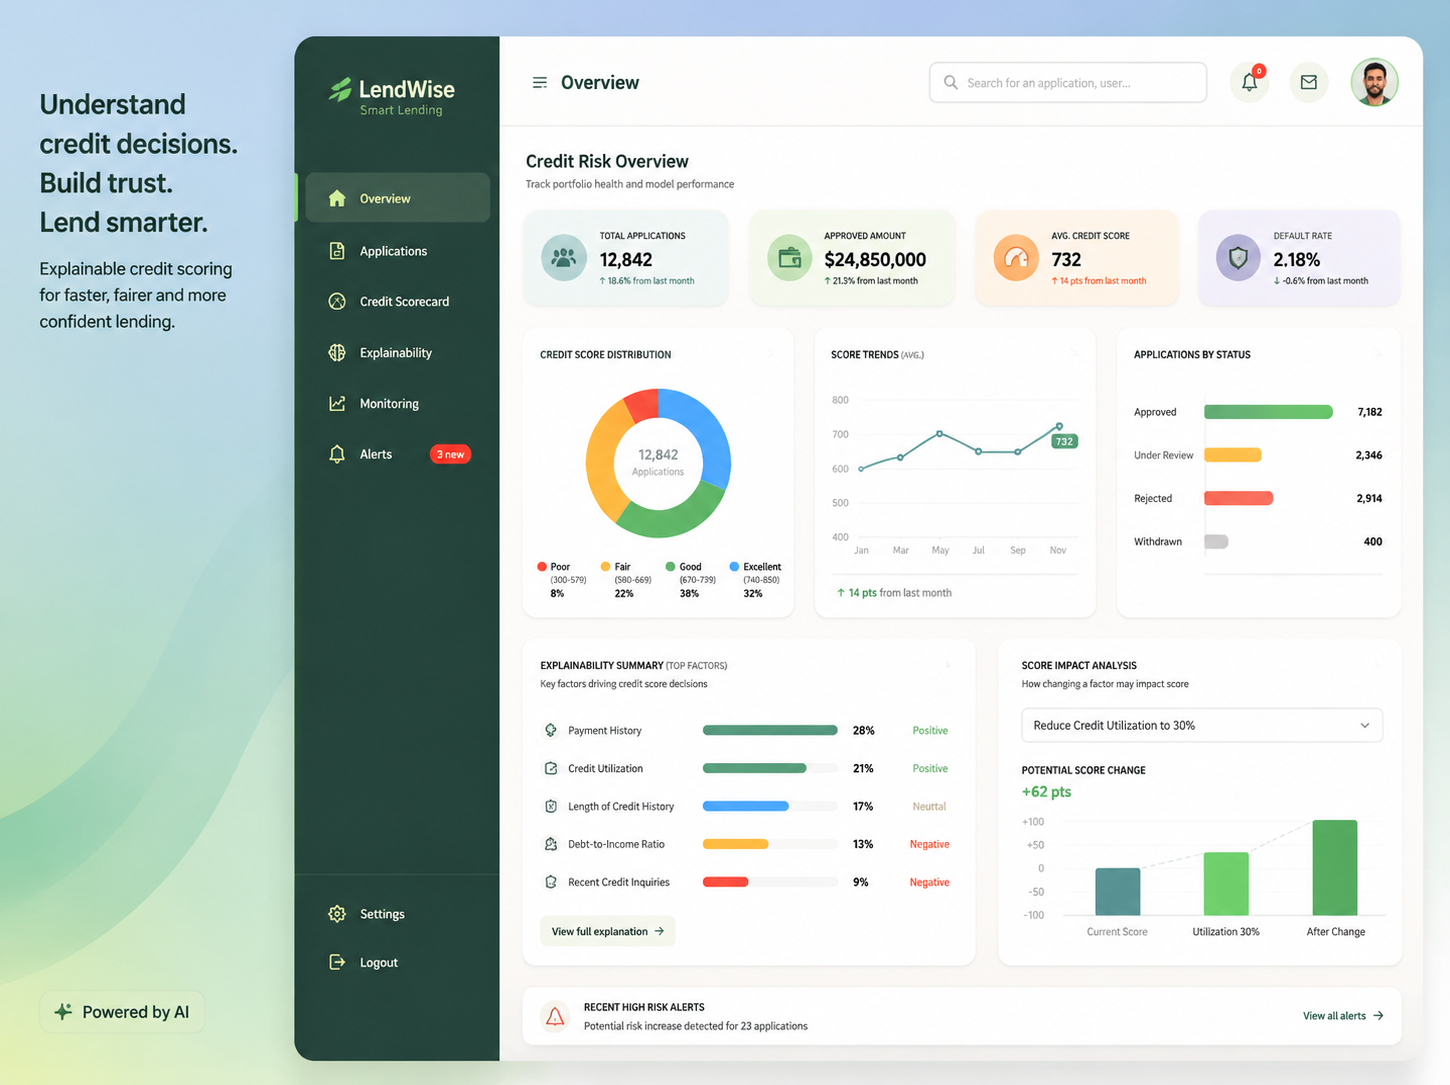
Lifted approval rates 31% at constant loss, every decision reason-coded for the FCA.
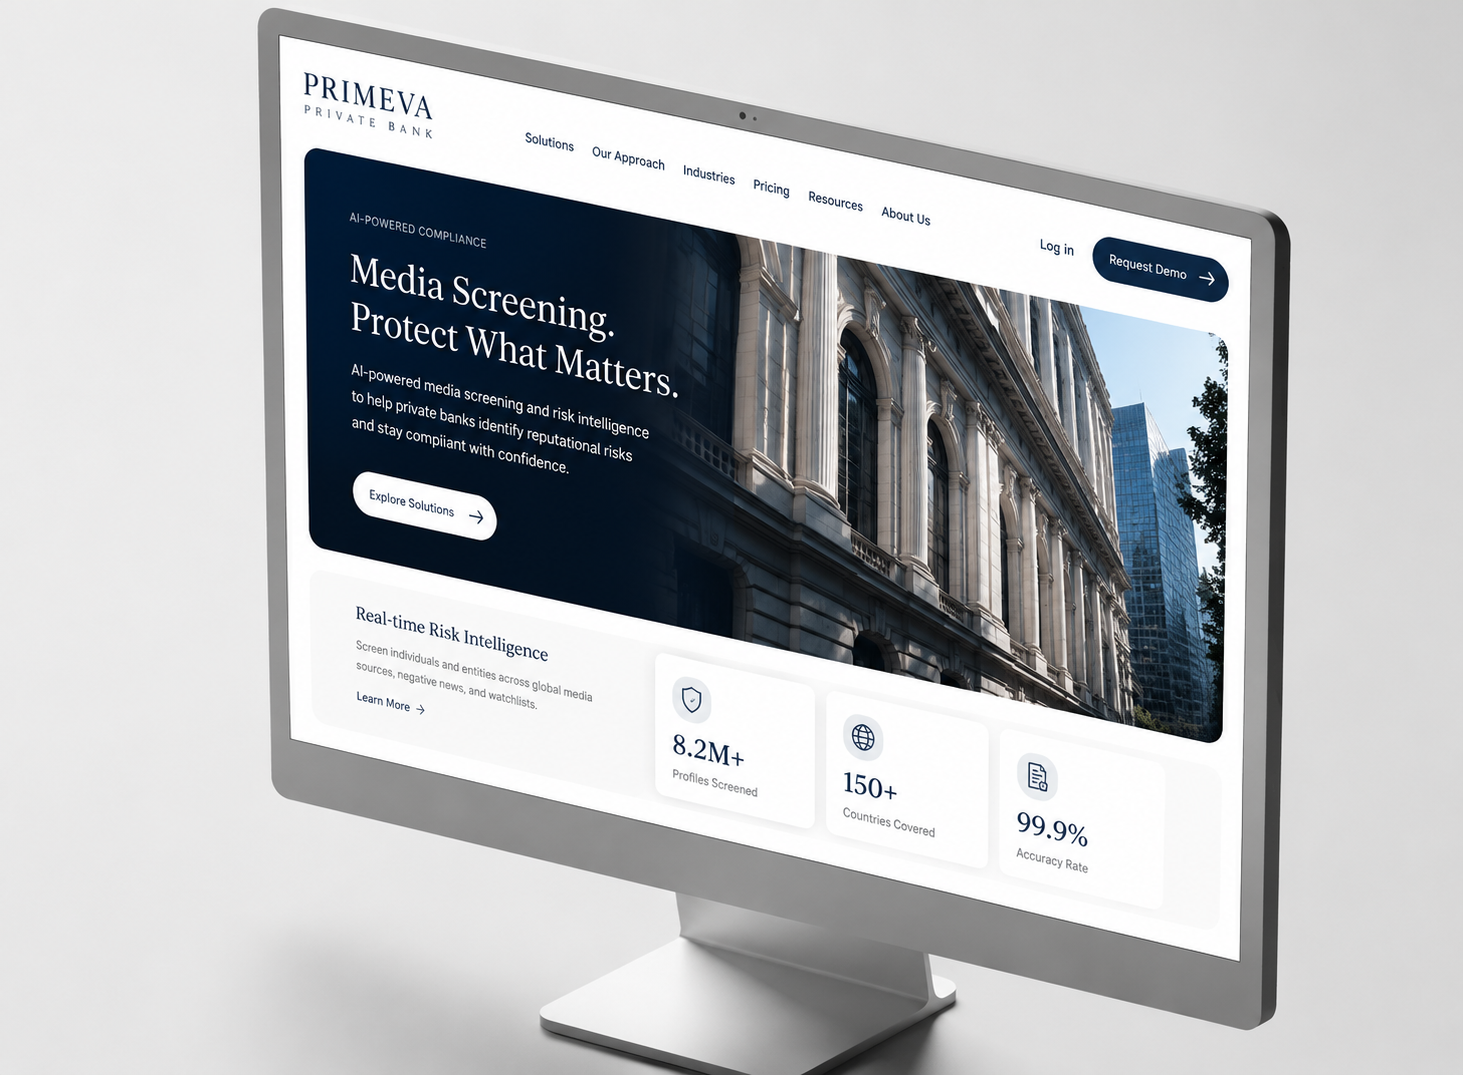
Screened 12x more names at a lower false-positive rate, each hit evidenced.
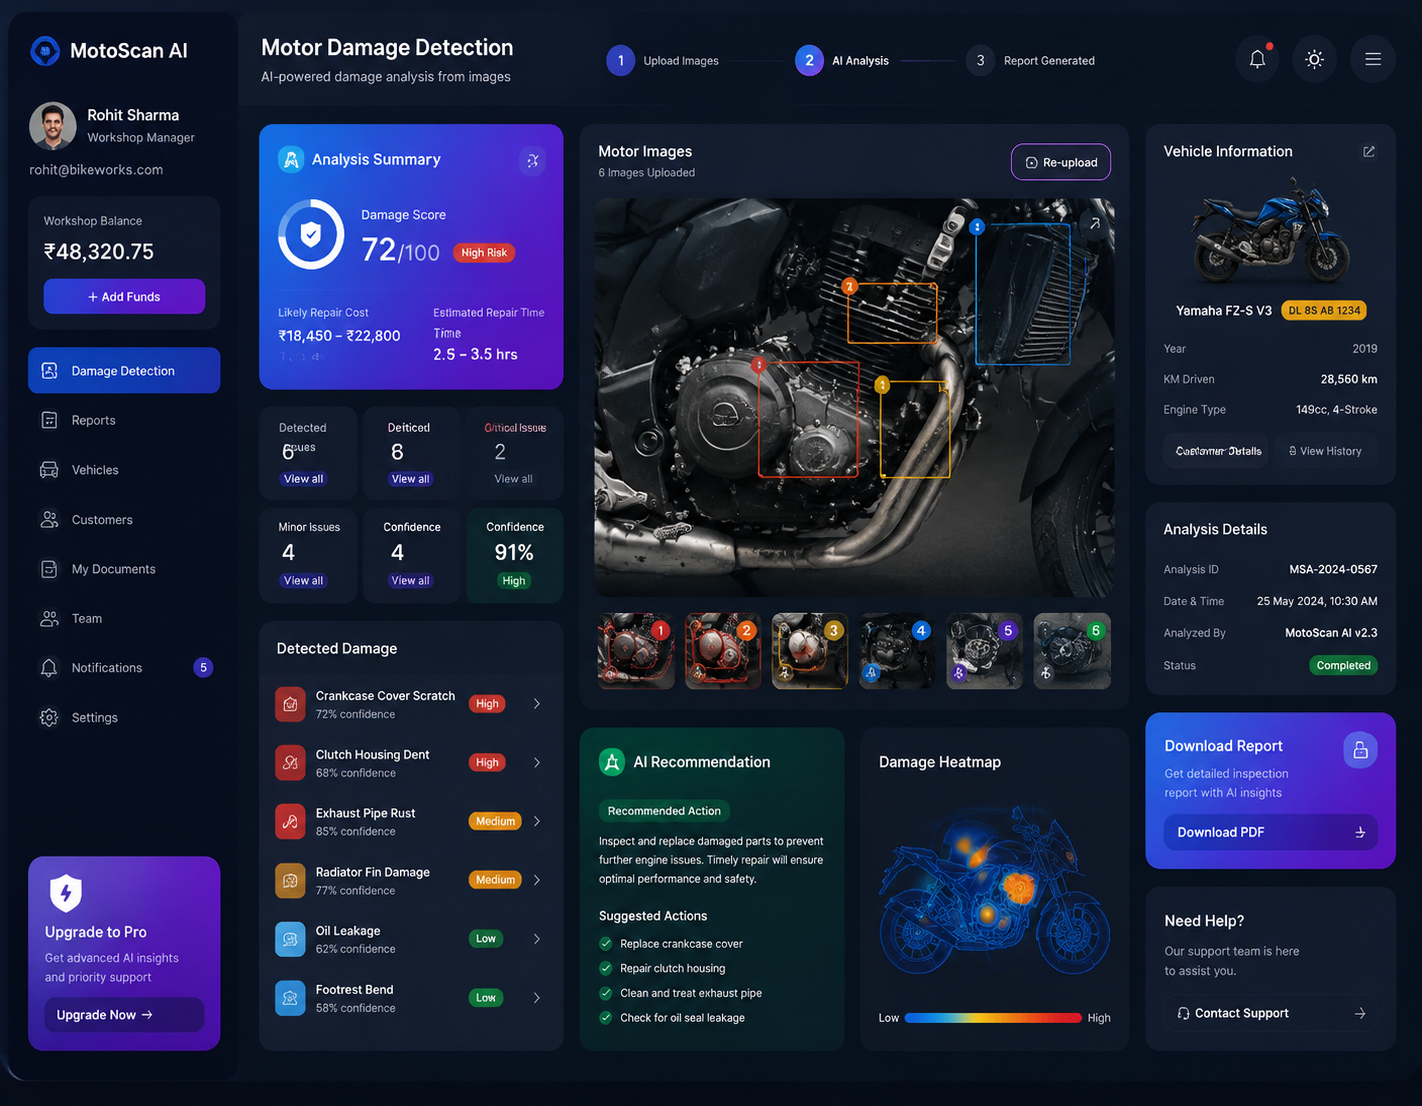
Settled 47% of motor claims from images alone, with fraud flags surfaced inline.
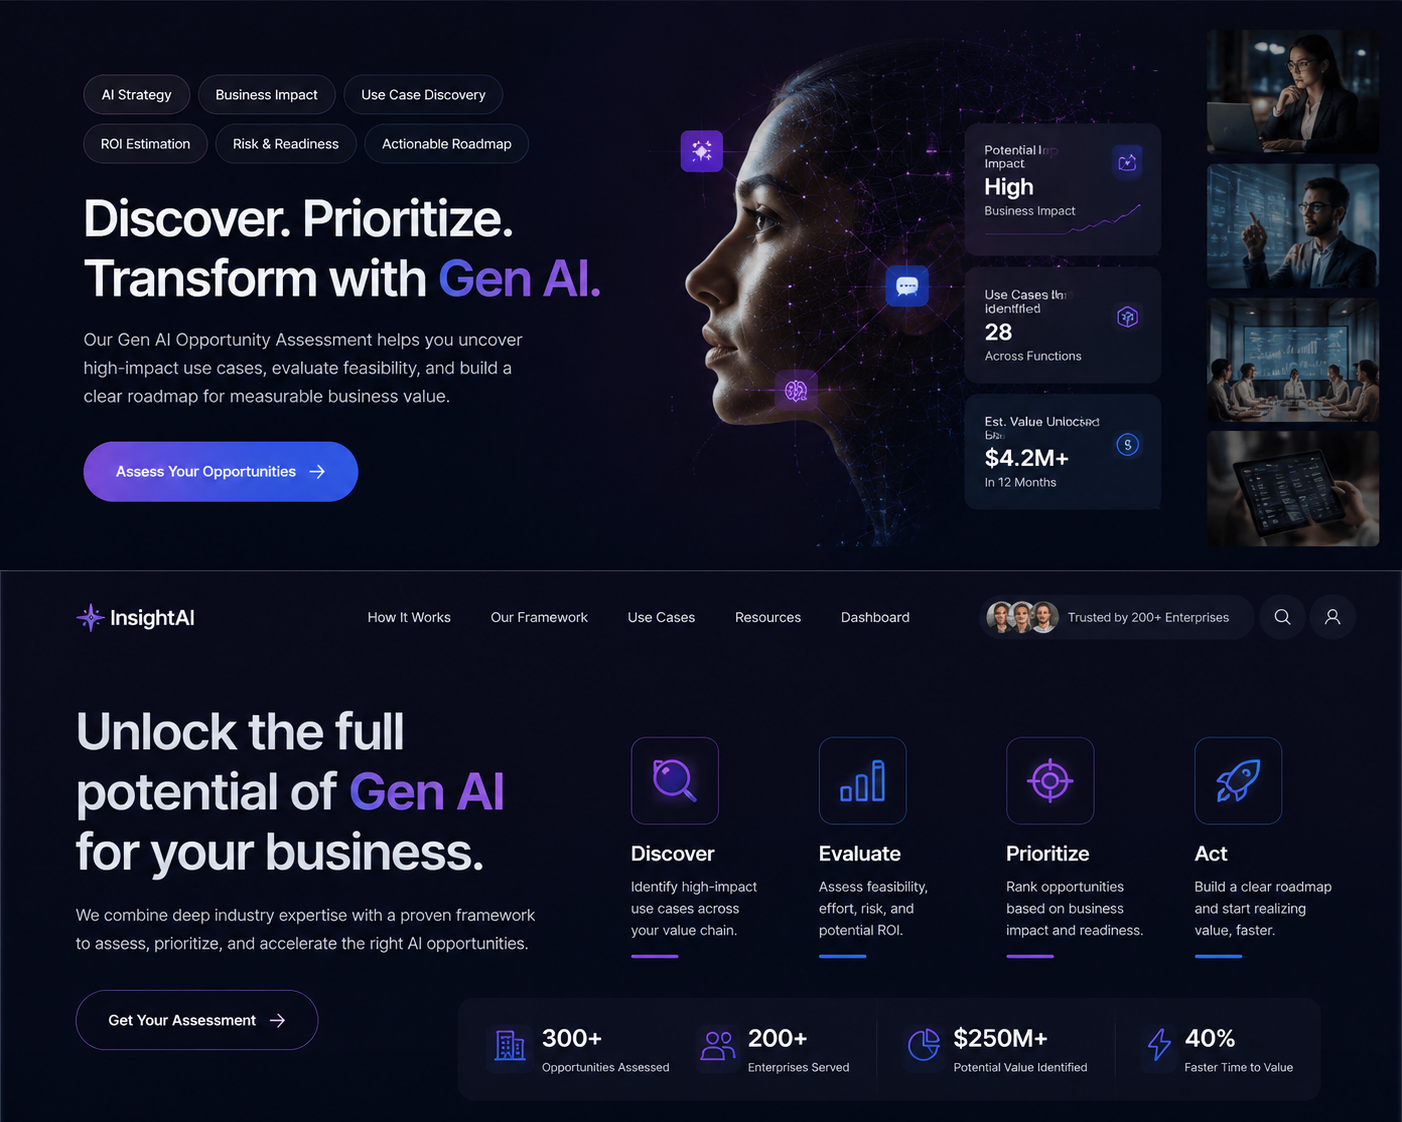
Mapped a £14M annual benefit pipeline across 40 use cases, sequenced by risk.
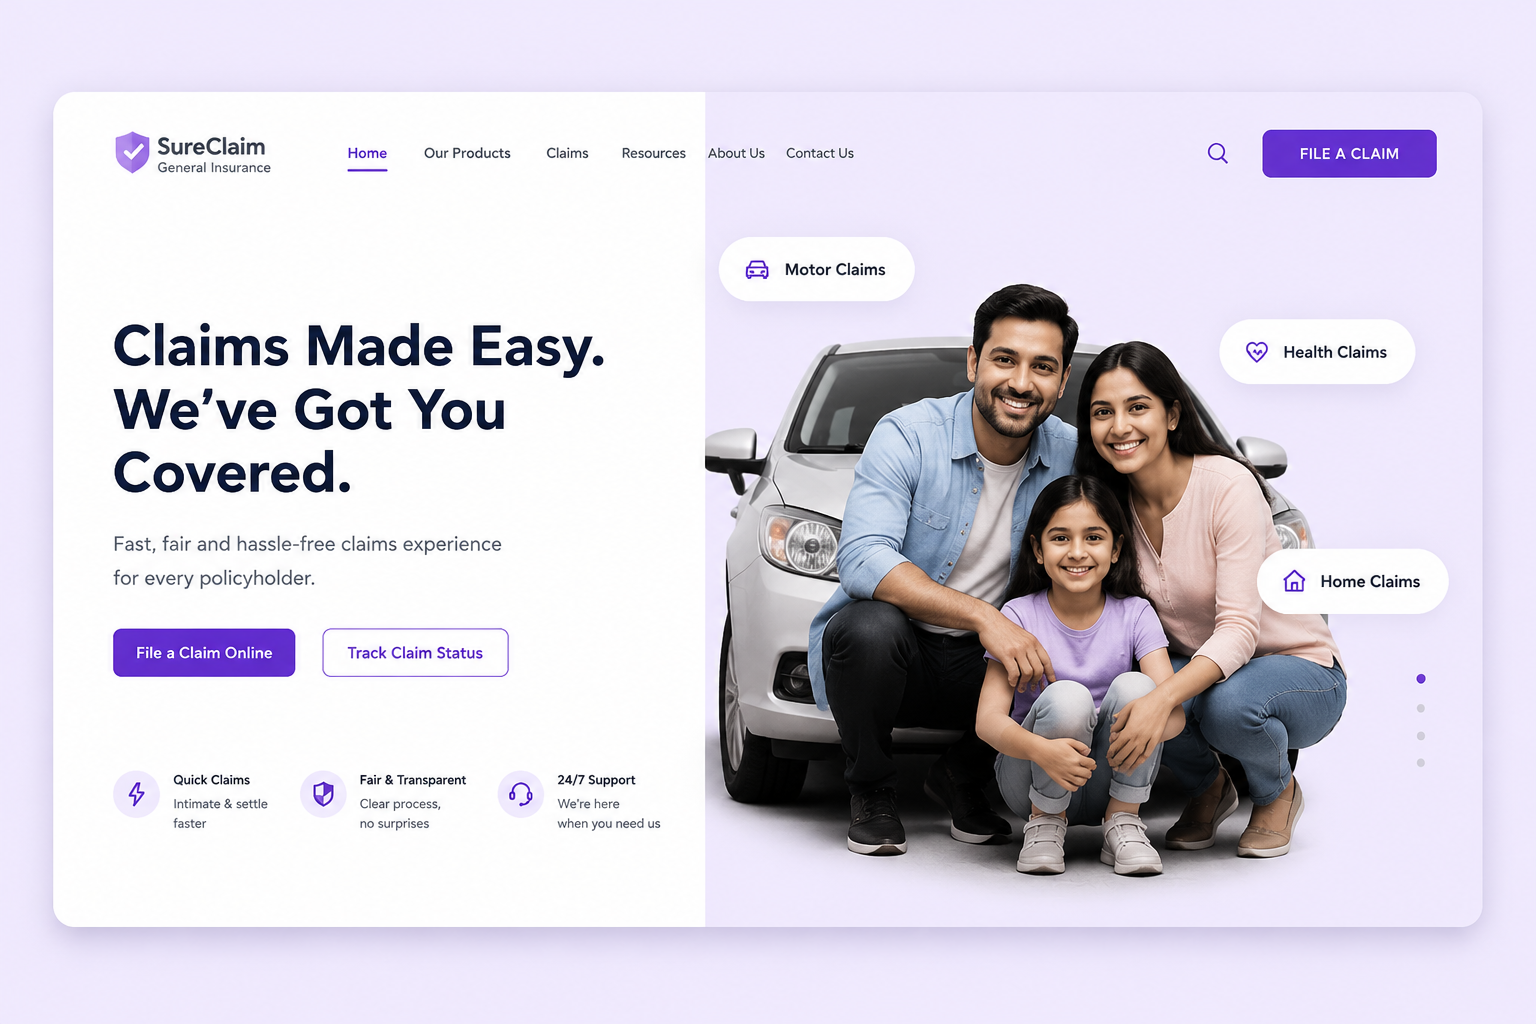
Replaced a 15-year-old claims system, tripling throughput per handler.
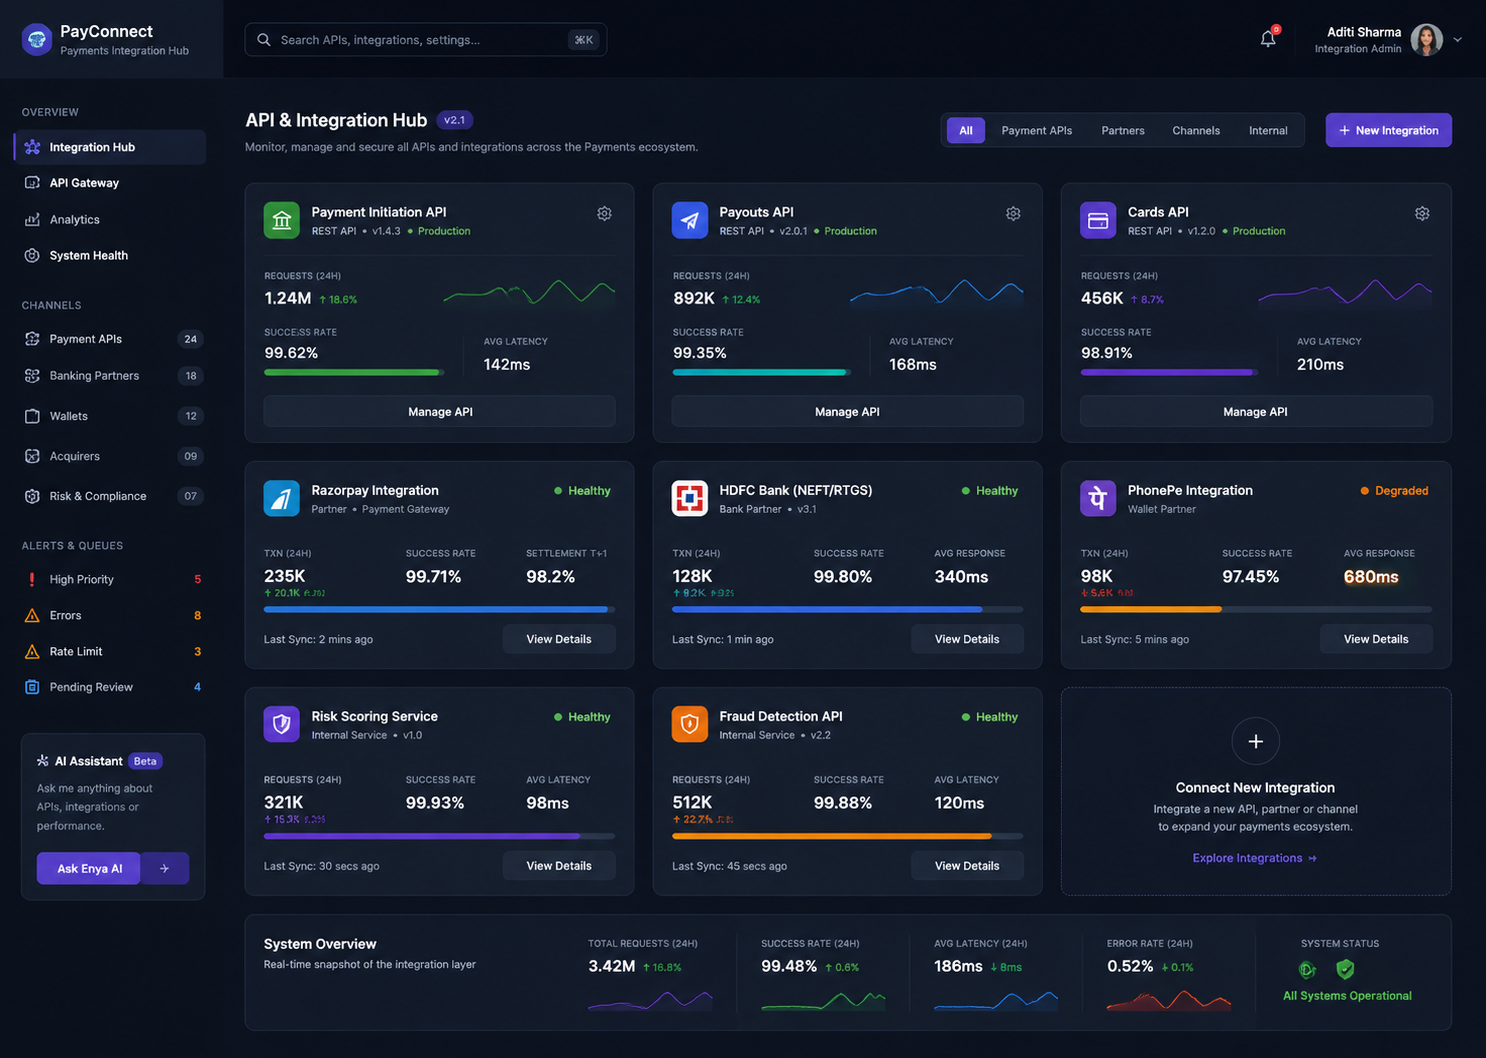
Unified 120+ partner integrations behind one governed API gateway.
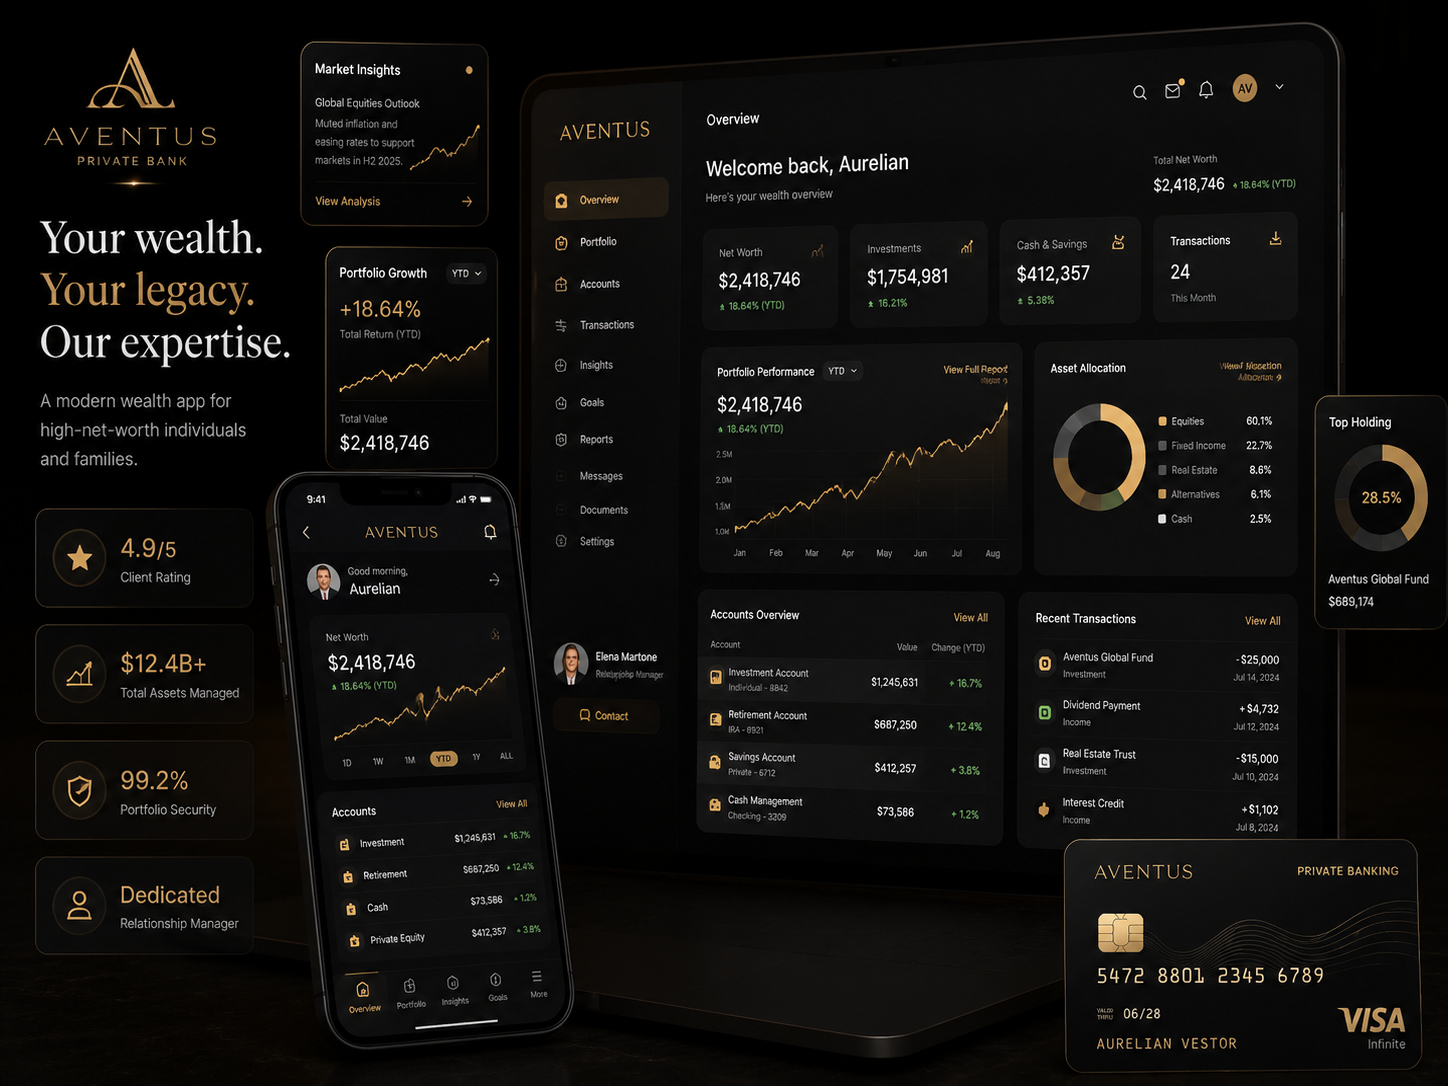
MiFID-compliant investing app doubled monthly active clients.
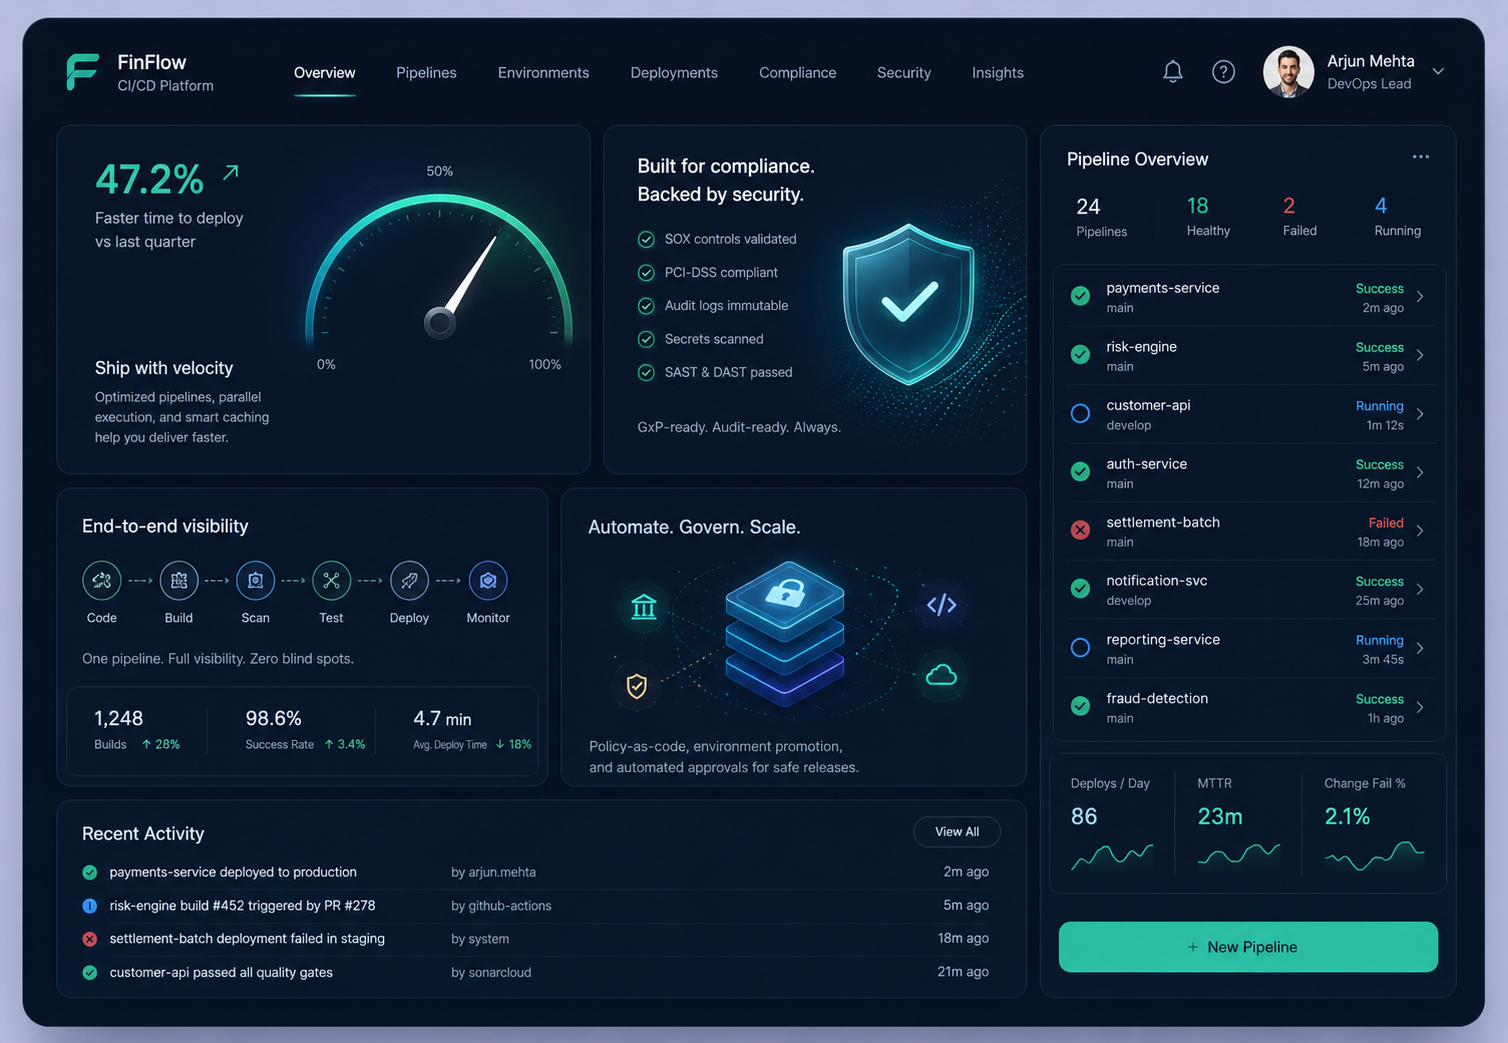
Lifted release frequency 15x with automated gates and one-click rollback.
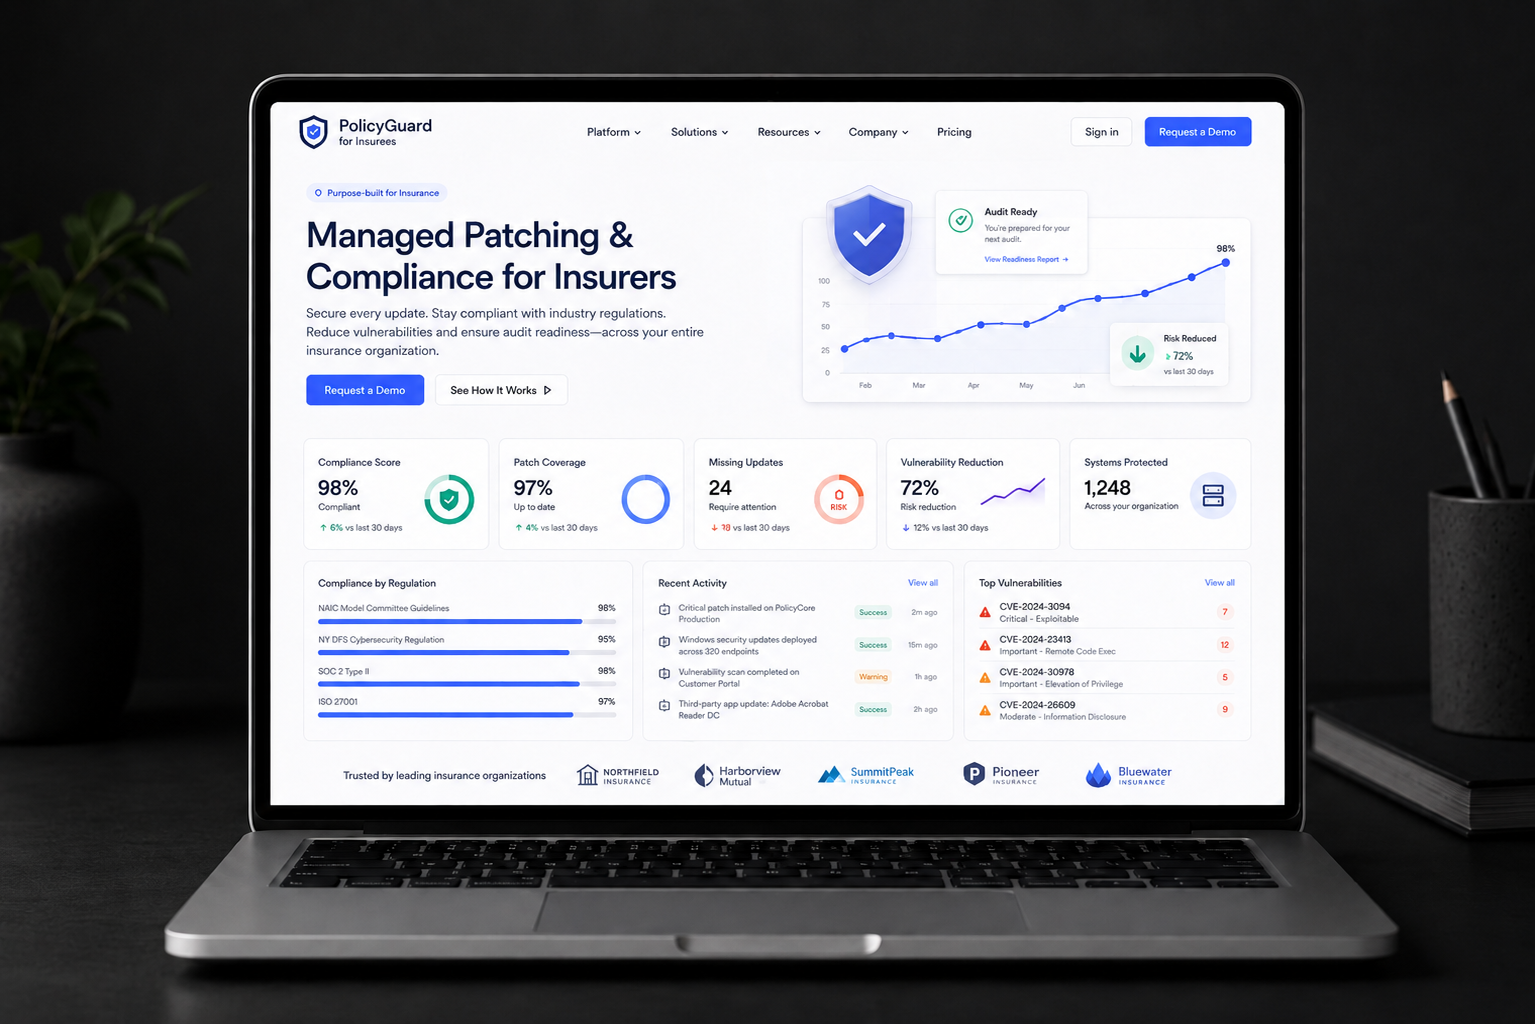
Held critical-patch SLA to 48 hours across an insurer's estate, evidenced every cycle.
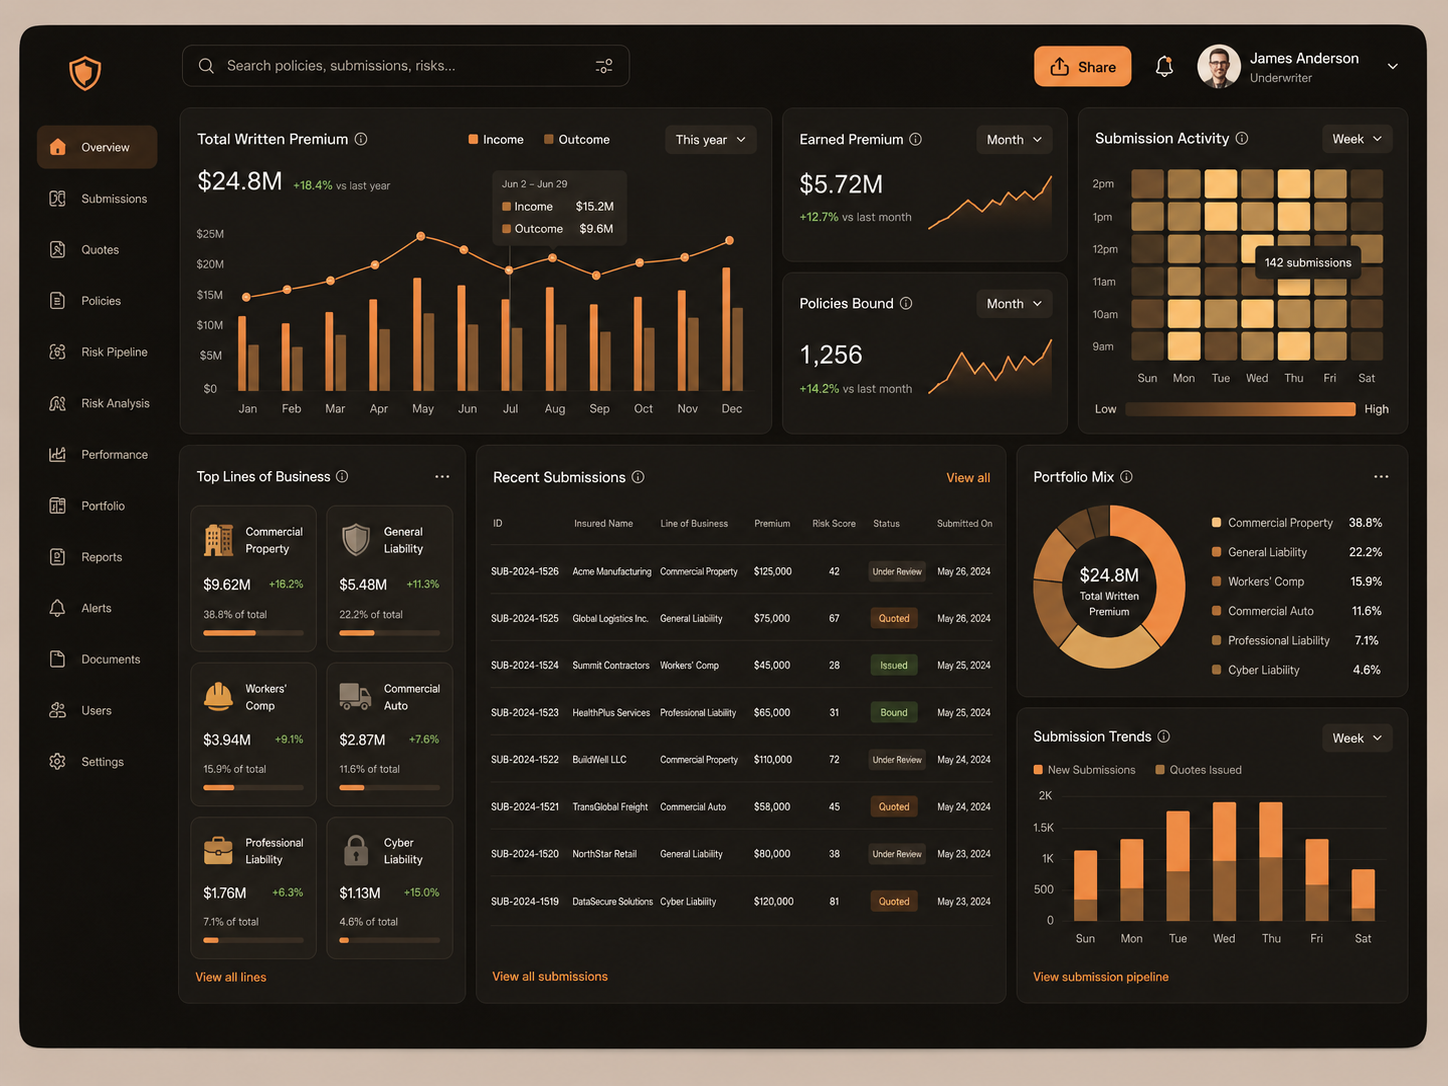
Replaced 60 spreadsheets with one governed underwriting board pack for an insurer.
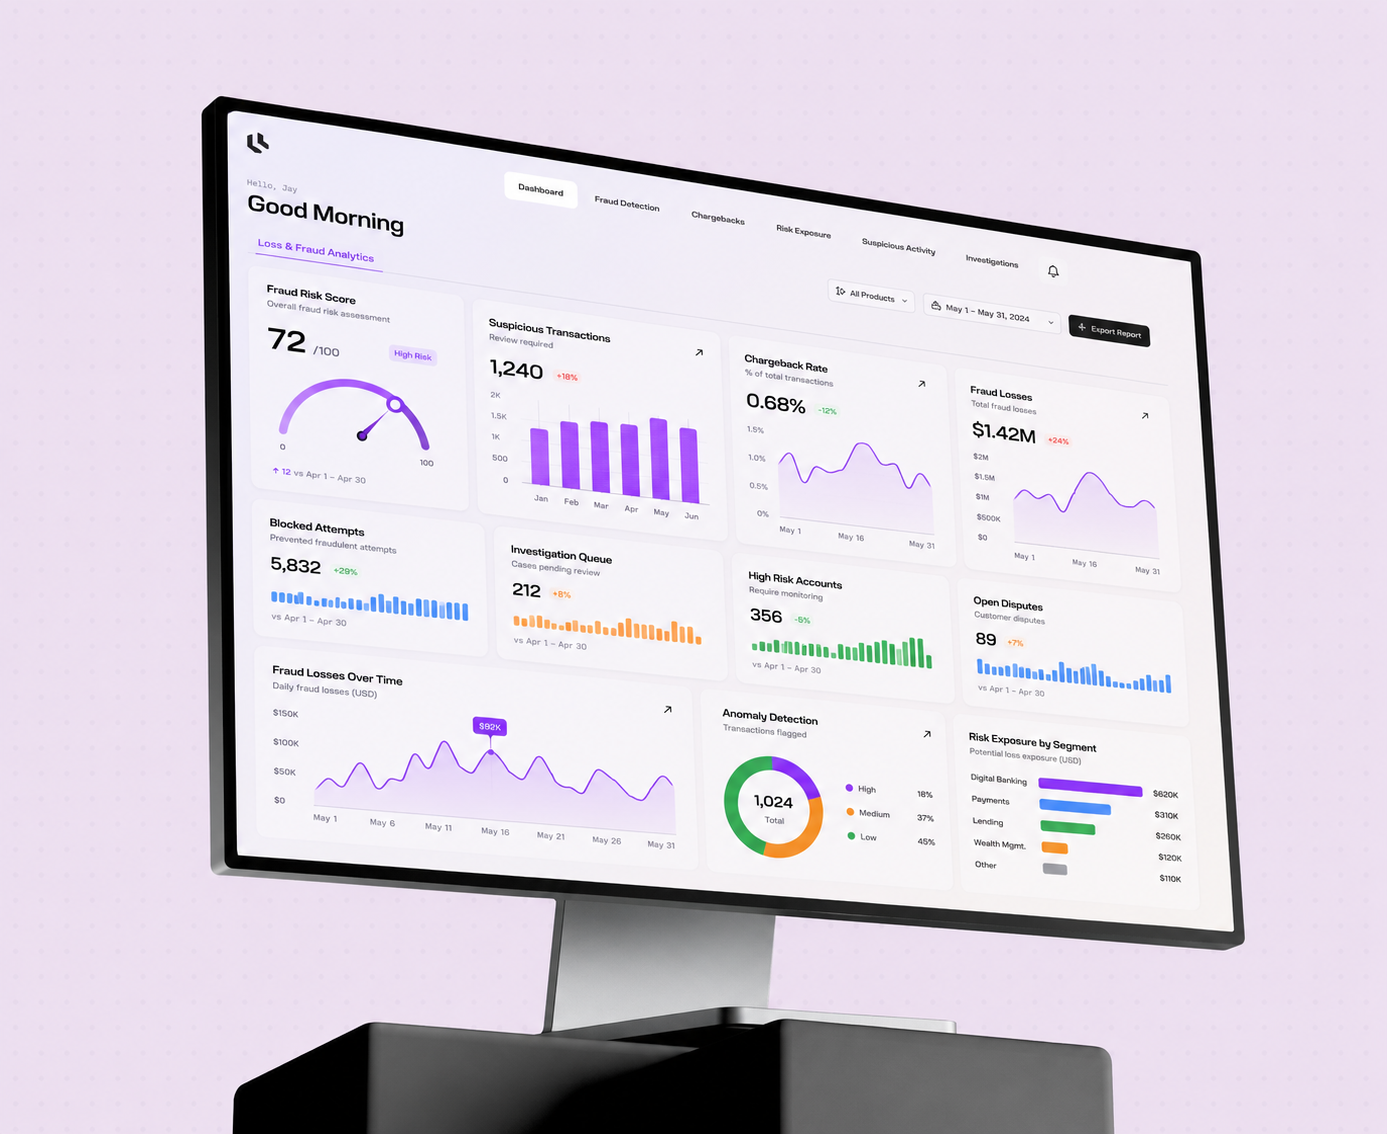
Live loss-and-fraud analytics replaced a two-day report at a fintech, surfacing emerging fraud same-day.
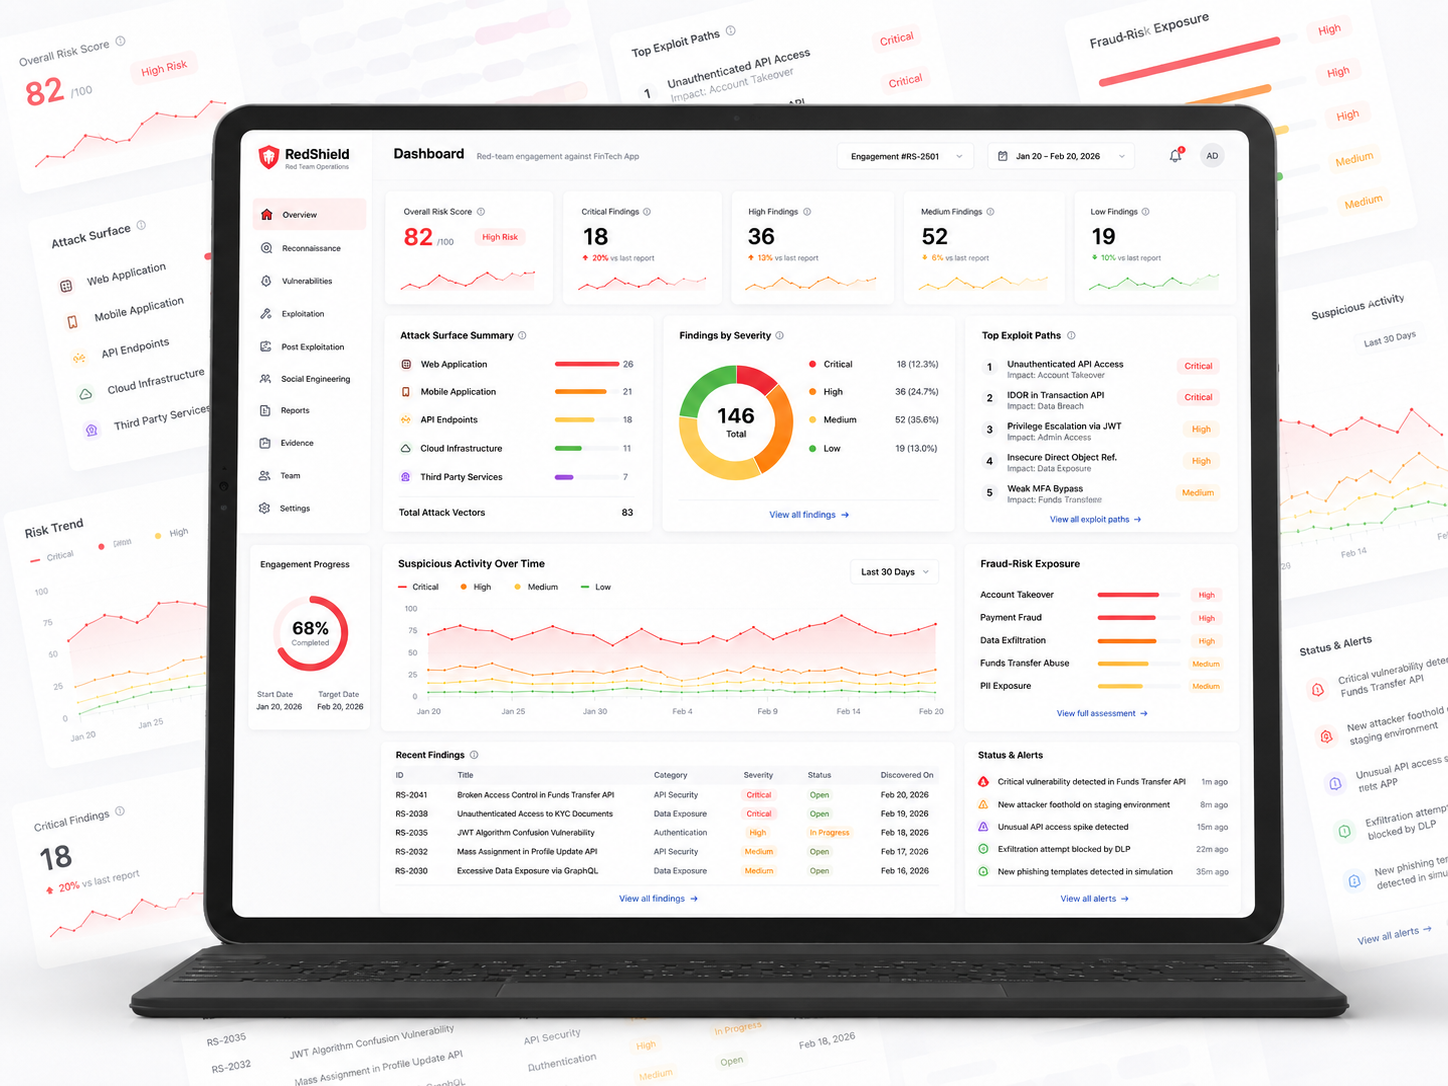
Found and helped close three account-takeover paths before a fintech's launch.
Passwordless identity cut account-takeover 22% and sign-in friction at a wealth platform.
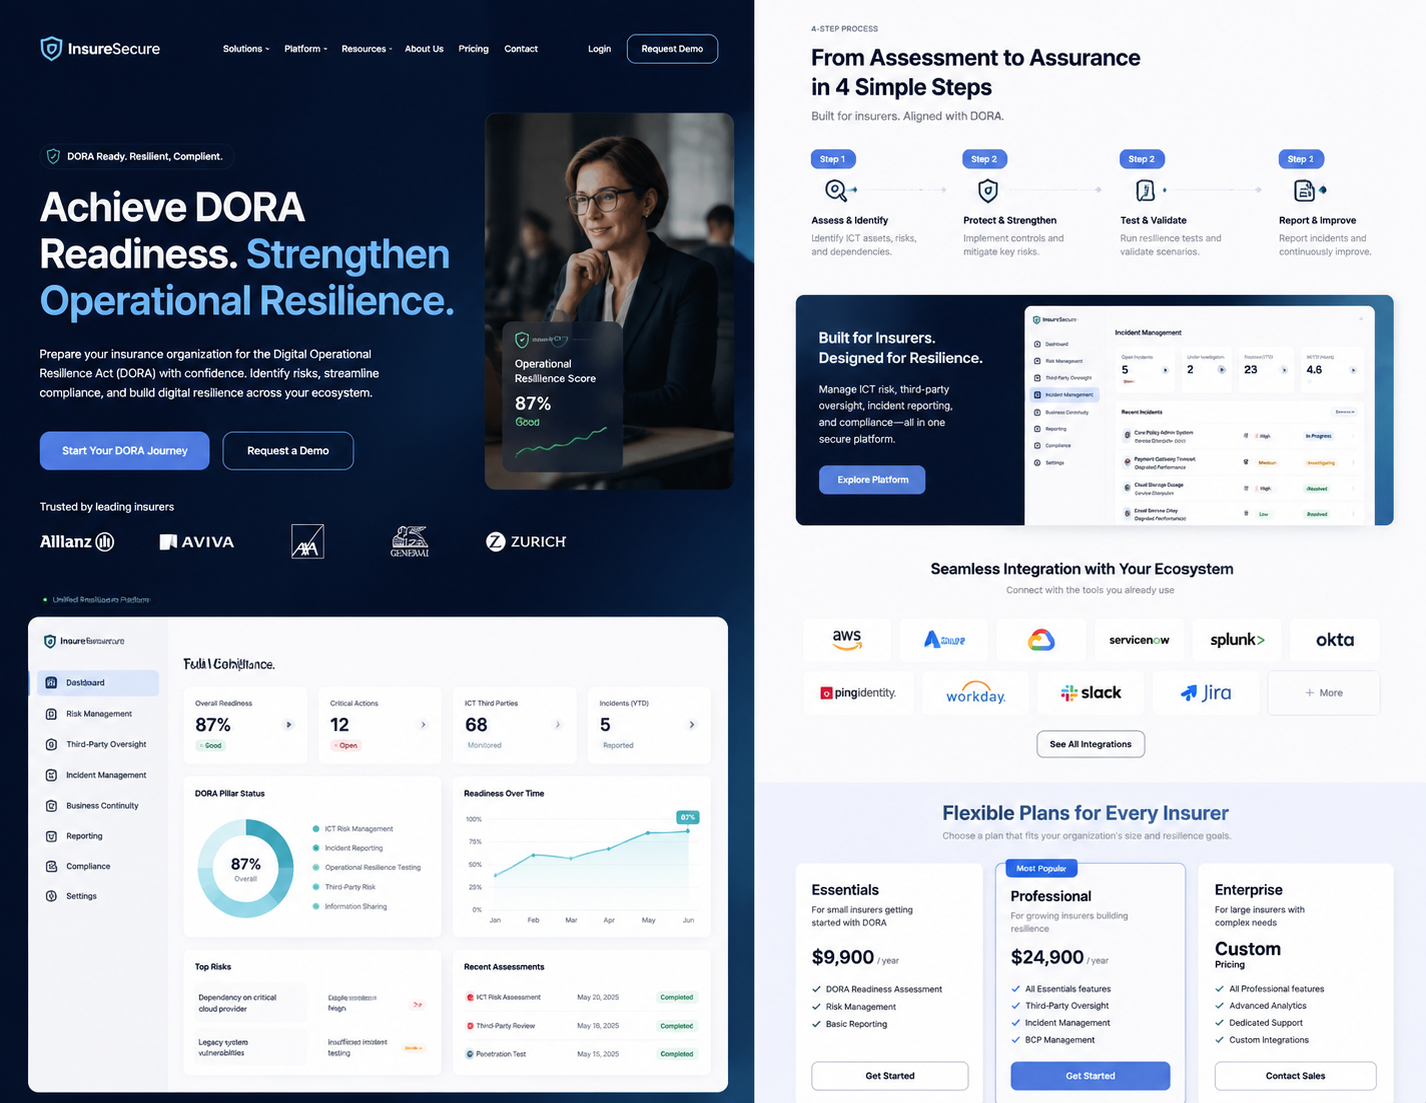
Reached DORA operational-resilience readiness in 11 weeks for an insurer.
Automated quote, coverage, and claims journeys for a US insurer, holding 100% of critical paths green across a fast release train.
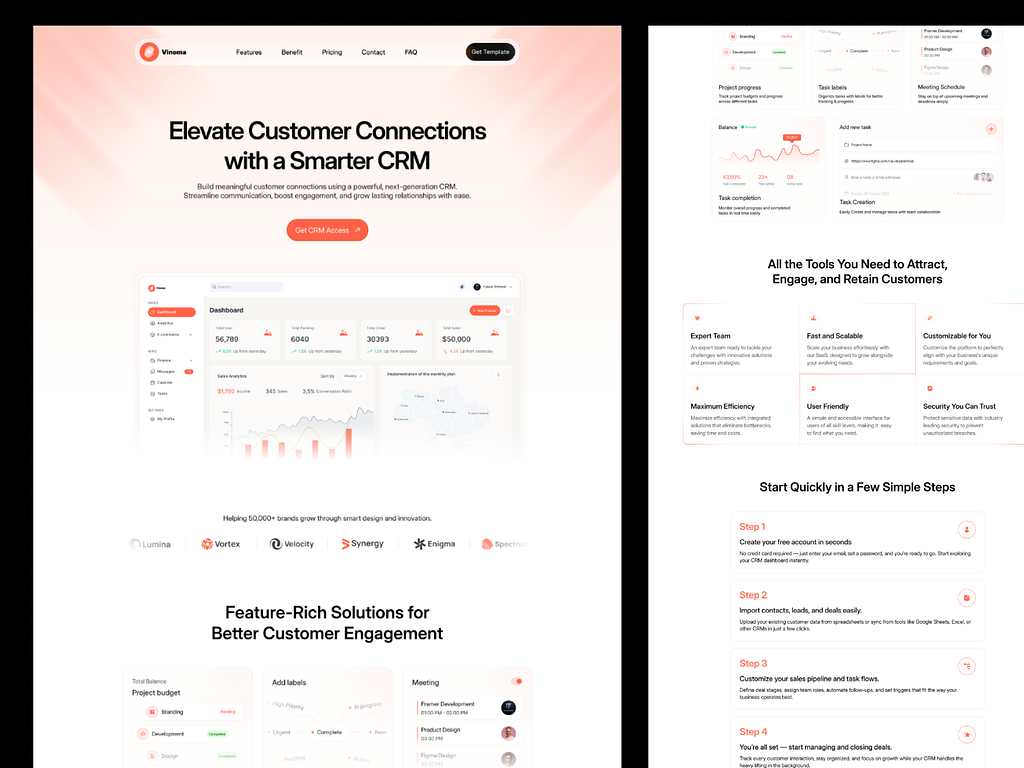
Exploratory and regression testing across pipelines, analytics, and customer records surfaced more than thirty edge-case defects that scripted suites had missed, hardening a German fintech's CRM before a major rollout.
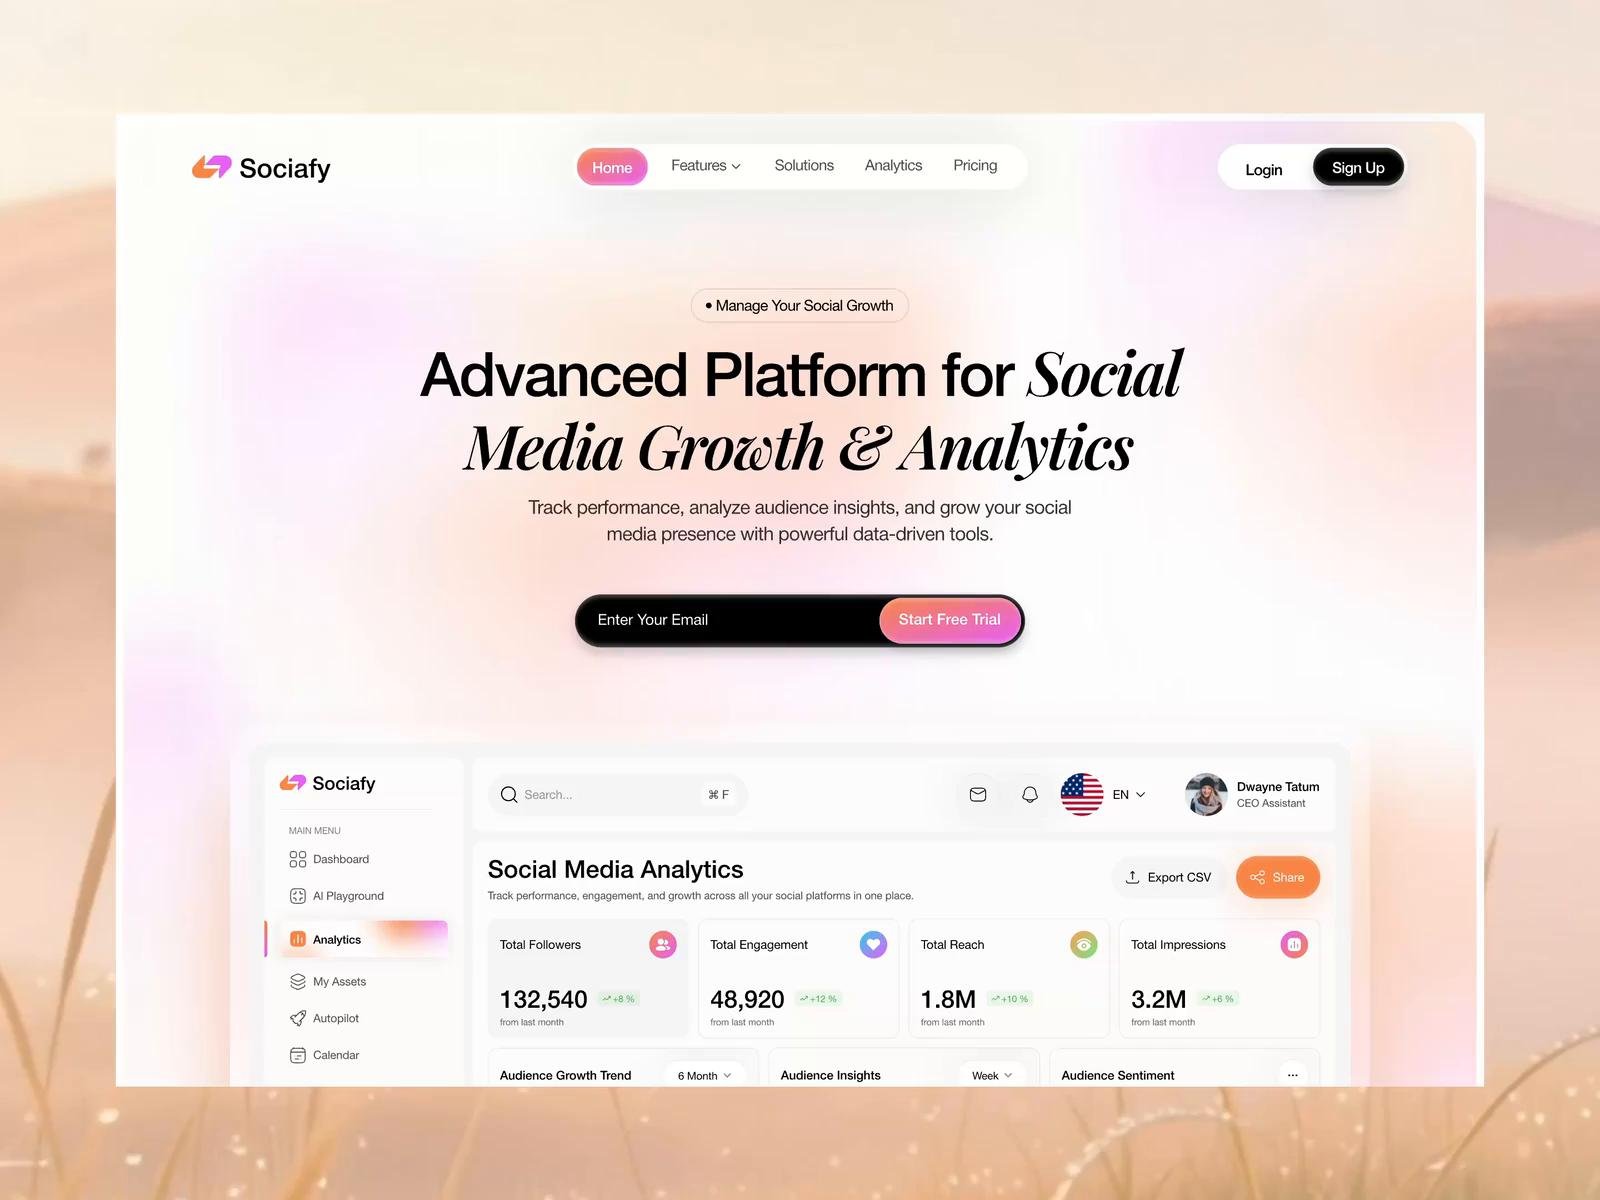
Kept p95 latency flat as audience data and concurrency scaled, proving the analytics dashboards would not slow as customers grew.
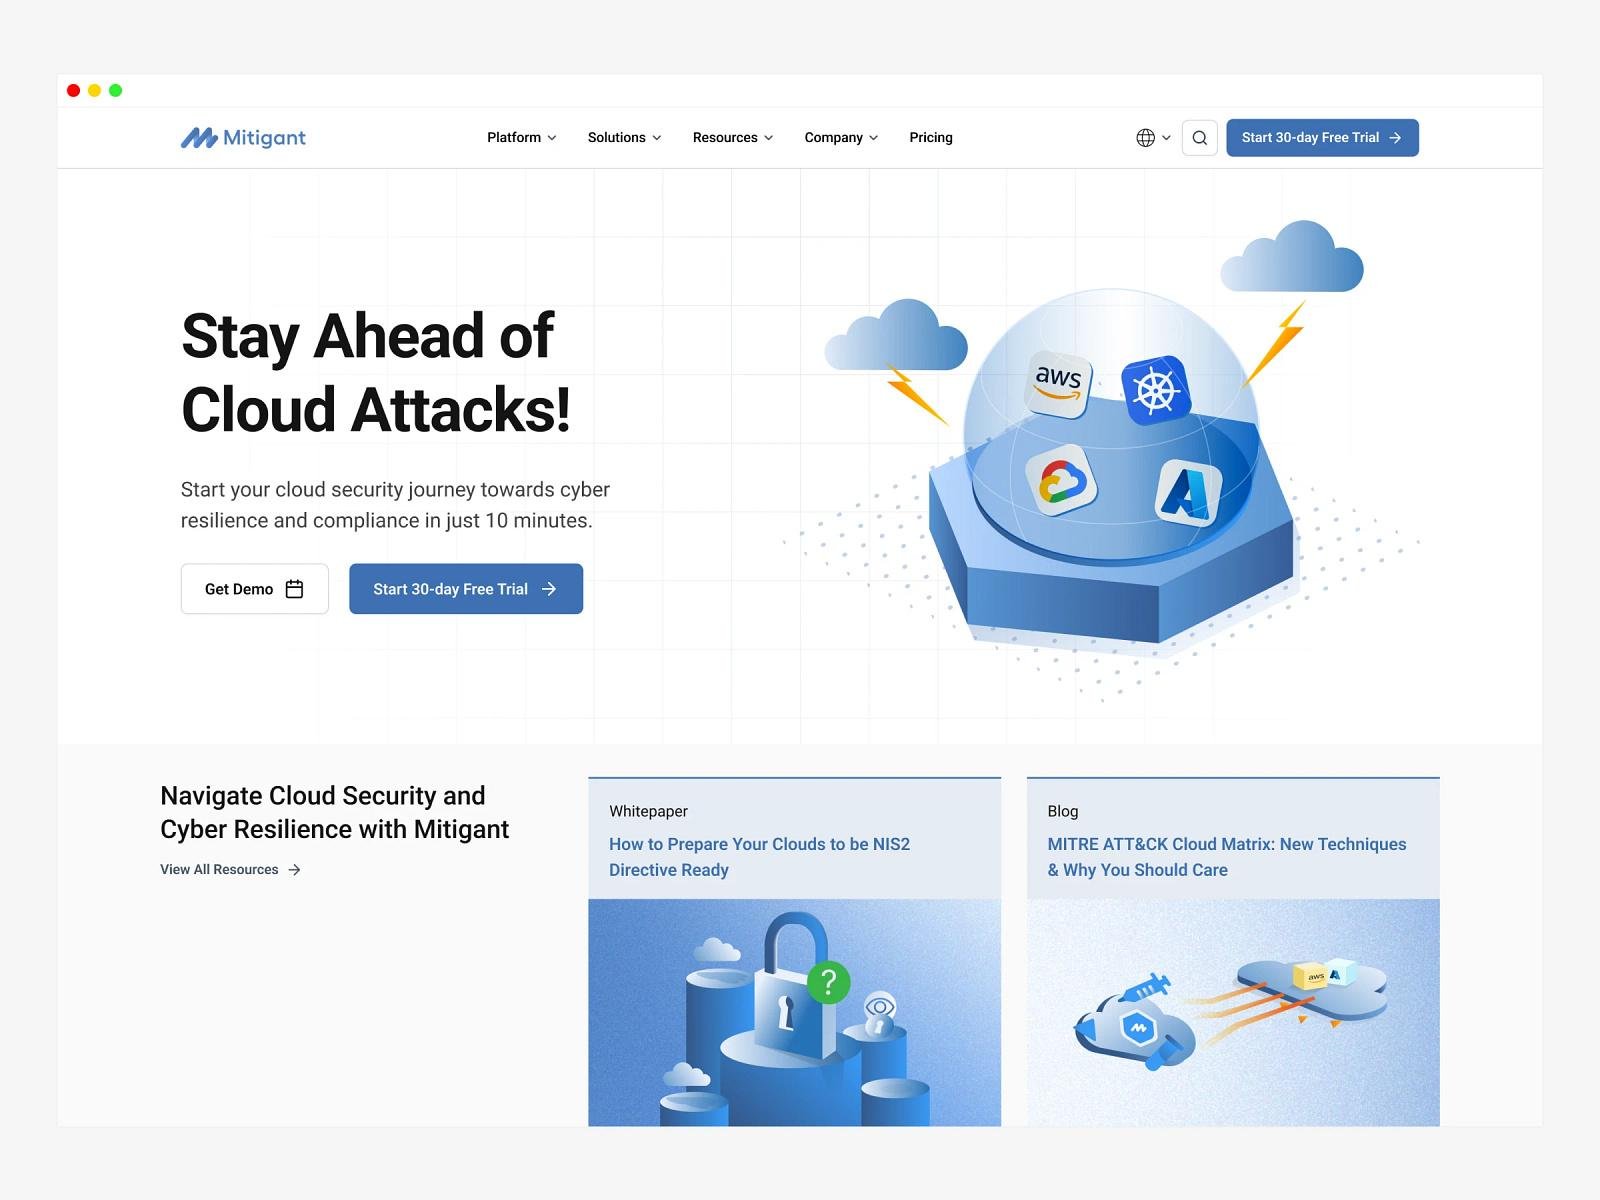
Assessed the attack surface and misconfigurations across AWS, Azure, and GCP and mapped every finding to compliance, leaving the estate audit-ready.
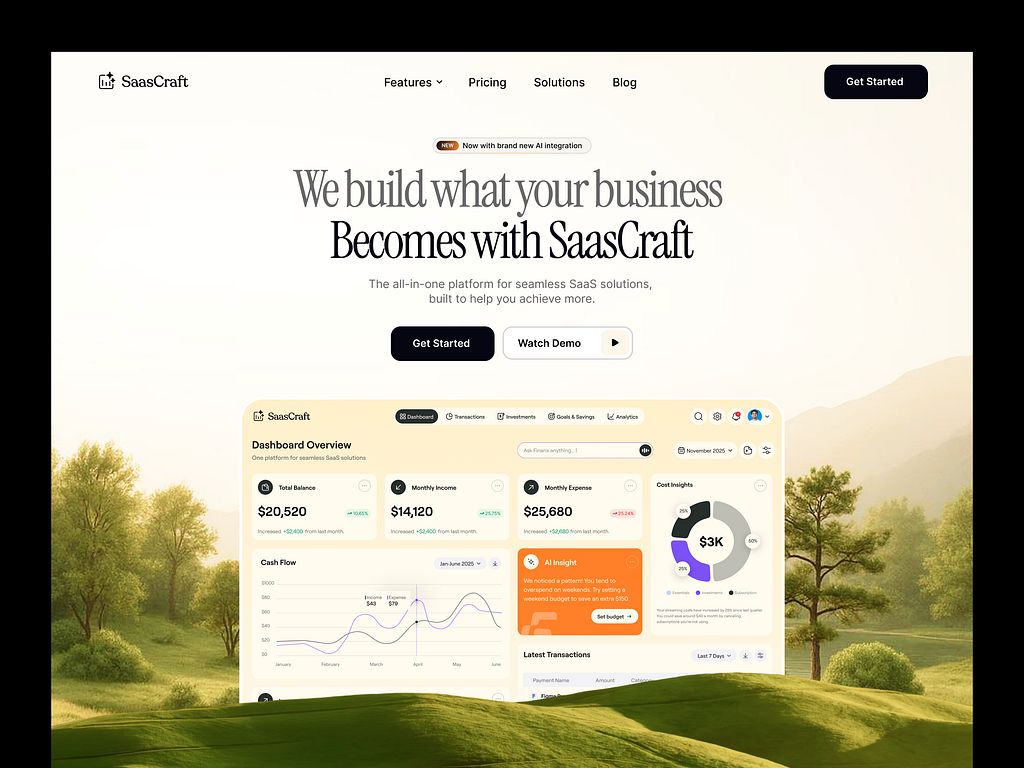
Delivered a reference architecture and a three-chain shortlist for embedding stablecoin settlement into a SaaS finance platform's cash-flow workflows.
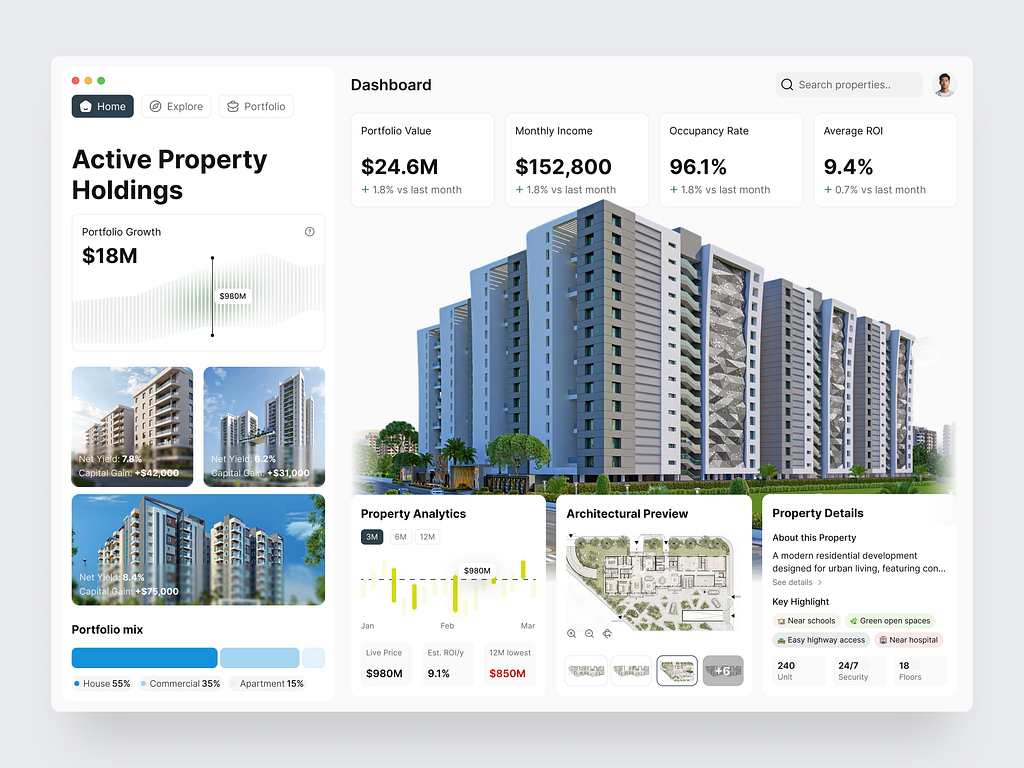
Delivered a fractional real-estate tokenisation model with an ERC-3643 compliance blueprint for regulated investor onboarding.
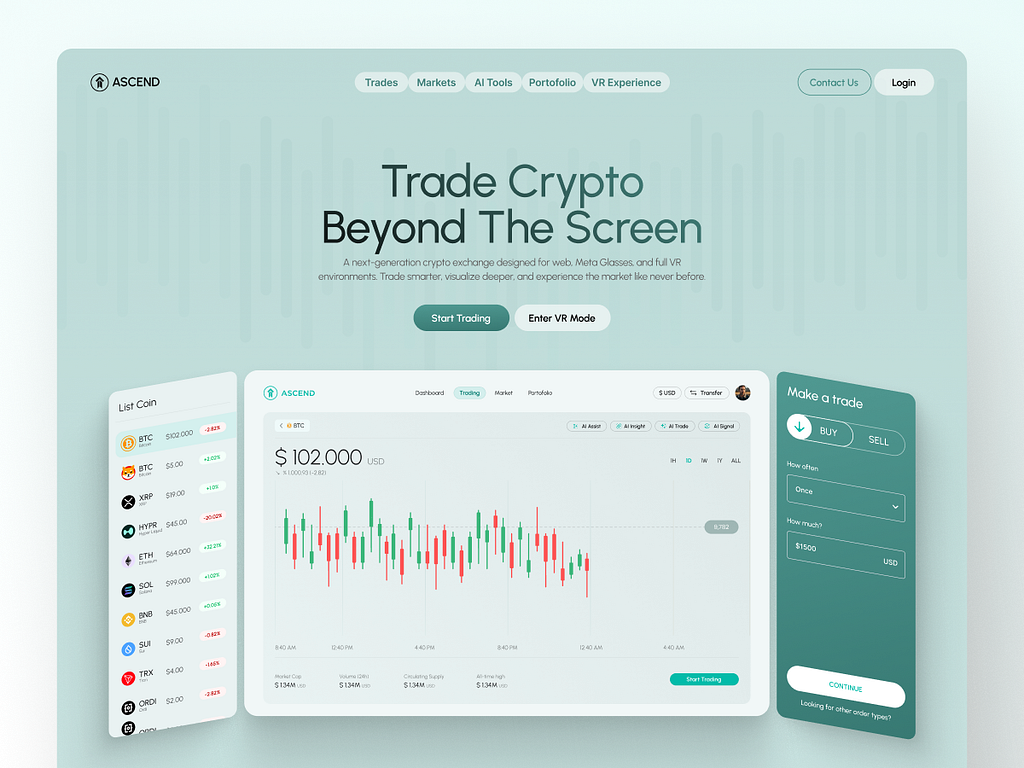
Delivered a web and VR exchange with real-time candlestick markets and on-chain order execution that settles in a single confirmation for a digital-asset trading platform.
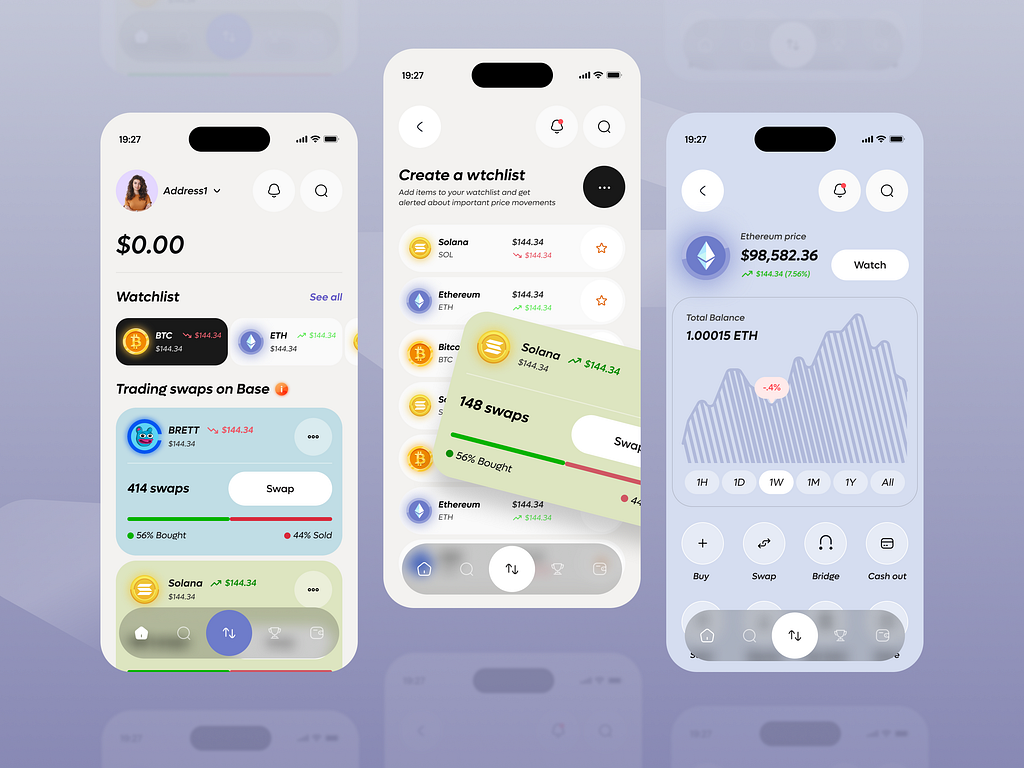
Delivered a non-custodial mobile wallet with multi-chain watchlists, swap and bridge flows, and live portfolio tracking across Ethereum and Base for a digital wealth platform.
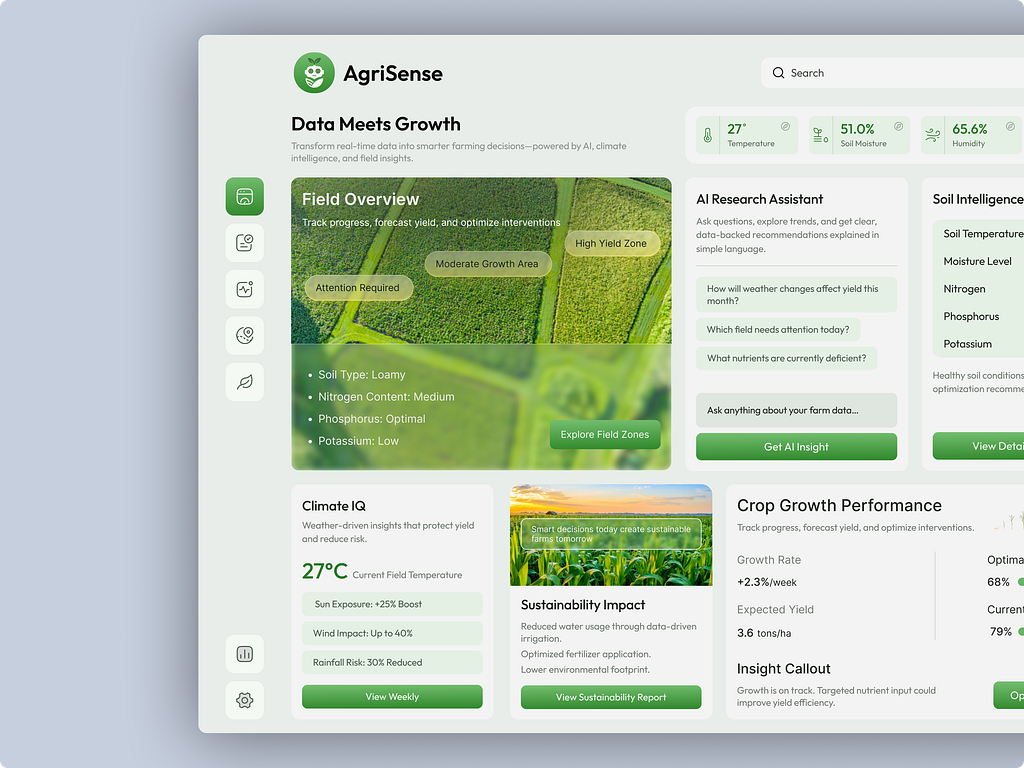
Indexed on-chain positions across more than 40 pools in real time, giving a DeFi asset manager one live view of where yield was actually moving.
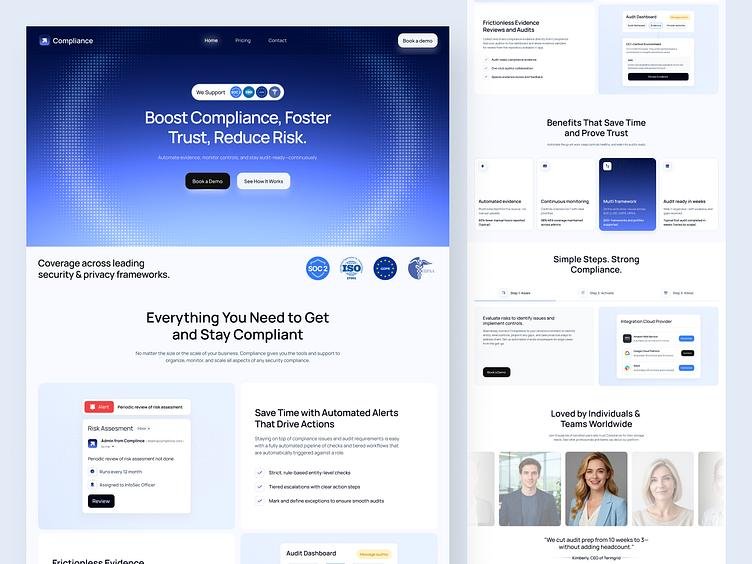
Automated evidence collection and continuous monitoring got a protocol audit-ready in weeks rather than months, with a complete controls trail behind every review.
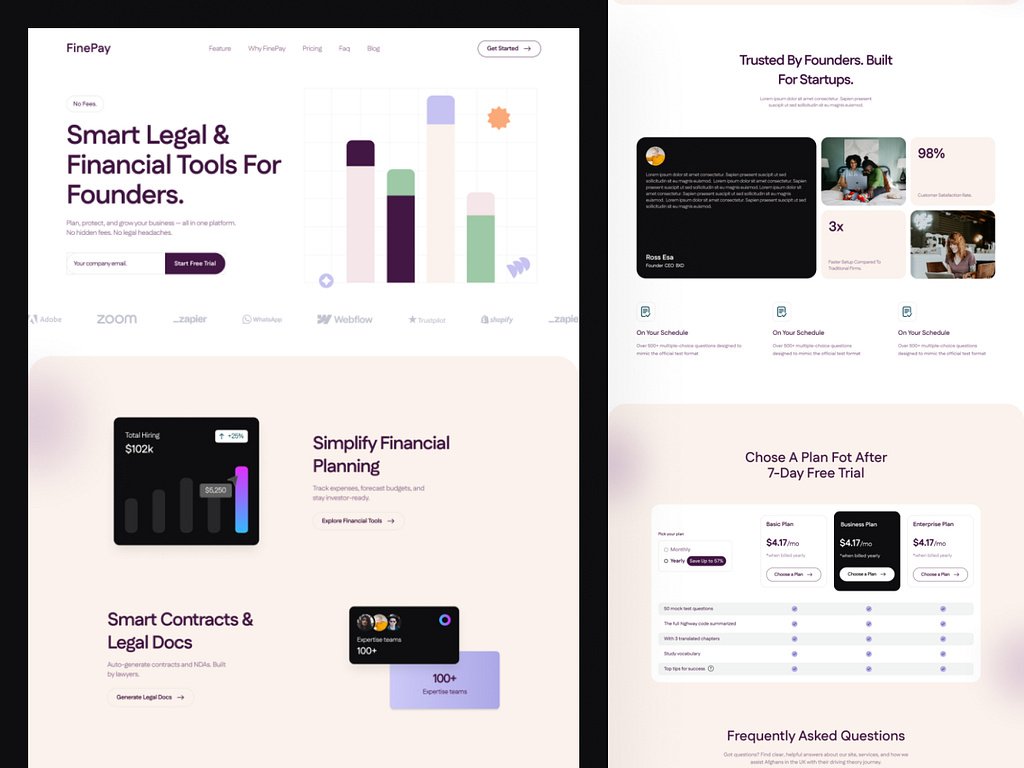
Programmable escrow and stablecoin payout contracts cleared external audit with zero critical or high findings for a founder finance platform.
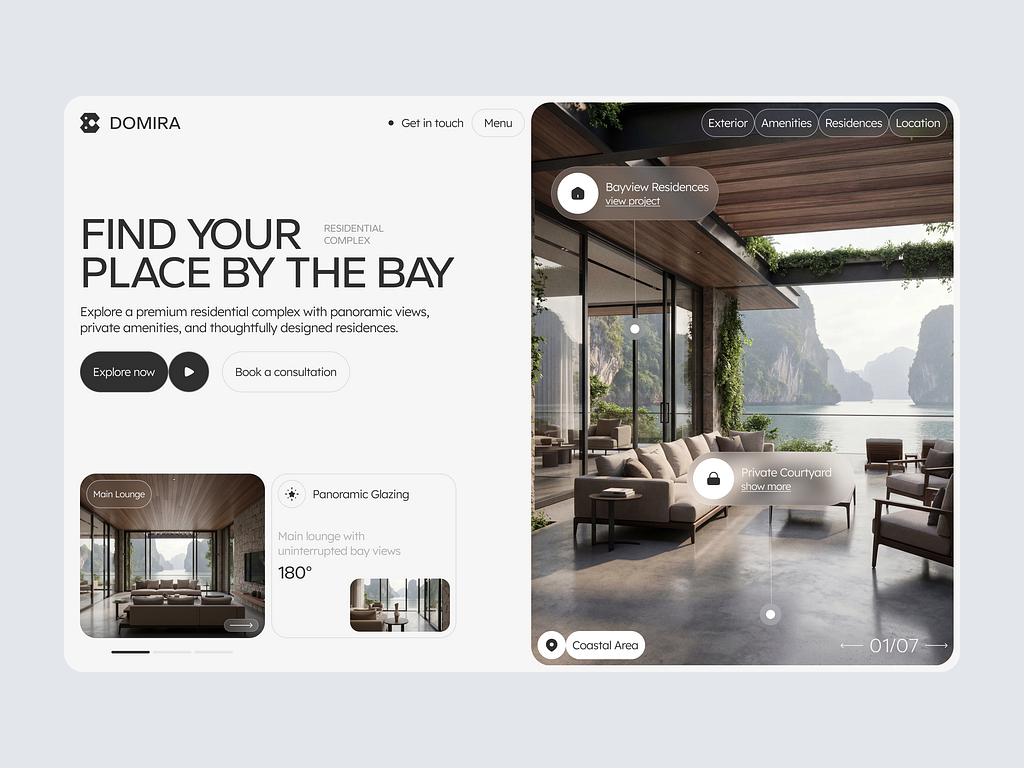
Fractional, permissioned ownership contracts with on-chain title records reached mainnet inside a tight launch window for a premium real-estate platform.
BritonOne Technology is a full-cycle engineering company that builds and operates production software for regulated estates. Since 2017, we have shipped programmes that clear audit on the first pass across banking, insurance, wealth, healthcare, and biotech. Our teams pair deep domain knowledge with disciplined engineering, treating compliance, security, and resilience as first-class deliverables. From architecture through to live operations, we stay accountable for the systems we build, measuring success by uptime, audit outcomes, and defensible business results.
We don't compete on lowest day-rate. We compete on shipped outcomes inside environments that have to clear audit.
Every engineer on every engagement is at least senior, typically eight to fifteen years deep in their craft. No bench rotations, no junior pyramid hidden behind a glossy proposal, no bait-and-switch after contract signature. The architect who scoped your engagement is the same person committing code by week three.
FCA, PRA, EBA, BaFin, FINMA, HIPAA, SOC 2 Type II: every framework we work under is treated as a design constraint from day one, not a final-stage gate. Evidence trails, model-risk packs, change-control artefacts, and pen-test reports ship alongside the code, ready for second-line review without a remediation sprint.
Small pods of three to seven engineers, each with a named delivery lead who owns scope, schedule, and outcomes from kickoff to hand-off, never a faceless team you have to chase for an answer. Weekly demos run against the signed scope, frequent verification gates catch regressions early, and quarterly outcome reviews measure real progress against the original business case rather than a moving target. Together those rituals catch scope drift before it has any chance to compound, so programmes that should take six months don't quietly stretch into eighteen, budgets stay anchored to what was agreed, and every milestone ships with a written, testable definition of done that both sides sign off before we move on.
We don't disappear the moment the engagement closes. Managed services, hypercare windows, named on-call rotations, or quarterly health checks: pick the depth that matches your operational risk profile. About seventy percent of clients return for a second programme, usually because the team that shipped the first one is still on the other end of the page.
Anonymous under MNDA. Each quote is from a senior banking buyer who owned the engagement end to end.
“Two previous vendors had eighteen months and nothing in production. BritonOne Technology walked in, cut the scope to what mattered, and we were live with a licensed product in nine.”
Direct answers to what procurement, security, and delivery leads weigh before signing: compliance, integration, and the accountability we put in writing.
Customer data and processing stay inside your chosen jurisdiction by default (EU-only or UK-only) using region-pinned cloud regions, BYOK encryption, and a no-egress posture for personal data. We work to your DPIA template, document cross-border flows under SCCs or the UK IDTA where unavoidable, and our delivery team can be staffed onshore on request.