
Red-team engagement against a fintech app
Found and helped close three account-takeover paths before a fintech's launch.
3 critical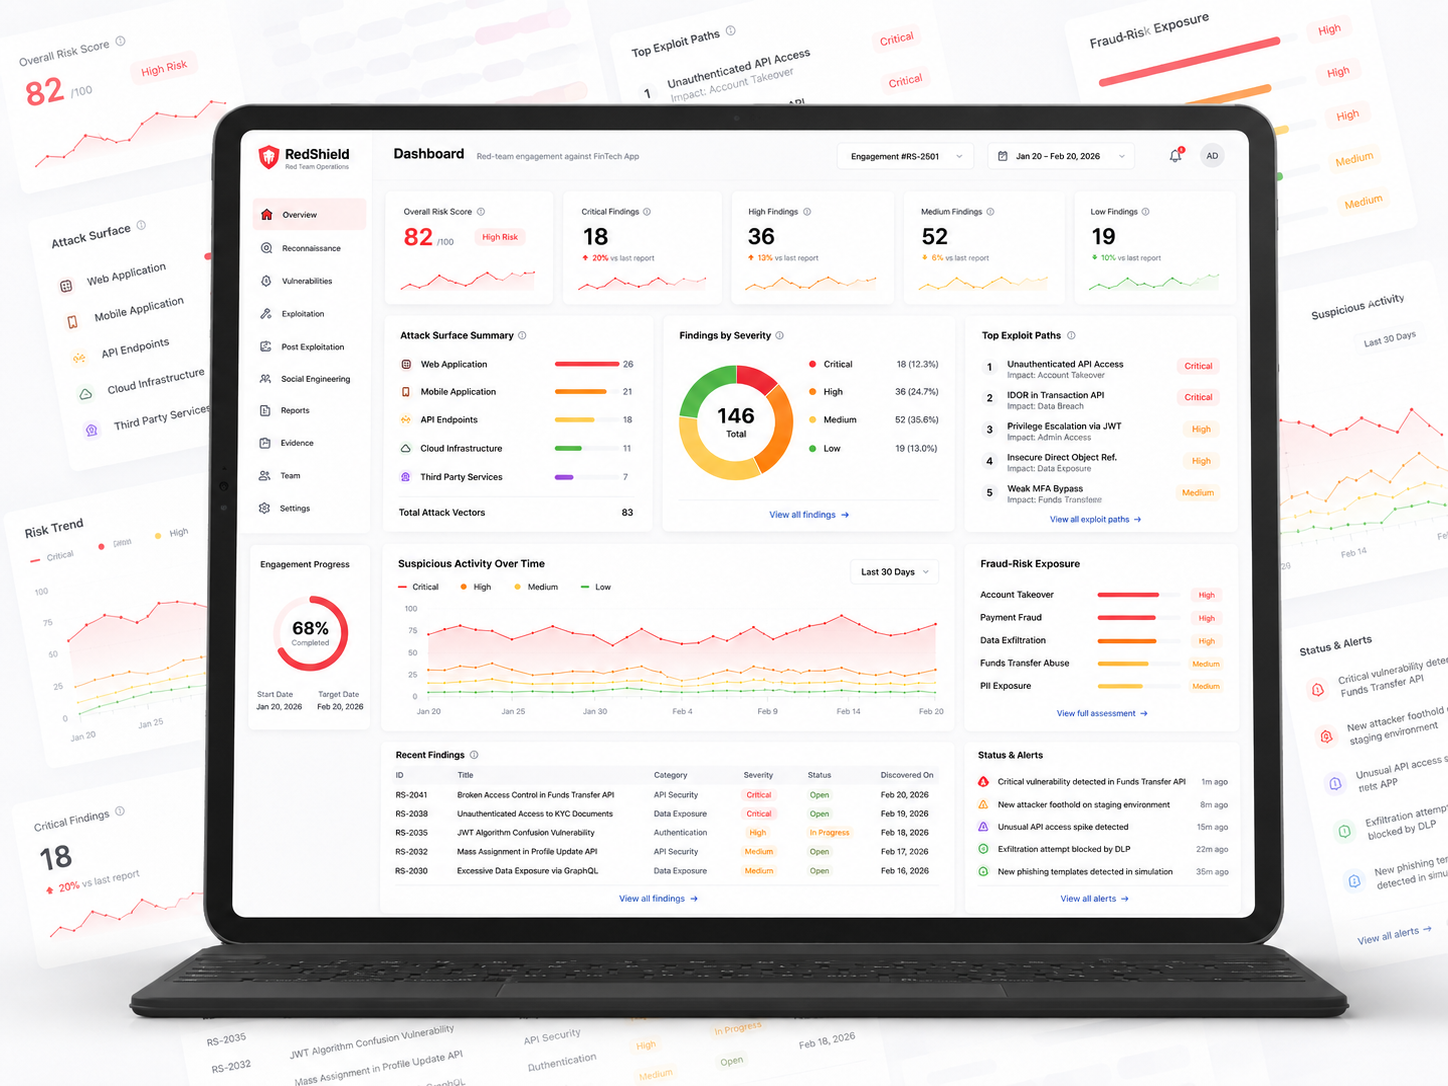
Problem, approach, and the outcome
The client is a UK fintech days away from launching a consumer app that would hold customer money. For a young brand, a post-launch security incident is not just costly: it can be fatal to trust and to the business.
They needed genuine assurance, not a checklist tick, that an attacker could not reach customer funds before they went live.
Days from launch, the fintech needed to know an attacker could not reach customer money, not hope so. The margin for error at launch was zero.
A checklist scan would tick boxes without answering the question that actually mattered: could someone chain small weaknesses into a real path to funds? Compliance-style testing would have given false comfort.
With regulators and early customers watching, a post-launch incident would have been existential for a young brand. The stakes made a superficial test worse than none.
We ran a goal-based red-team across the app, API, and backend, working towards a concrete objective the way a real attacker would rather than enumerating isolated findings. Chasing a real goal is what surfaces the paths that matter.
We chained weaknesses together, showing how a minor disclosure plus a permissive endpoint became a route to account takeover. Demonstrating the full chain is far more convincing, and more useful, than a list of isolated issues.
Each path came with a clear reproduction and a prioritised fix, and after the team remediated, we re-tested to confirm every fix held under the same attack. The launch cleared with the real routes to funds closed.
- Three account-takeover paths found and closed
- Findings chained into real attack paths, not just listed
- Re-tested to confirm every fix held
- Launch cleared with the critical routes to funds closed
More Cybersecurity case studies
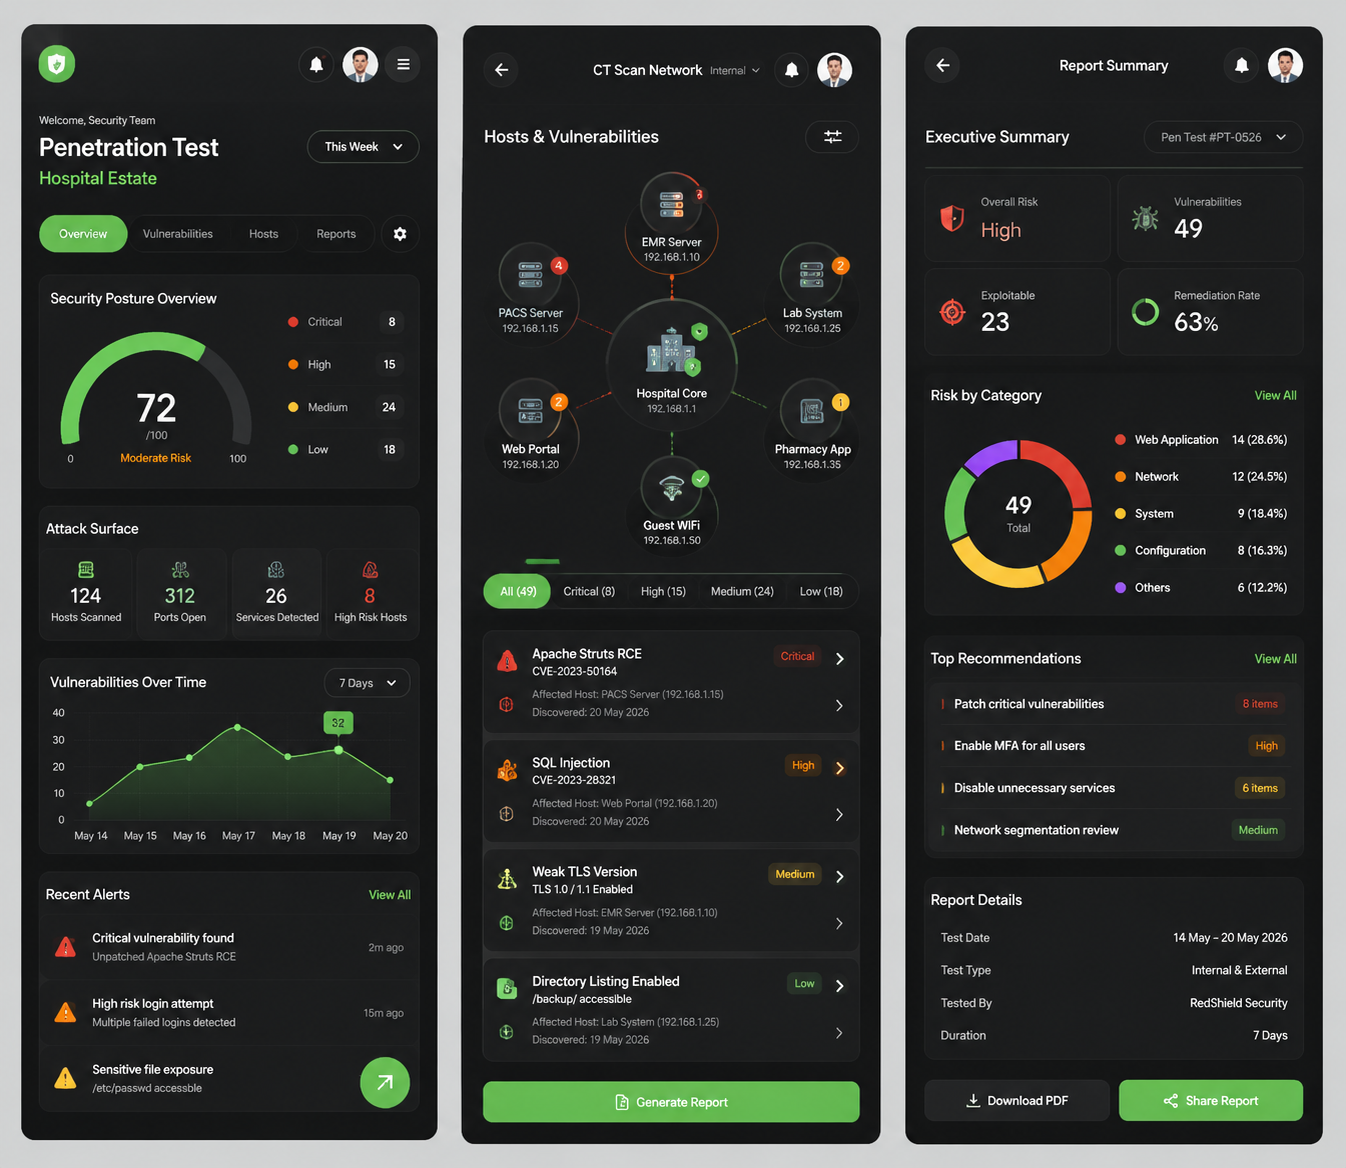
Penetration test for a hospital estate
Surfaced 61 exploitable paths across a hospital estate, prioritised by patient-safety impact.
Read the full case study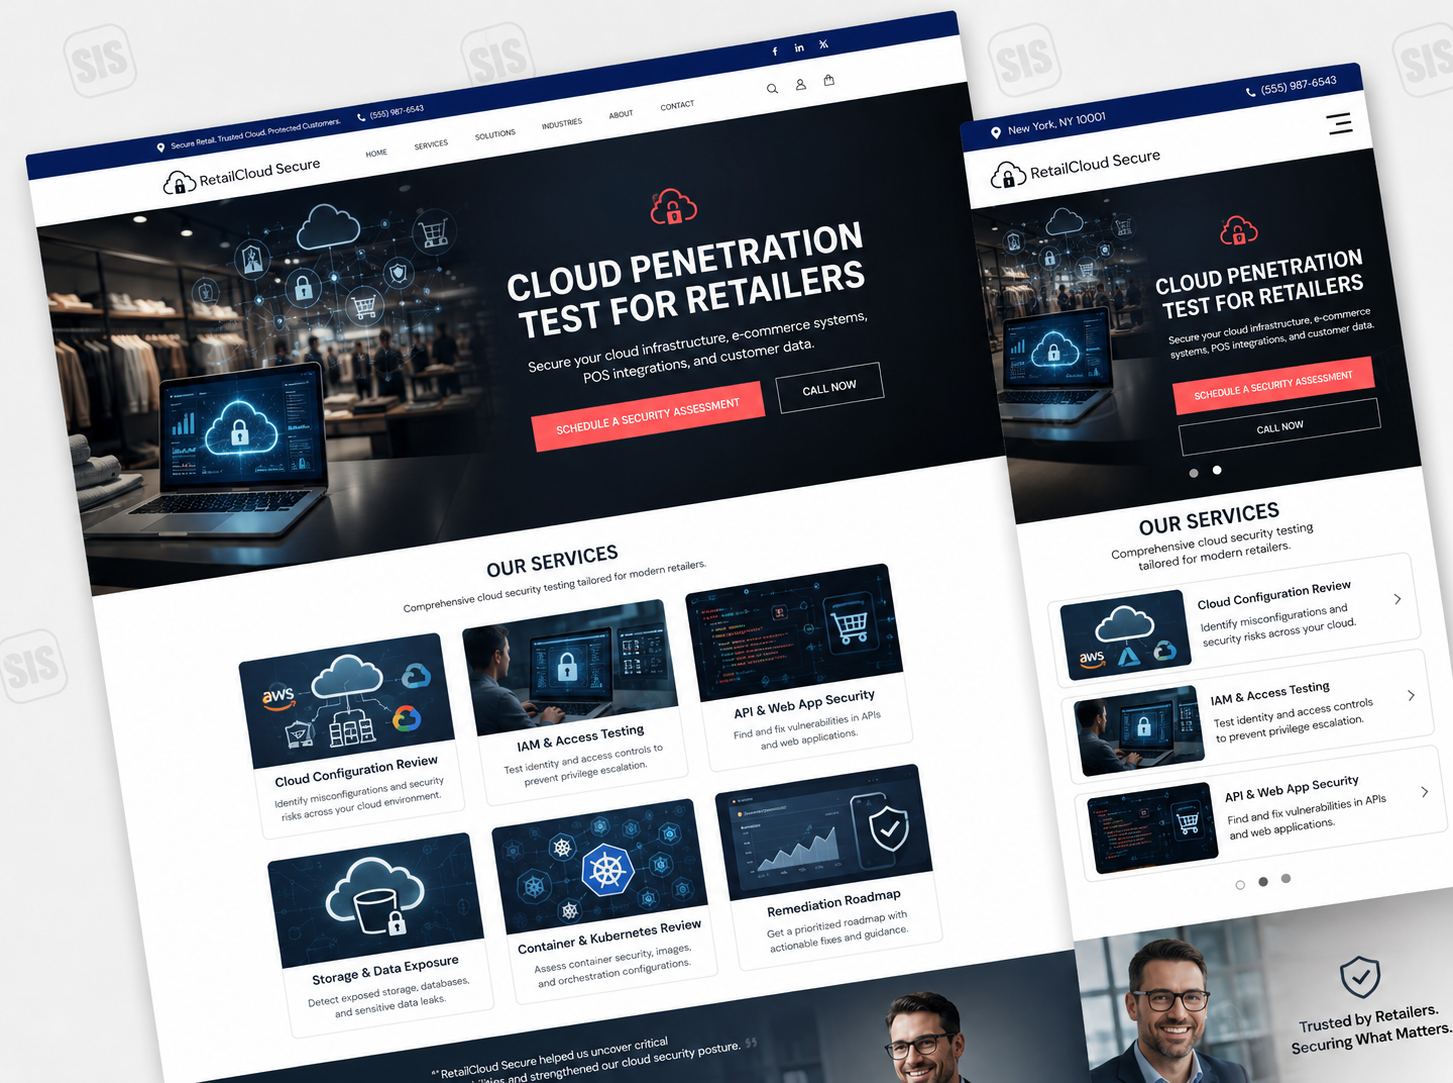
Cloud penetration test for a retailer
Surfaced 74 exploitable misconfigurations across a retailer's multi-account cloud estate.
Read the full case study
Zero-trust rollout for a government agency
Rolled zero-trust access to 25,000 civil servants without a productivity dip.
Read the full case studyGet a senior architect on the call, first time, every time.
No SDR gauntlet. 30 minutes with an engineer who can scope the problem, name the risks, and give you an honest feasibility call.