
API testing for a digital banking app
Delivered 10,000+ automated assertions across balance, transfer, and payment APIs, catching every schema and auth regression before release for a digital bank.
10k+ assertions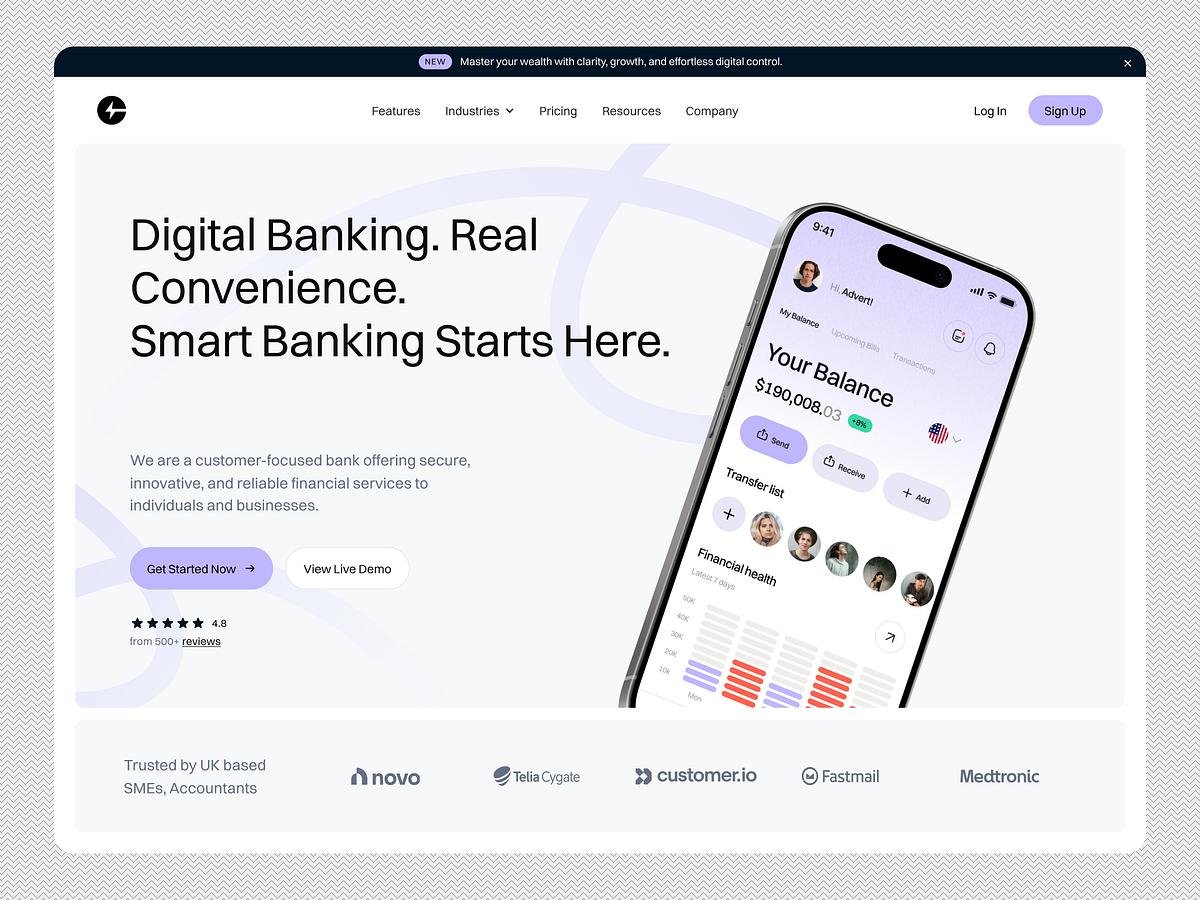
Problem, approach, and the outcome
The client is a UK digital bank whose mobile app sits on top of a growing surface of balance, transfer, and payment APIs. For a bank, a single wrong response on a money-movement endpoint is a customer-trust and regulatory problem, not a minor bug.
Release cadence had accelerated to weekly, but API assurance was still a manual, spreadsheet-driven affair that could not keep pace with the change.
Money-movement endpoints were being tested by hand each release, so coverage was thin and inconsistent, and reviewers had no reliable evidence that a passing check meant a correct response.
Auth flows, error paths, and response contracts were the highest-risk part of the surface, yet they were the least systematically covered. A wrong balance or a leaked field would surface in production, not in review.
The bank needed dependable, repeatable API assurance that ran on every build and produced evidence its auditors could trust, without slowing the weekly release train.
We built a functional, contract, and security suite across the balance, transfer, and payment APIs, asserting status codes, headers, and response schemas on every endpoint so schema drift and breaking changes are caught in CI rather than by a customer.
We exercised the OAuth and JWT flows directly, testing token expiry, scopes, and role-based access, and confirmed that over-scoped or invalid tokens are rejected on every protected route. Rate limits and negative paths were tested as first-class cases, not afterthoughts.
The suite runs headless through Newman in the pipeline, and we layered JMeter load checks over the money-movement endpoints so behaviour under concurrency was verified too. Every failure ships with the exact request, expected versus actual response, and environment, linked in the tracker.
- 10,000+ automated assertions across the money-movement surface
- Contract and schema drift caught in CI, not production
- Auth, scope, and token-expiry paths verified on every protected route
- Every failure shipped with reproducible request-and-response evidence
More Quality Assurance & Testing case studies
API testing for an IoT device platform
Validated device, telemetry, and notification APIs under live conditions, shipping a release with zero contract breaks across connected consumers for an IoT platform.
Read the full case study
API testing for a video-streaming platform
Achieved full endpoint coverage across upload, playback, and monetisation APIs, with auth, rate limits, and error paths verified end to end for a streaming platform.
Read the full case study
API testing for a travel-booking aggregator
Contract and integration testing across hotel, flight, and car-rental APIs cut integration bugs 62% by catching schema and pricing mismatches before release.
Read the full case studyGet a senior architect on the call, first time, every time.
No SDR gauntlet. 30 minutes with an engineer who can scope the problem, name the risks, and give you an honest feasibility call.