
ISO 27001 and DTAC for a telemedicine platform
Achieved ISO 27001 and NHS DTAC assurance at first assessment for a telemedicine platform.
first pass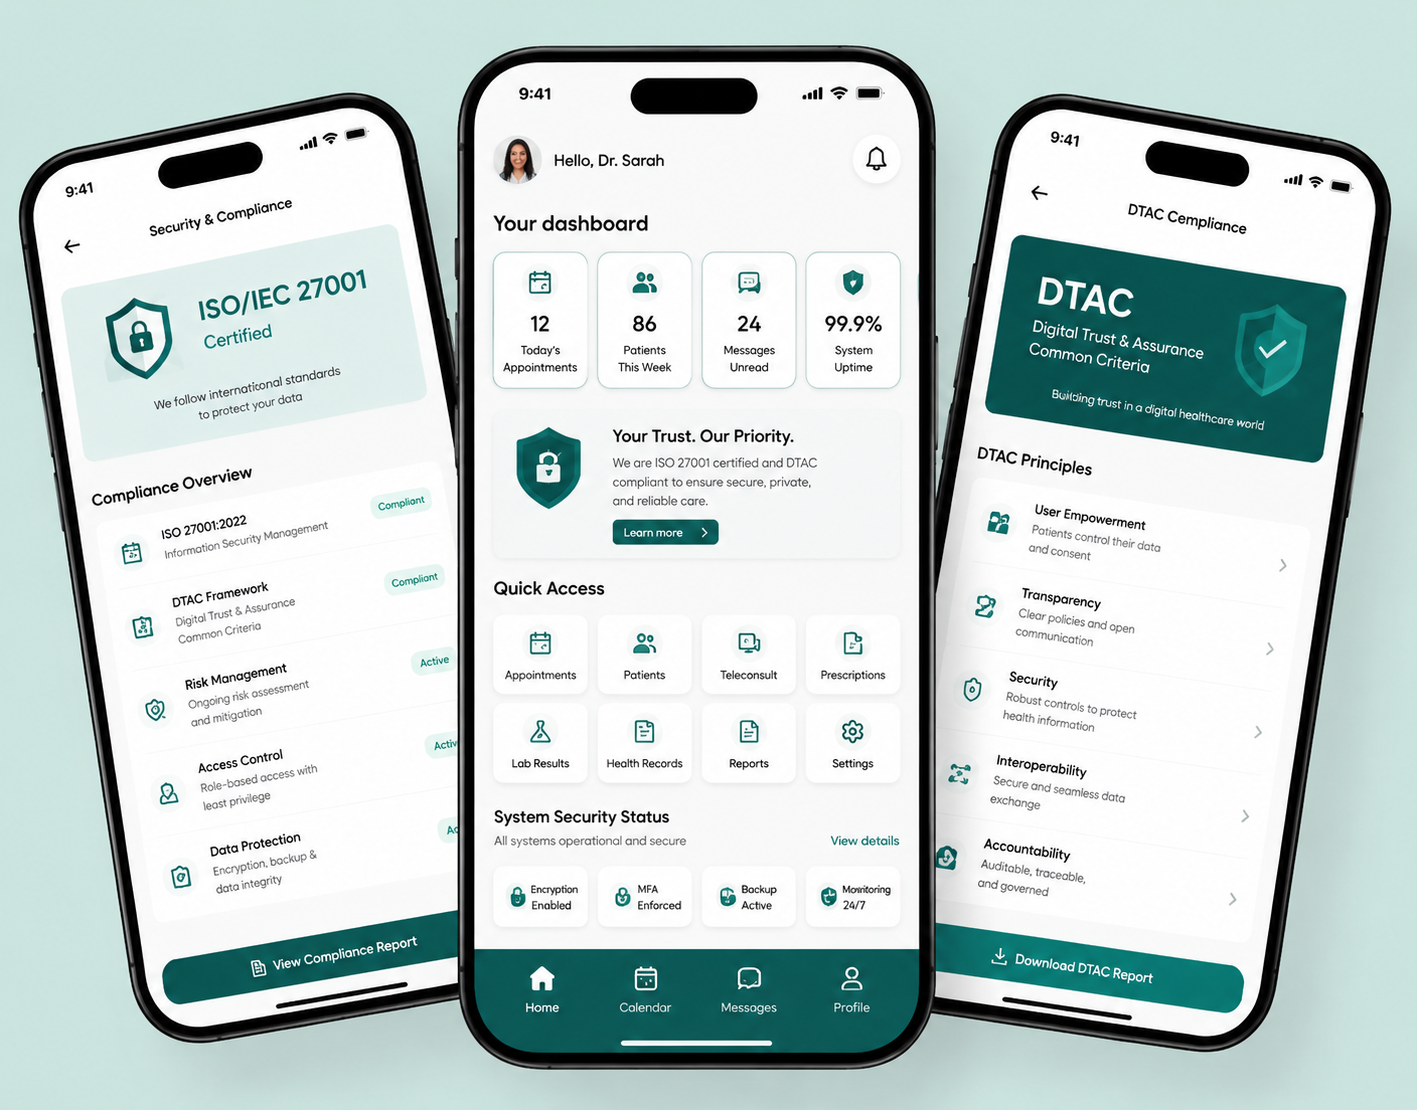
Problem, approach, and the outcome
The client is a growing UK telemedicine platform selling into the NHS, where ISO 27001 and DTAC assurance are effectively table stakes. Without them, deals stall regardless of the product's merits.
The platform did not yet hold these certifications, so revenue was being held hostage to assurance questions on every deal.
NHS buyers demanded ISO 27001 and DTAC assurance the platform did not yet hold, and every deal stalled on the same assurance questions. Sales were blocked at the certification gate.
For a growing telemedicine business, each stalled deal was revenue held hostage to a certificate. The commercial cost of the gap was immediate.
A heavyweight, box-ticking ISMS would have slowed the engineering team the business depended on, so the fix had to fit how they actually work. Compliance could not become a drag on delivery.
We built a right-sized ISMS mapped to how the team already operates, so controls reinforced good practice rather than fighting it. Fitting the ISMS to the team is what kept it from slowing delivery.
Evidence collection was automated, keeping the certification live instead of a point-in-time snapshot that rots. Automation is what makes the certification sustainable.
We ran the internal assessment ourselves first to find and fix gaps before the external assessor saw them, and coached the team through the process so they could maintain and extend it afterwards. The platform passed at first assessment and can keep it.
- ISO 27001 and DTAC at first assessment
- Evidence collection automated
- An ISMS that fits how the team works
- Stalled NHS deals unblocked on assurance
More Cybersecurity case studies
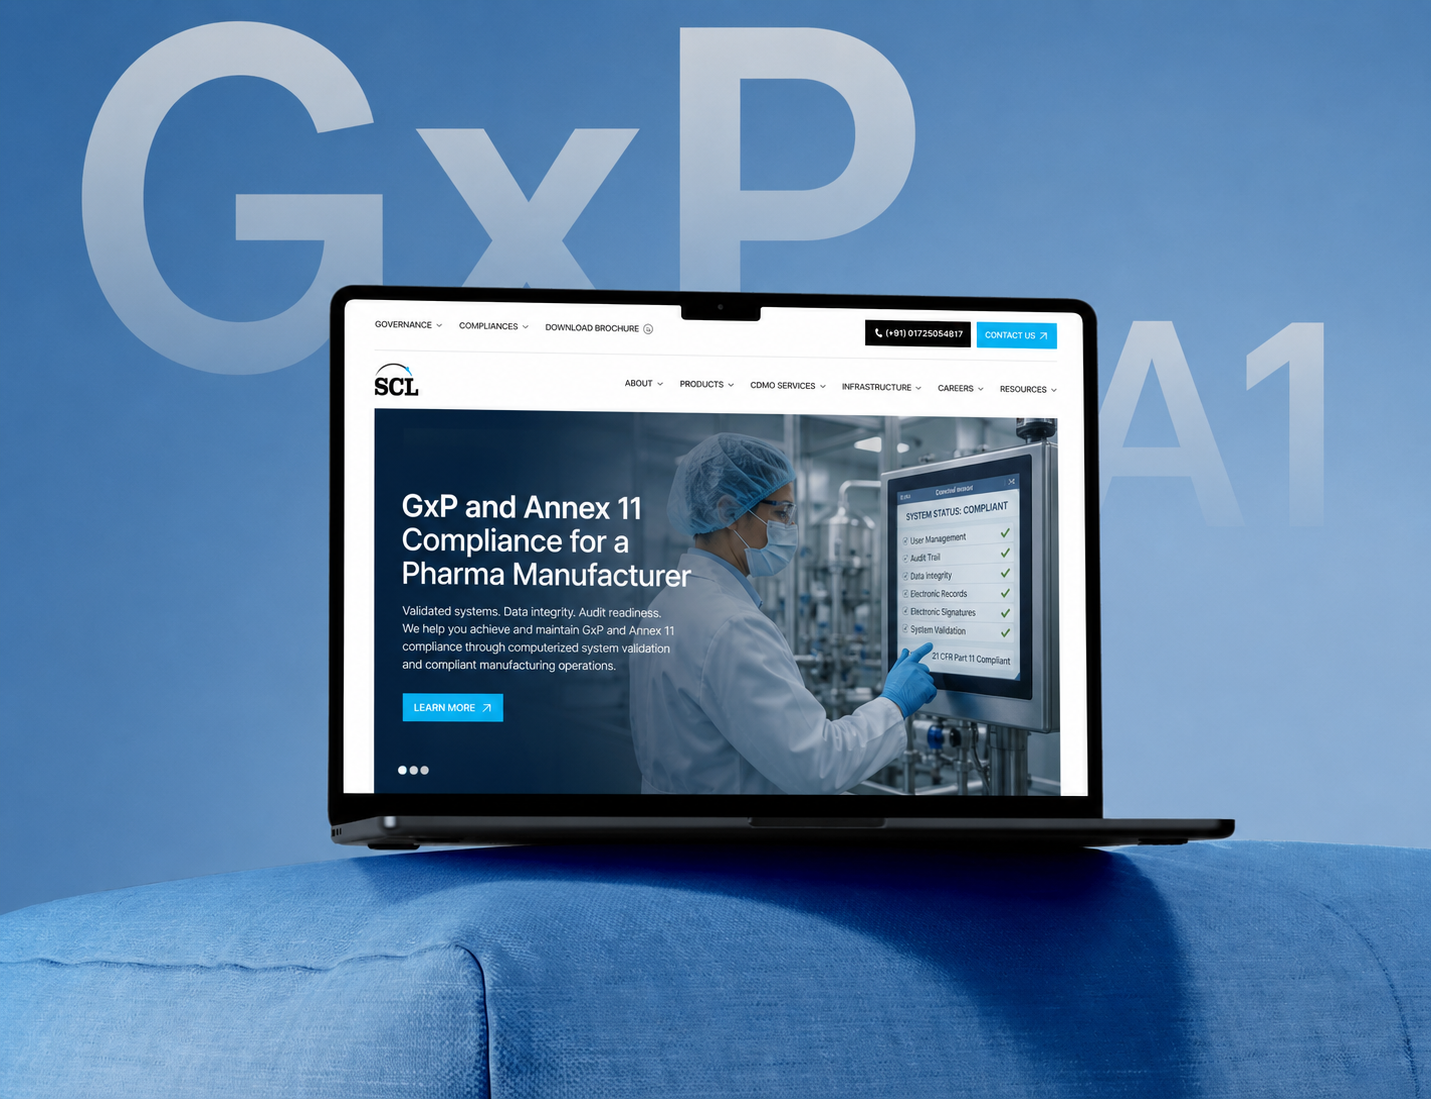
GxP and Annex 11 compliance for a pharma manufacturer
Reached validated Annex 11 compliance for a pharma manufacturer in 12 weeks.
Read the full case study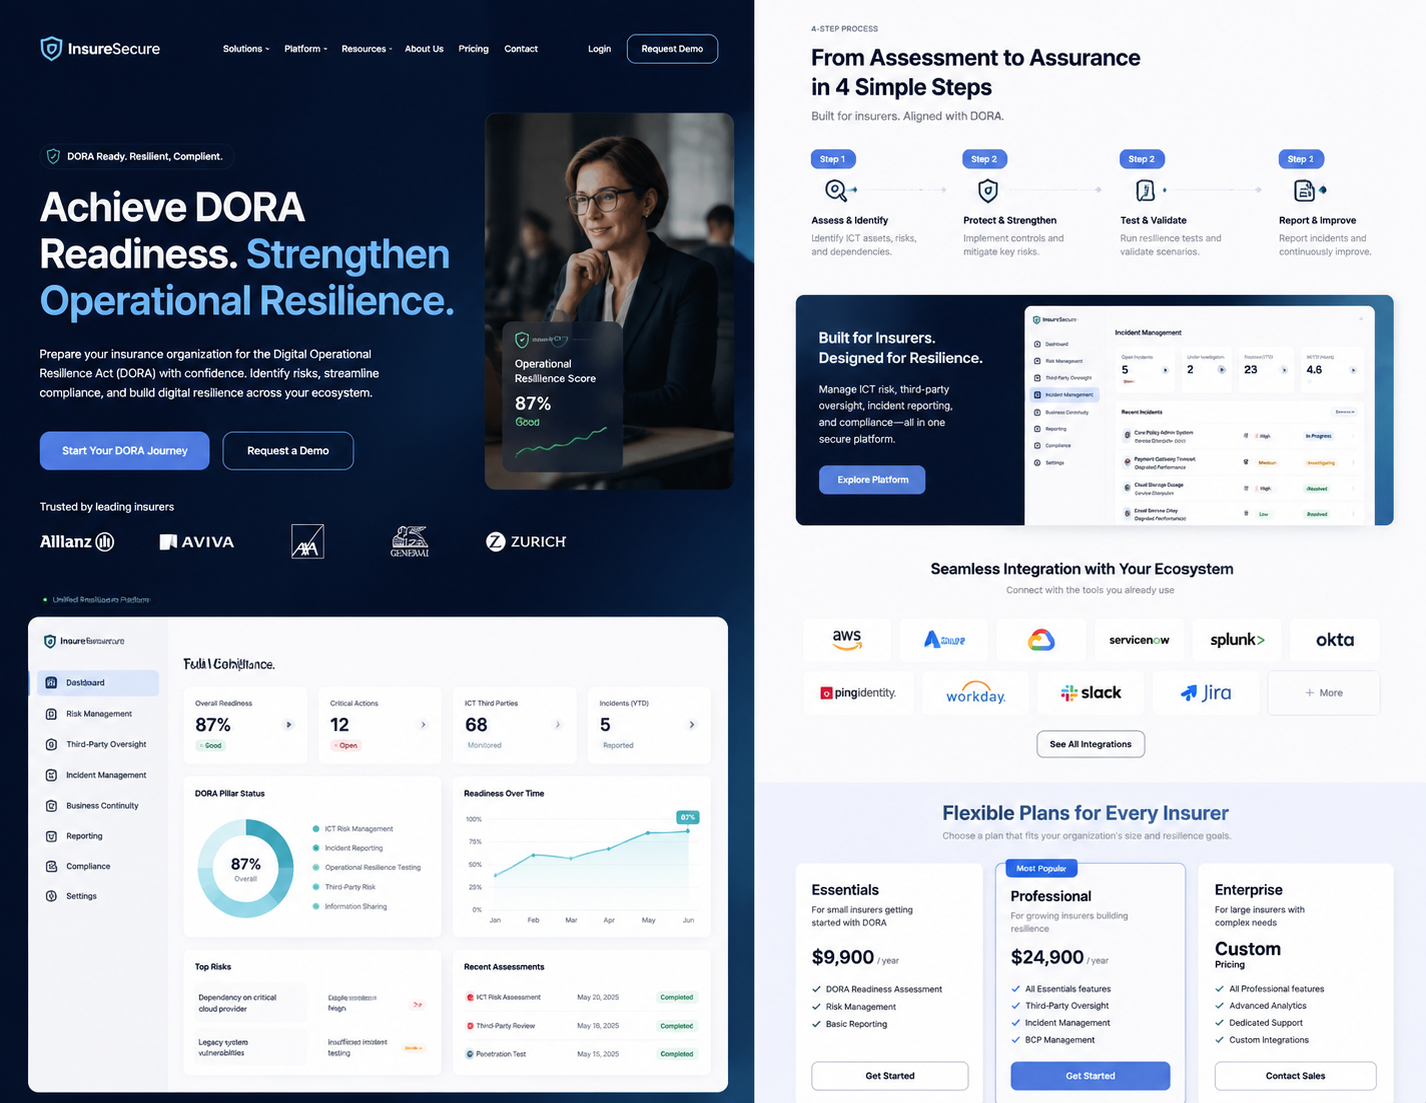
DORA readiness for an insurer
Reached DORA operational-resilience readiness in 11 weeks for an insurer.
Read the full case study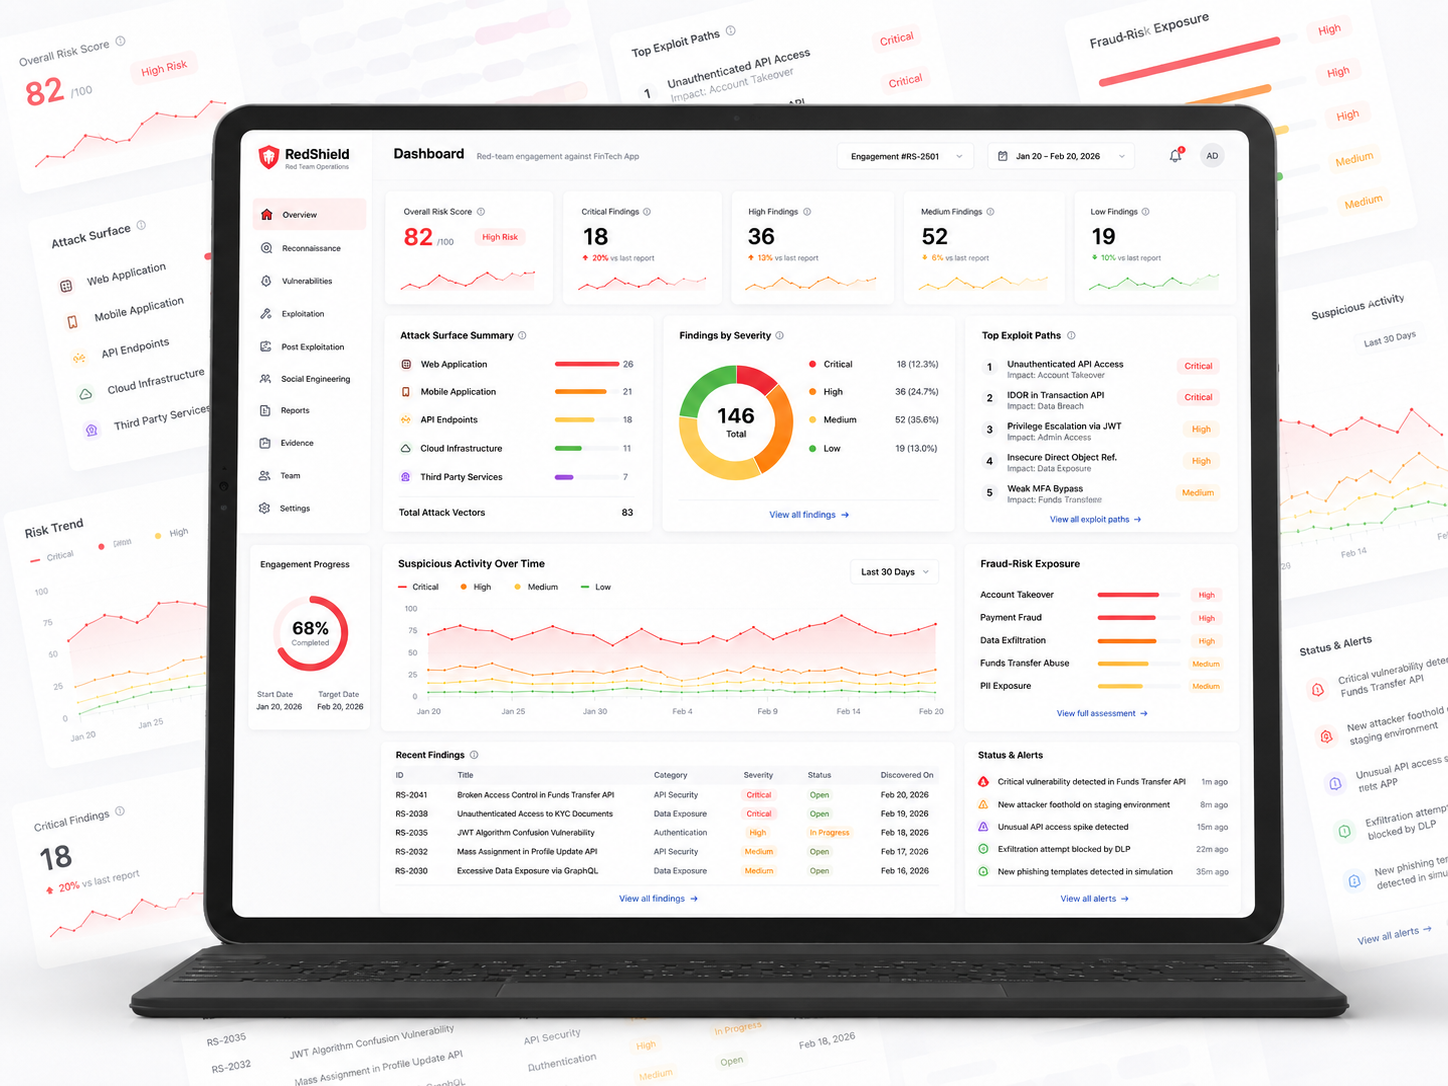
Red-team engagement against a fintech app
Found and helped close three account-takeover paths before a fintech's launch.
Read the full case studyGet a senior architect on the call, first time, every time.
No SDR gauntlet. 30 minutes with an engineer who can scope the problem, name the risks, and give you an honest feasibility call.