
Cybersecurity
Offensive, defensive, and governance security for estates that answer to a regulator.
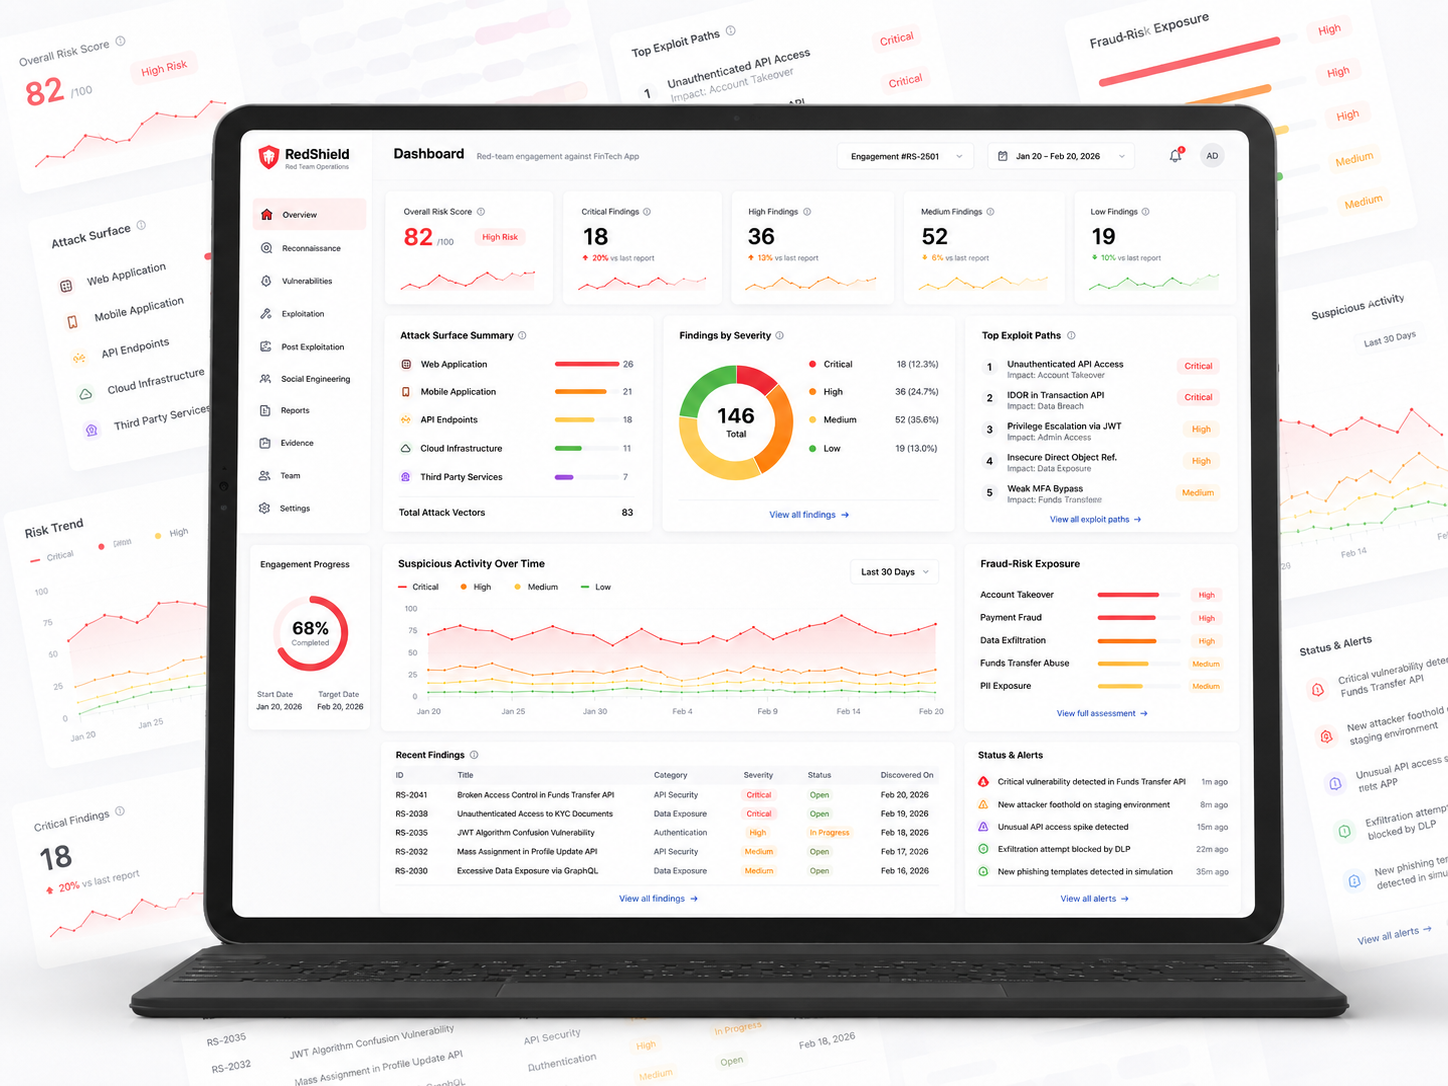
Red-team engagement against a fintech app
Found and helped close three account-takeover paths before a fintech's launch.
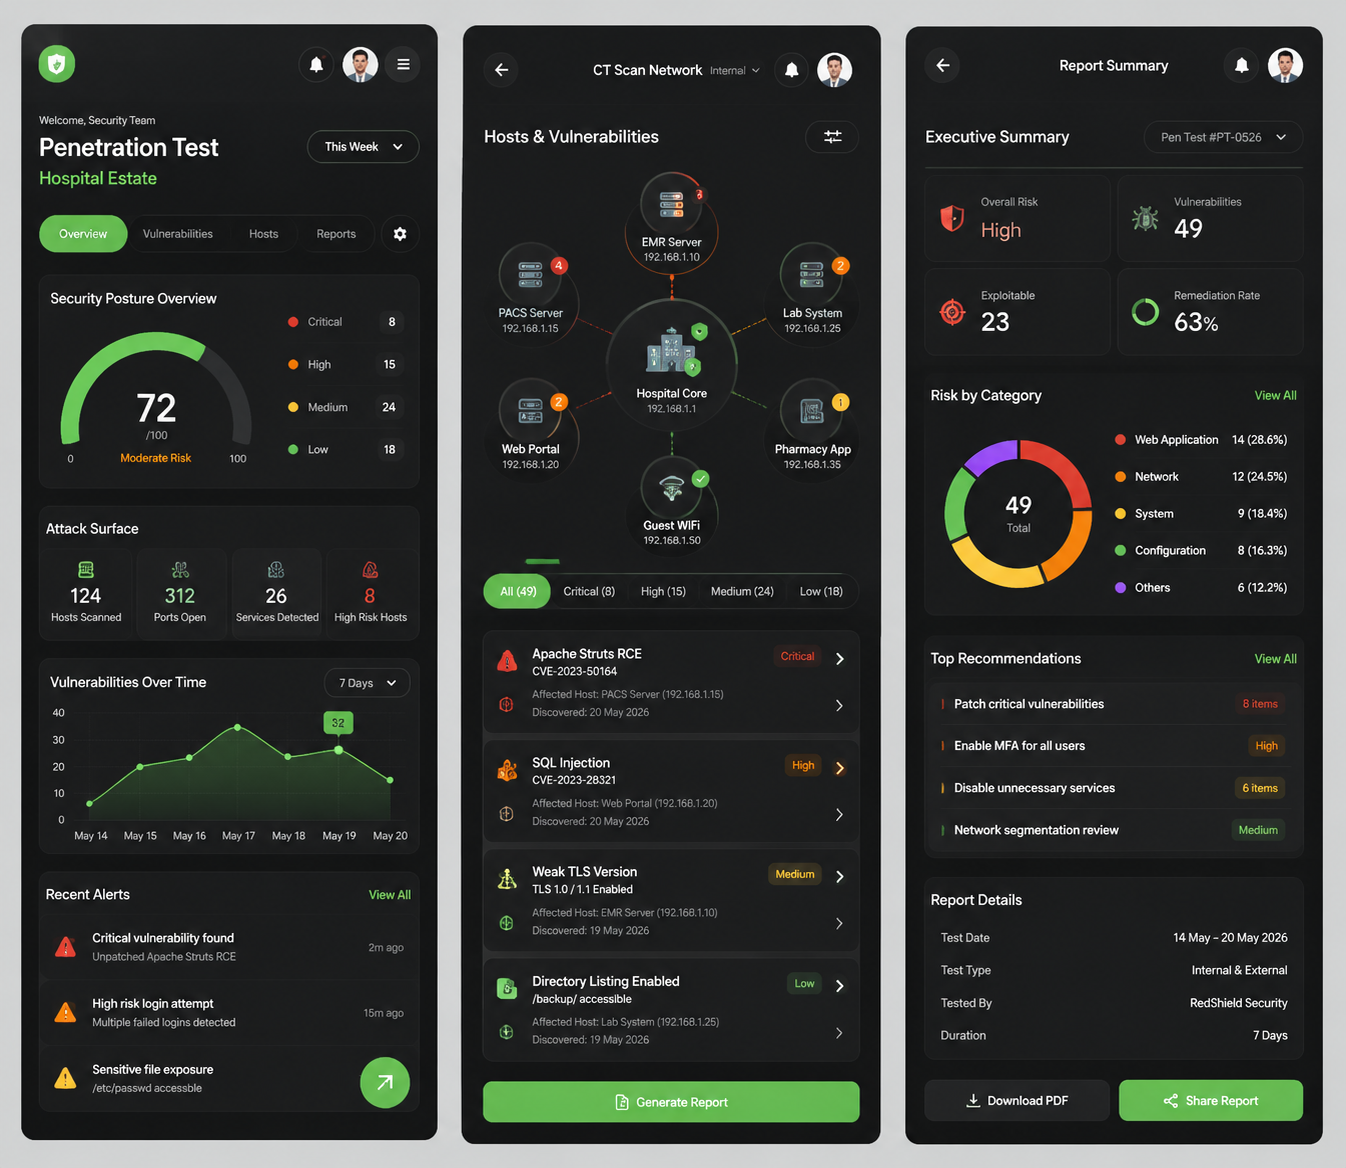
Penetration test for a hospital estate
Surfaced 61 exploitable paths across a hospital estate, prioritised by patient-safety impact.
Cloud penetration test for a retailer
Surfaced 74 exploitable misconfigurations across a retailer's multi-account cloud estate.
Zero-trust rollout for a government agency
Rolled zero-trust access to 25,000 civil servants without a productivity dip.
Privileged access overhaul for a manufacturer
Cut standing privileged access 90% across a manufacturer's IT and OT estate.
Customer identity rebuild for a wealth platform
Passwordless identity cut account-takeover 22% and sign-in friction at a wealth platform.
GxP and Annex 11 compliance for a pharma manufacturer
Reached validated Annex 11 compliance for a pharma manufacturer in 12 weeks.
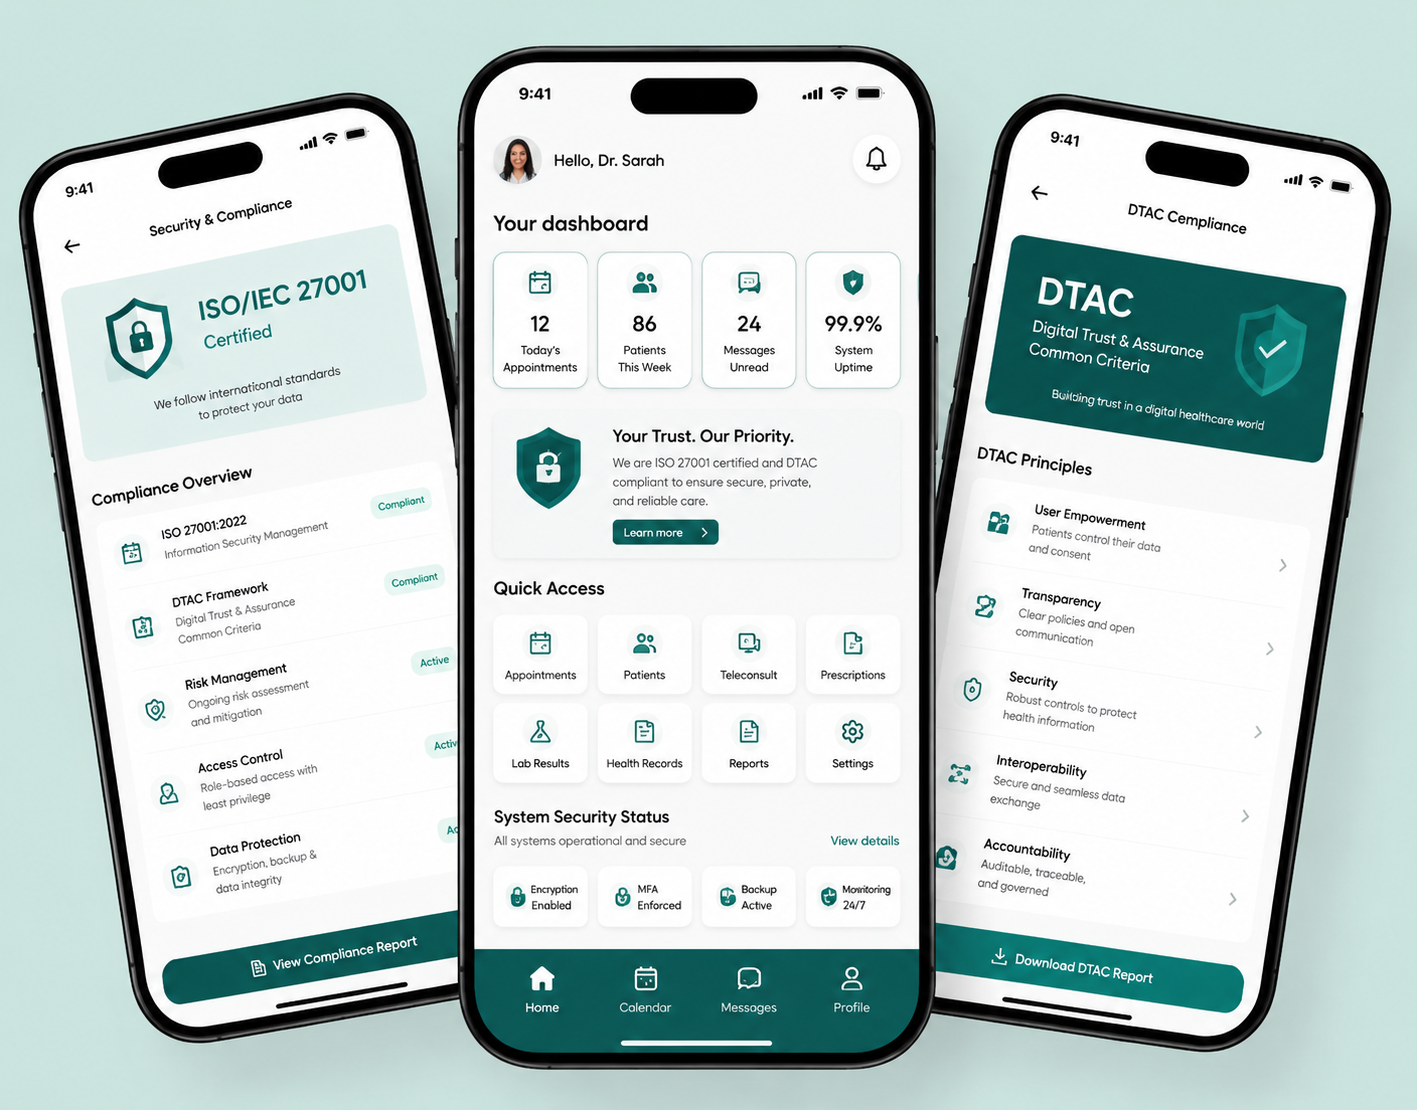
ISO 27001 and DTAC for a telemedicine platform
Achieved ISO 27001 and NHS DTAC assurance at first assessment for a telemedicine platform.
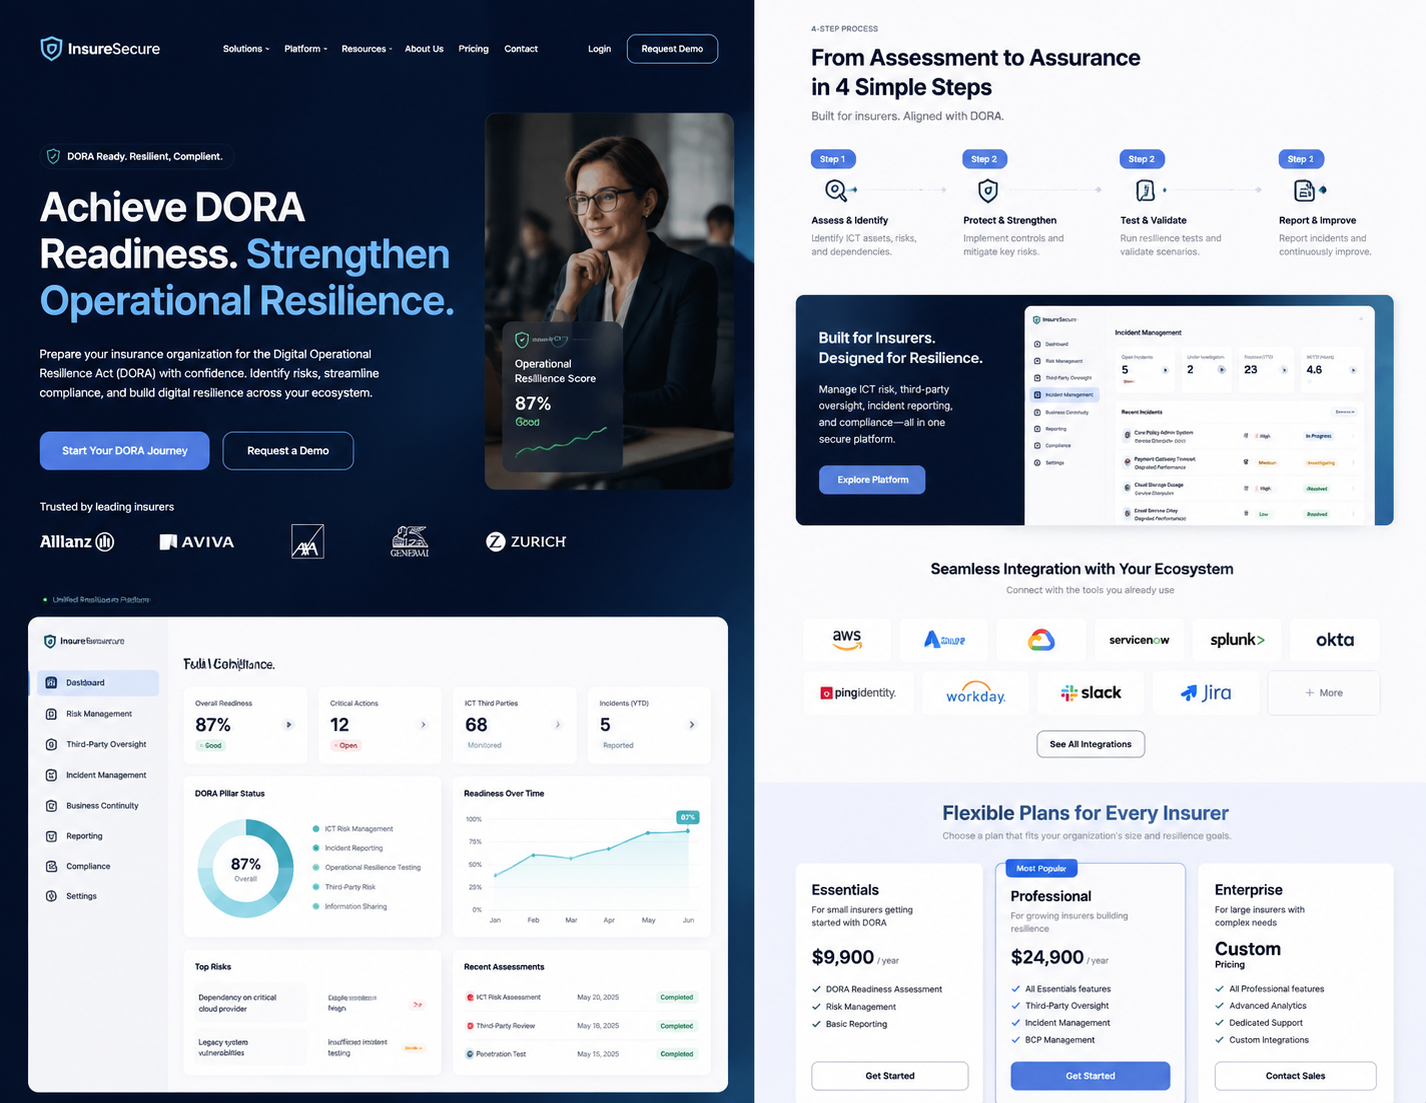
DORA readiness for an insurer
Reached DORA operational-resilience readiness in 11 weeks for an insurer.
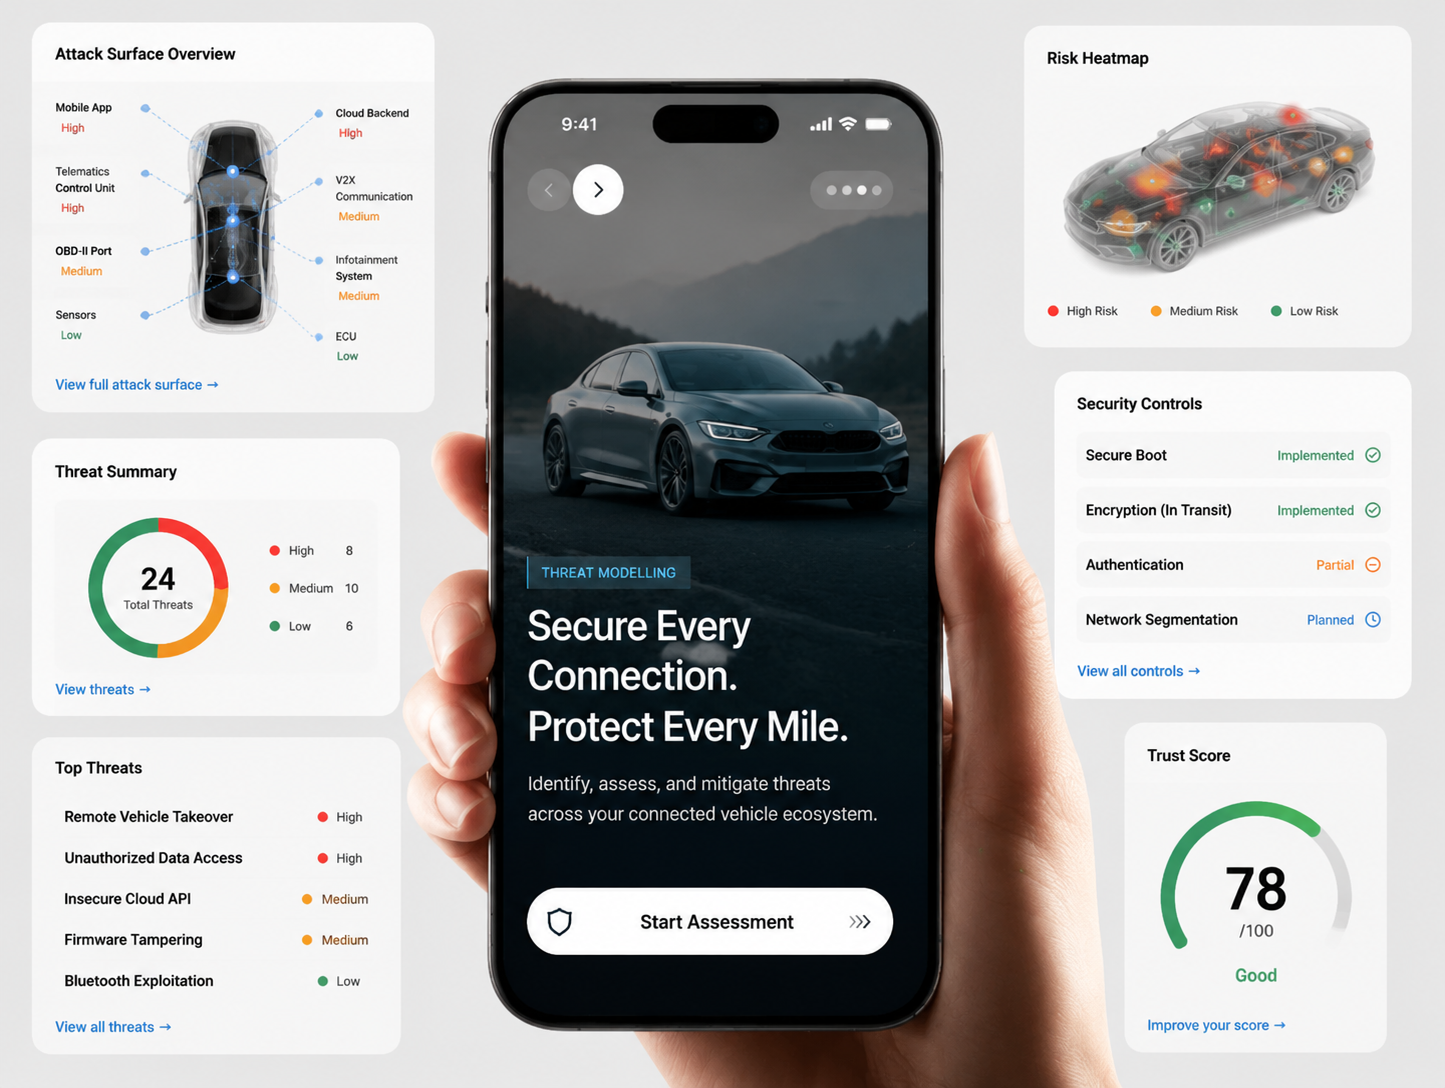
Threat modelling a connected vehicle
Mapped and mitigated attack paths for a UNECE R155-regulated connected vehicle.
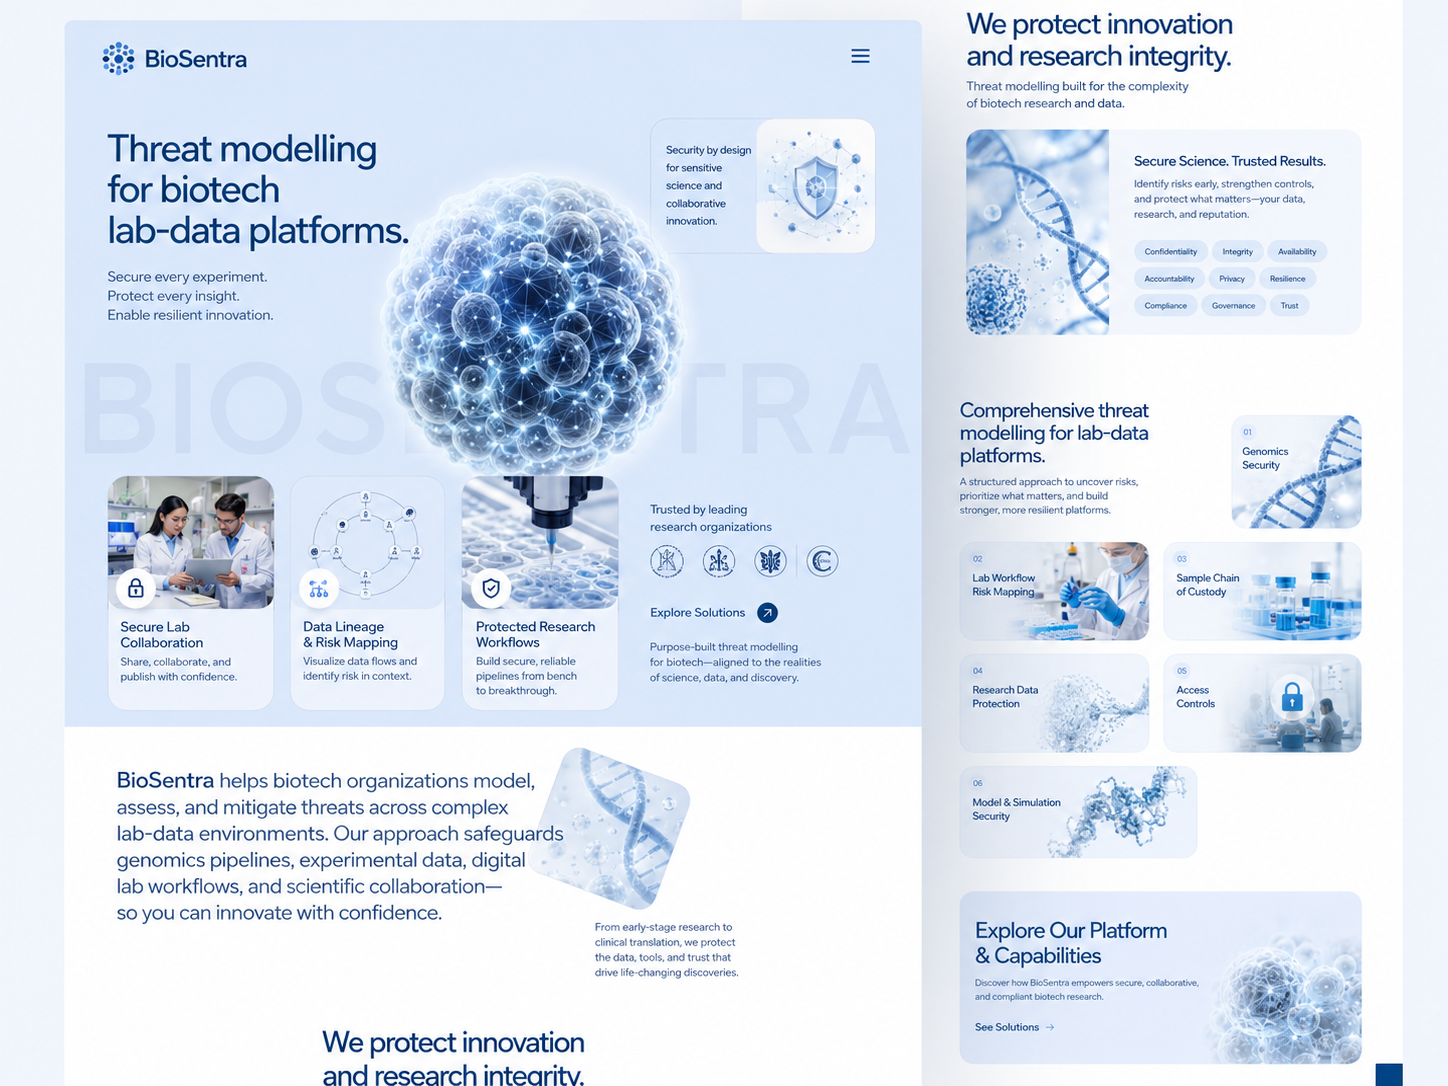
Threat modelling a biotech lab-data platform
Identified nine design-level risks in a biotech's lab-data platform before build.
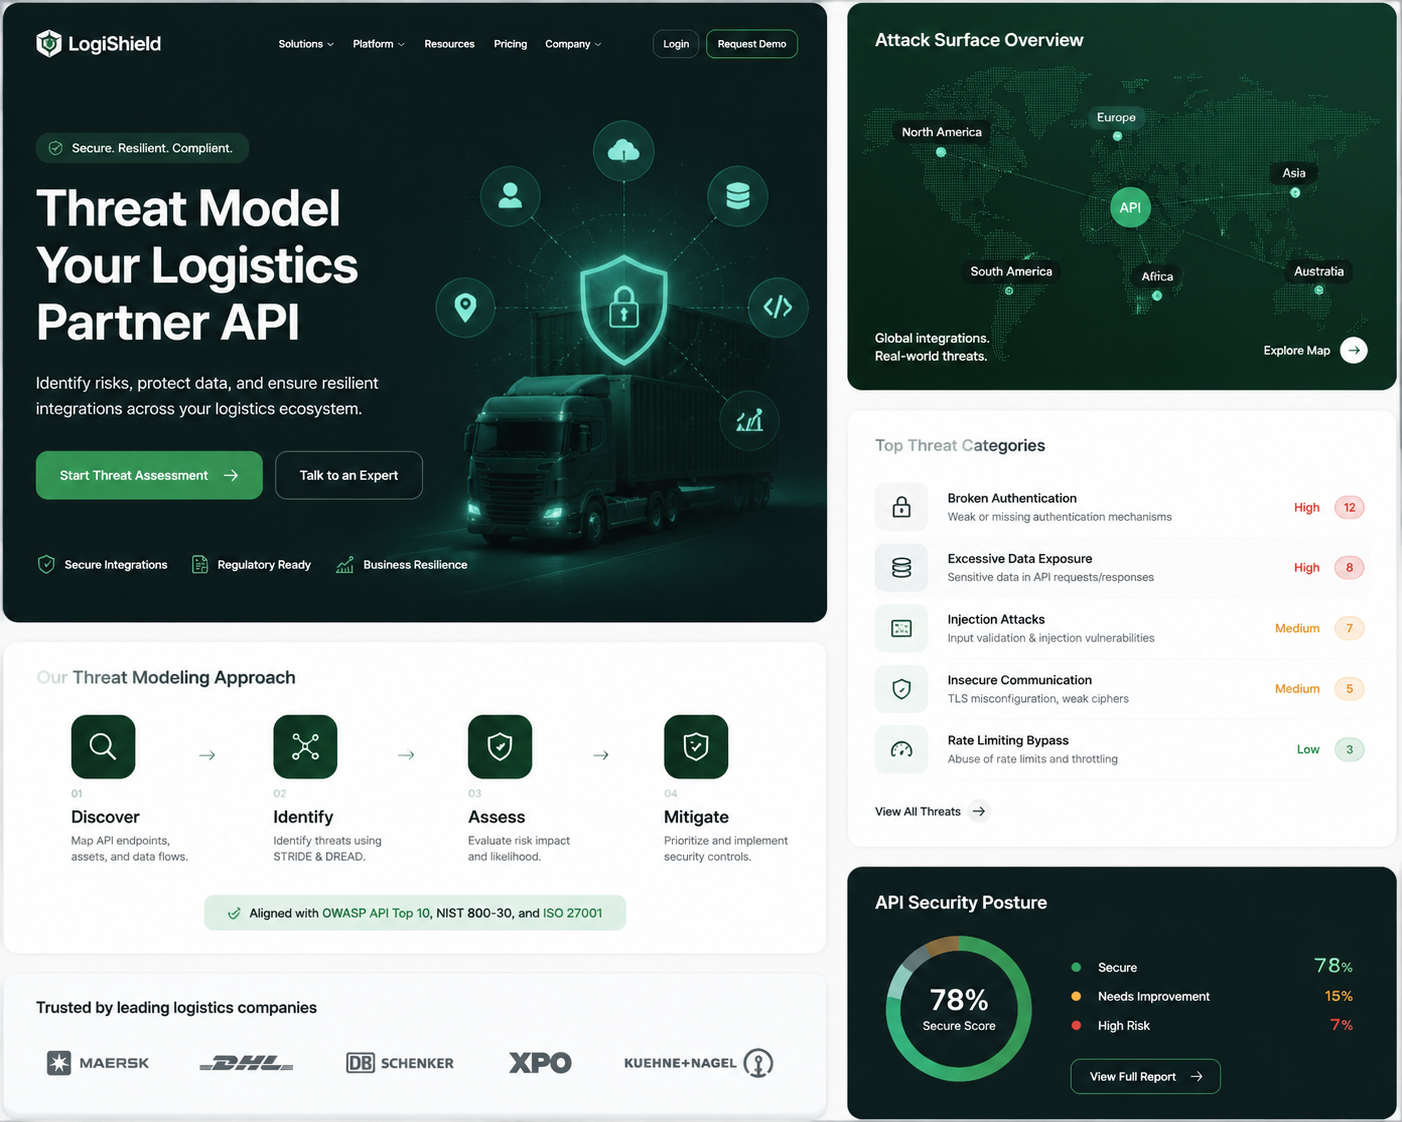
Threat modelling a logistics partner API
Hardened a logistics partner API against abuse before third-party onboarding.
Questions about our case studies
Get a senior architect on the call, first time, every time.
No SDR gauntlet. 30 minutes with an engineer who can scope the problem, name the risks, and give you an honest feasibility call.